
TitanHide
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
anti-botbinary-analysisdebuggers+4
mrexodia/titanhideWindows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
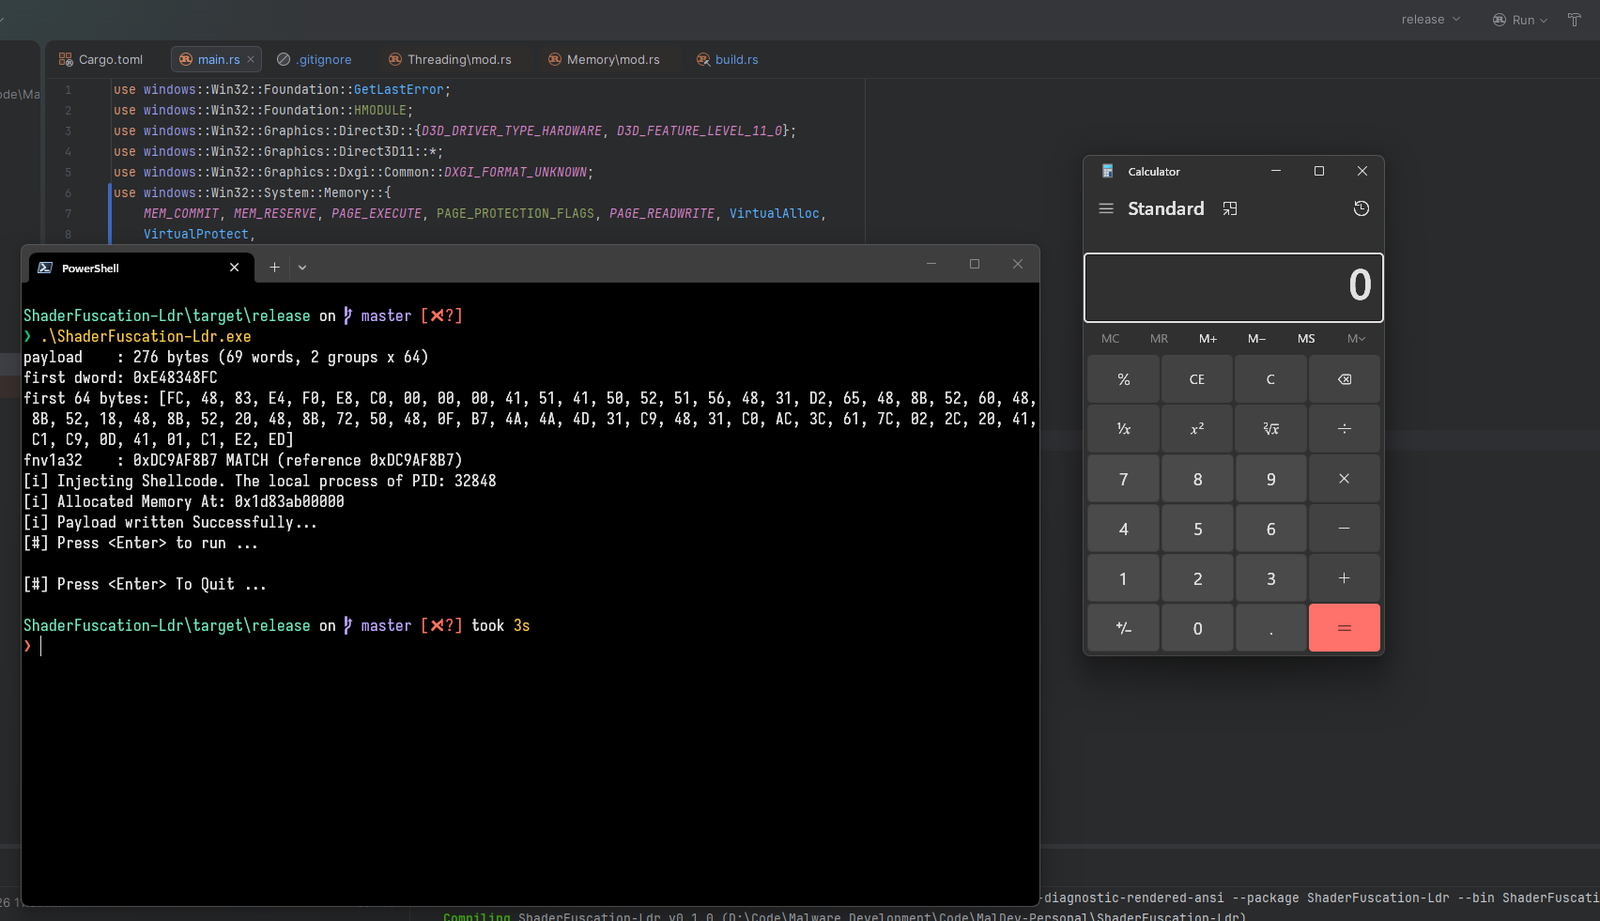 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 gmh5225/eac
Compiles EAC and EOC anti-cheat SDKs, reversing research, and code resources to study how game anti-cheat systems integrate and operate.
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 withsecurelabs/amsidetection
Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.
 mindcrypt/covertchannels-steganography
A list of covert channels and steganography/steganalysis resources (books, papers & tools)
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
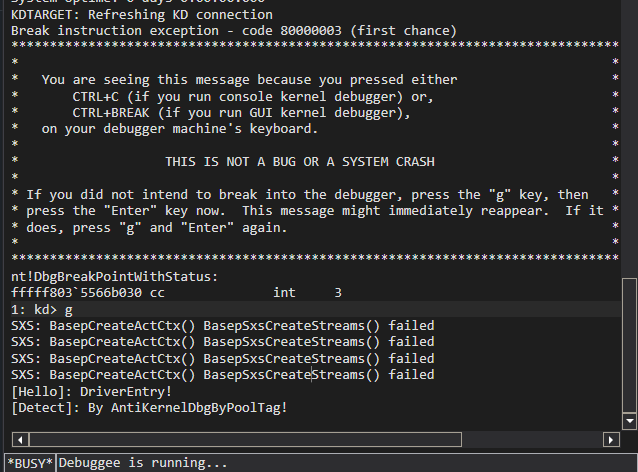 gmh5225/antikerneldebug-poc
POC about how to detect windows kernel debug by pool tag.
 neo23x0/yara-performance-guidelines
A guide on how to write fast and memory friendly YARA rules
 frank2/packer-tutorial
A tutorial on how to write a packer for Windows!
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
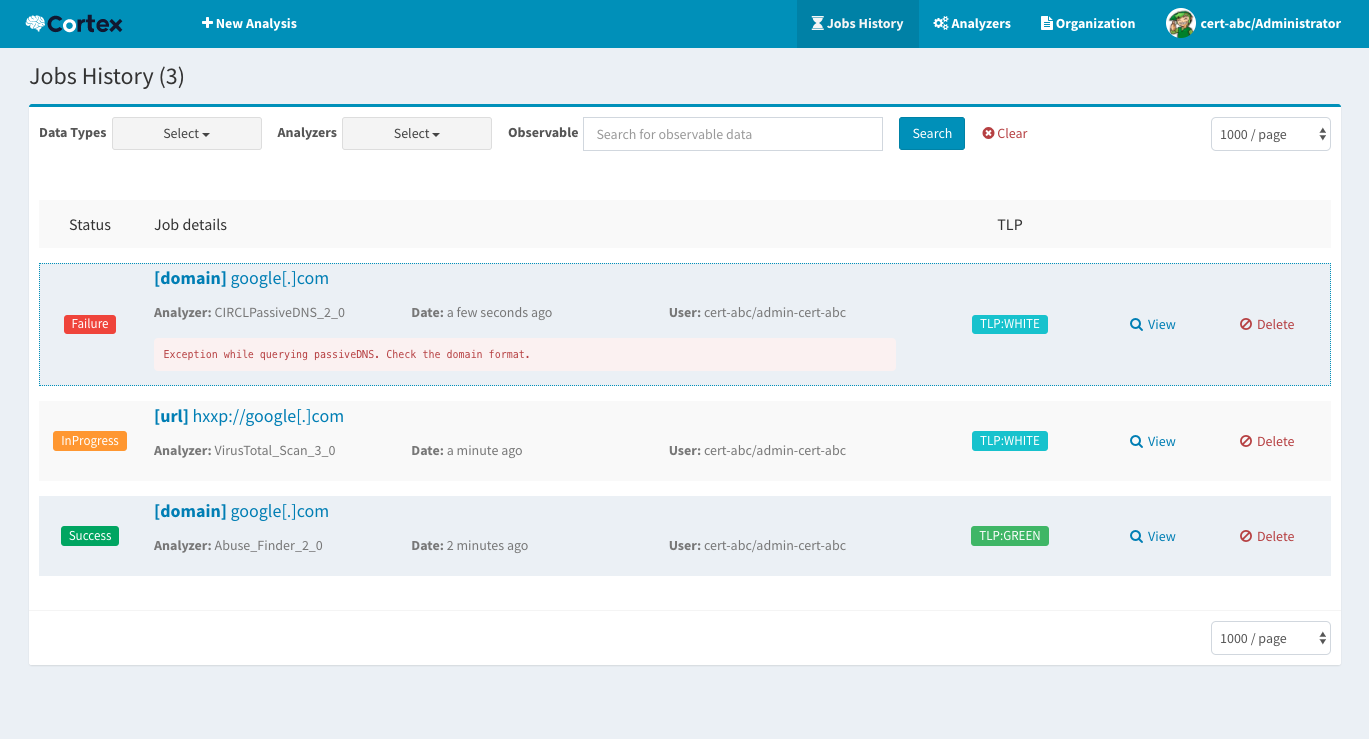 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
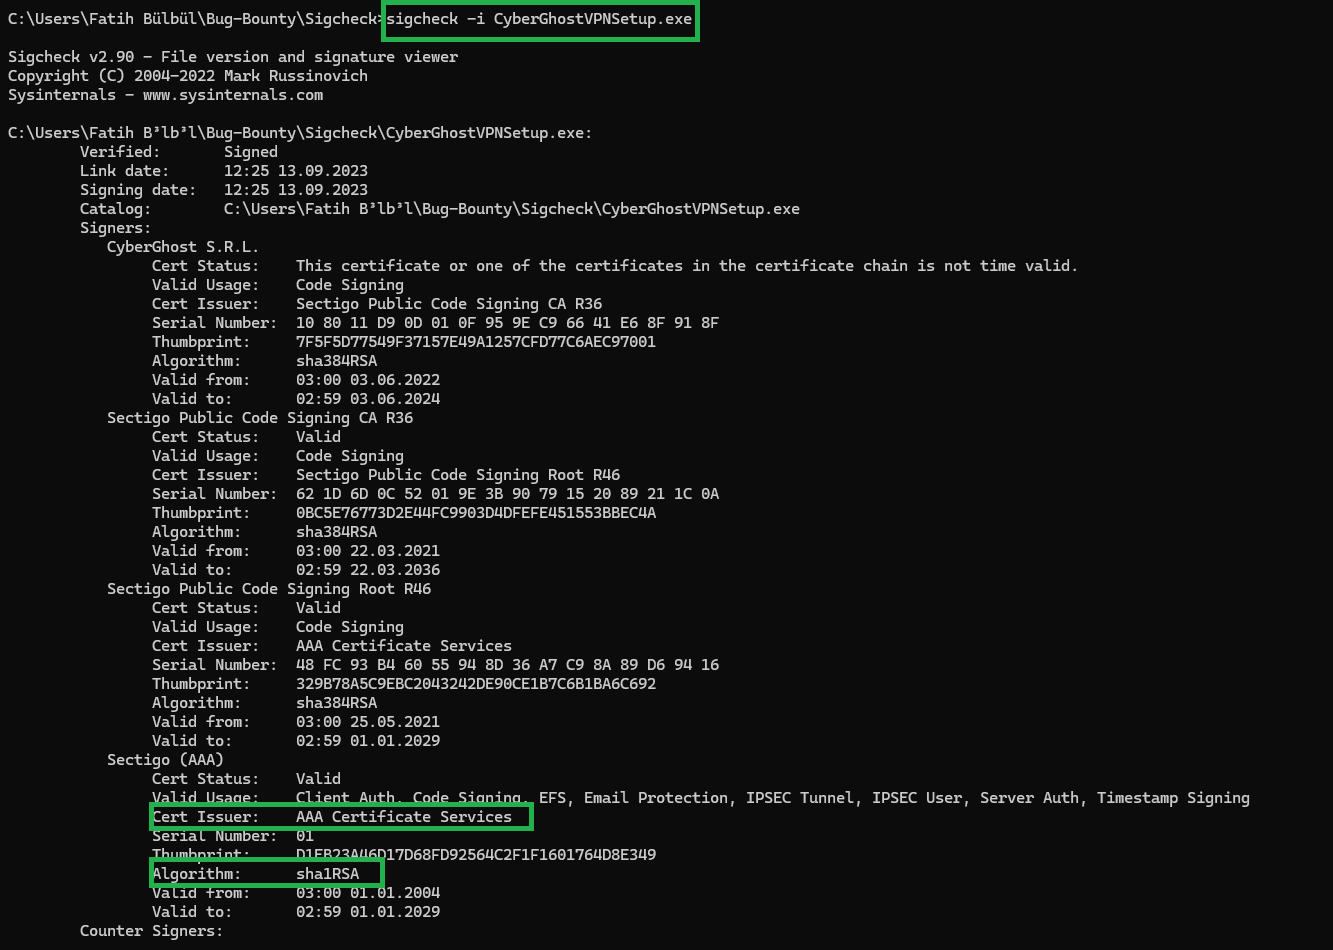 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 nccgroup/cve-2017-8759
NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements
 mrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack
It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…