
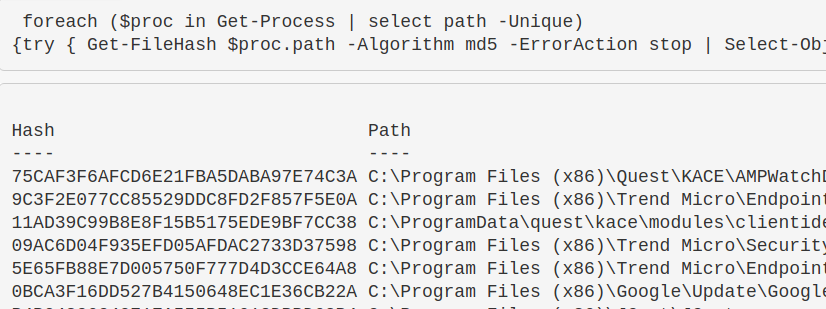
Blue-Team-Notes
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
curated-resourcesdigital-forensicseducation+5
1.8k
purp1ew0lf/blue-team-notesYou didn't think I'd go and leave the blue team out, right?
 fr0gger/iatelligence
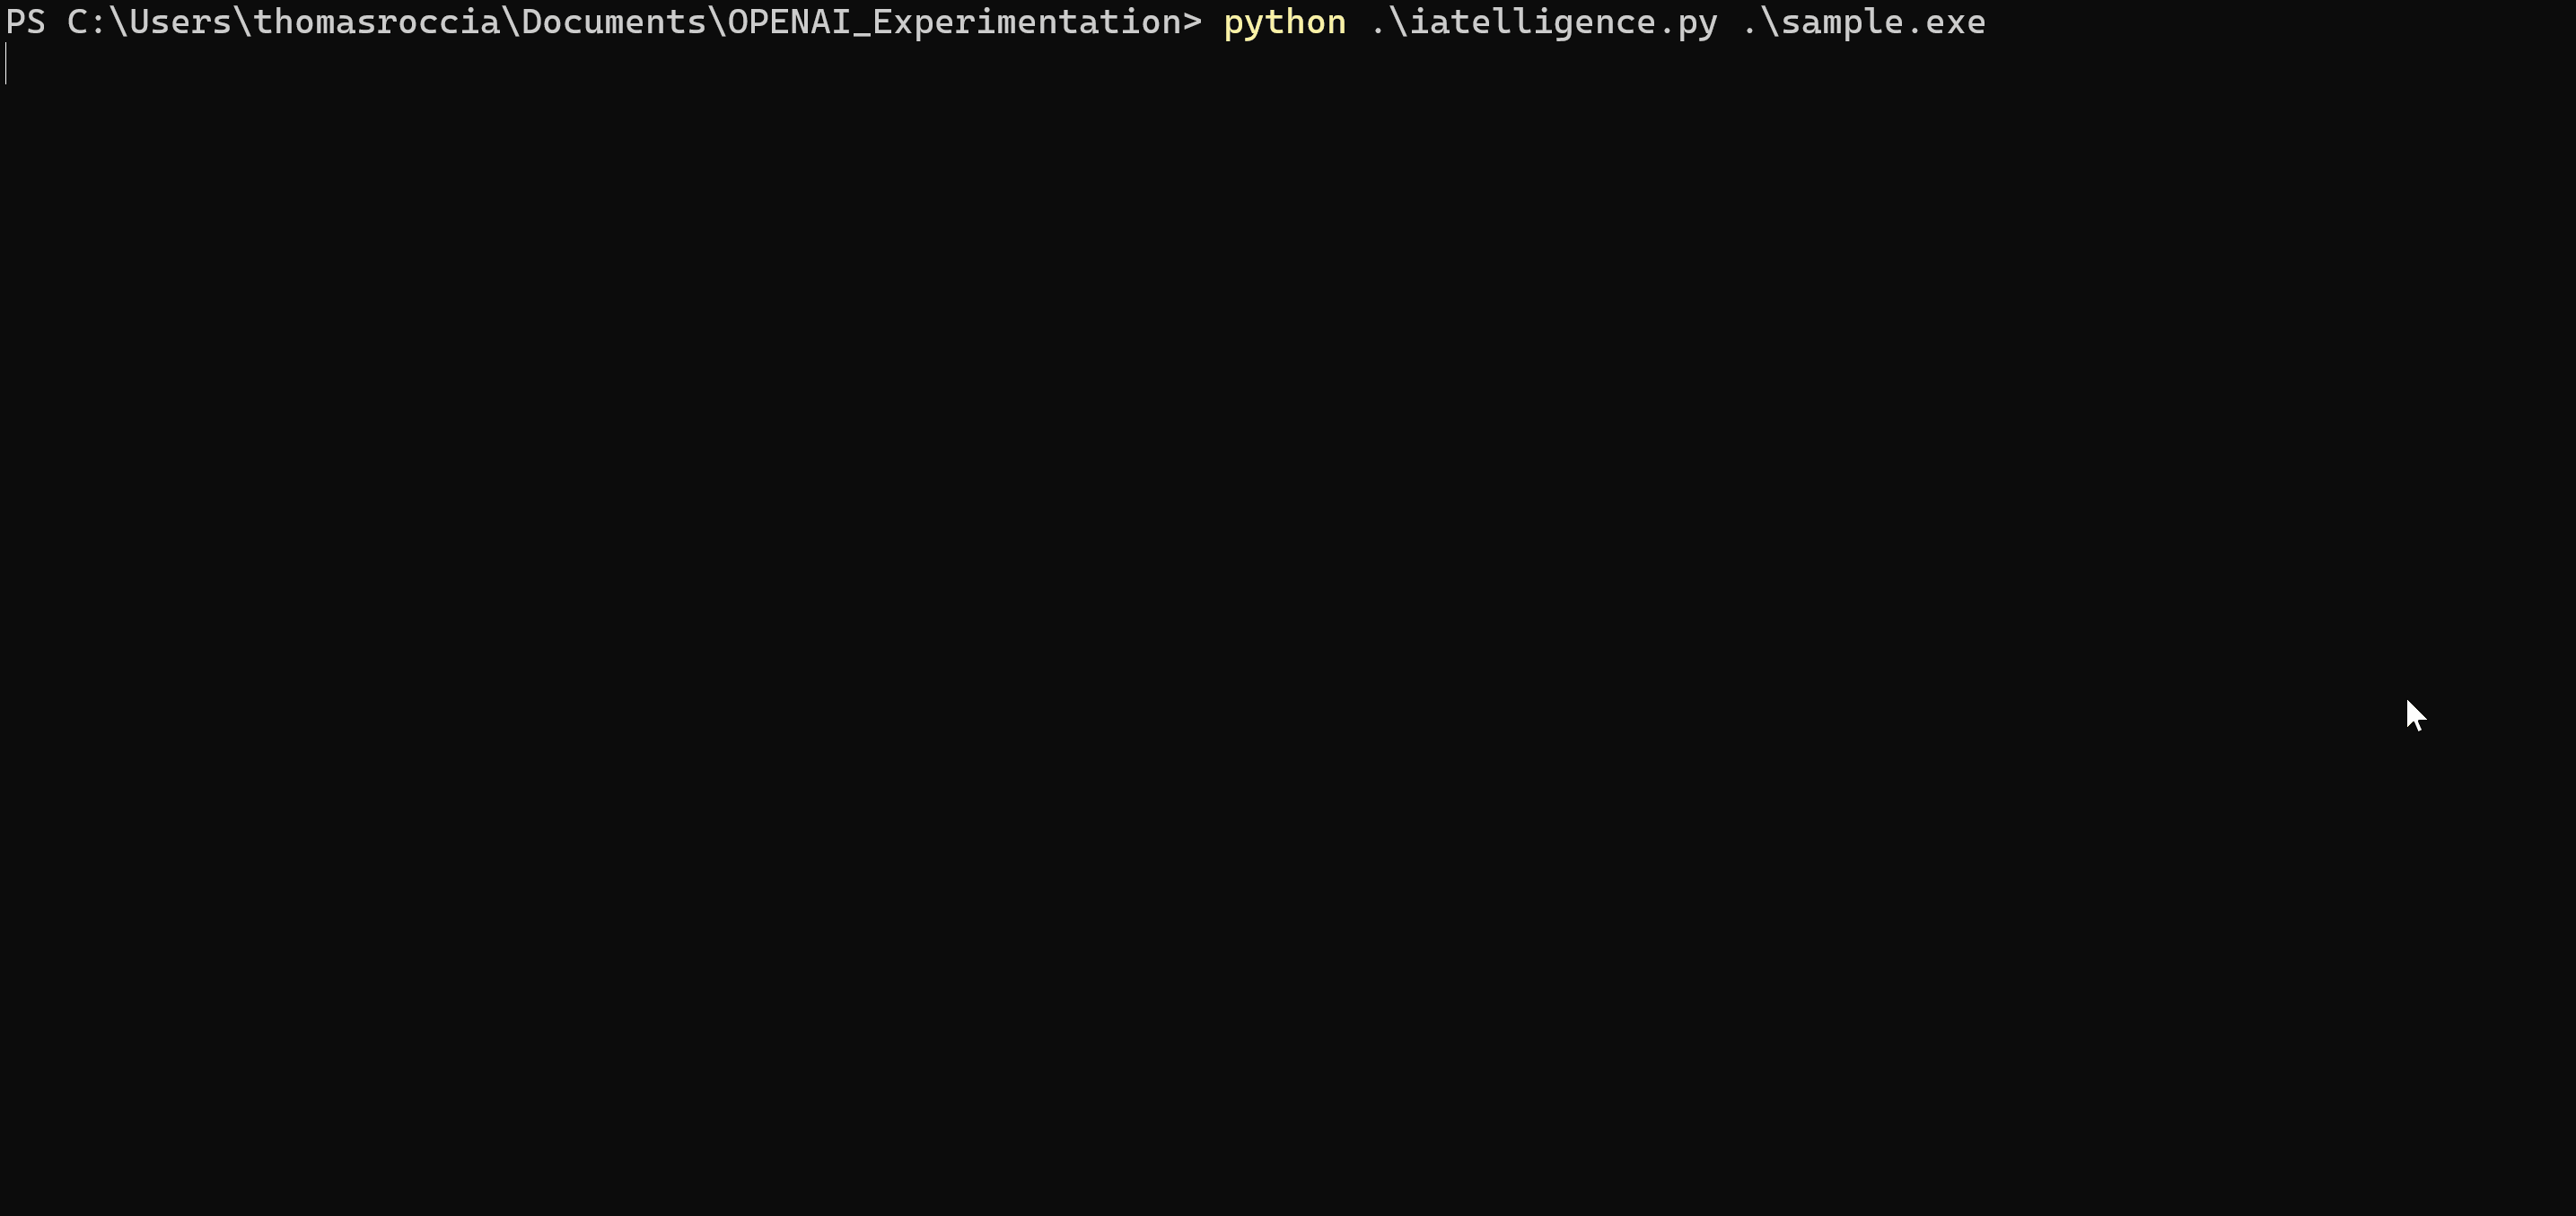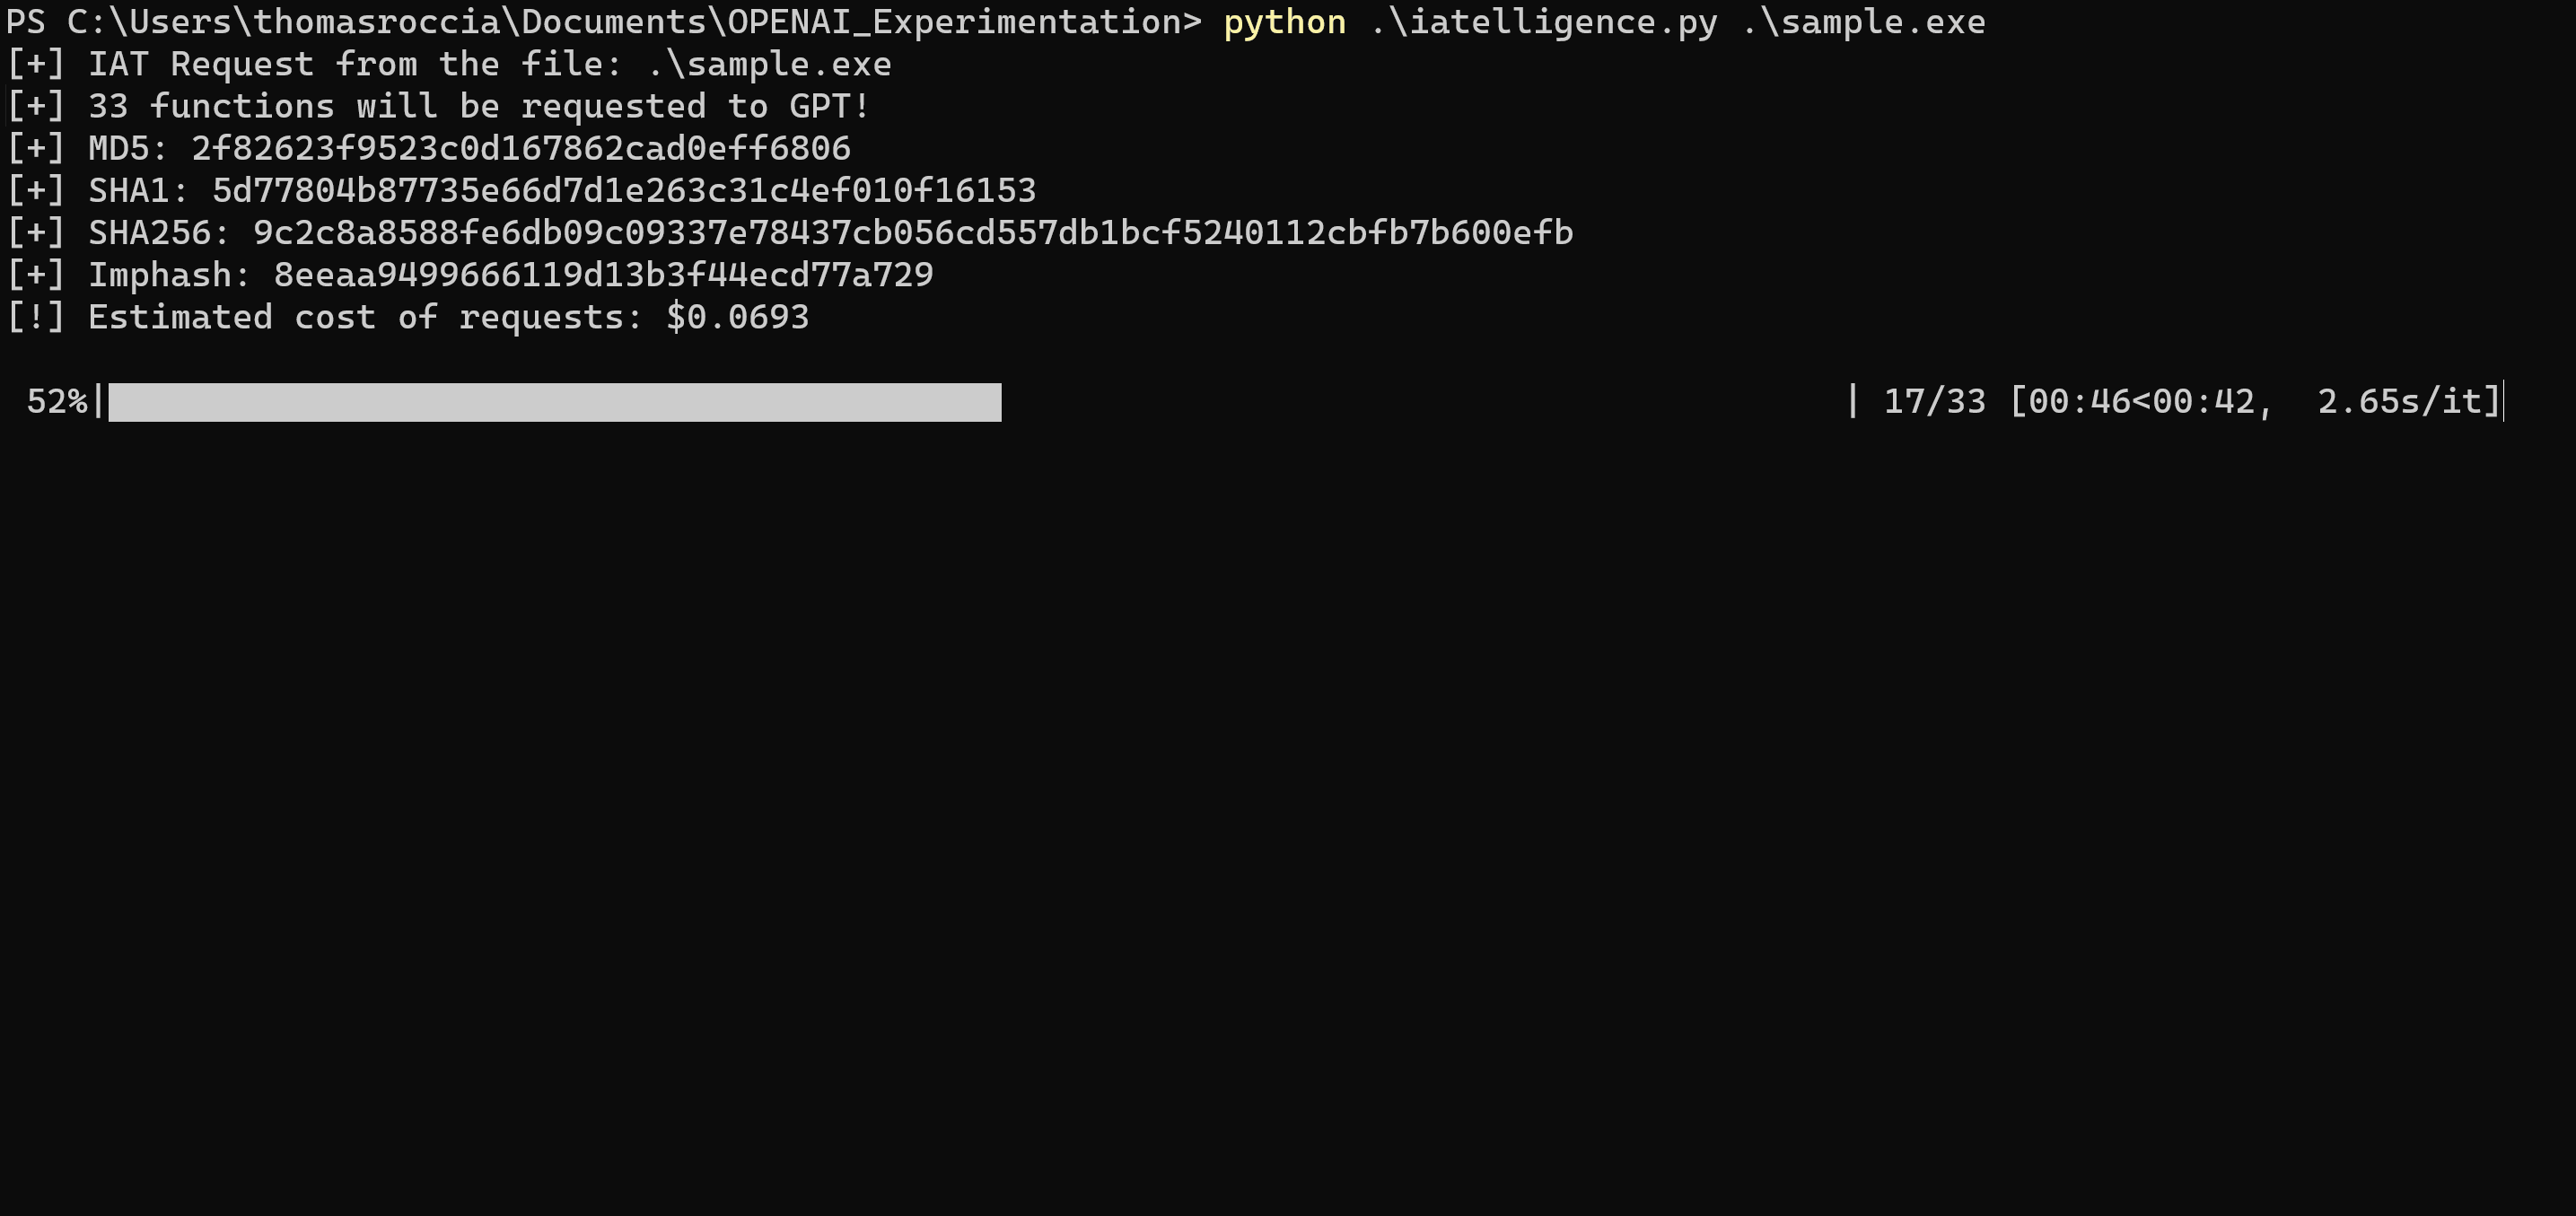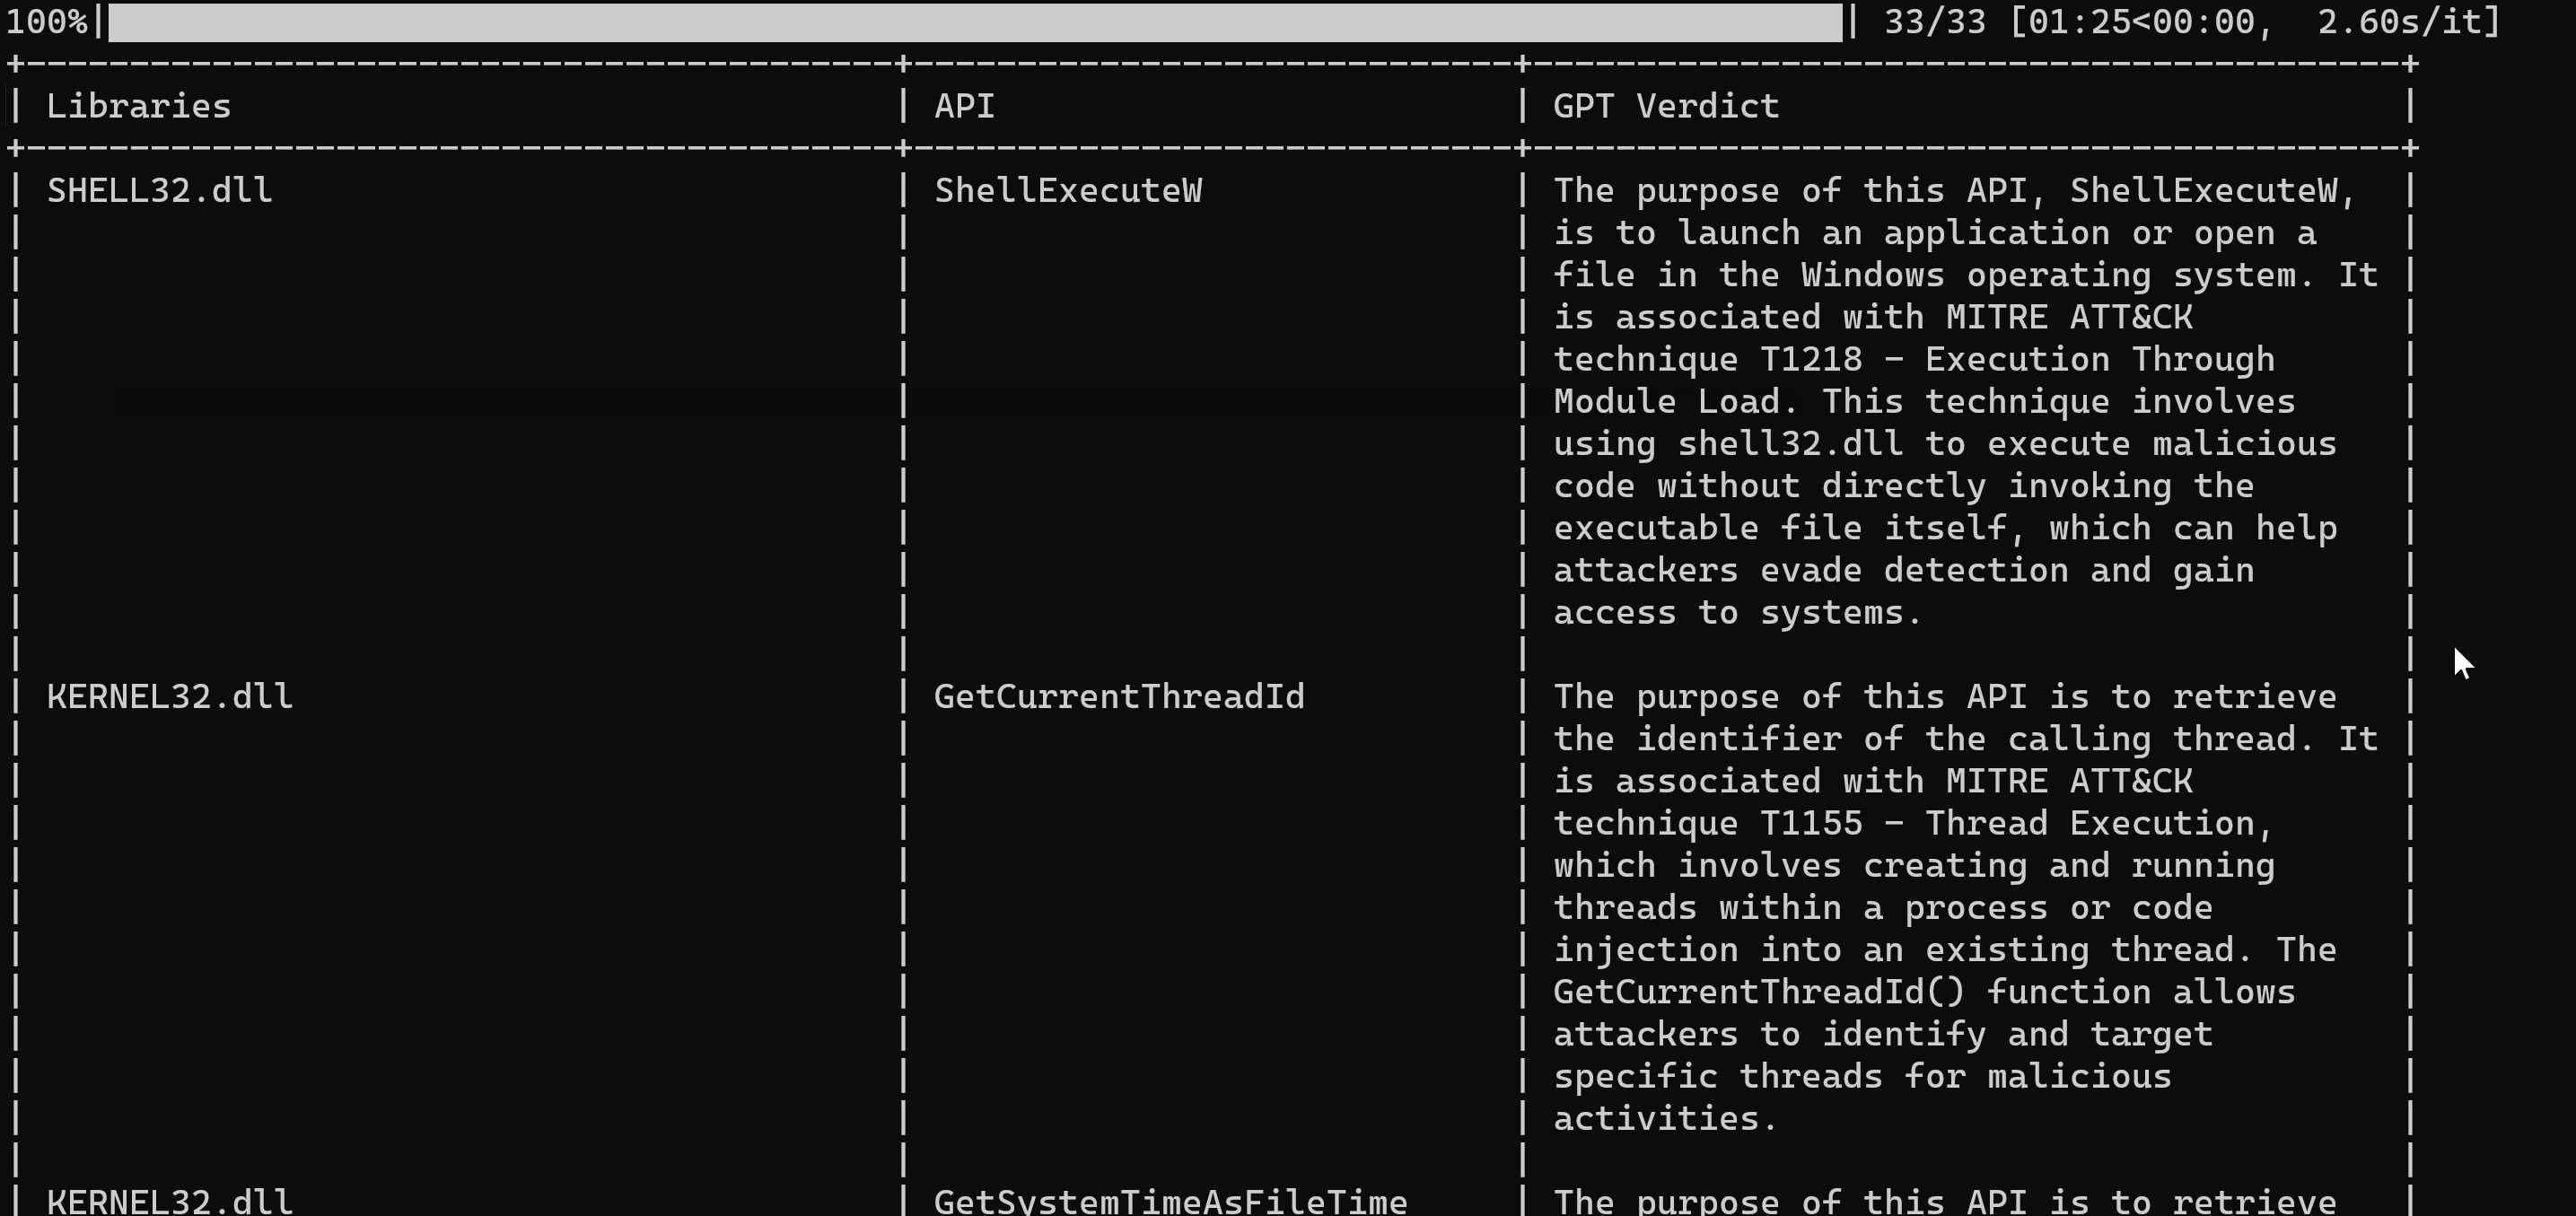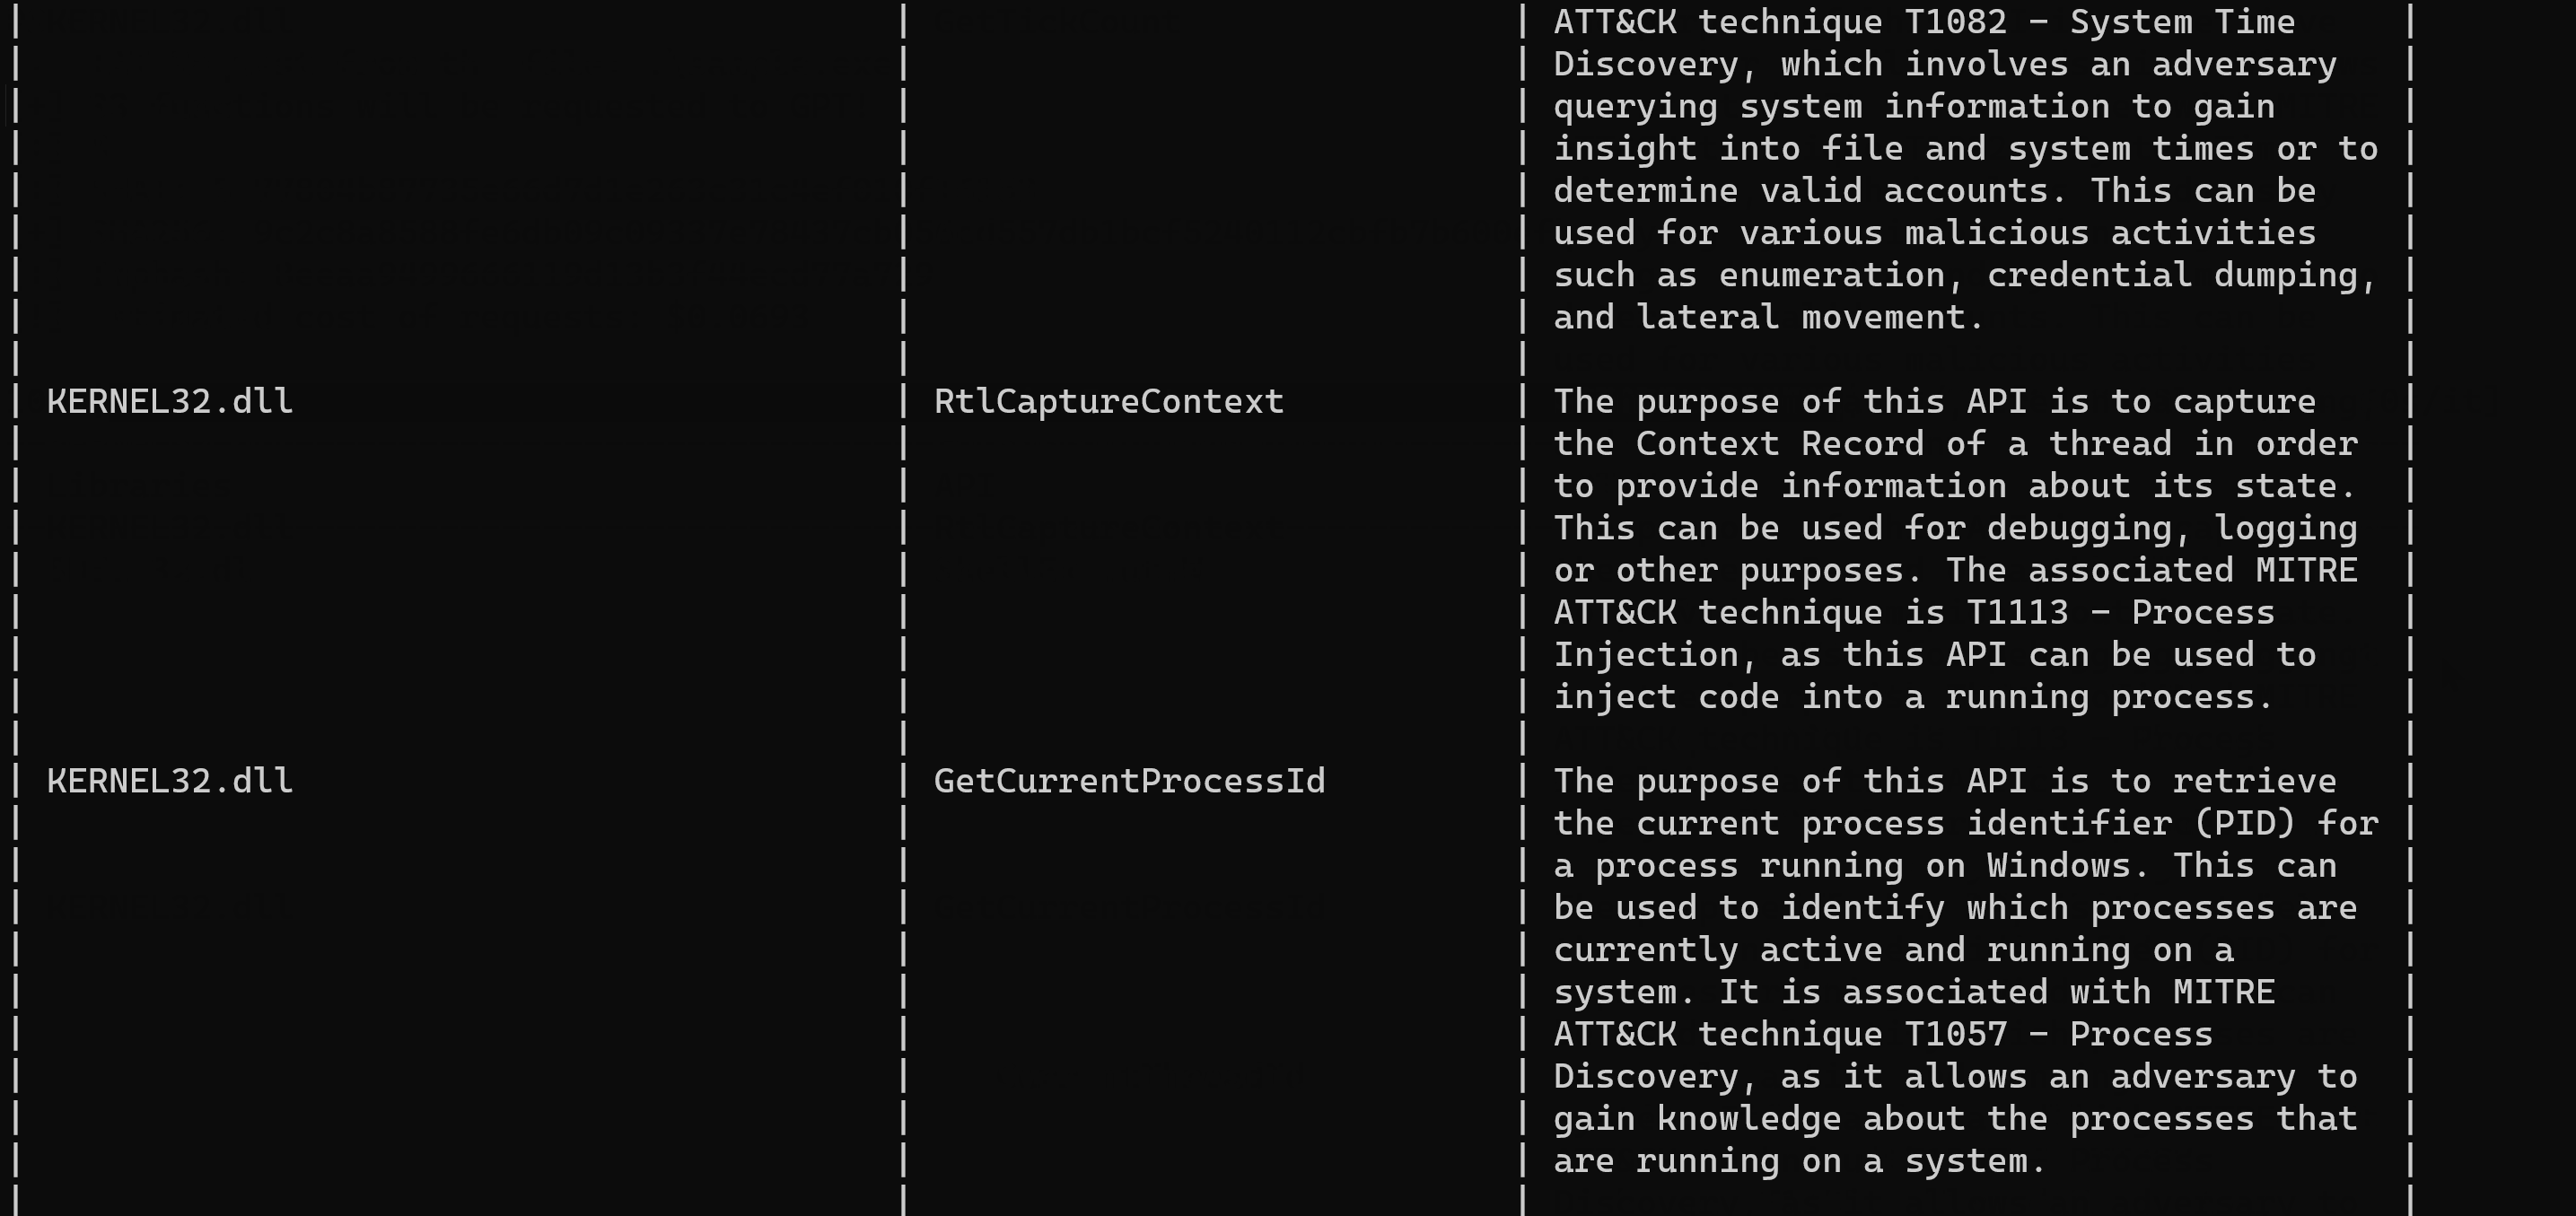
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 buguroo/cuckooautoinstall
Auto Installer Script for Cuckoo Sandbox
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
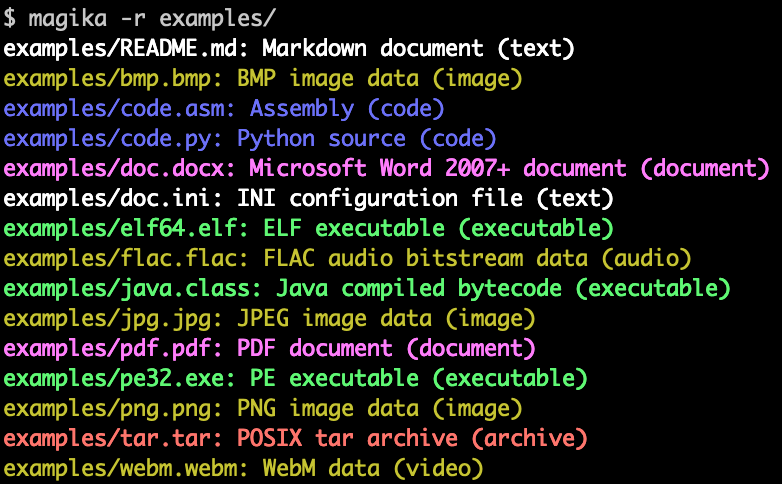 google/magika
Fast and accurate AI powered file content types detection
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
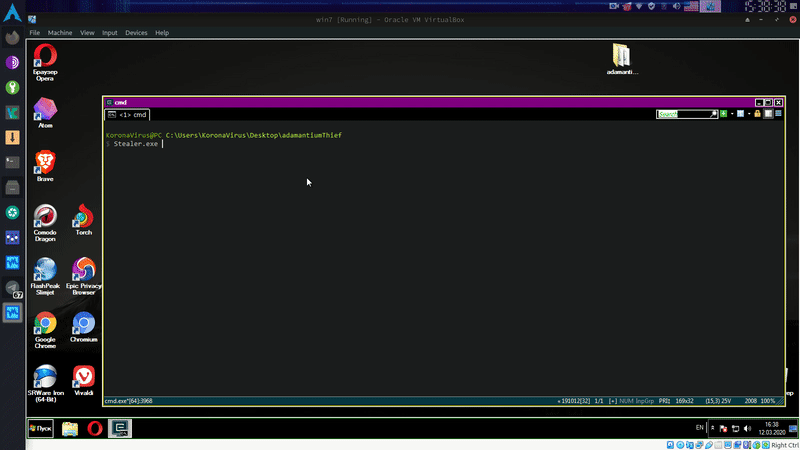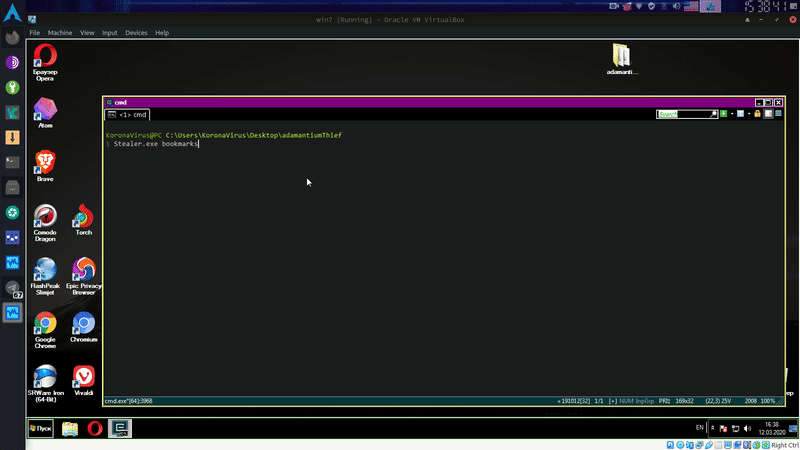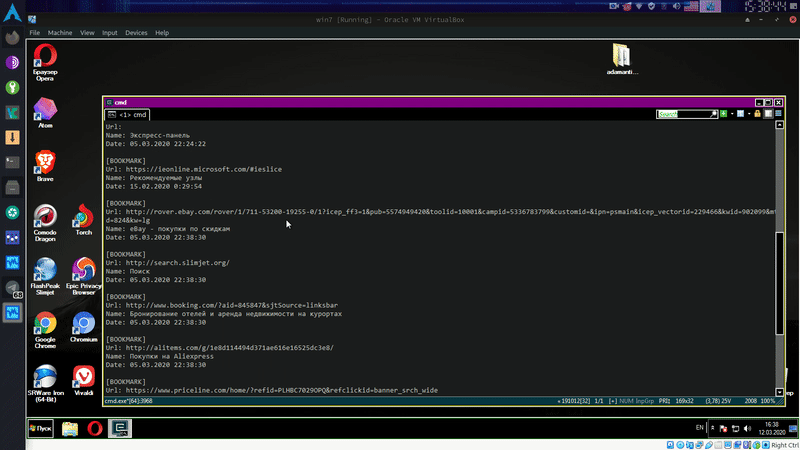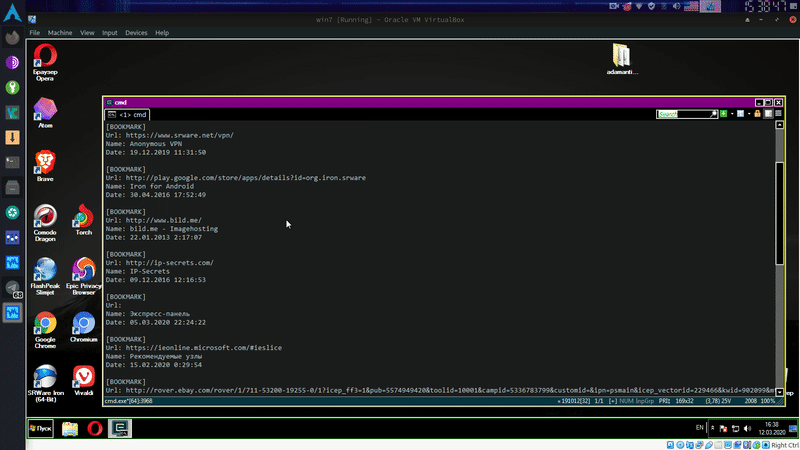 limerboy/adamantium-thief
:key: (THIS CODE IS OUTDATED FOR NEW CHROME VERSIONS) Decrypt chromium based browsers passwords, cookies, credit cards, history, bookmarks, autofill.…
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
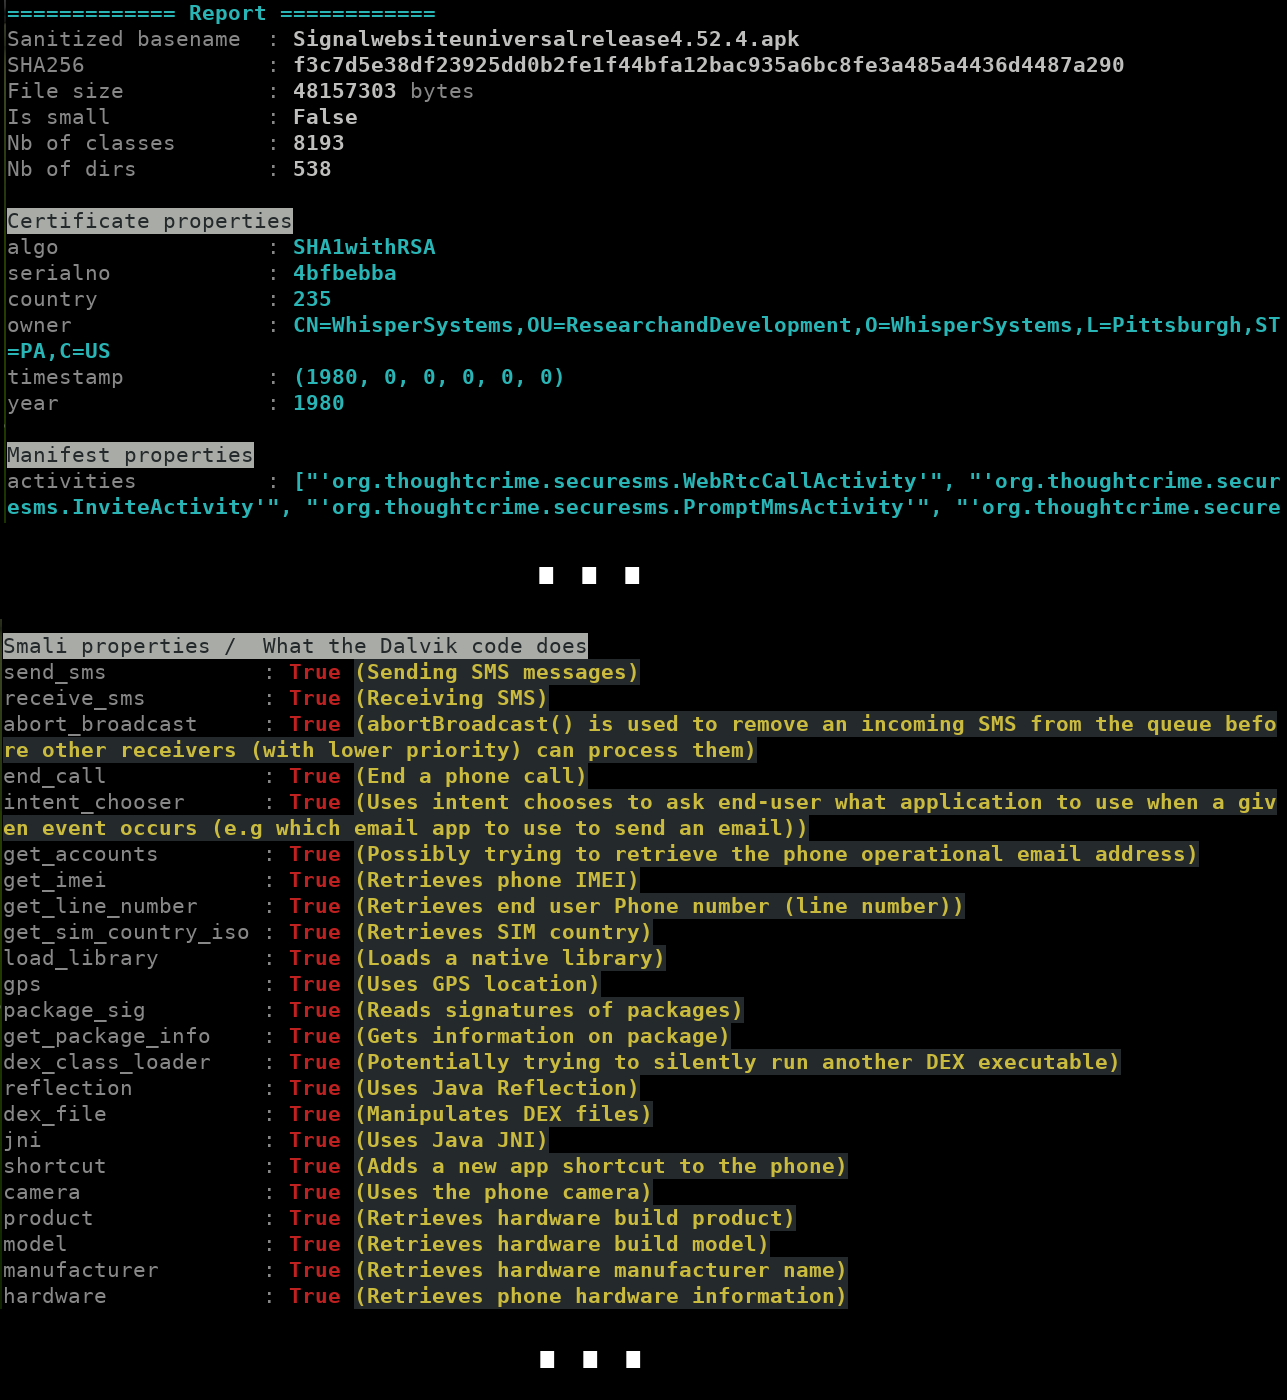 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.