SuperGhidra
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
ai-assisted-reversingandroid-securitybinary-analysis+8
192
yuatemycat/superghidraPython toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 eset/malware-research
Code written as part of our various malware investigations
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 simoesctt/sctt-2026-33-0007-the-ole-vortex-laminar-bypass-
Microsoft just released emergency patches for CVE-2026-21509, a zero-day in the Office Suite that bypasses OLE/COM mitigations when a user simply…
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 hasherezade/pesieve-go
Golang bindings for PE-sieve
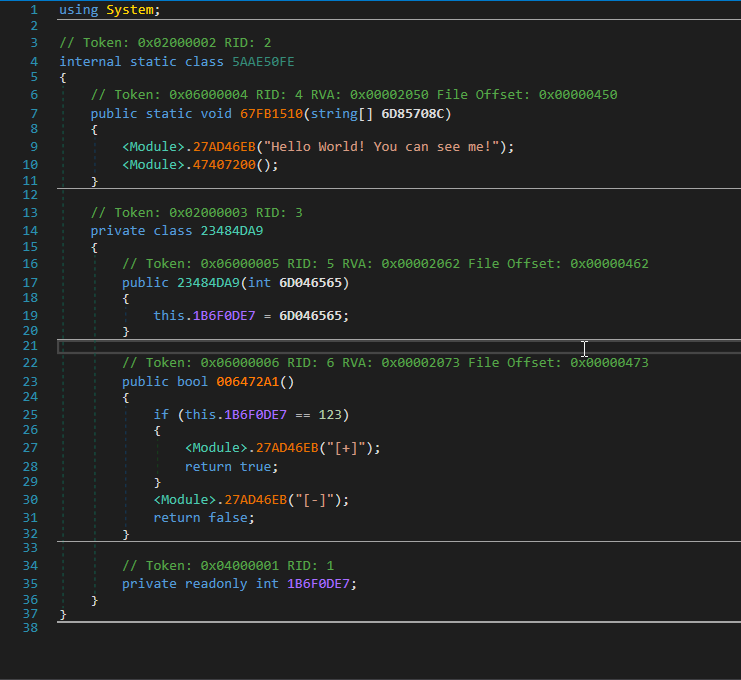 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
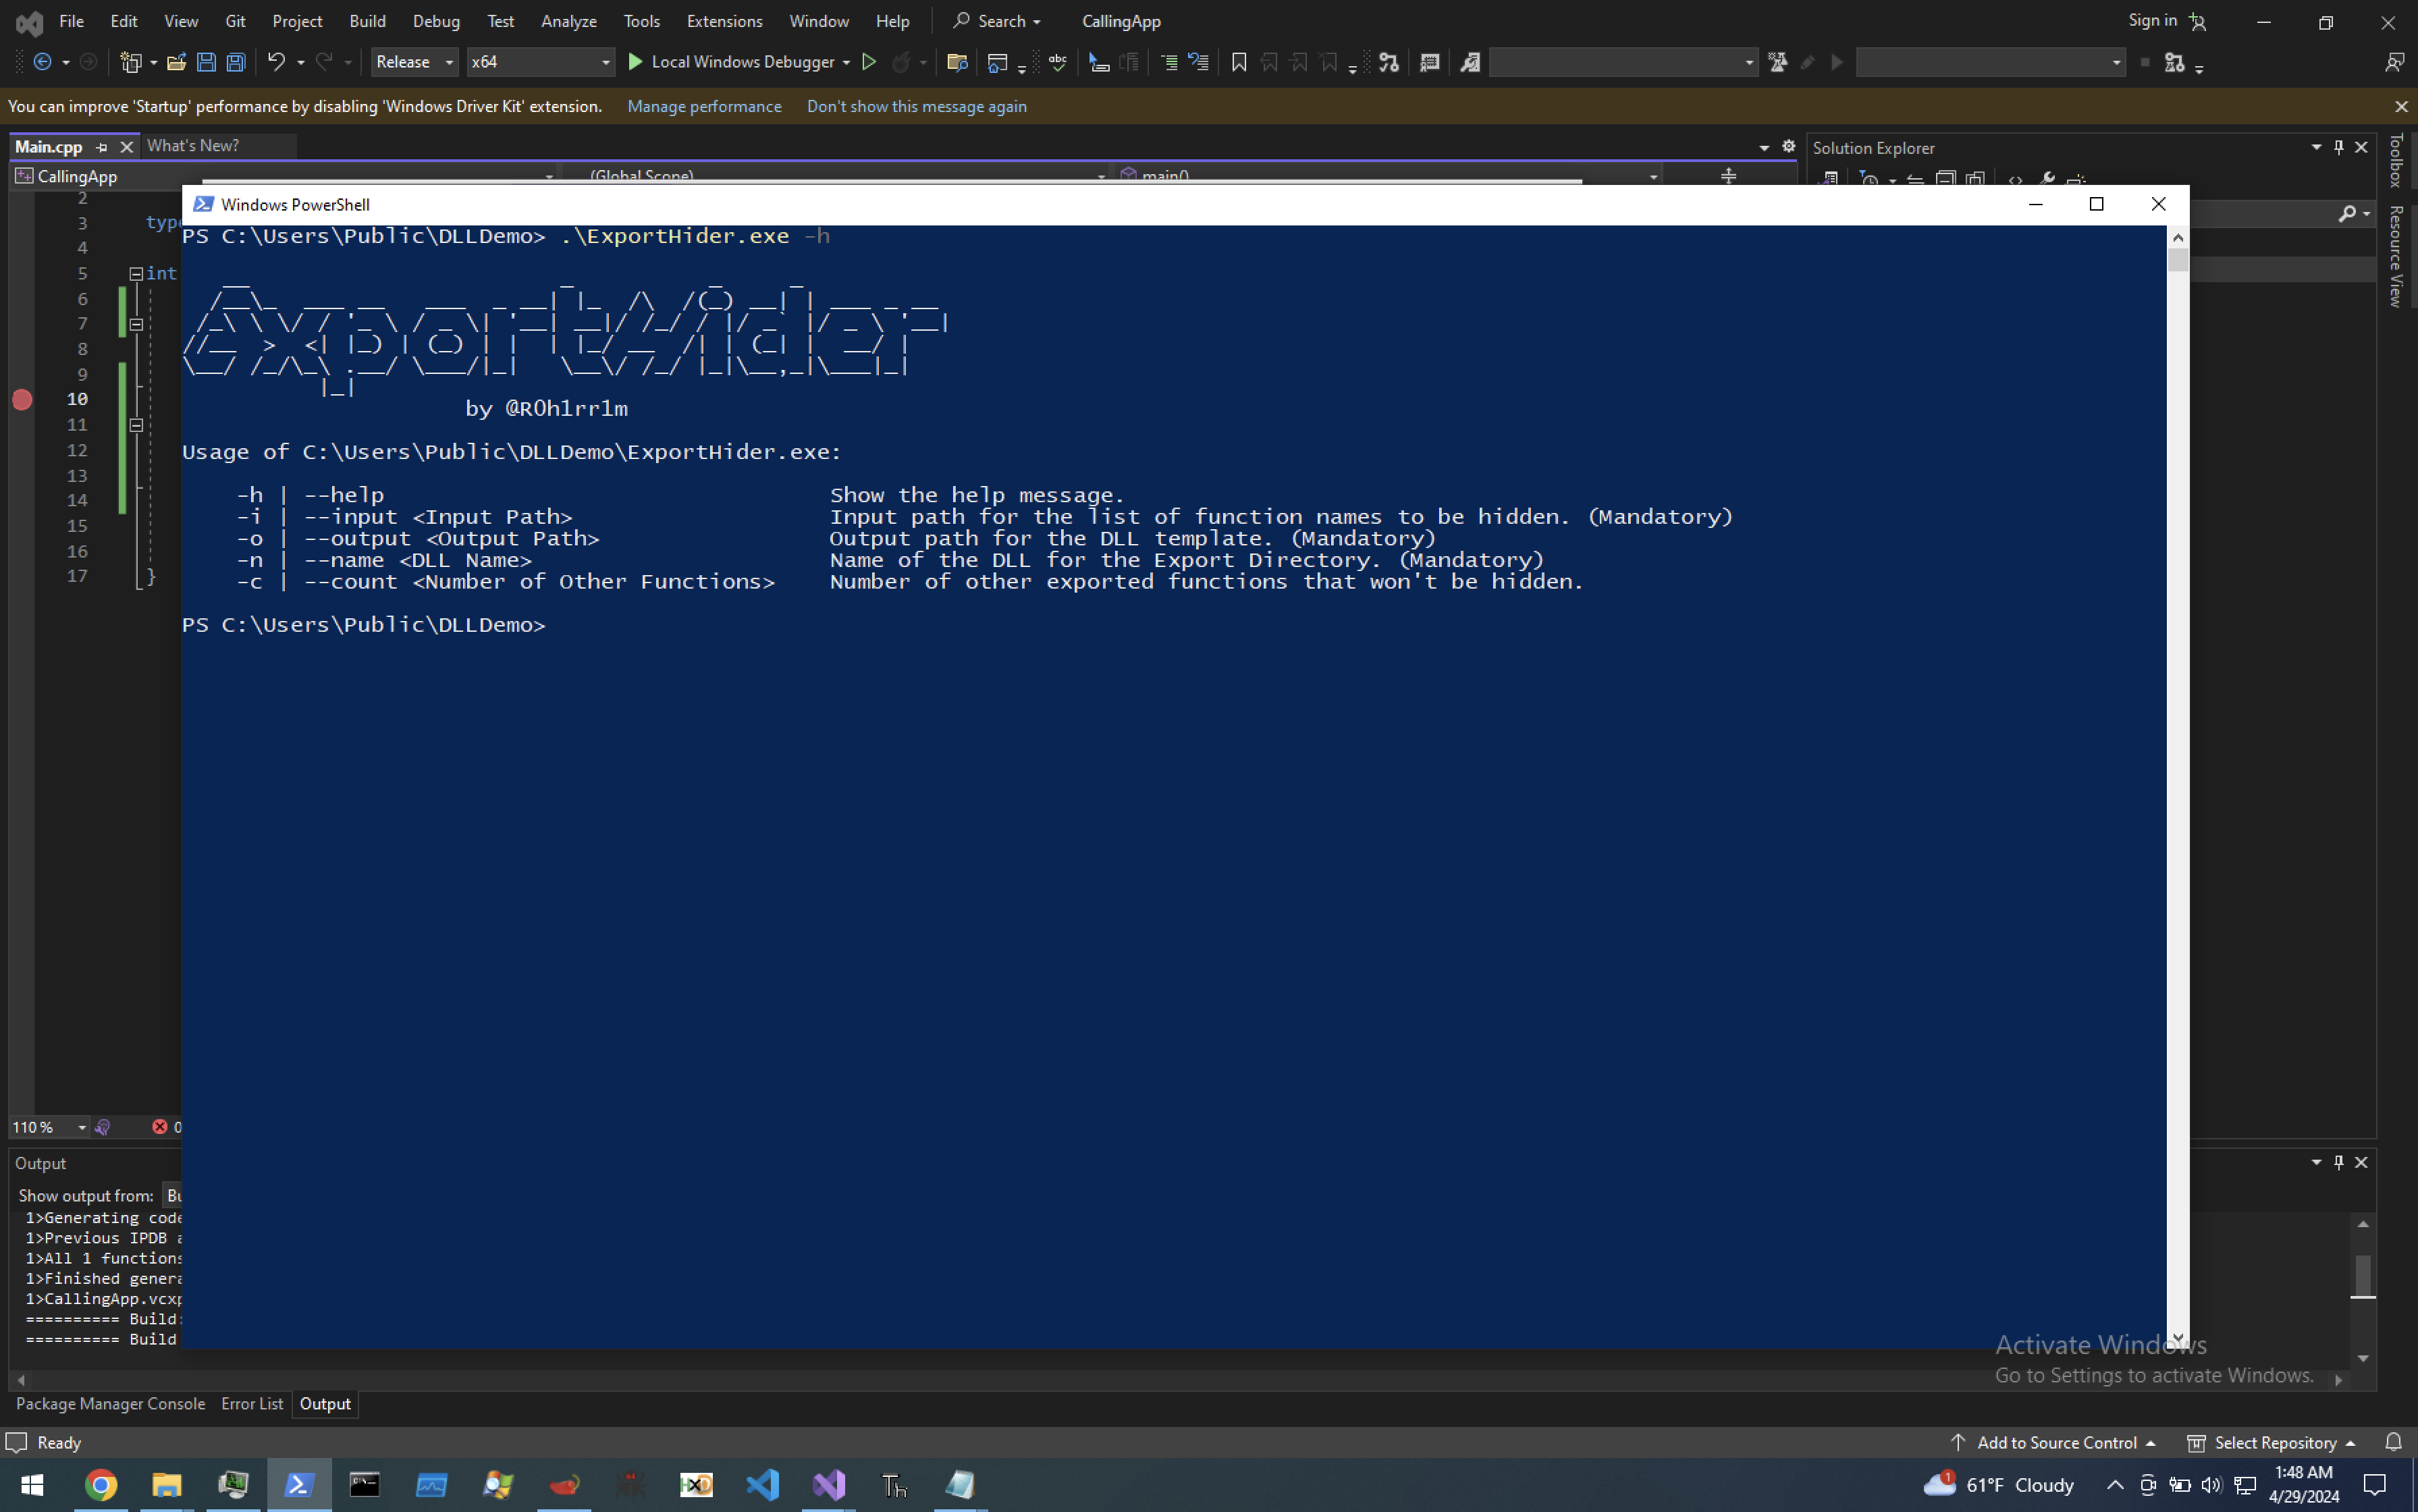 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
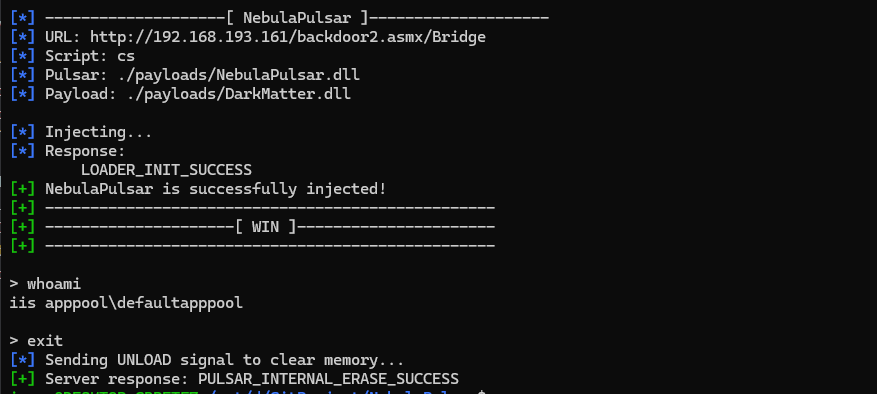 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…