
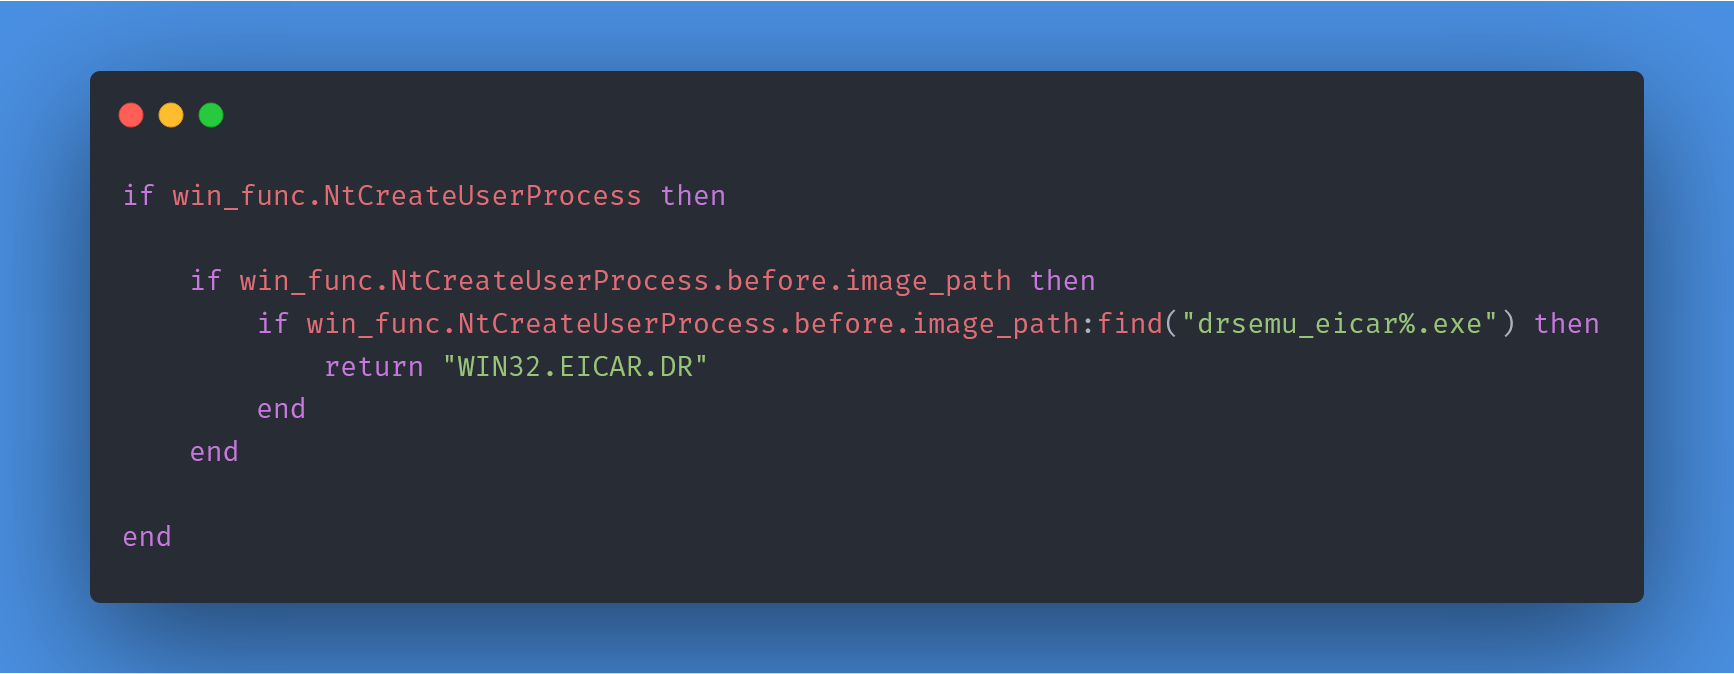
DrSemu
 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2807 years ago
secrary/drsemuDrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 0x534a/dynmx
Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
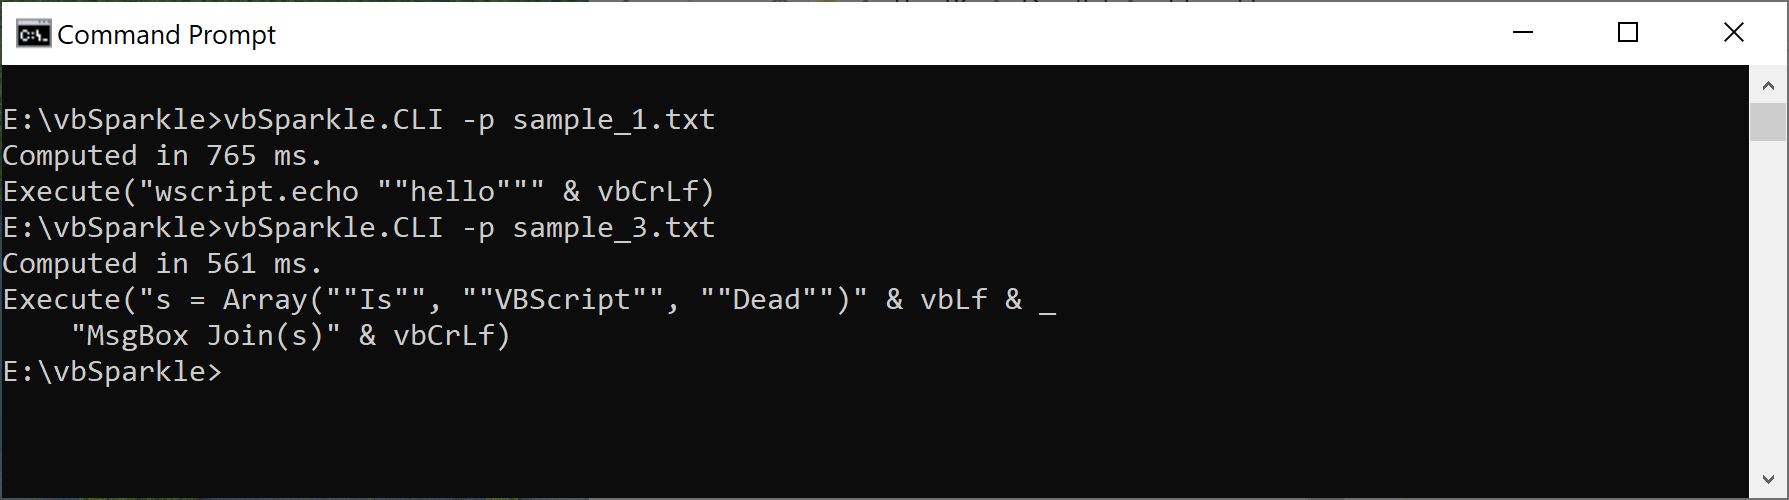 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
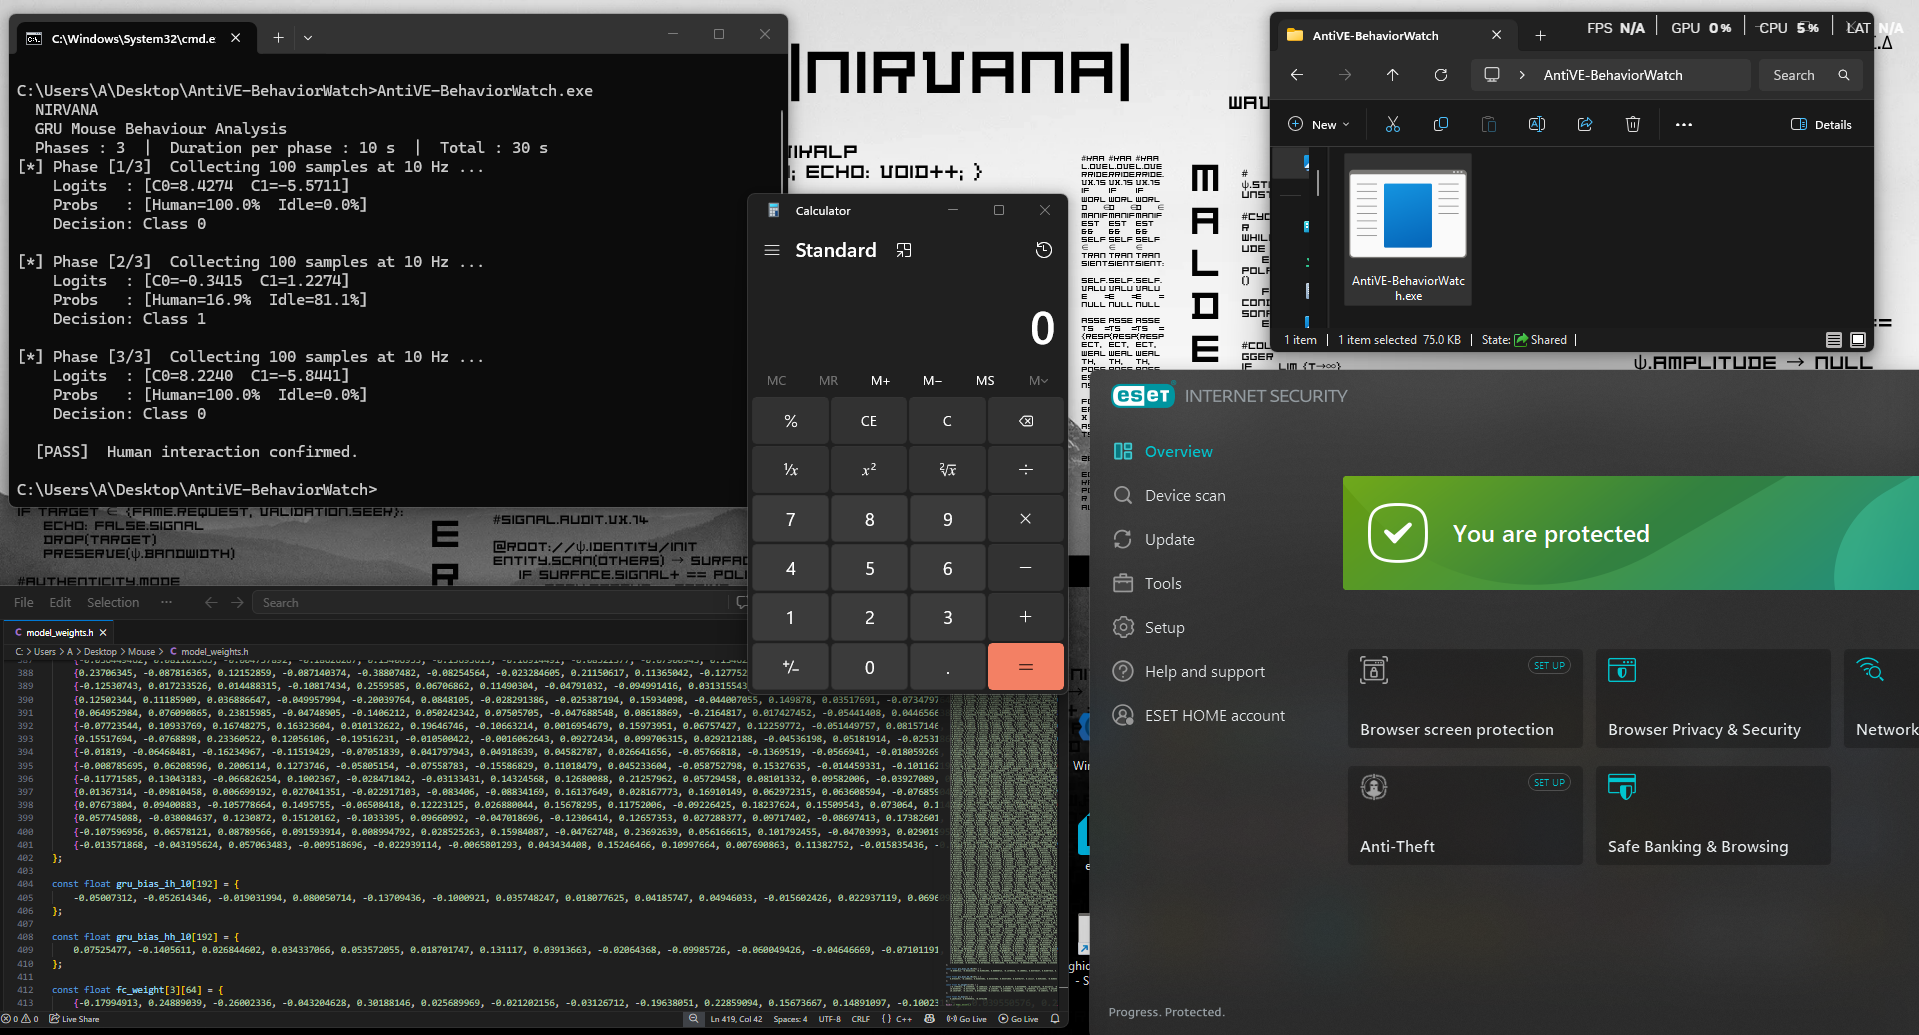 nirvanaon/antive-behaviorwatch
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
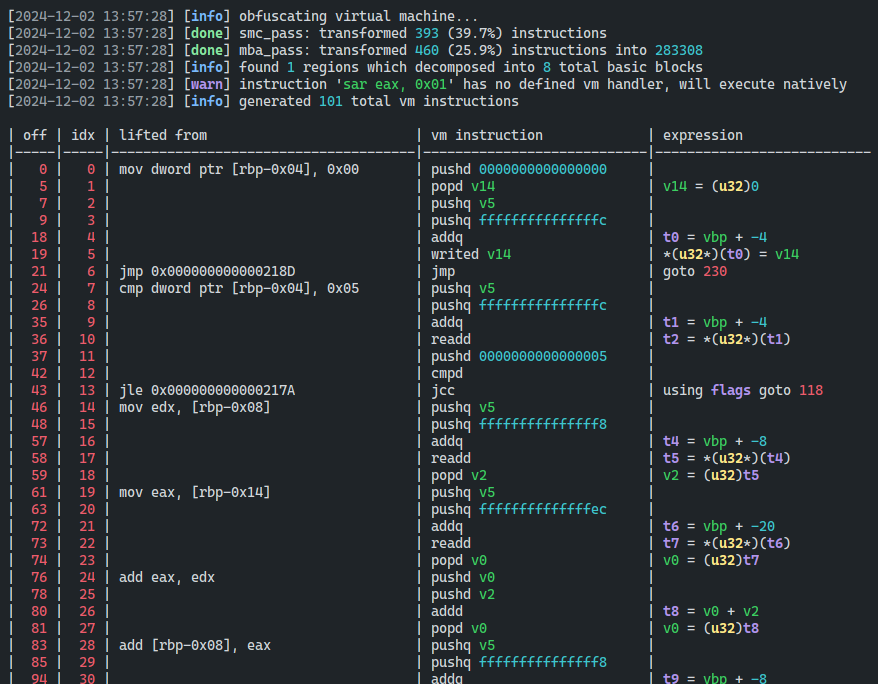 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
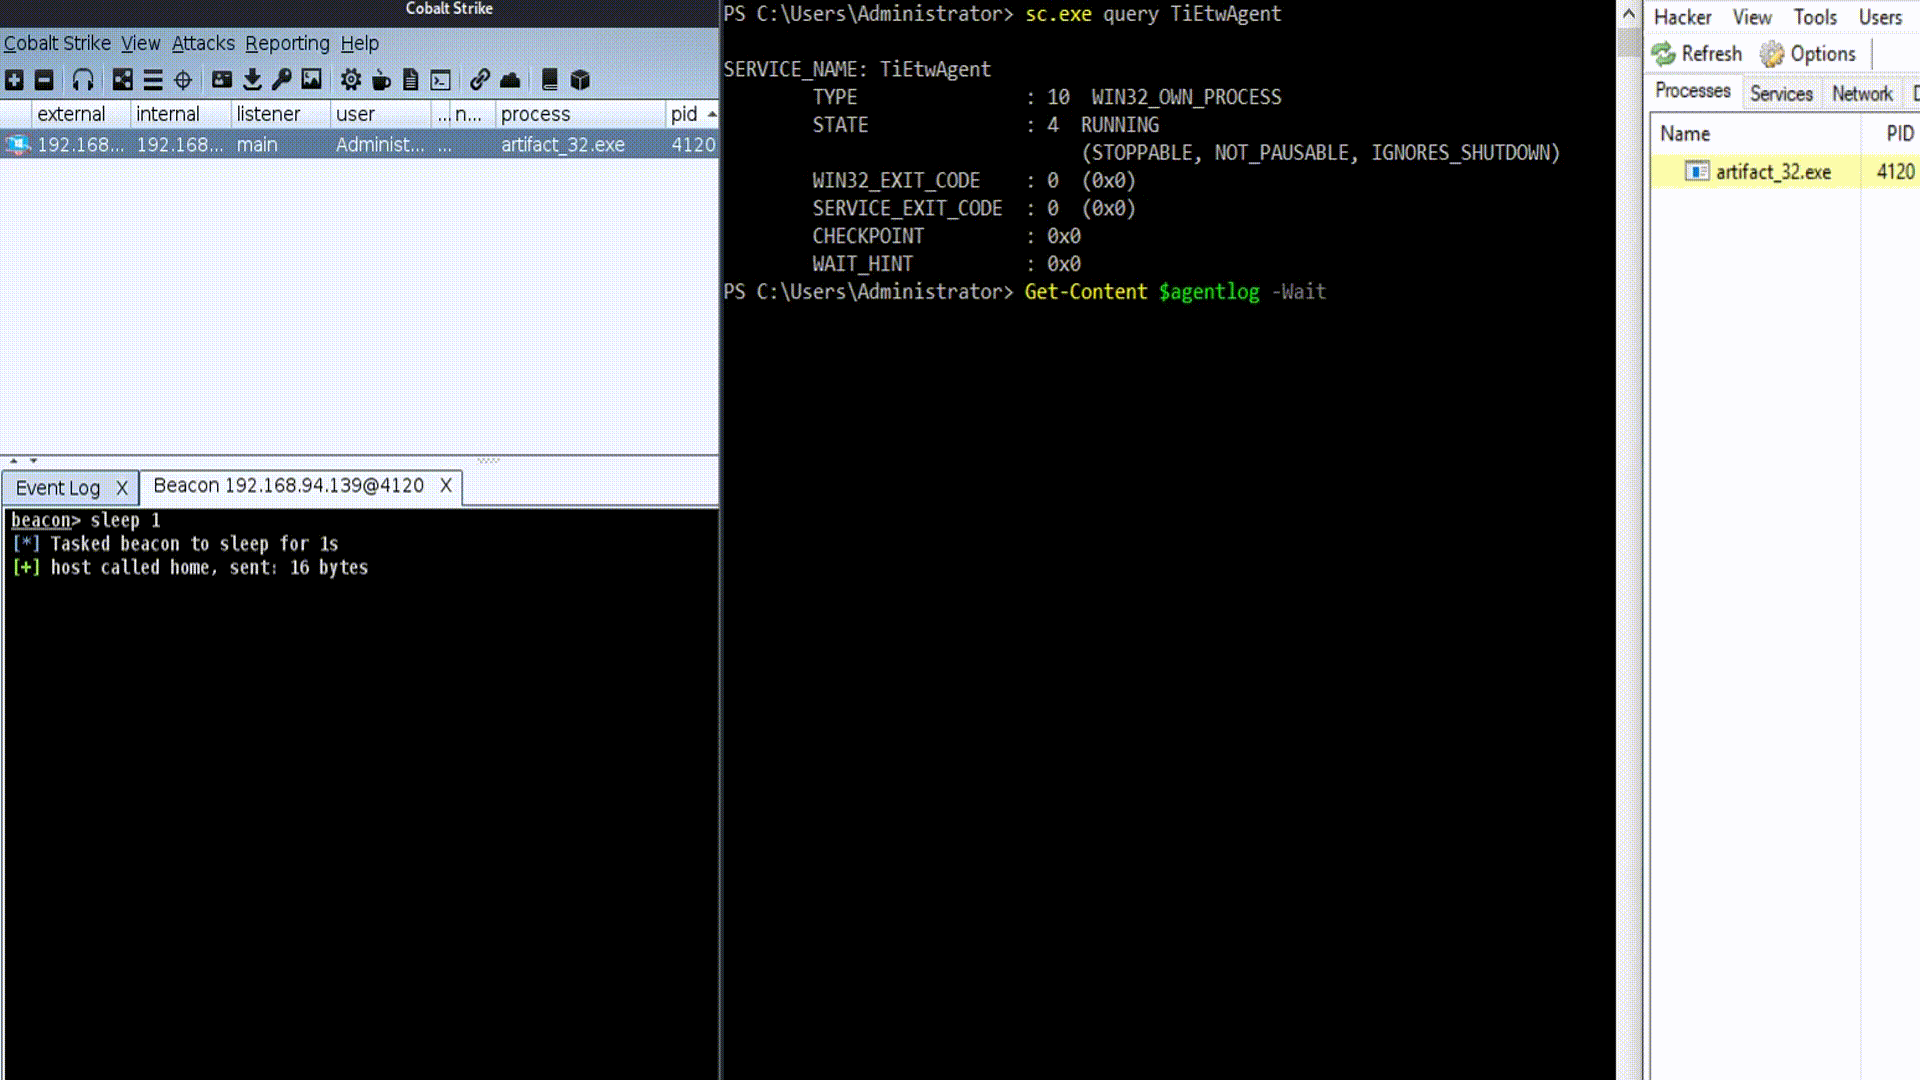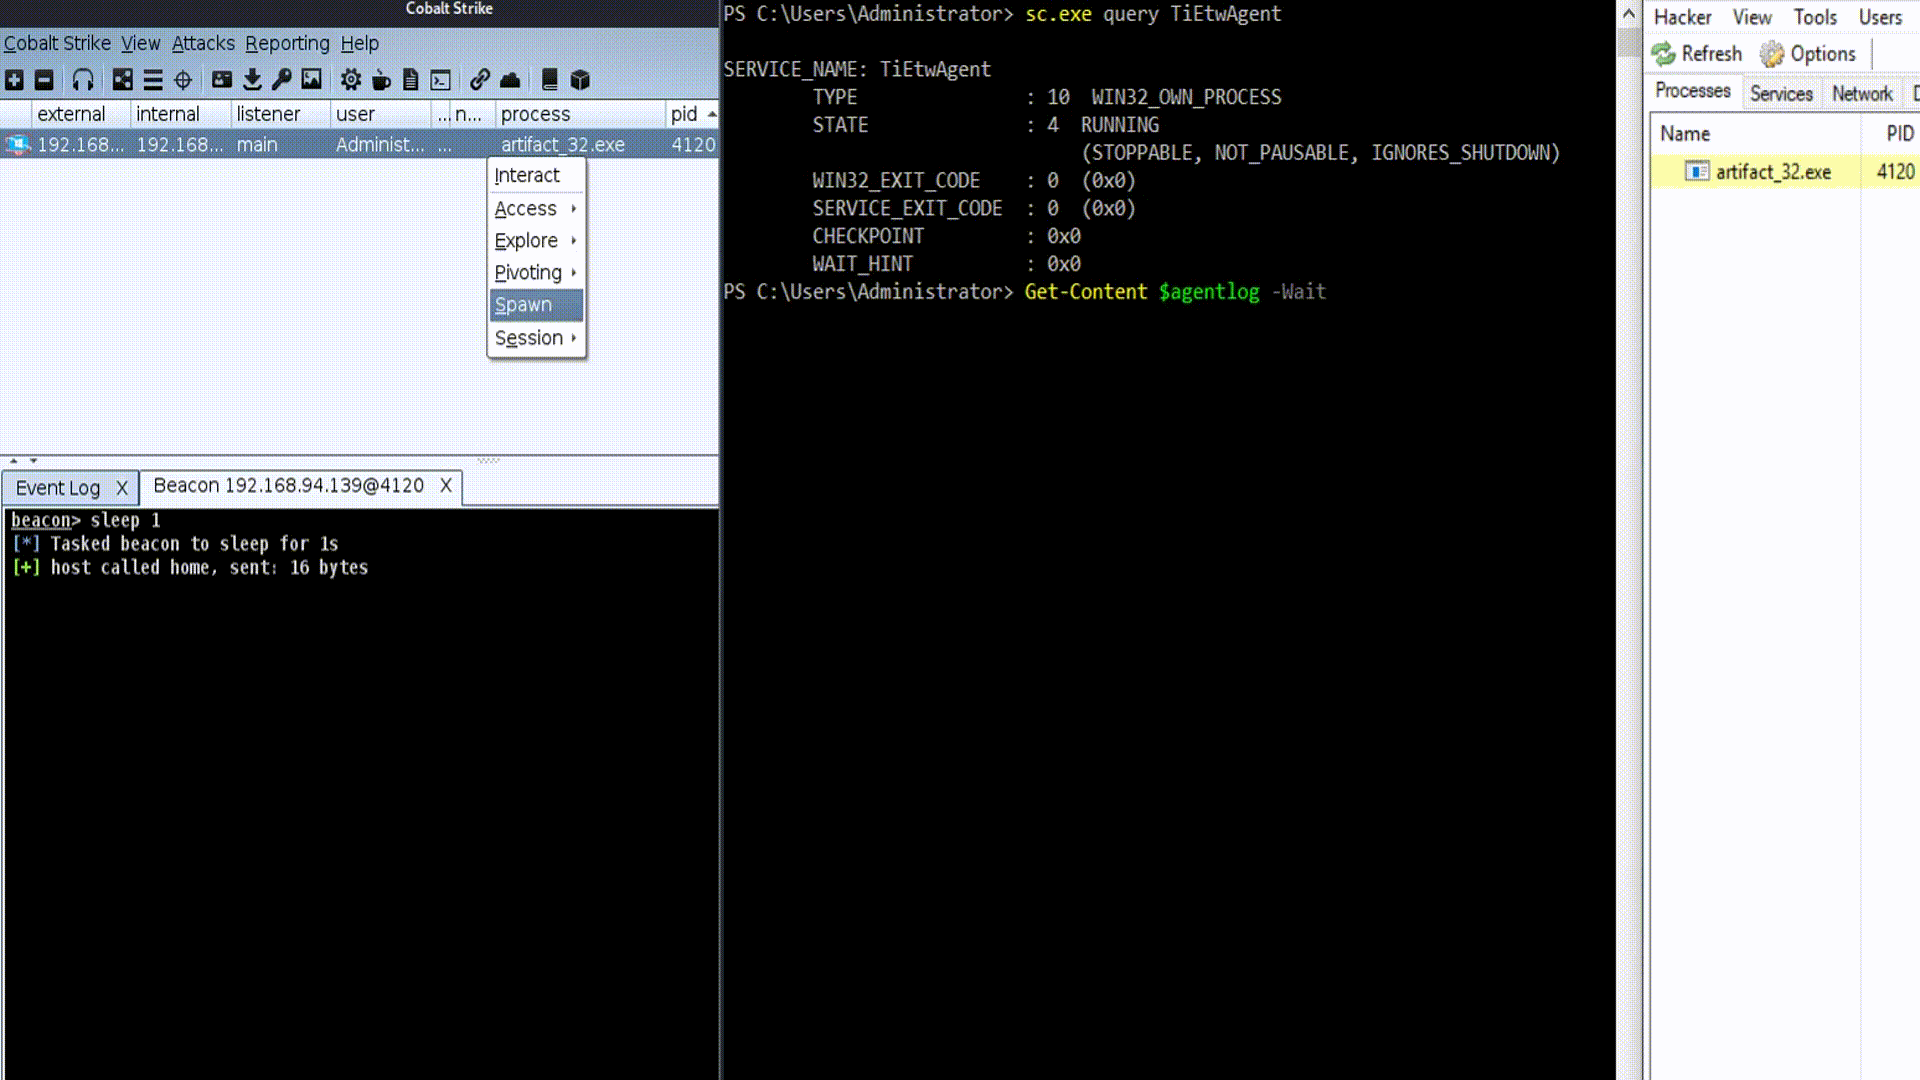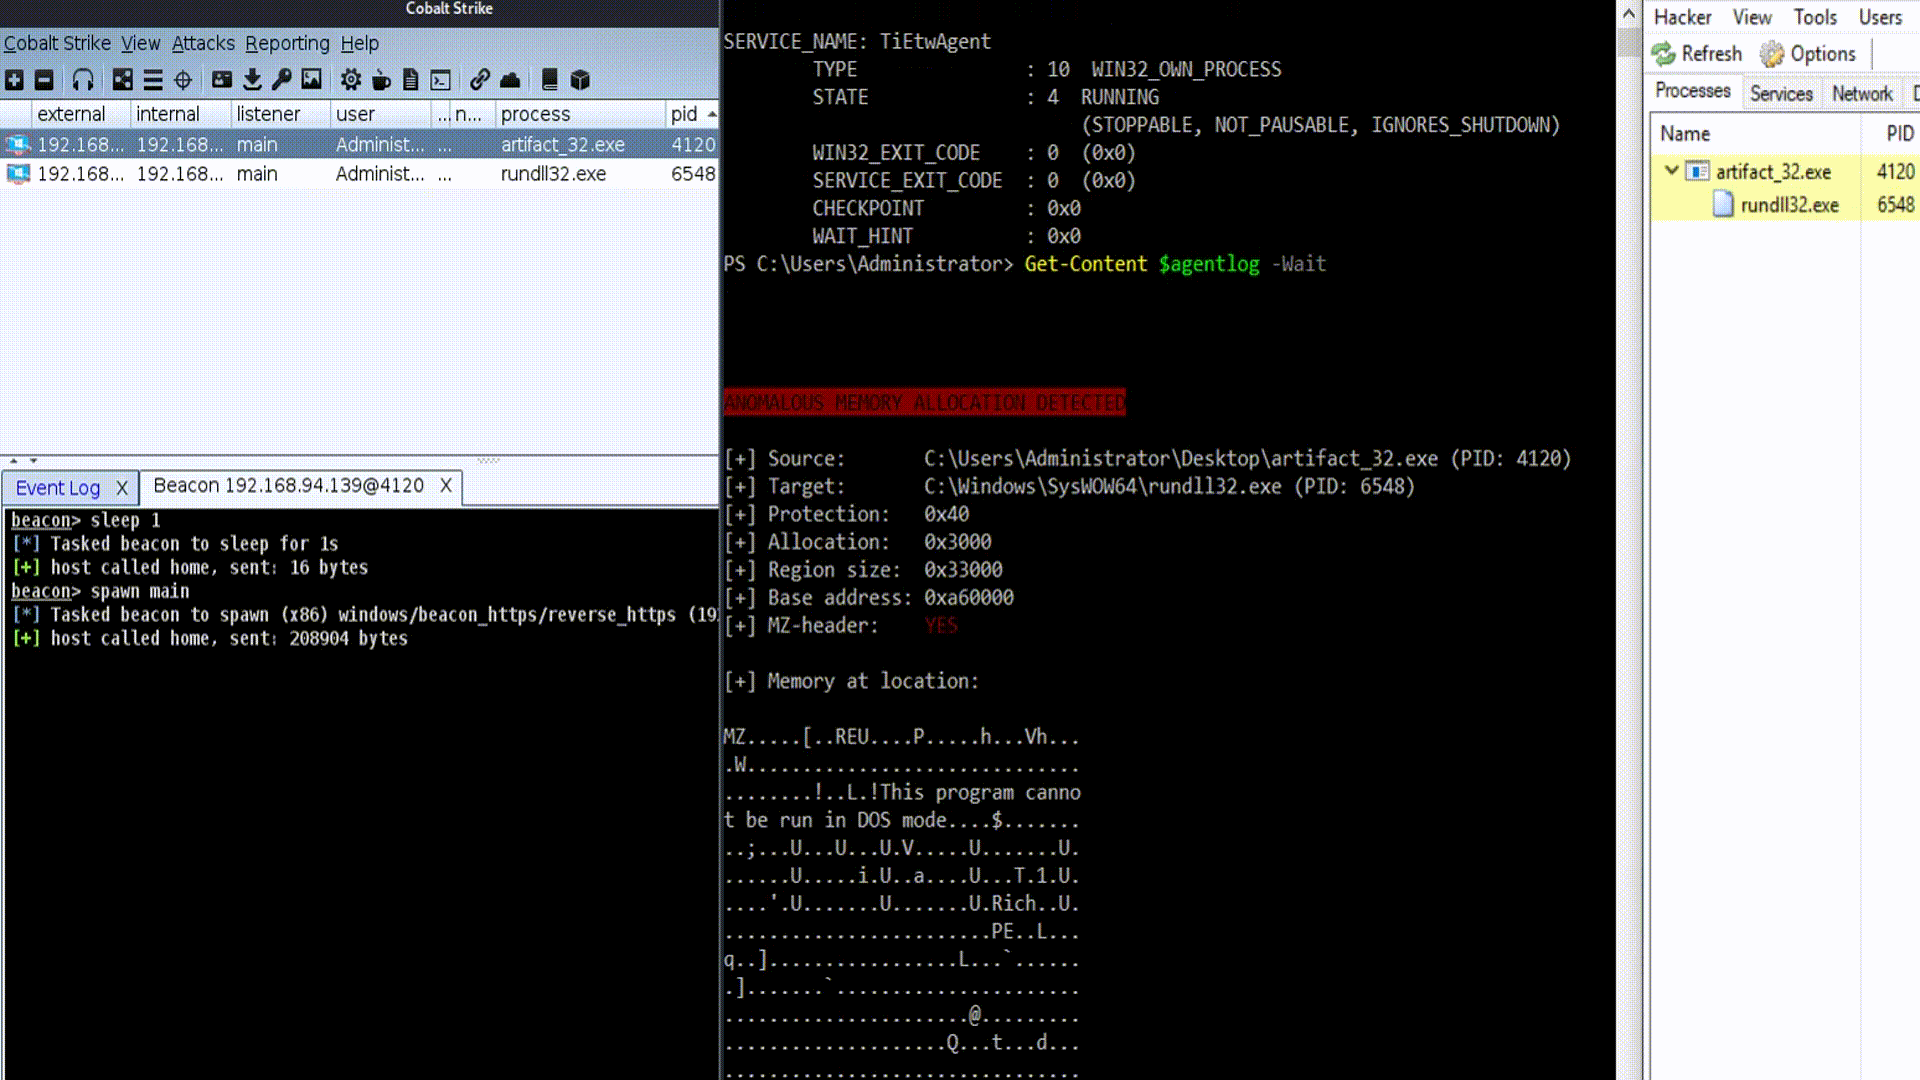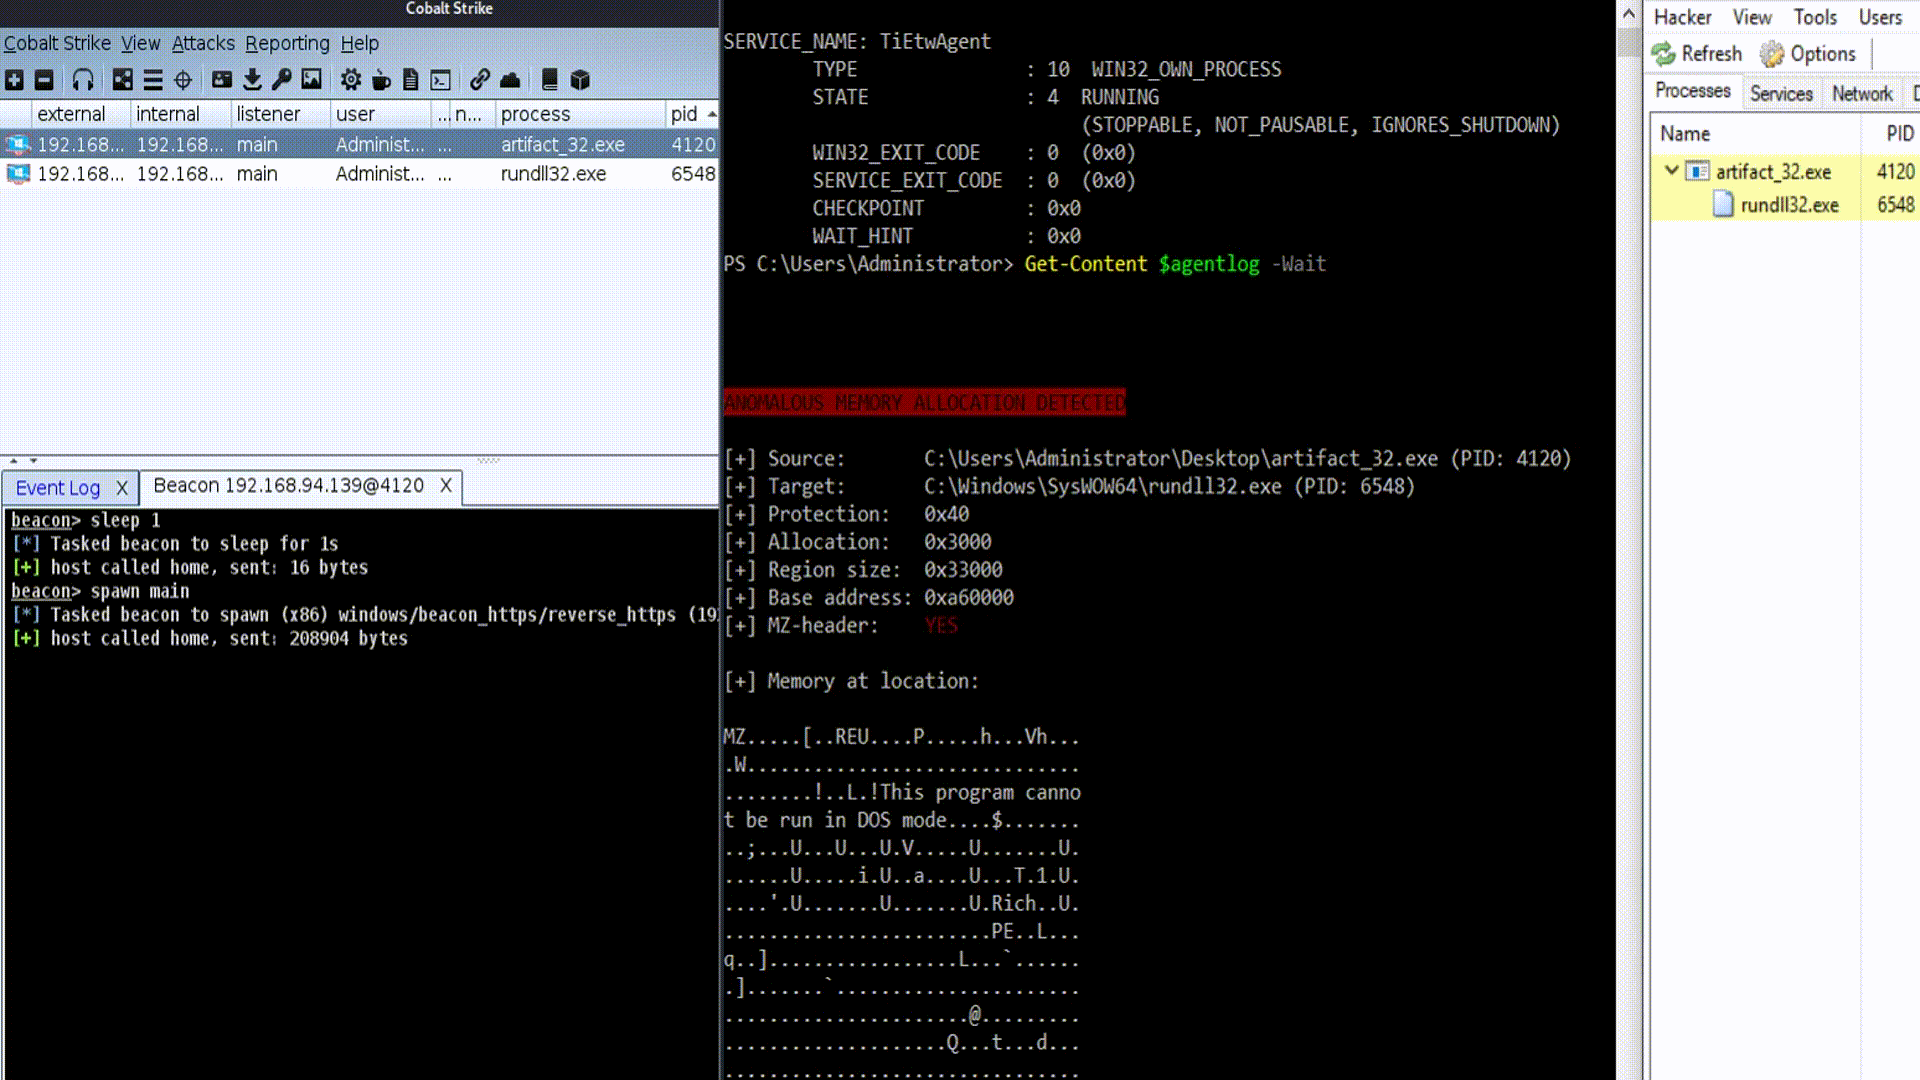 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 gmh5225/ntstrace
frida-stalker based system call tracer on windows(x64).
 lockedbyte/cve-2021-40444
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…