
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
9 results
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k
1 day ago
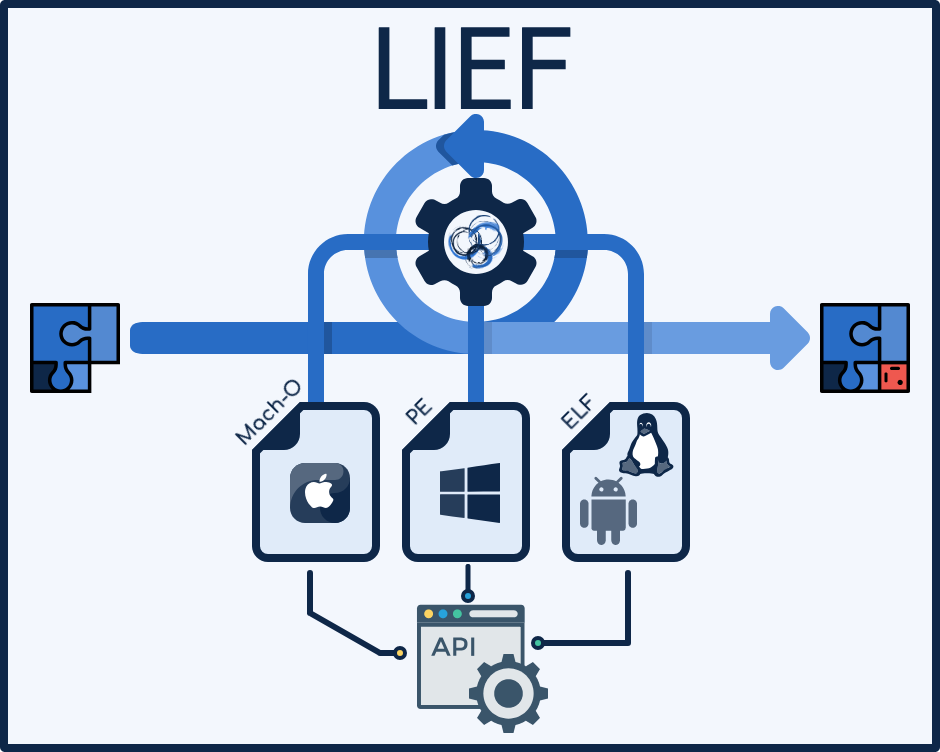
LIEF preview

LIEF

GitHublief-project/lief

Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k13 days ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
data-exfiltrationdigital-forensicsforensics+5
139 years ago
r2gopclntabParser preview

r2gopclntabParser

GitHubasherdll/r2gopclntabparser

A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.

binary-analysisdebuggersforensics+3
175 months ago
pyOneNote preview

pyOneNote

GitHubdissectmalware/pyonenote

A python library to parse OneNote (.one) files

digital-forensicsmalware-analysisstatic-analysis
1532 years ago
amcache-evilhunter preview

amcache-evilhunter

GitHubcristianzsh/amcache-evilhunter

Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
digital-forensicsforensicsincident-response+2
1141 year ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files
binary-analysisforensicsmalware-analysis+2
997 months ago
asclepius preview

asclepius

GitHubmatank001/asclepius

Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…

data-recoveryforensicsmalware-analysis+2
118 months ago
WhoamiAlternatives preview

WhoamiAlternatives

GitHubricardojoserf/whoamialternatives

Different methods to get current username without using whoami

information-gatheringmalware-analysispost-exploitation+2
1872 years ago