

ImHex
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
55.0k1 day ago
werwolv/imhex🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
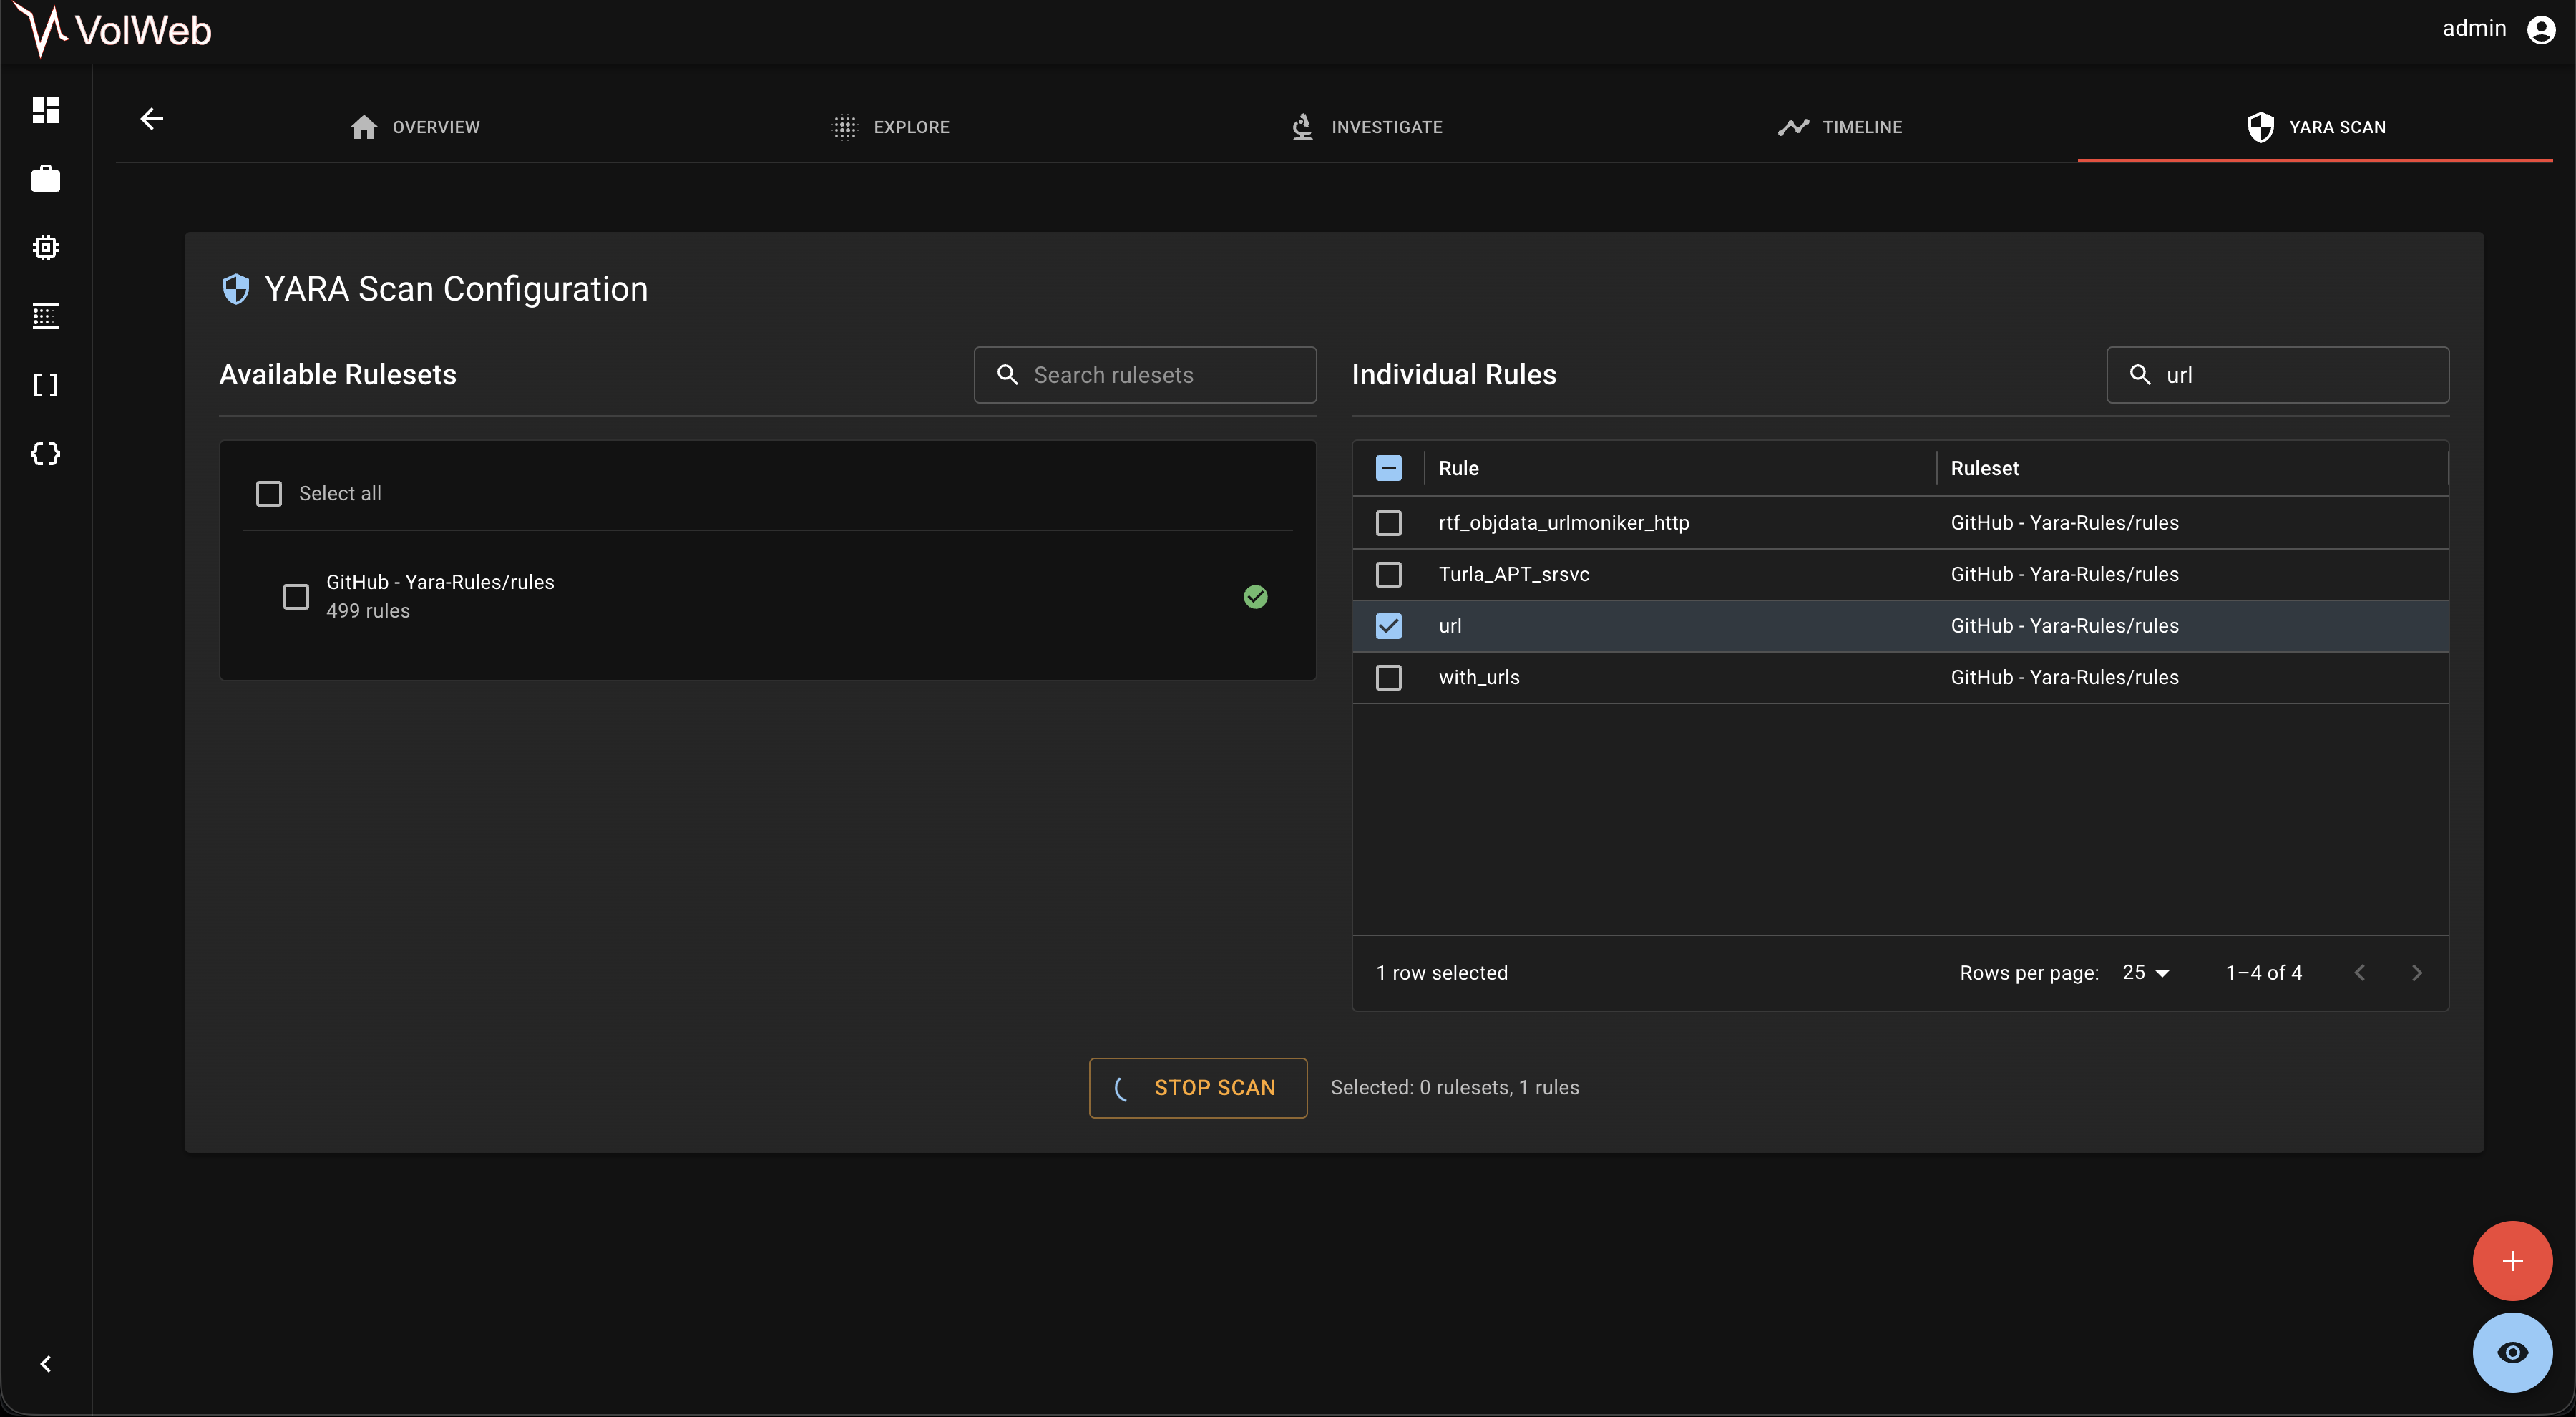 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 m10ust/machscope
macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content

 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 stonelinks/react-cve-2025-55182
Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints