
yaraast
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
code-analysismalware-analysisscripting-automation+3
54
seifreed/yaraastA powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
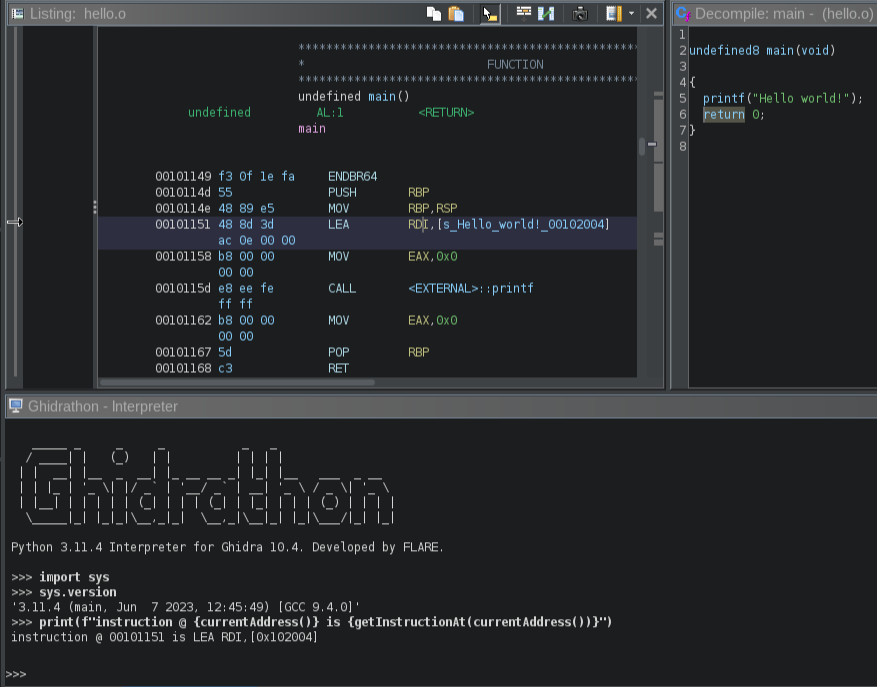 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 kaysec/hybrid-submit
A script that automatically submits files to Hybrid Analysis (API)
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
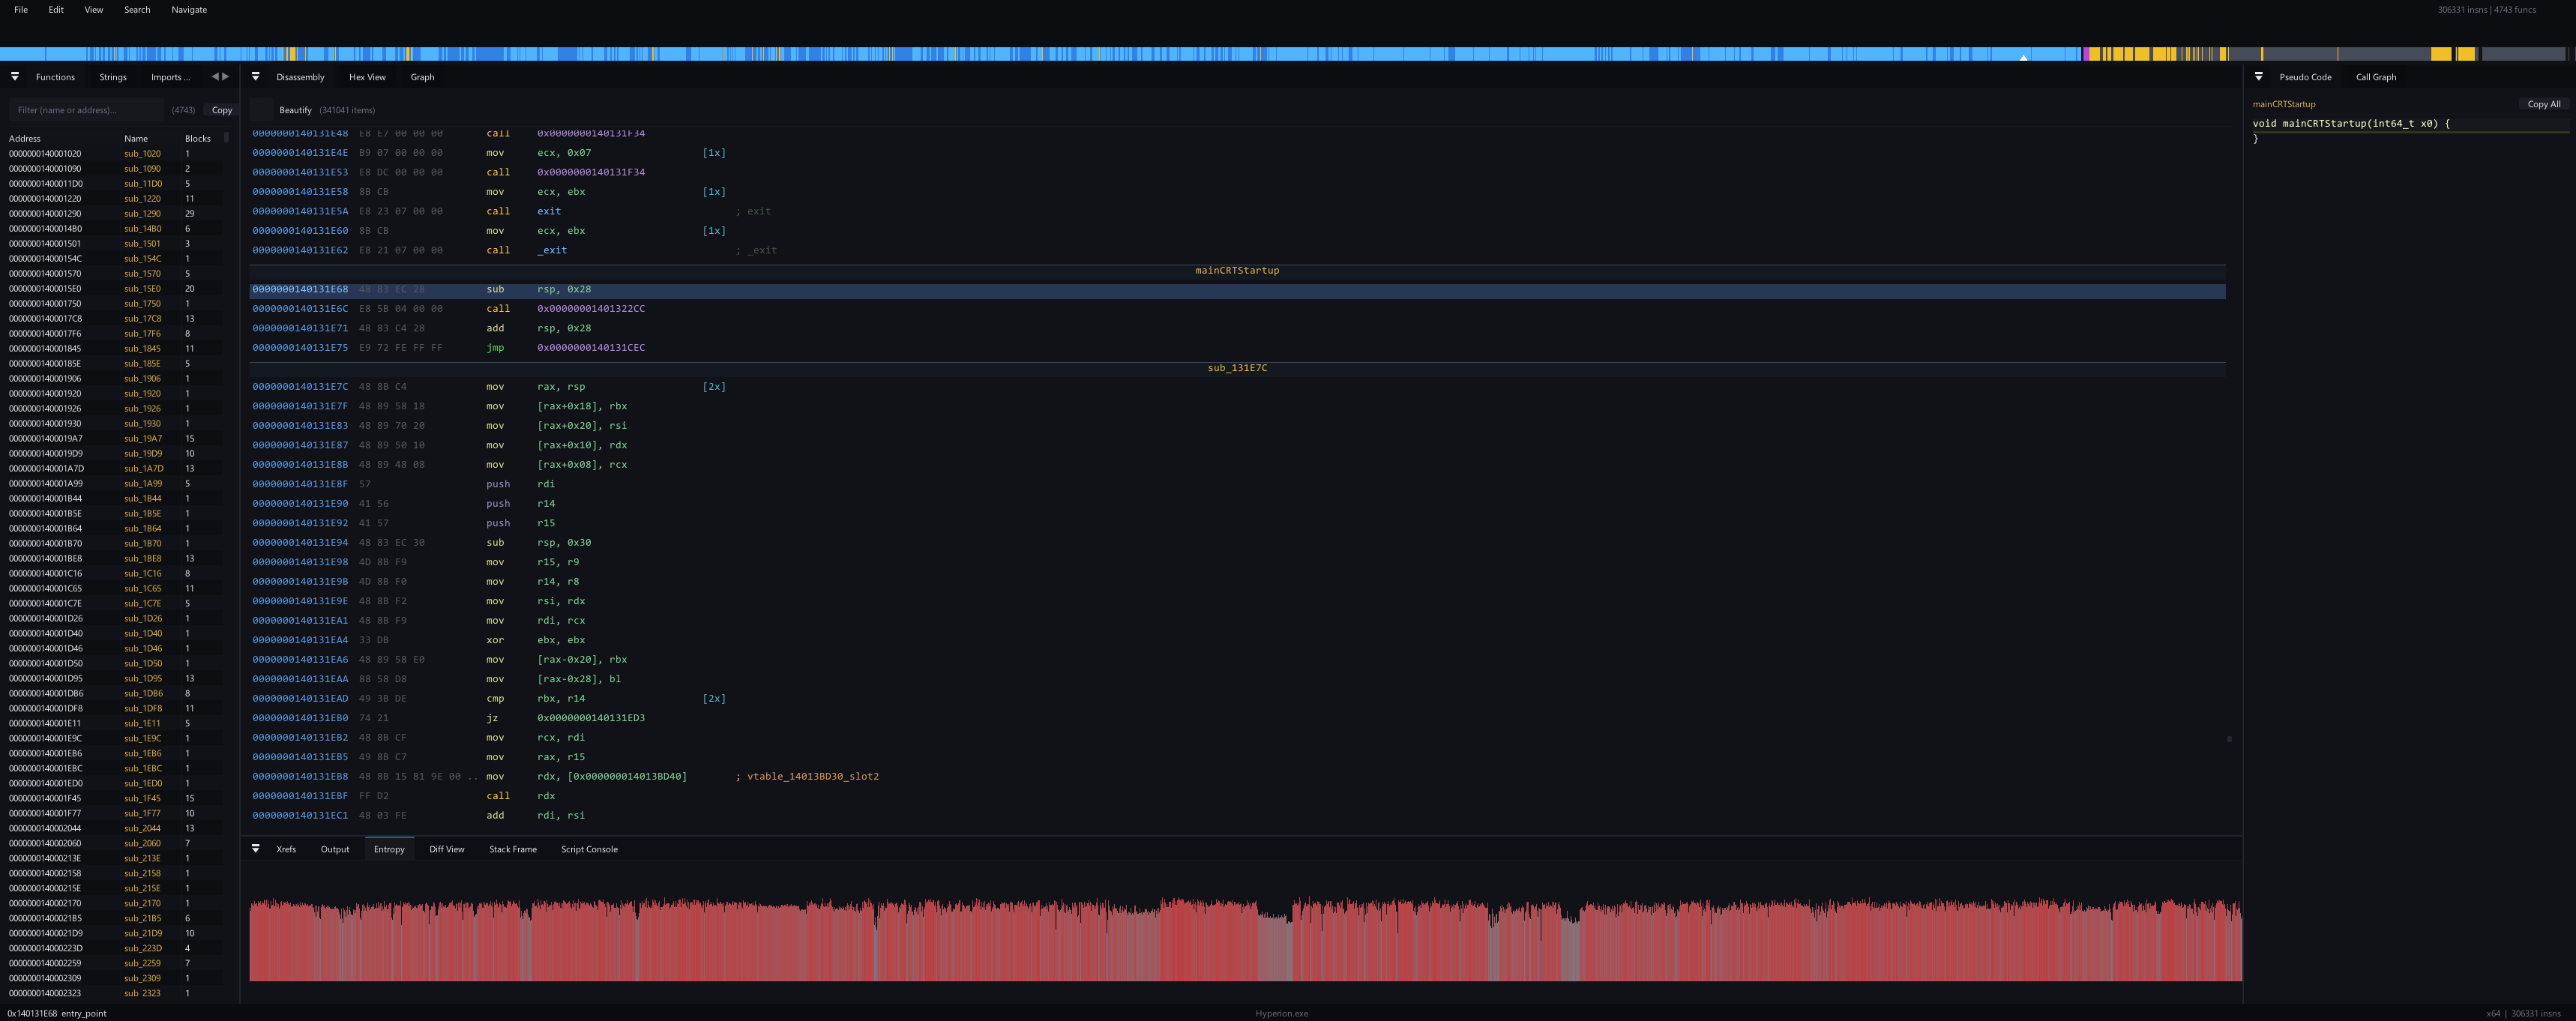 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery