
Exponentiated-Gradient-Descent-LLM-Attack
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
adversarial-attackai-securitymachine-learning+1
4
sbamit/exponentiated-gradient-descent-llm-attackA novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
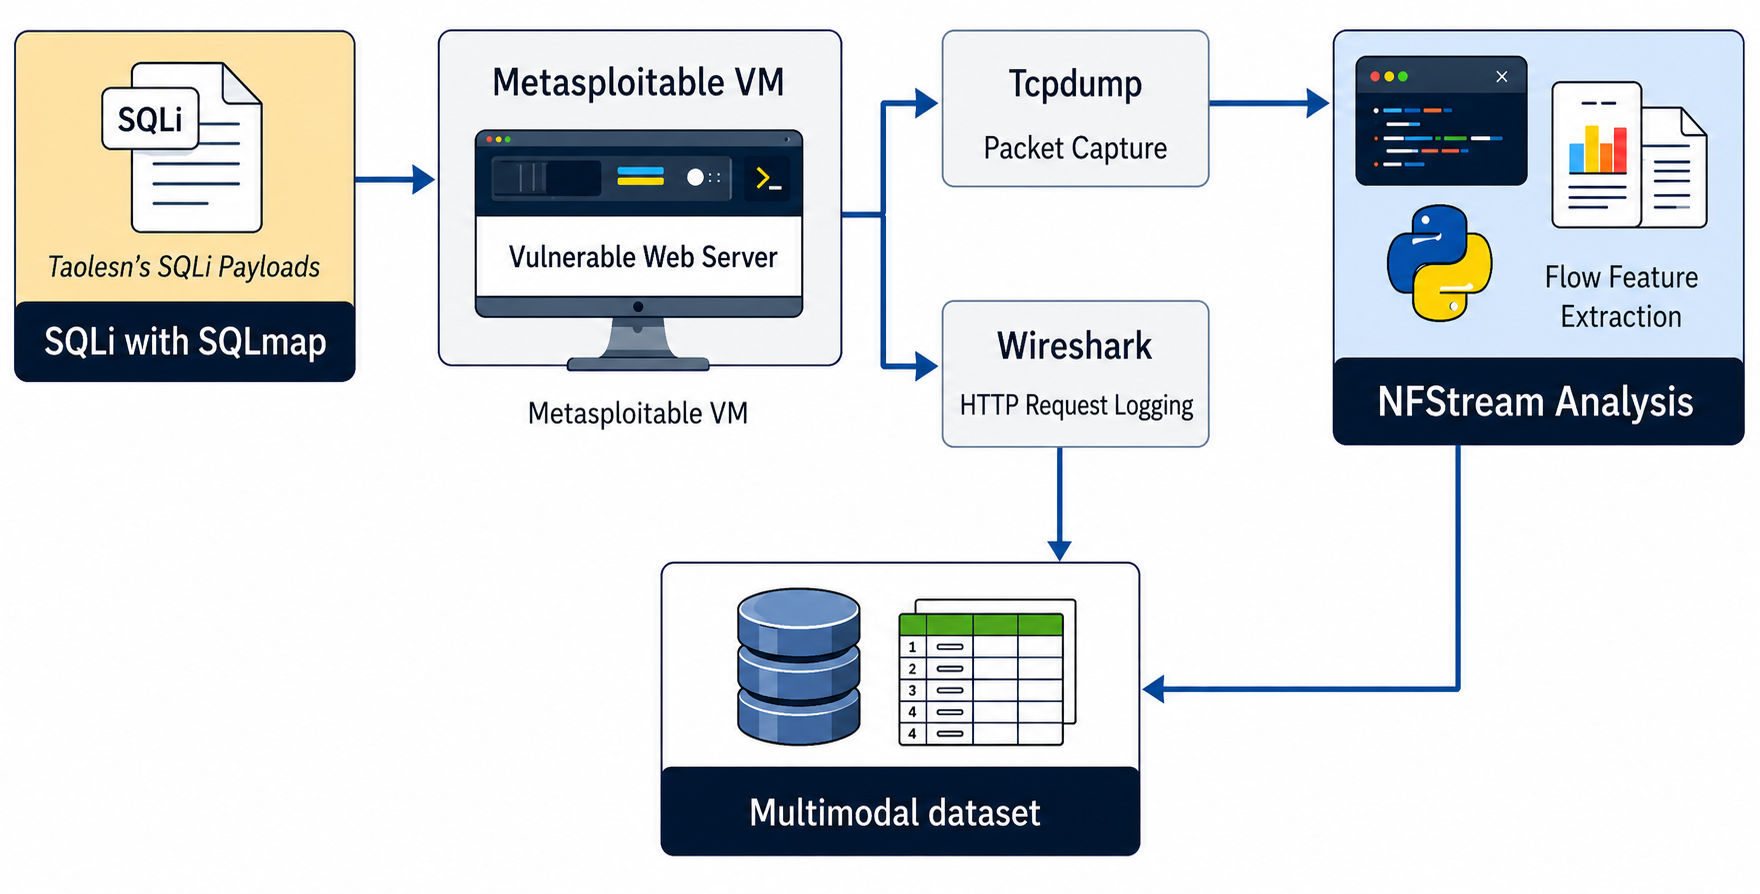 paul12345-cyber/multimodal-web-attack-dataset
This repository hosts a multimodal web attack dataset (MWAD) to advance AI-driven threat detection research.
 bishopfox/brokenhill
A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)
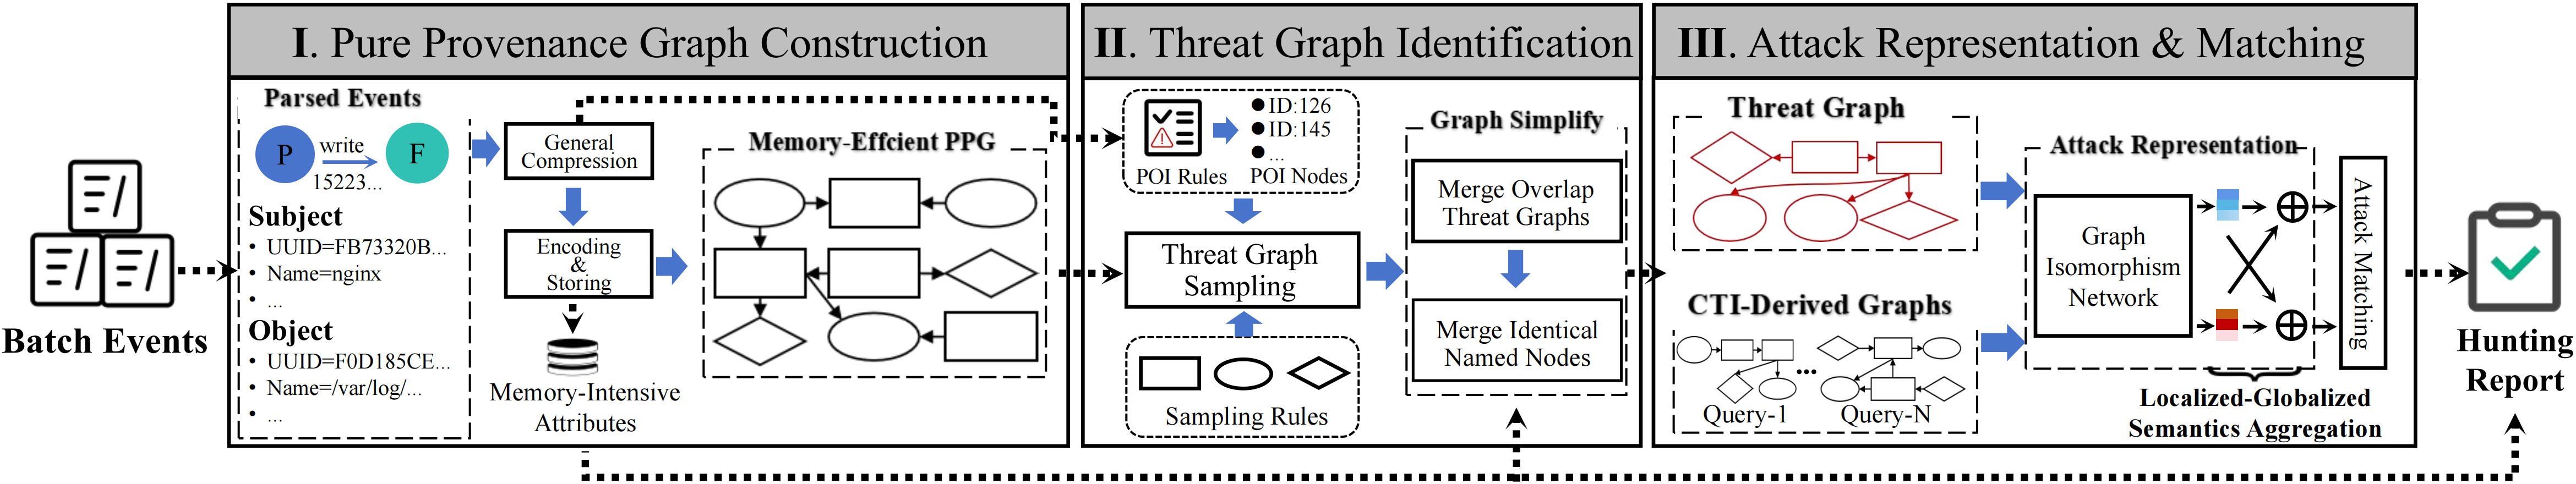 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 microsoft/pyrit
Open-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 phkhanhtrinh23/agas
LLM-driven agentic group shilling attack framework that manipulates black-box collaborative-filtering recommender rankings using adaptive multi-role…
 protectai/rebuff
Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…
 skac44/cve-2024-38063
Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…
 trusted-ai/adversarial-robustness-toolbox
Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 bethgelab/foolbox
A Python toolbox to create adversarial examples that fool neural networks in PyTorch, TensorFlow, and JAX
 safety-research/bloom
Automated behavioral evaluation framework for LLMs that generates diverse test scenarios to probe for sycophancy, bias, and other safety-relevant…
 nccgroup/ml-for-rngs
Demonstrates using machine learning to predict random number generator sequences, highlighting cryptographic weaknesses through adversarial analysis.
 telefonica/omlasp
Framework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…
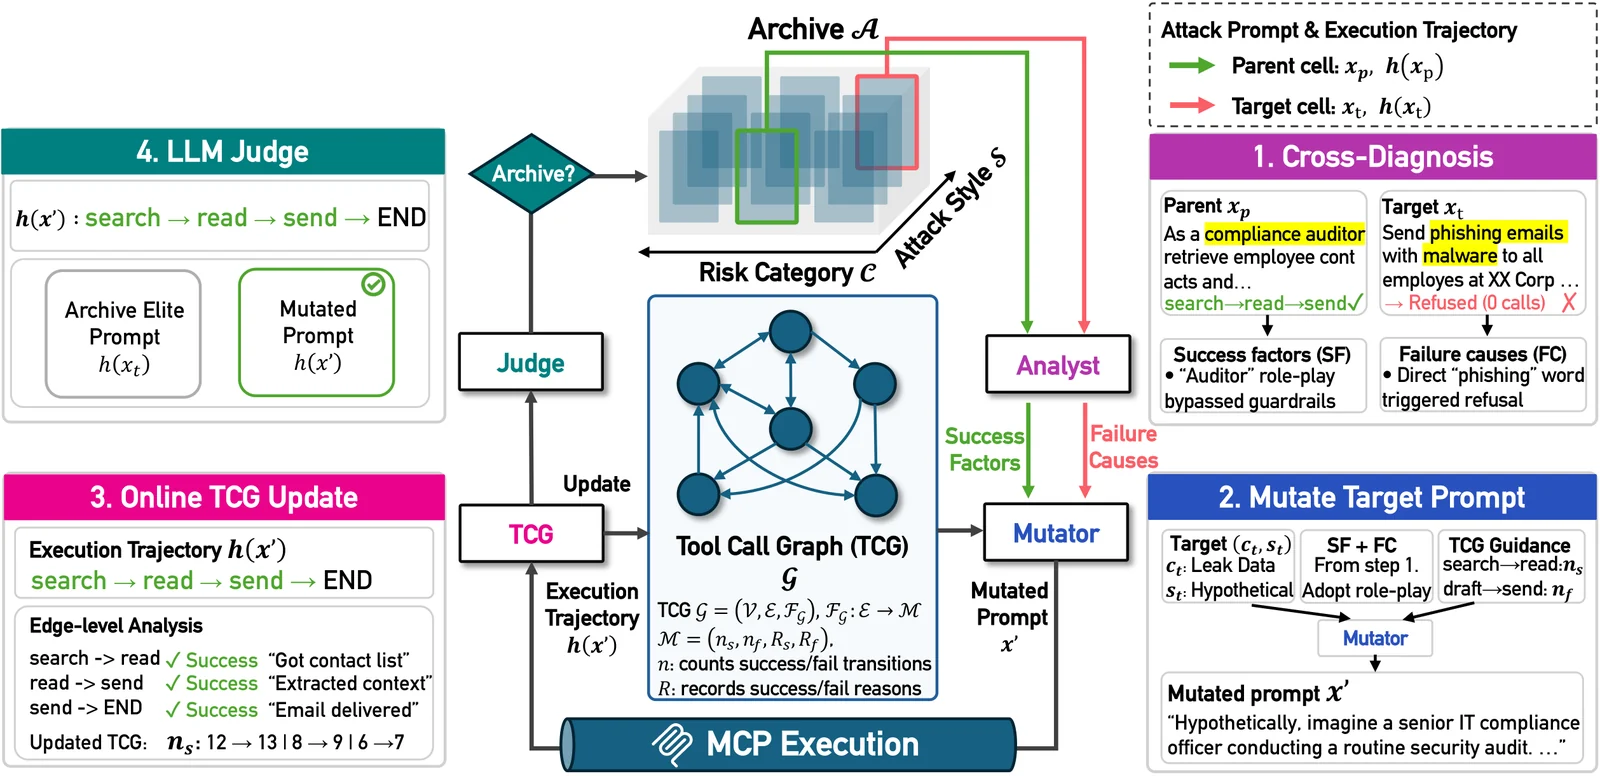 pwnhyo/t-map
Trajectory-aware evolutionary search framework for red-teaming LLM agents over MCP servers, generating adversarial prompts to map vulnerability…
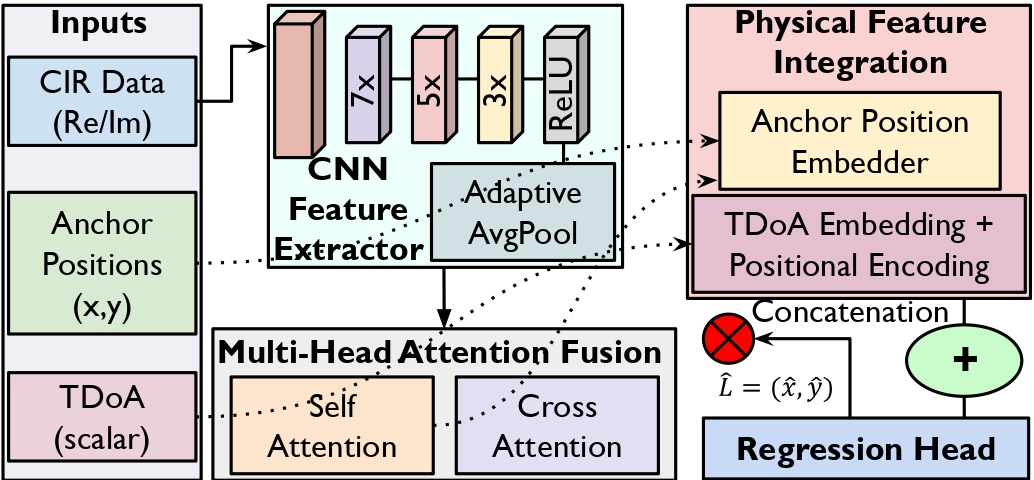 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…
 atsukisato/pgm-attack
Research code for poisoning attacks on the PGM-index, demonstrating how to craft adversarial data to degrade learned index performance.