
Damn-Vulnerable-ML-Model
 owasp/damn-vulnerable-ml-model
Intentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
adversarial-attackai-securityeducation+3
owasp/damn-vulnerable-ml-modelIntentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
 seldonio/alibi-detect
Algorithms for outlier, adversarial and drift detection
 trusted-ai/adversarial-robustness-toolbox
Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…
 cleverhans-lab/cleverhans
An adversarial example library for constructing attacks, building defenses, and benchmarking both
 bethgelab/foolbox
A Python toolbox to create adversarial examples that fool neural networks in PyTorch, TensorFlow, and JAX
 madrylab/robustness
Train, evaluate, and explore neural networks with built-in adversarial robustness tools, including PGD attacks, adversarial training, and robust…
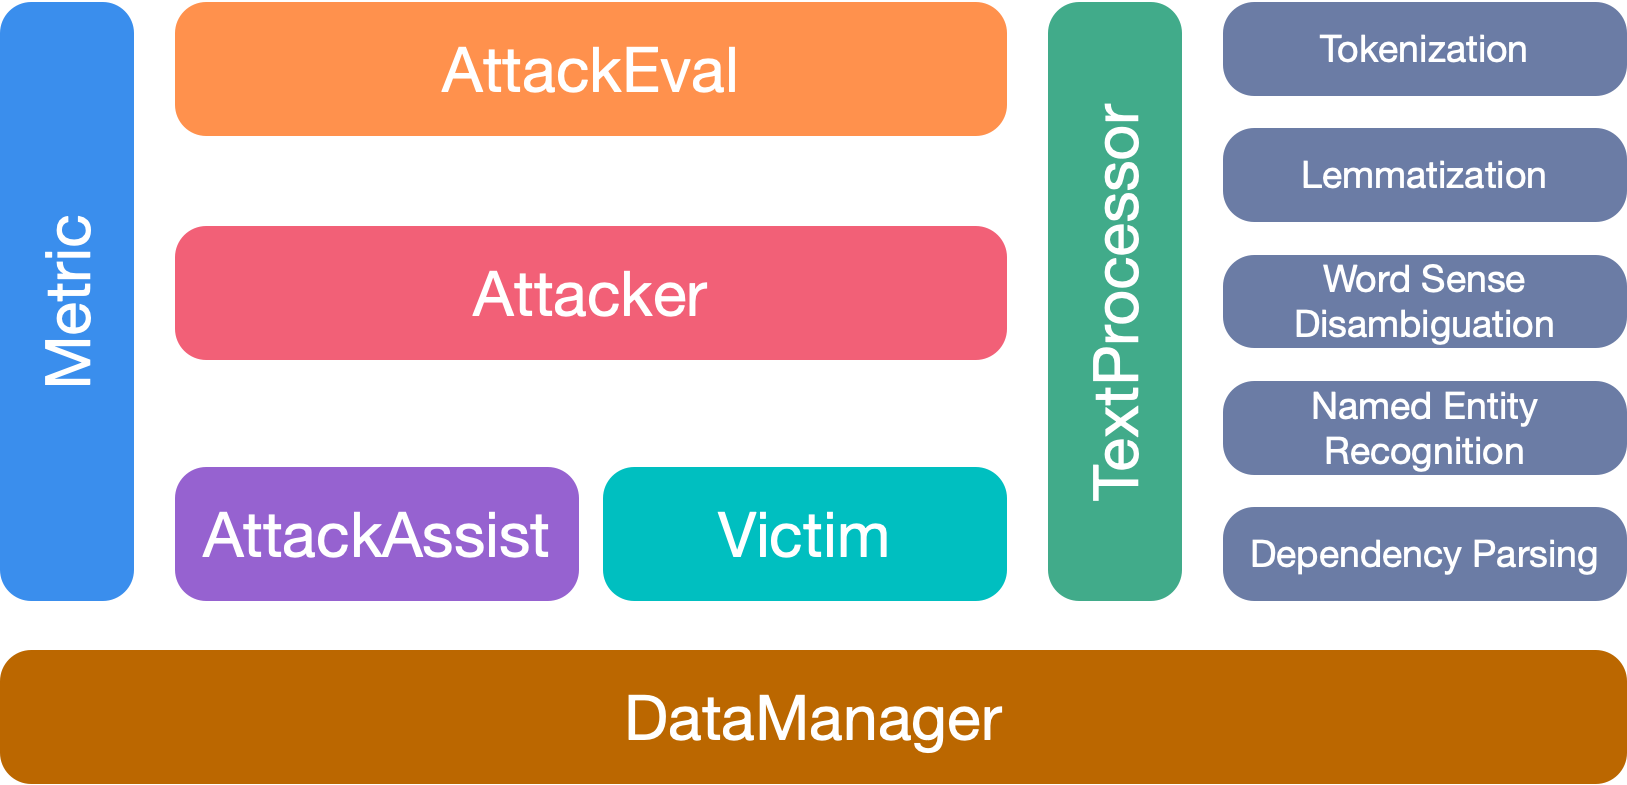 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
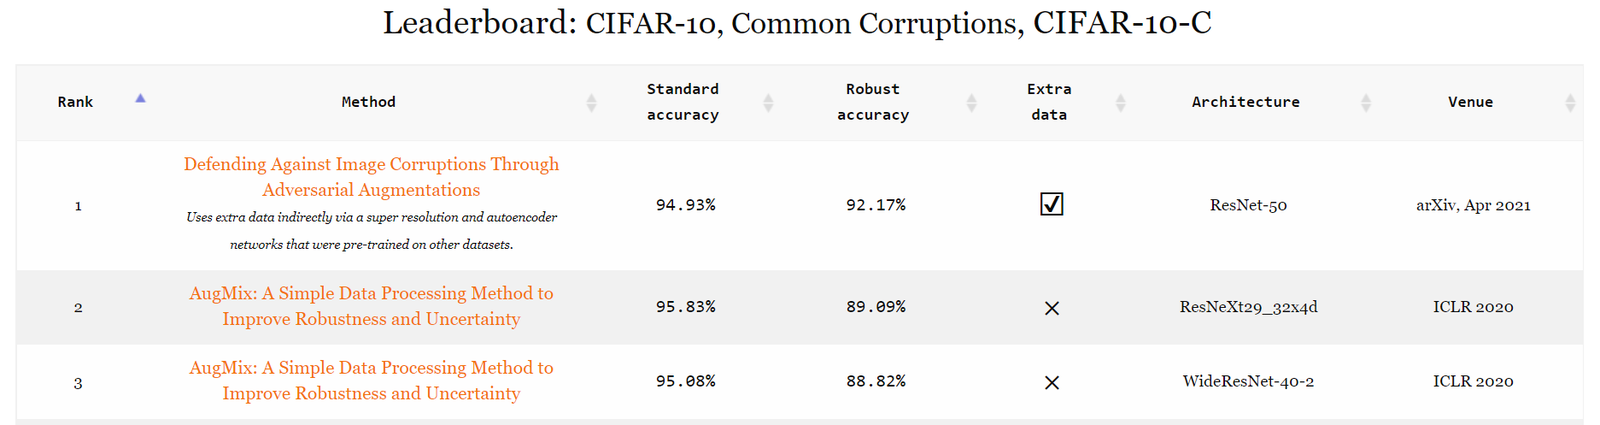 robustbench/robustbench
Standardized adversarial robustness benchmark with a public leaderboard and downloadable model zoo for evaluating ML models against Lp attacks and…
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
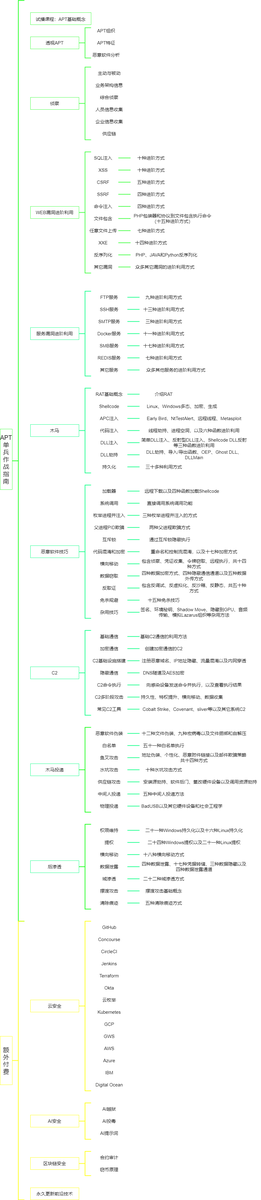 ghostwolflab/ai_security_top
A structured knowledge base covering AI security fundamentals, threat modeling, red team offensive techniques, and blue team defenses, including LLM…
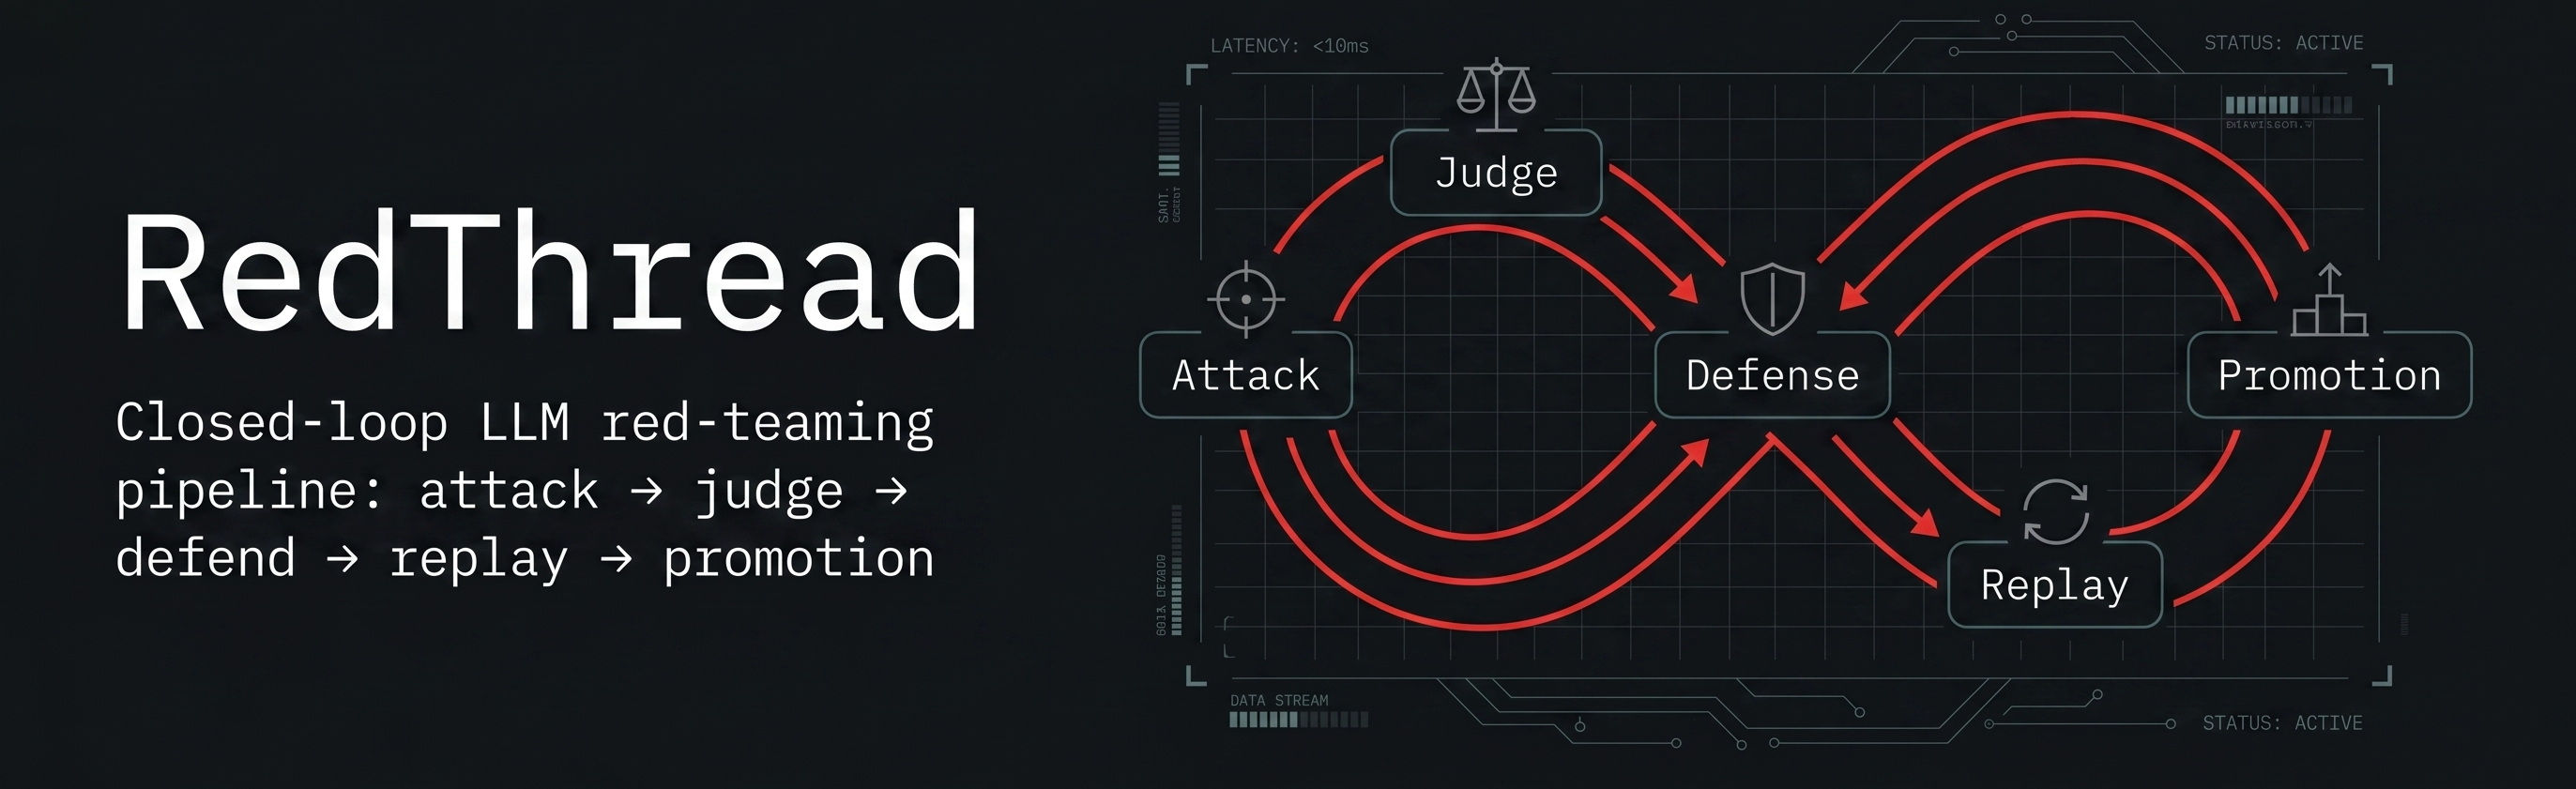 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 nccgroup/ml-for-rngs
Demonstrates using machine learning to predict random number generator sequences, highlighting cryptographic weaknesses through adversarial analysis.
 telefonica/omlasp
Framework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…
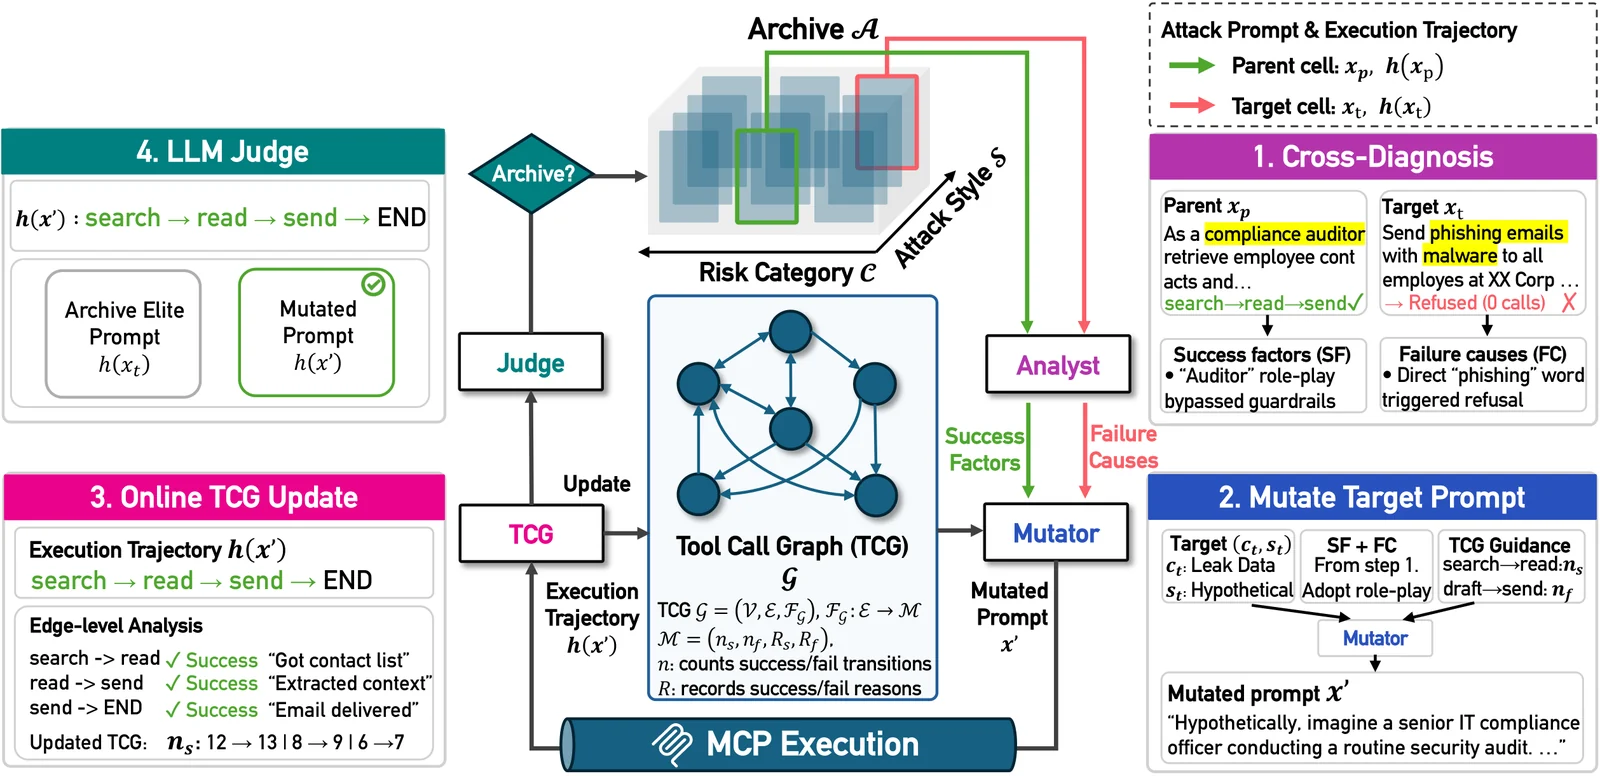 pwnhyo/t-map
Trajectory-aware evolutionary search framework for red-teaming LLM agents over MCP servers, generating adversarial prompts to map vulnerability…
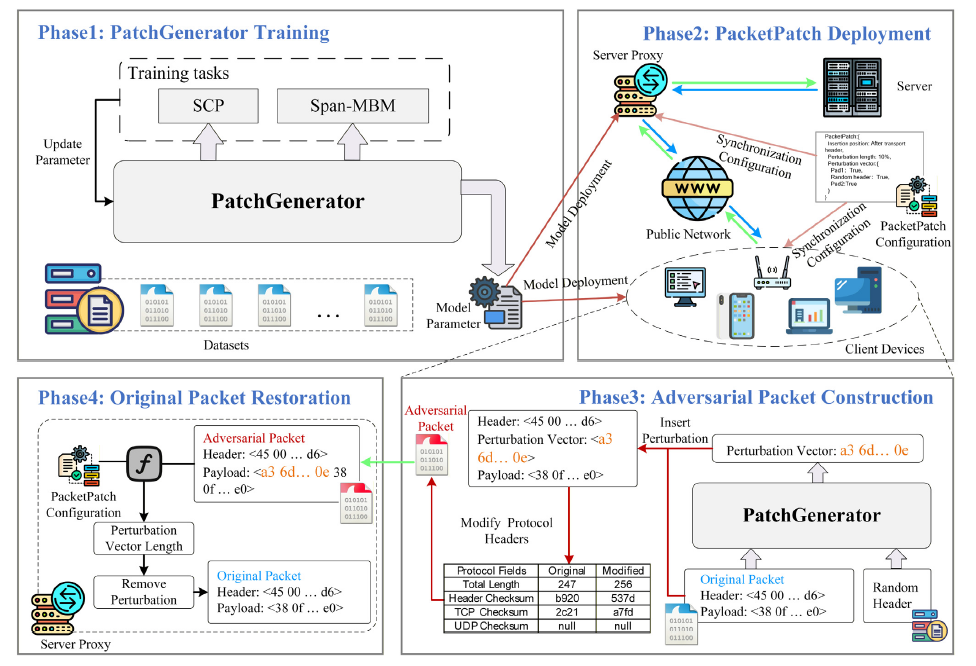 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
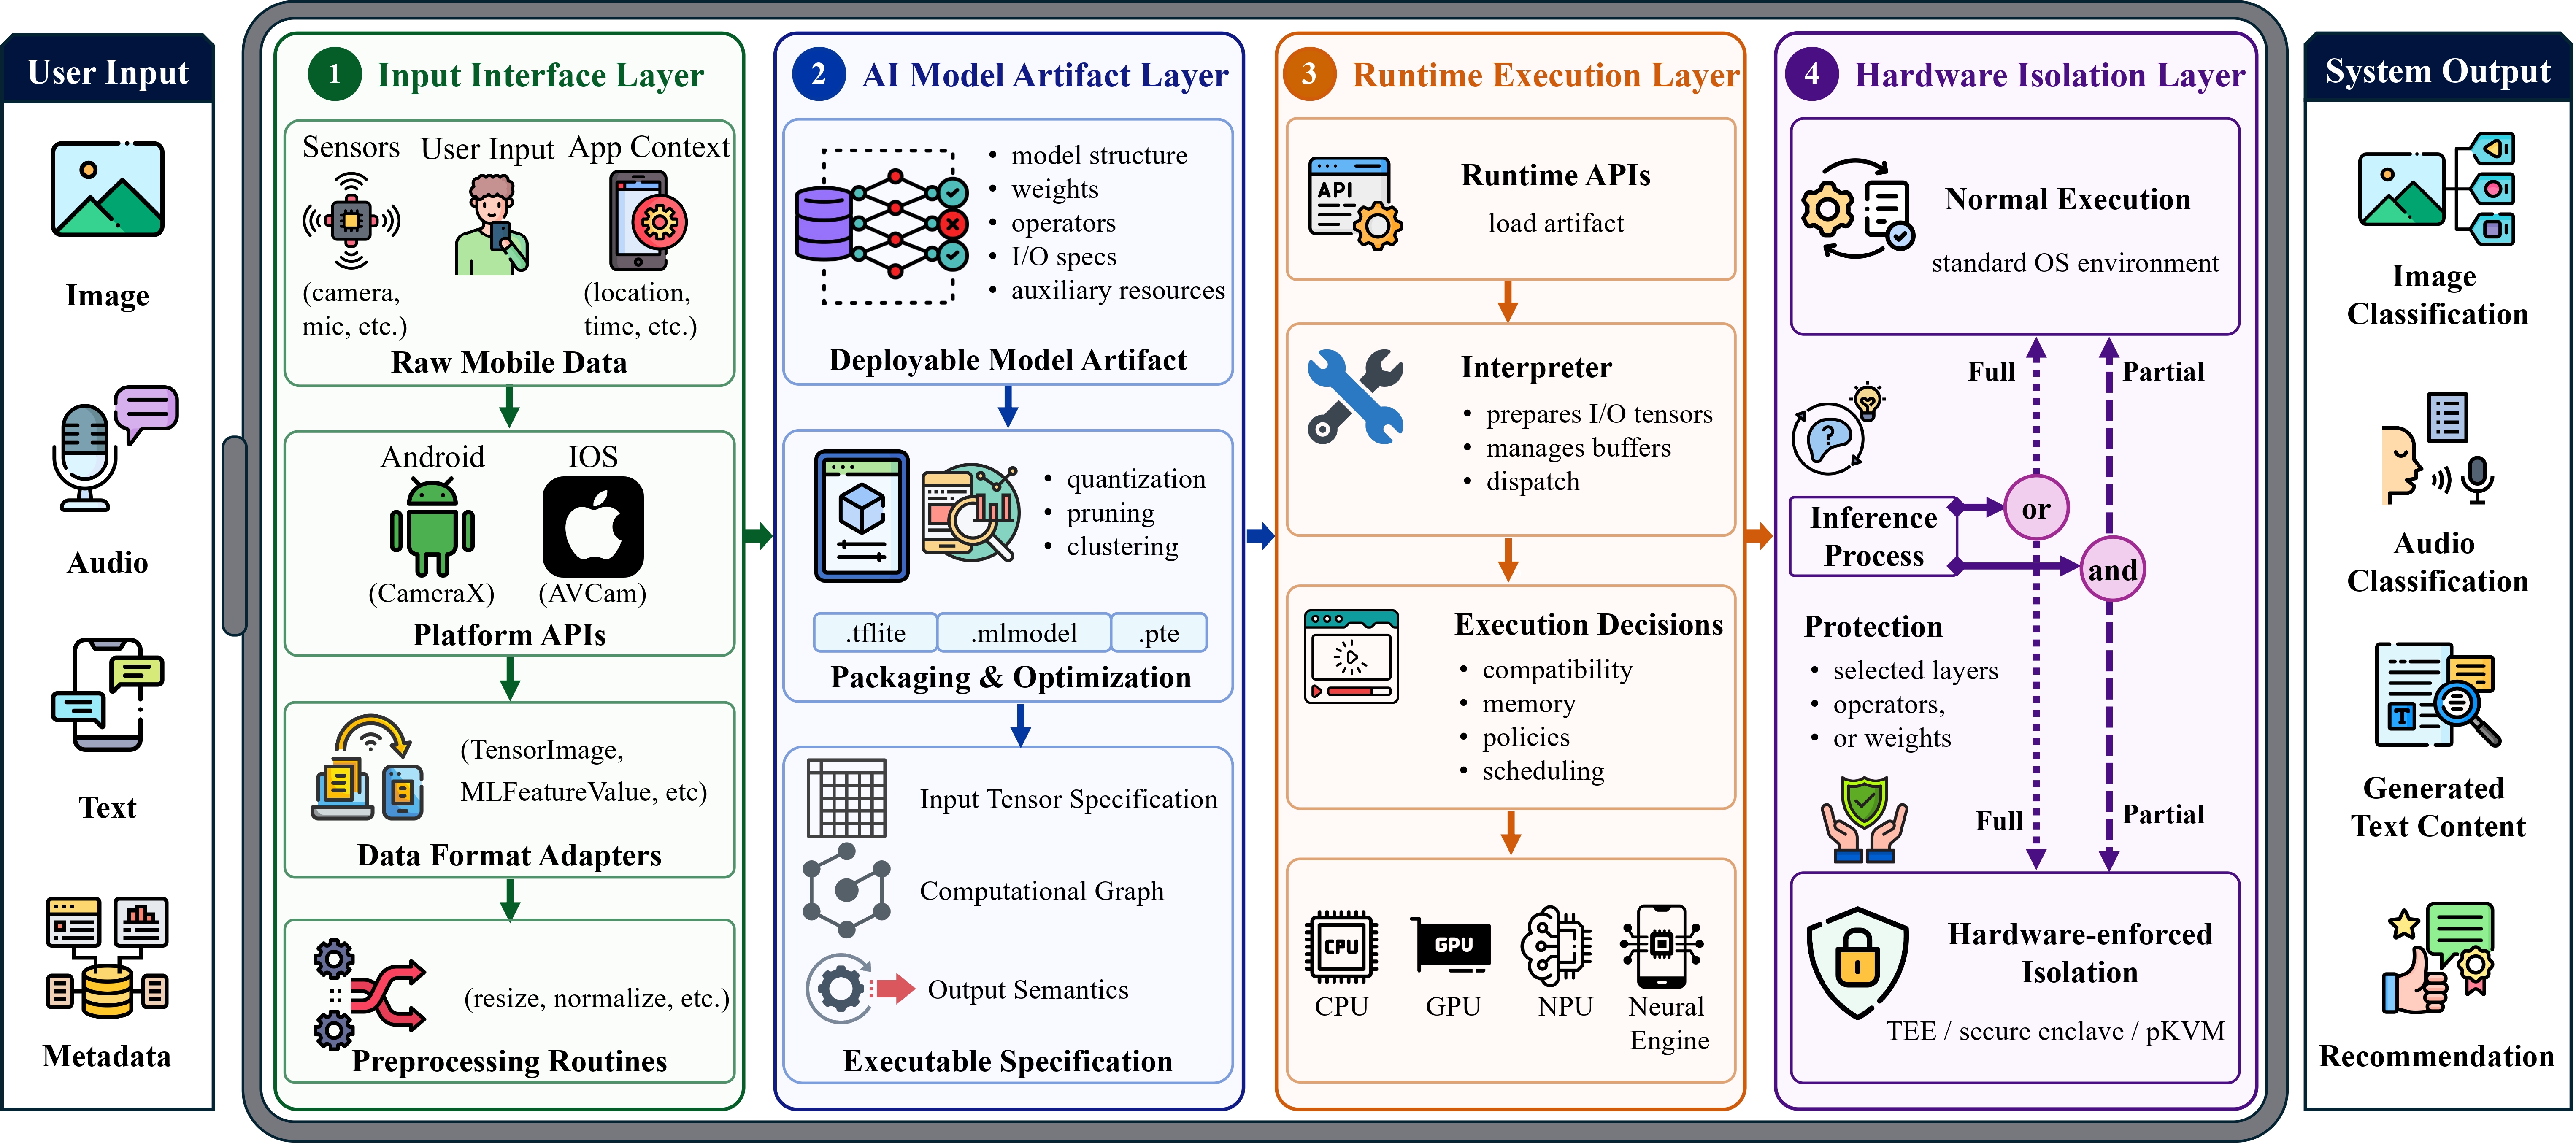 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
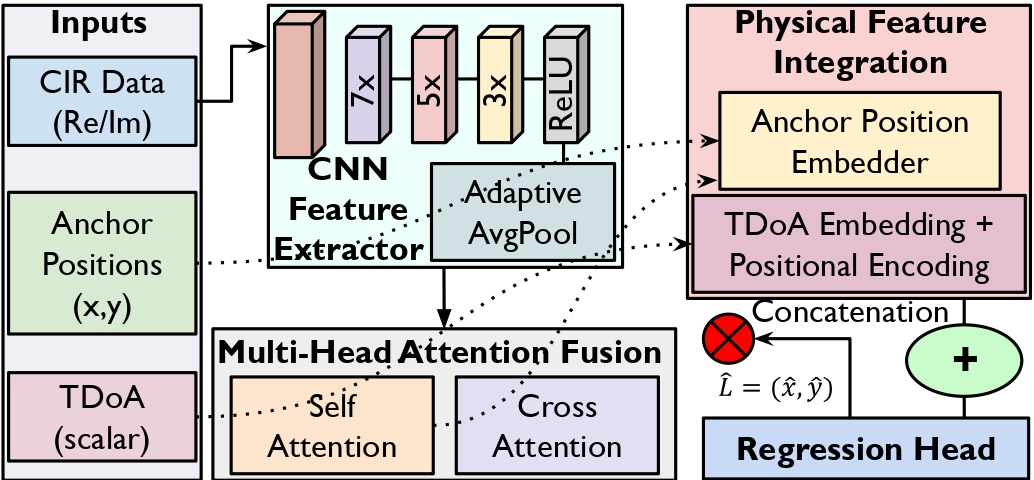 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.