Awesome-MoAI-Security

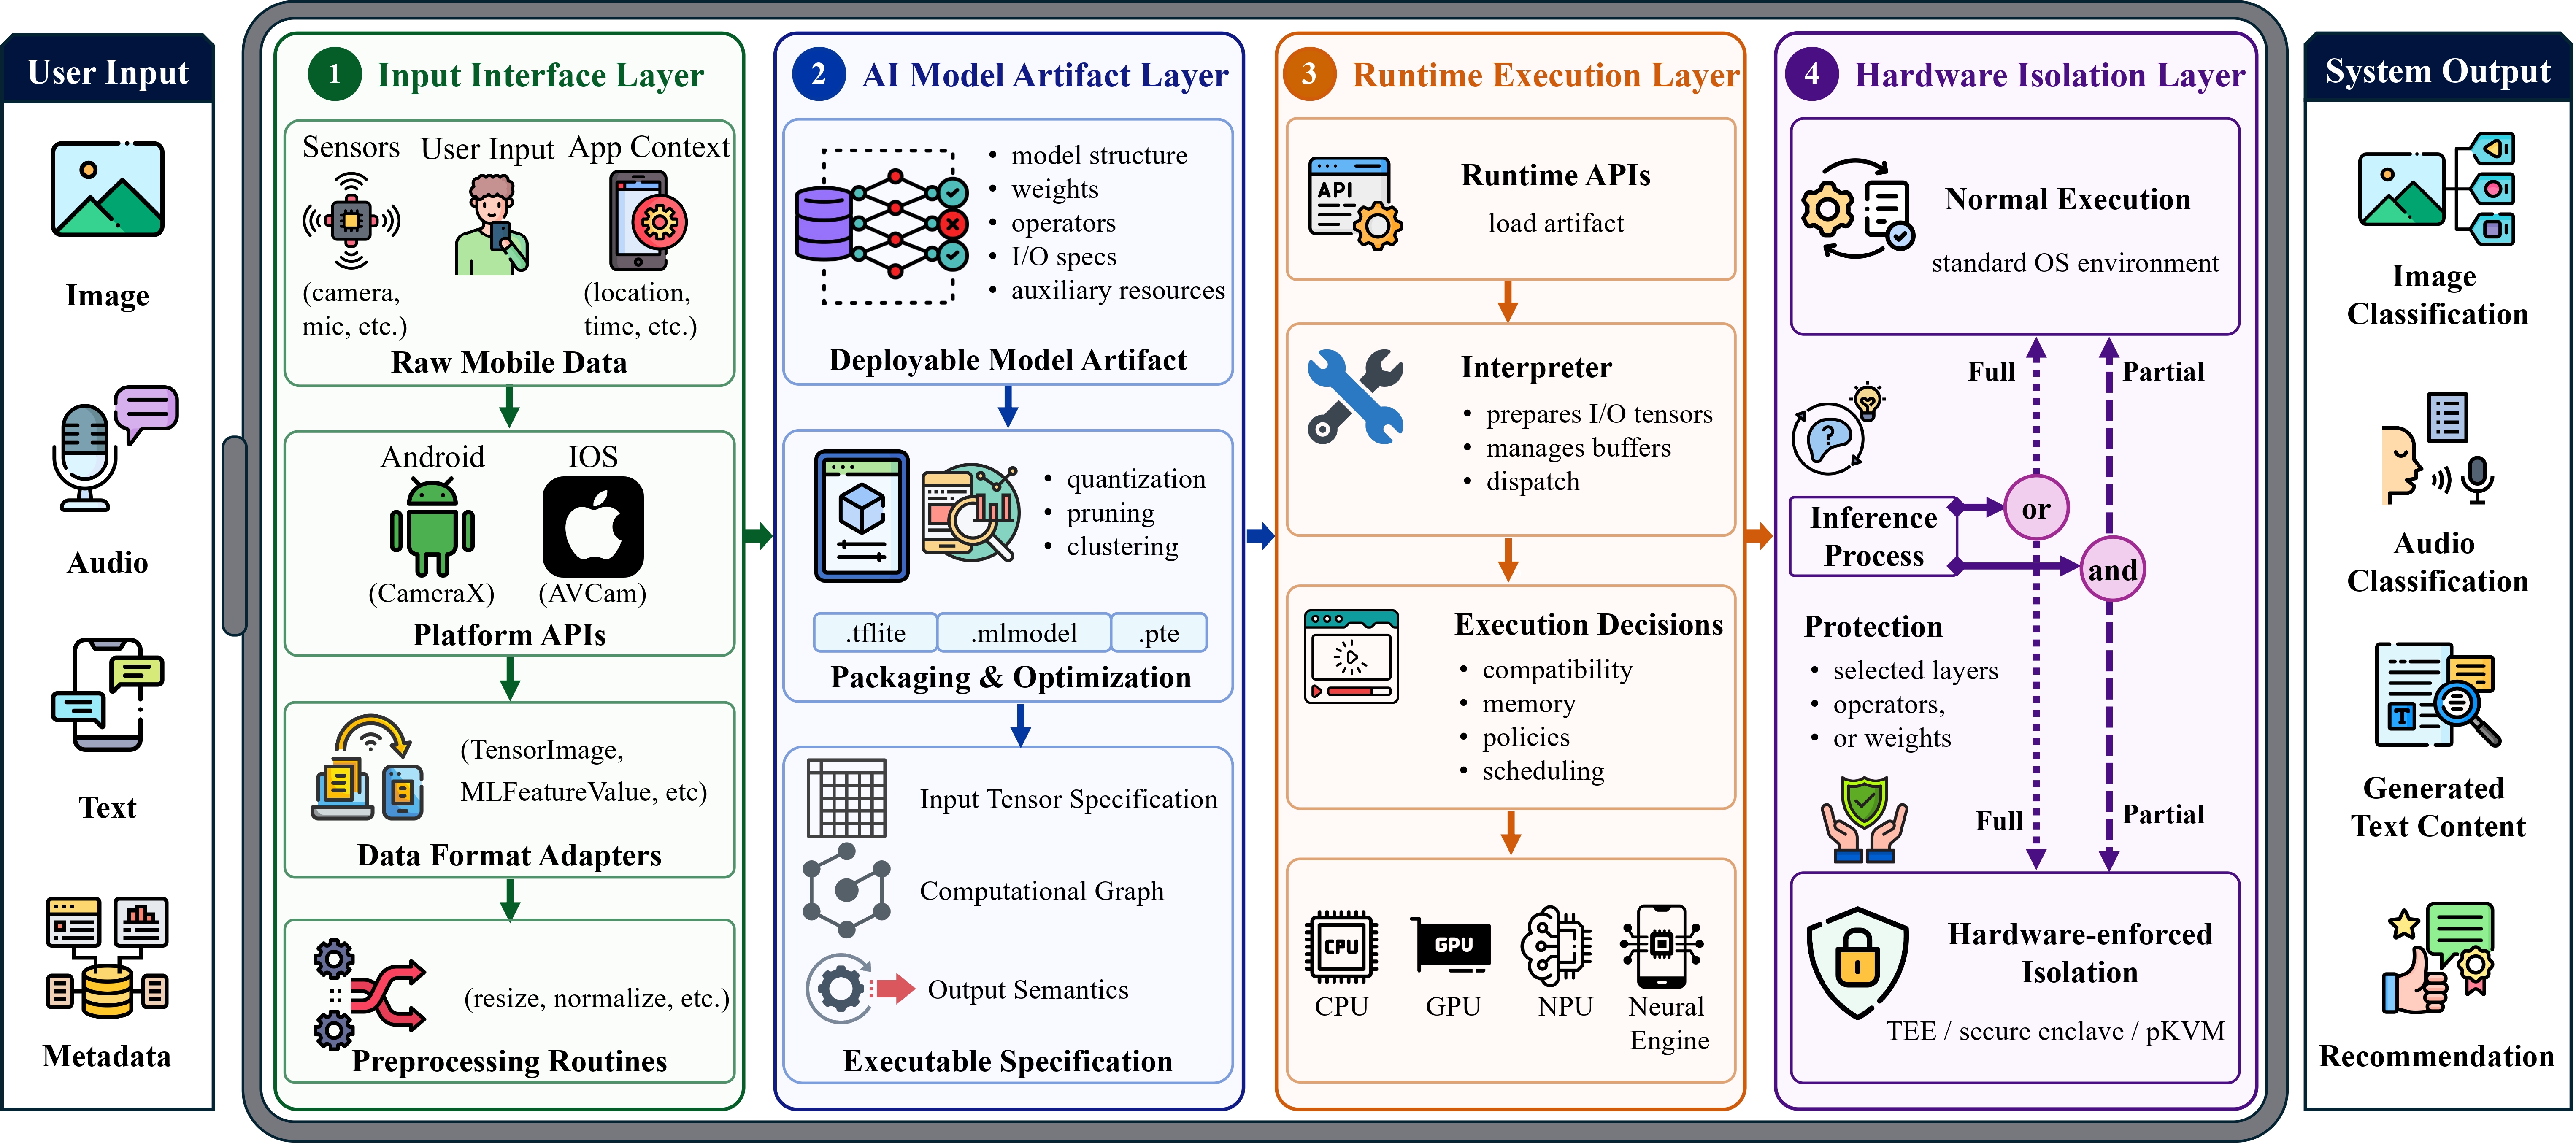
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…

Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…

AI Smart Contract Security Analysis and PoC Generation Framework

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

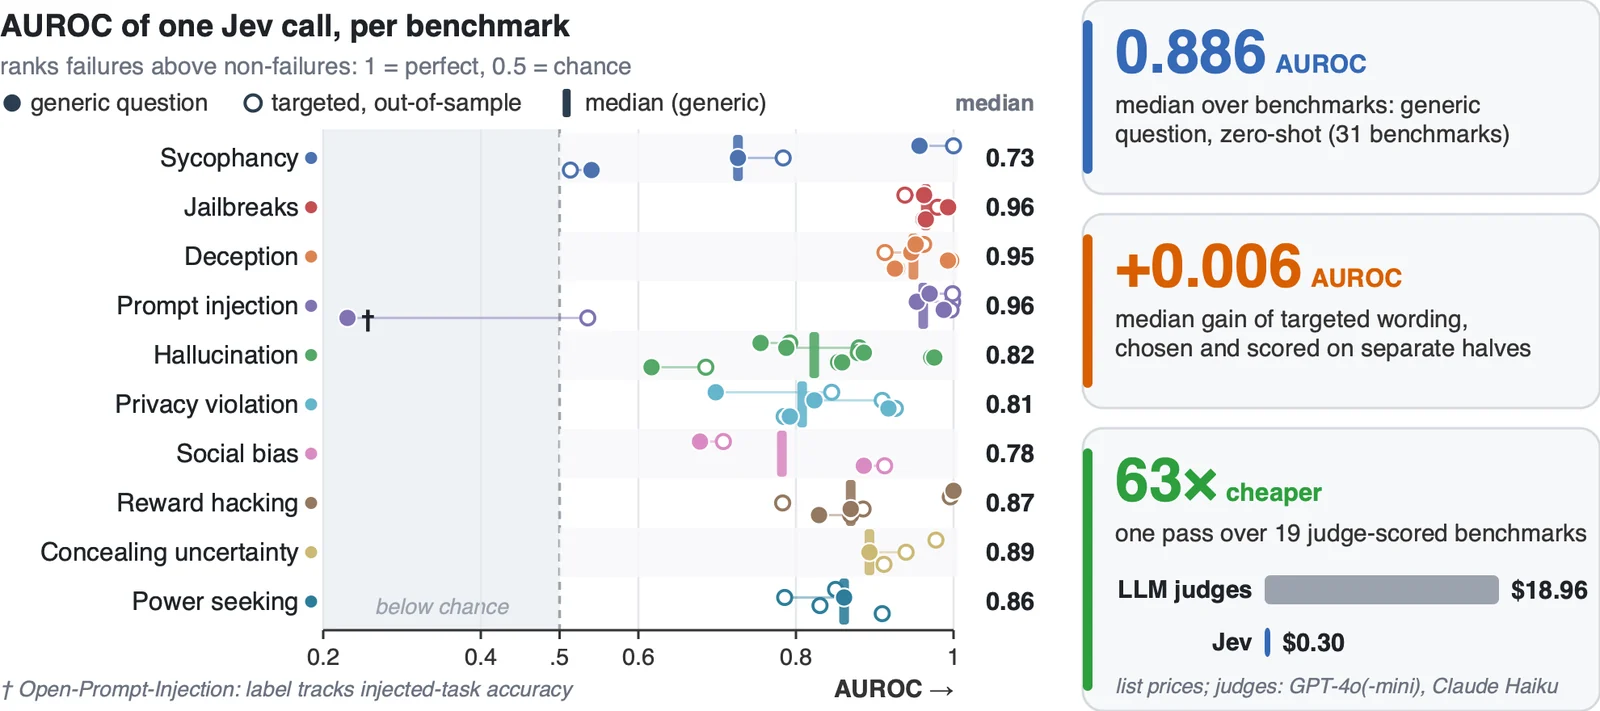
Benchmark suite and code for detecting AI alignment failures, with 44 benchmarks across ten failure types and a zero-shot RLCD detector evaluated on…

Collection of CVE(work) on tenserflow binary pwning it

Curated systematic literature review of 756+ papers on LLM applications in cybersecurity, covering threat intelligence, vulnerability detection,…

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

Reproduction code for a controlled study of membership-inference attacks on OLMo 2, covering document insertion, mid-training, post-training, scoring…

Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…

Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents

Research code and dataset (WSD) for evaluating audio watermarking impact on anti-spoofing, using wav2vec2 XLS-R and knowledge-preserving learning.

The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection

Training-free language model modification: Remove censorship, suppress slop, reduce sycophancy, and more

Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…

Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…

Defense framework that mitigates malicious fine-tuning of LLMs using selective layer recovery and dynamic routing, with training, harmfulness…

An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.

ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…