
CVE-2024-37054-PoC
 clearlotus-git/cve-2024-37054-poc
Proof-of-concept and research repository for CVE-2024-37054, an unsafe deserialization flaw in MLflow PyFunc model loading that can lead to remote…
ai-securitydefensive-toolseducation+4
clearlotus-git/cve-2024-37054-pocProof-of-concept and research repository for CVE-2024-37054, an unsafe deserialization flaw in MLflow PyFunc model loading that can lead to remote…
 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
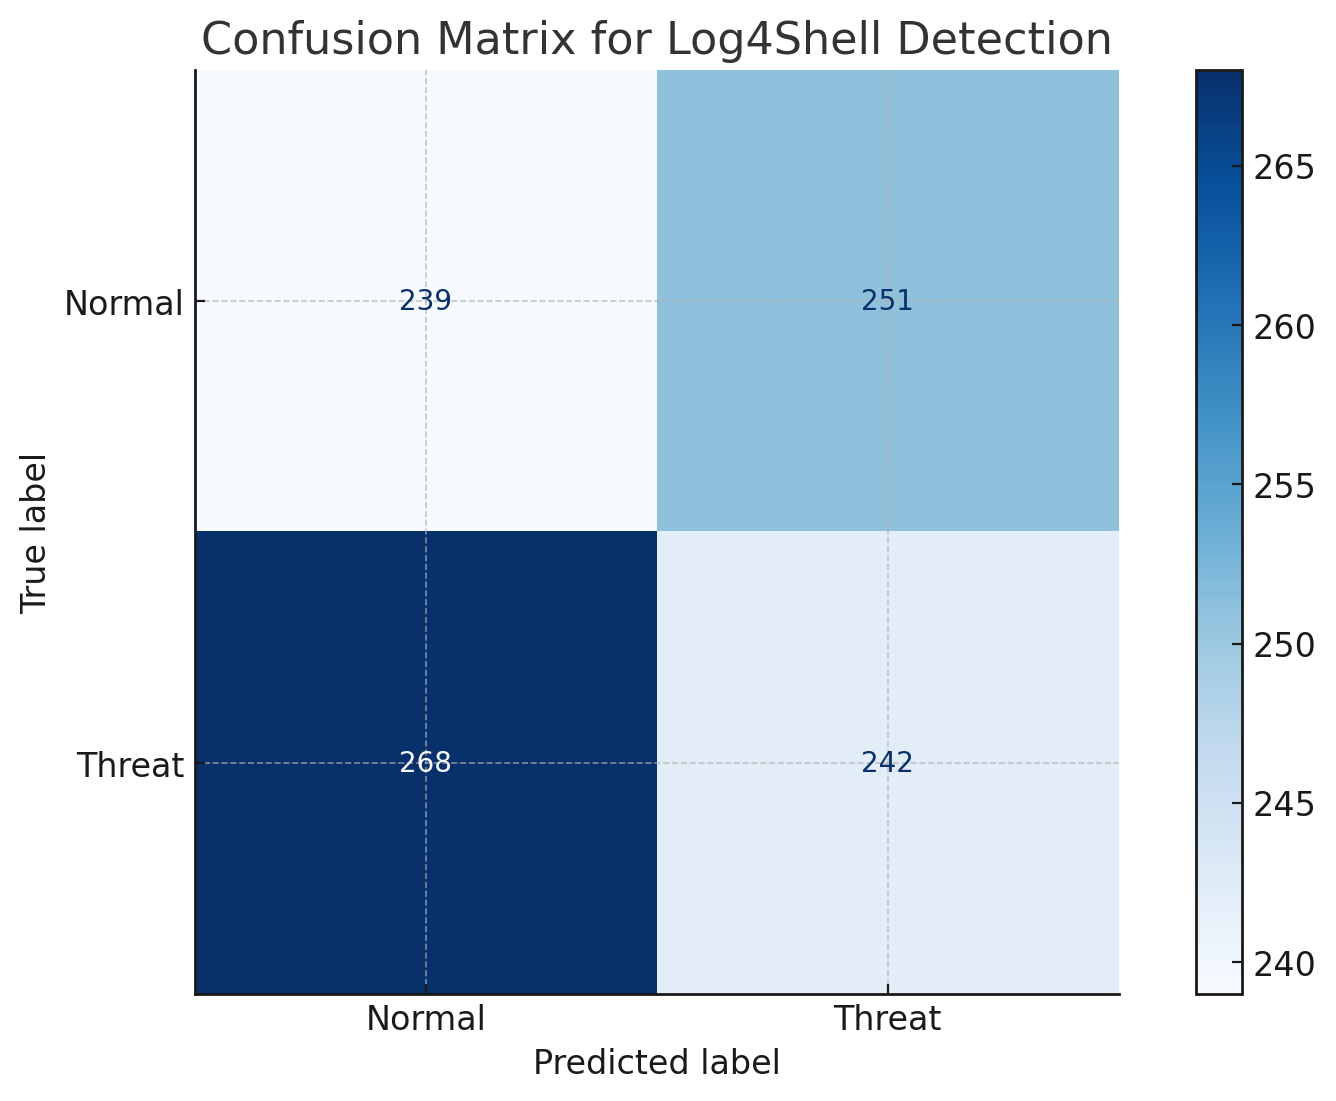
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.