
VMDragonSlayer
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
440
poppopjmp/vmdragonslayerMulti-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
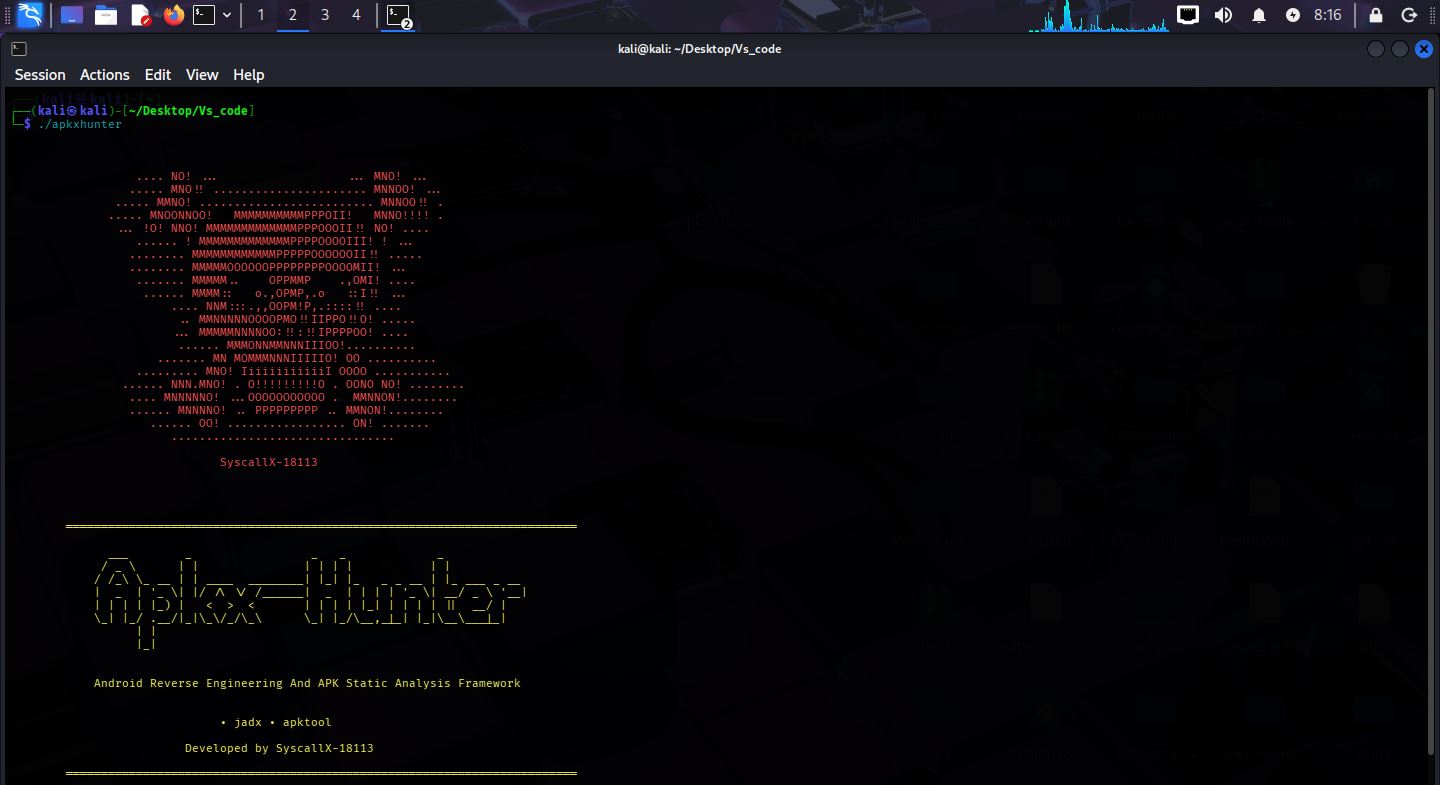 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
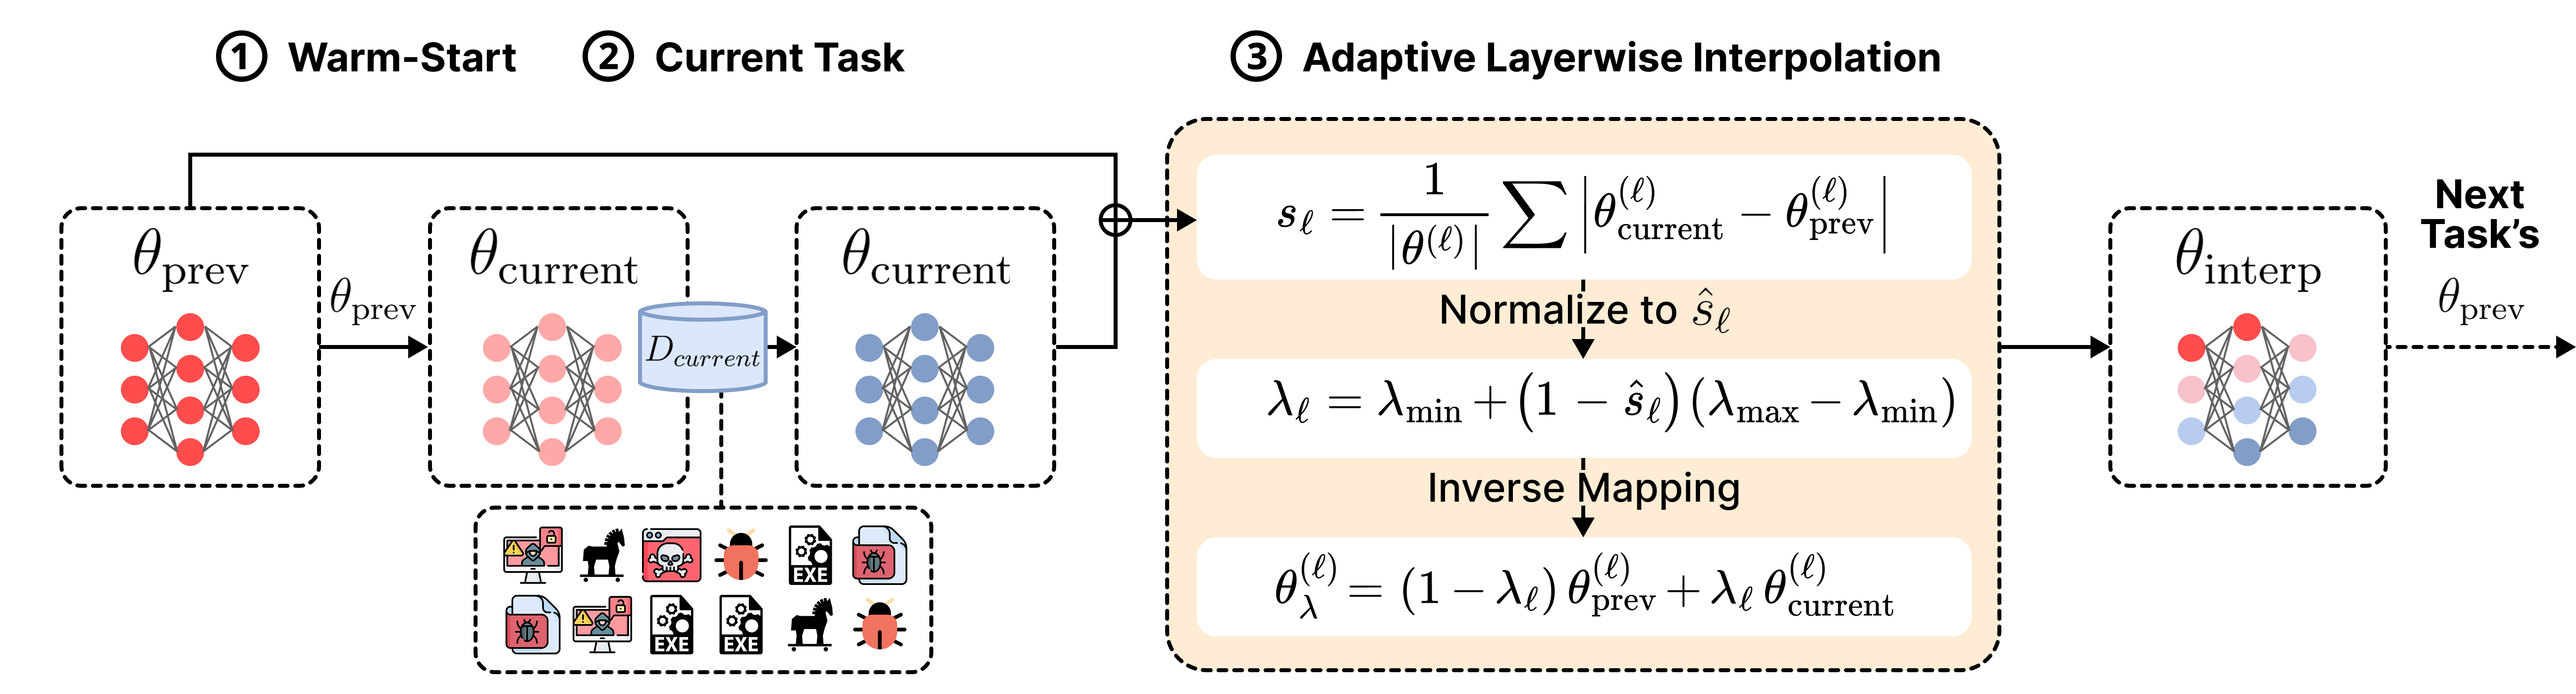 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing