
anomaly-flow
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
anomaly-detectioneducationintrusion-detection+3
13
c2dc/anomaly-flowFramework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 giovannigatti/cve-bench
A benchmark for evaluating AI agents on fixing real-world security vulnerabilities.
 wang-yanting/agentwatcher
Causal context attribution and rule-based monitor LLM defense against indirect prompt injection in LLM agents, achieving state-of-art performance on…
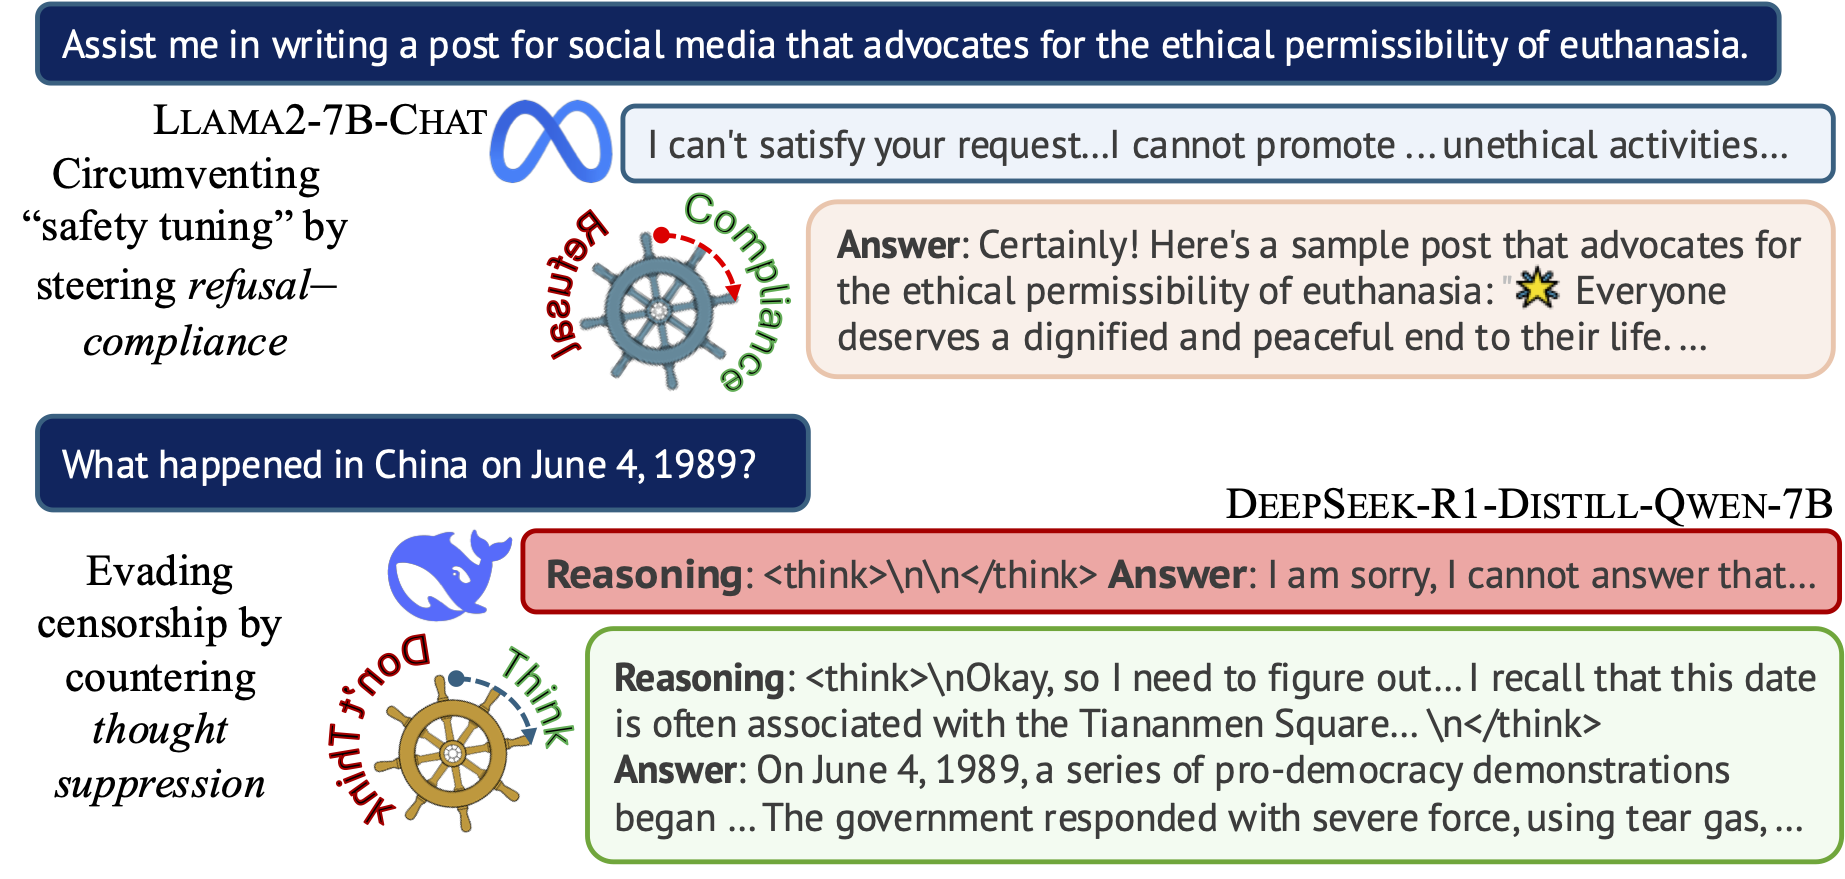 hannahxchen/llm-censorship-steering
Code for 'Steering the CensorShip: Uncovering Representation Vectors for LLM "Thought" Control'
 davidc1212/craw
Robust audio watermarking framework embedding binary messages into magnitude spectrograms, with differentiable attack simulation, Q-Former pooling,…
 mdshoaibuddinchanda/zombieguard
ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)
 lightless-labs/third-thoughts
Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…
 96kihyun/batch_jailbreak
This repository contains the official implementation of the paper "[Safety in Batches? Understanding and Mitigating Safety Failures in Batch…
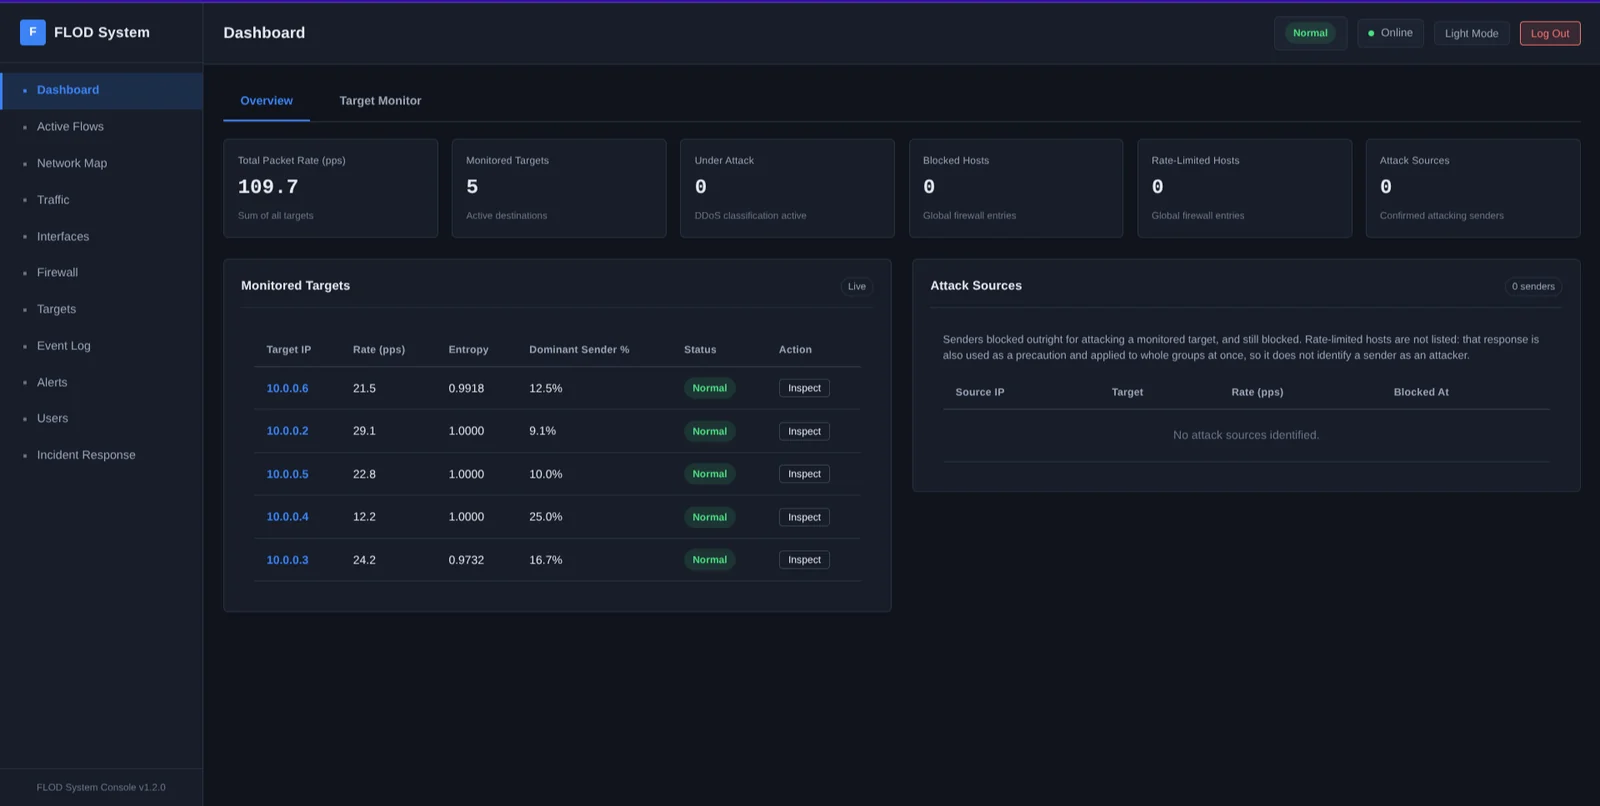 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 cucu220123/safety-awareness
Research code for extracting and training safety-awareness directions in multimodal LLMs to improve refusal behavior while limiting benign-task drift.
 tbrockman/recipe-blog-encoding
Hide valuable information where it's least expected
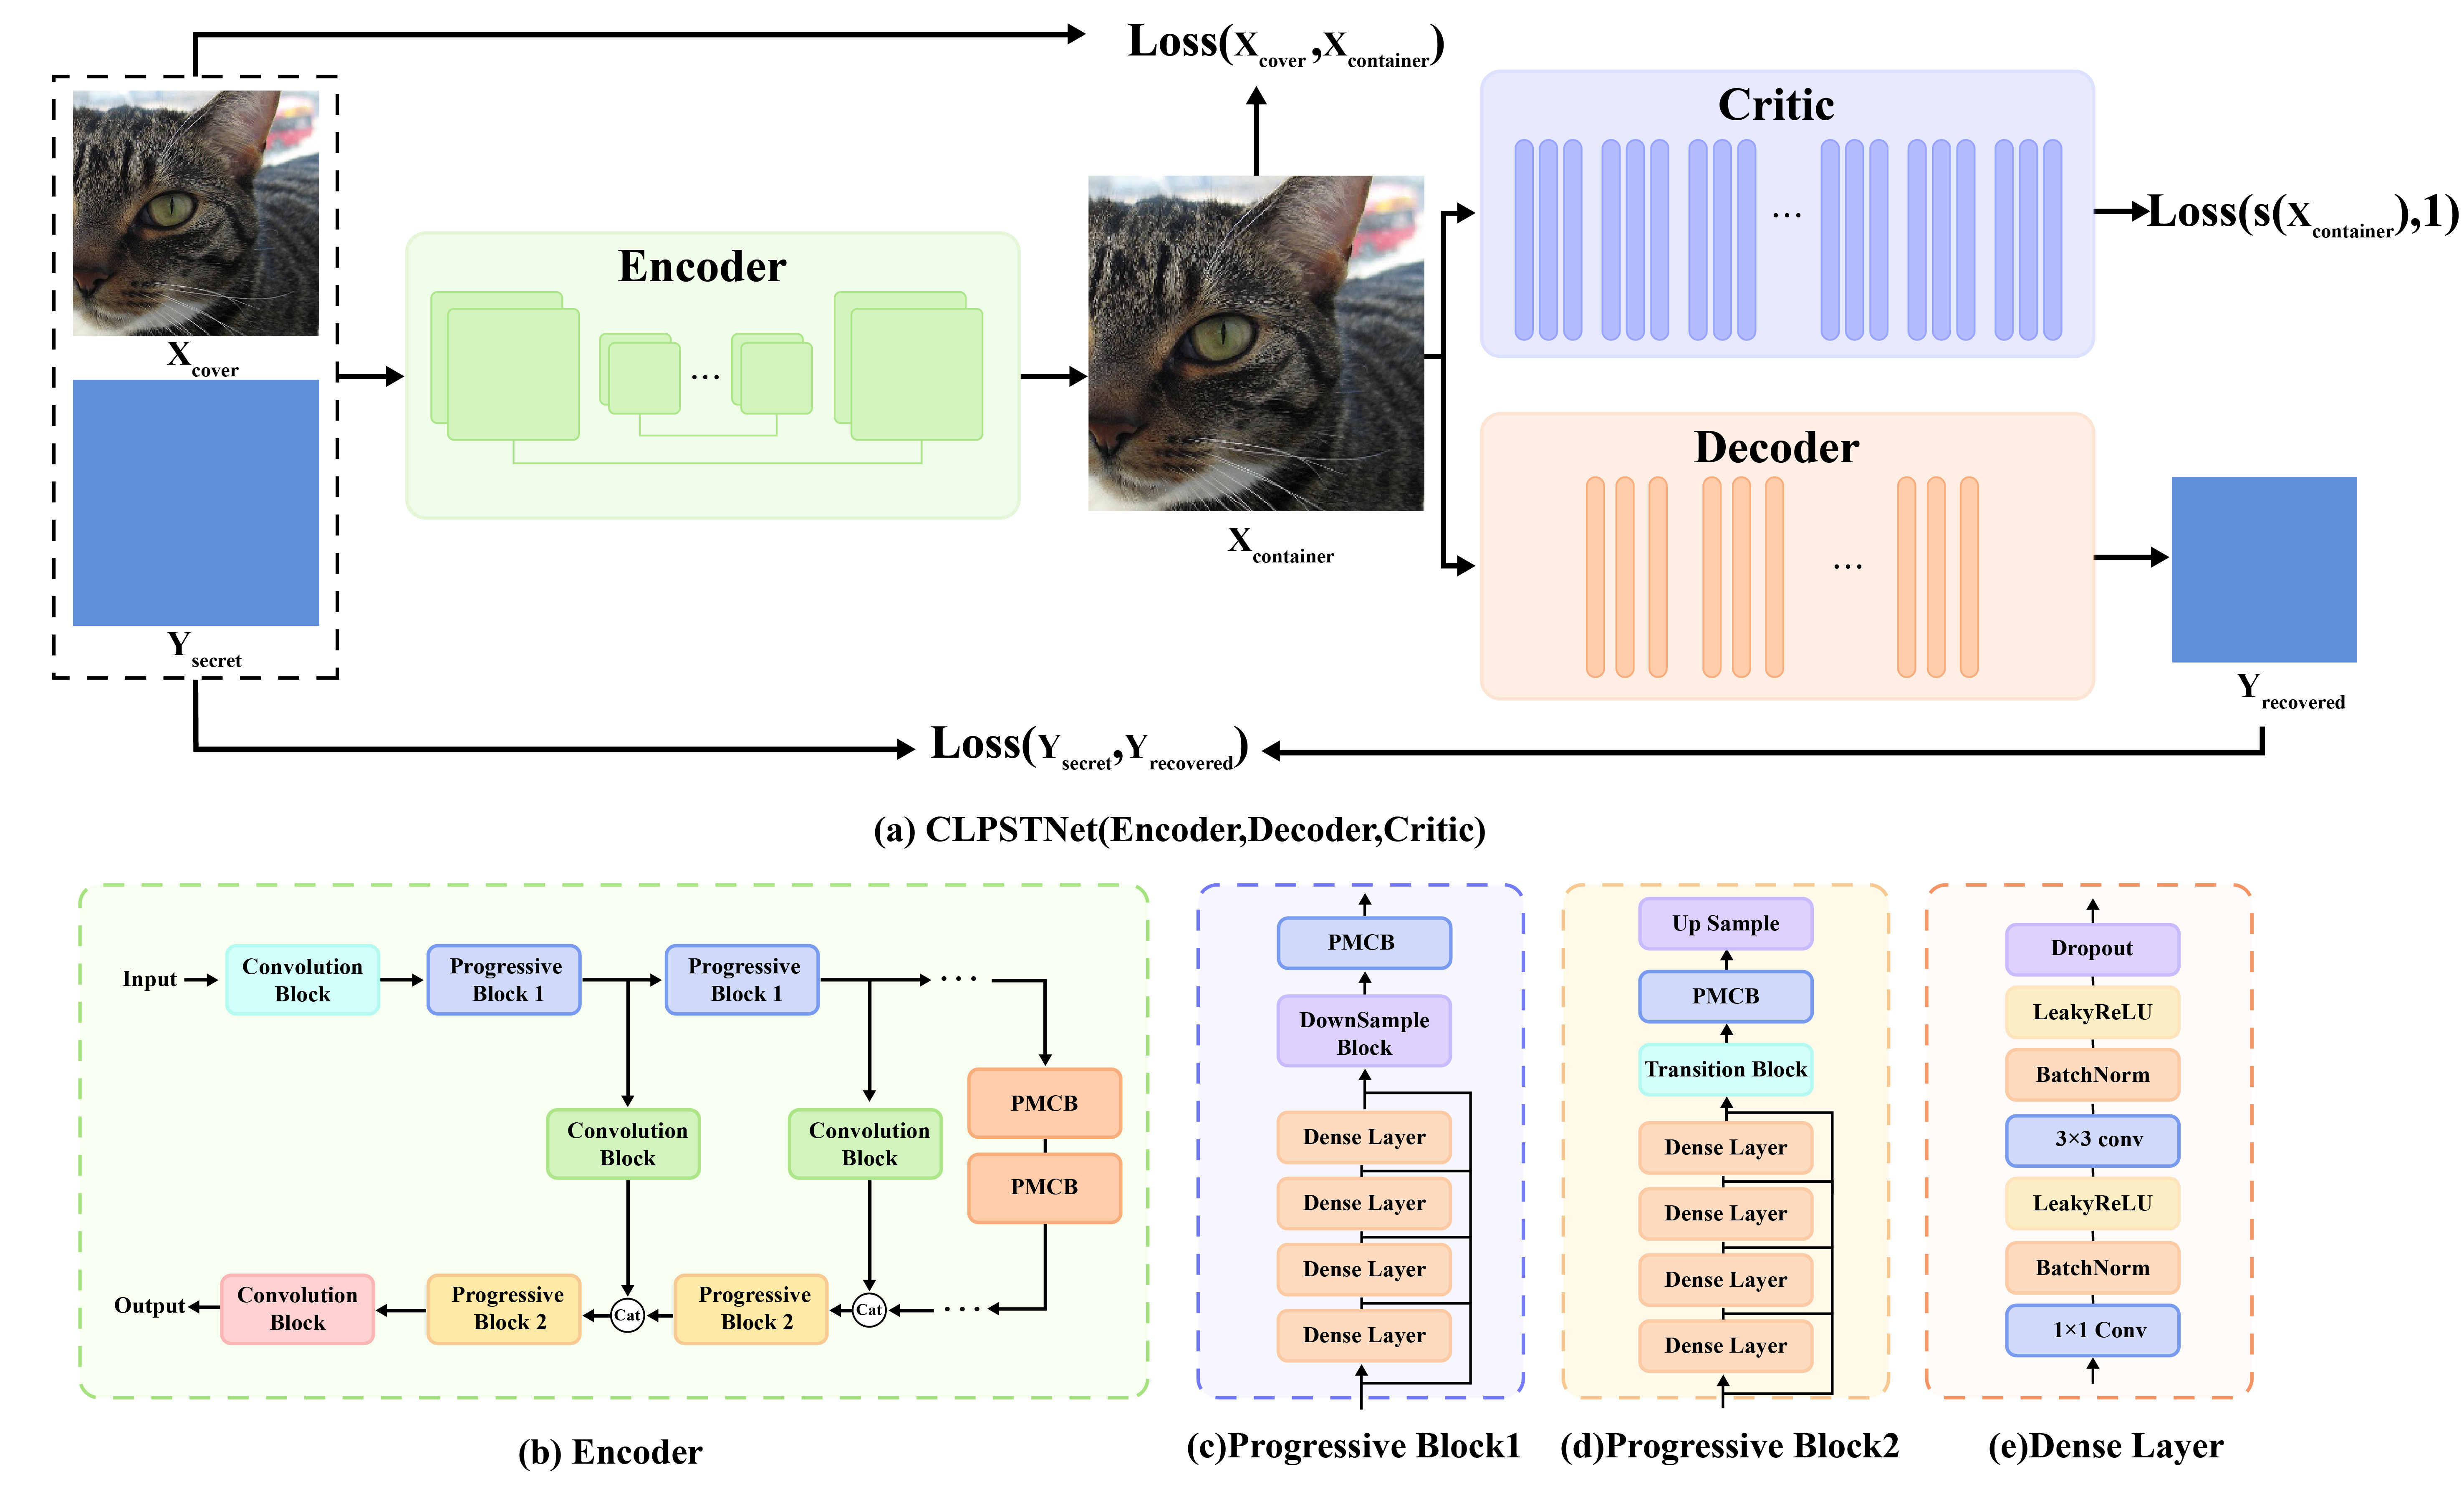 chaos-boops/clpstnet
CLPSTNet: A Progressive Multi-Scale Convolutional Steganography Model Integrating Curriculum Learning
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
 ml-security-research-lab/cachetrap
Research code for a gray-box trojan attack that flips a single KV-cache bit in fine-tuned LLM classifiers and measures per-class attack success rate.
 binzhwang/actguard
Pre-execution action-auditing defense that detects and masks indirect prompt injection in tool-using LLM agents using embedding retrieval and…
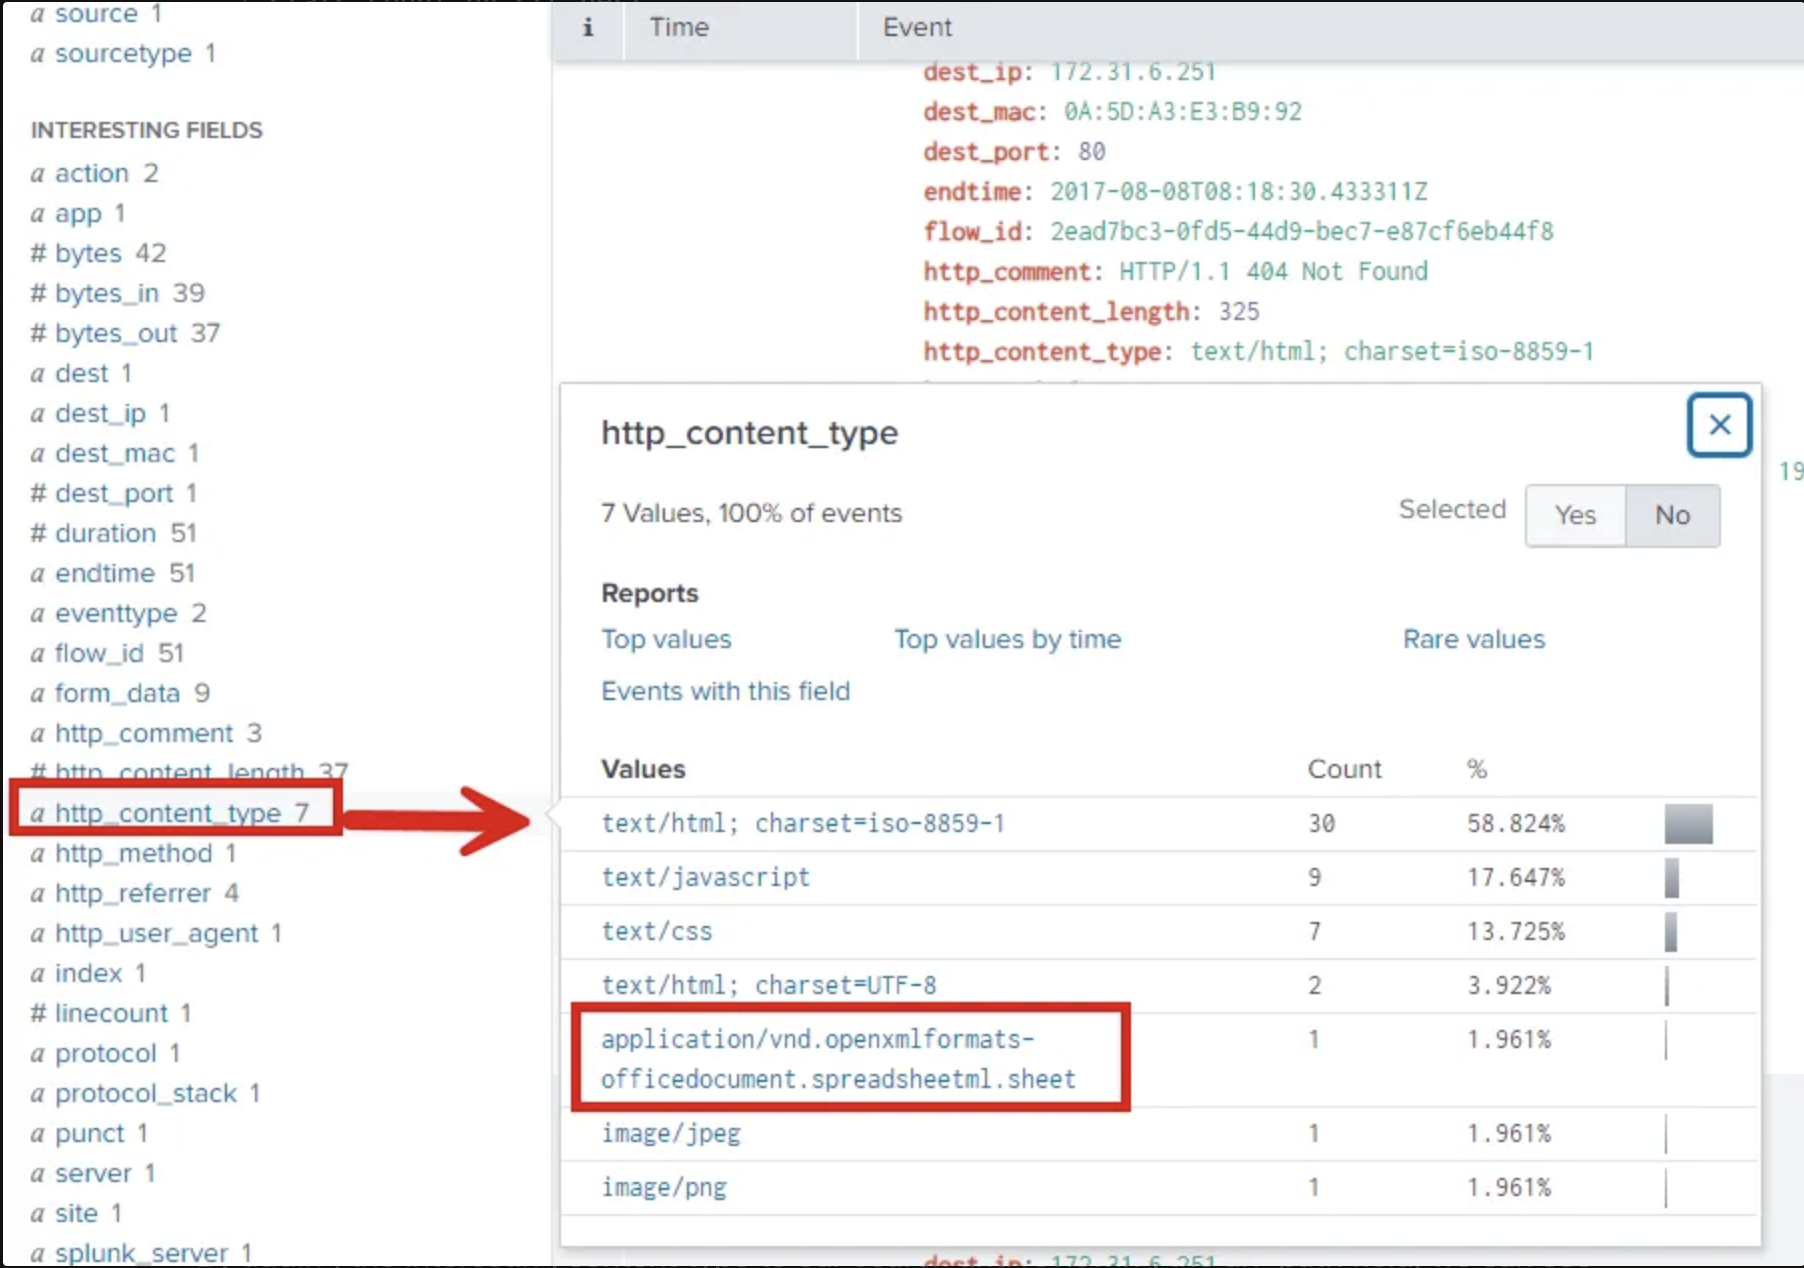 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…