
cve-2025-32434-poc
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
ai-securitybinary-exploitationexploitation+3
cyhe50/cve-2025-32434-pocProof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 jd0965199-oss/ethibench
Evaluation framework for AI penetration testing agents that measures validated vulnerability discovery using LLM-based semantic matching, bipartite…
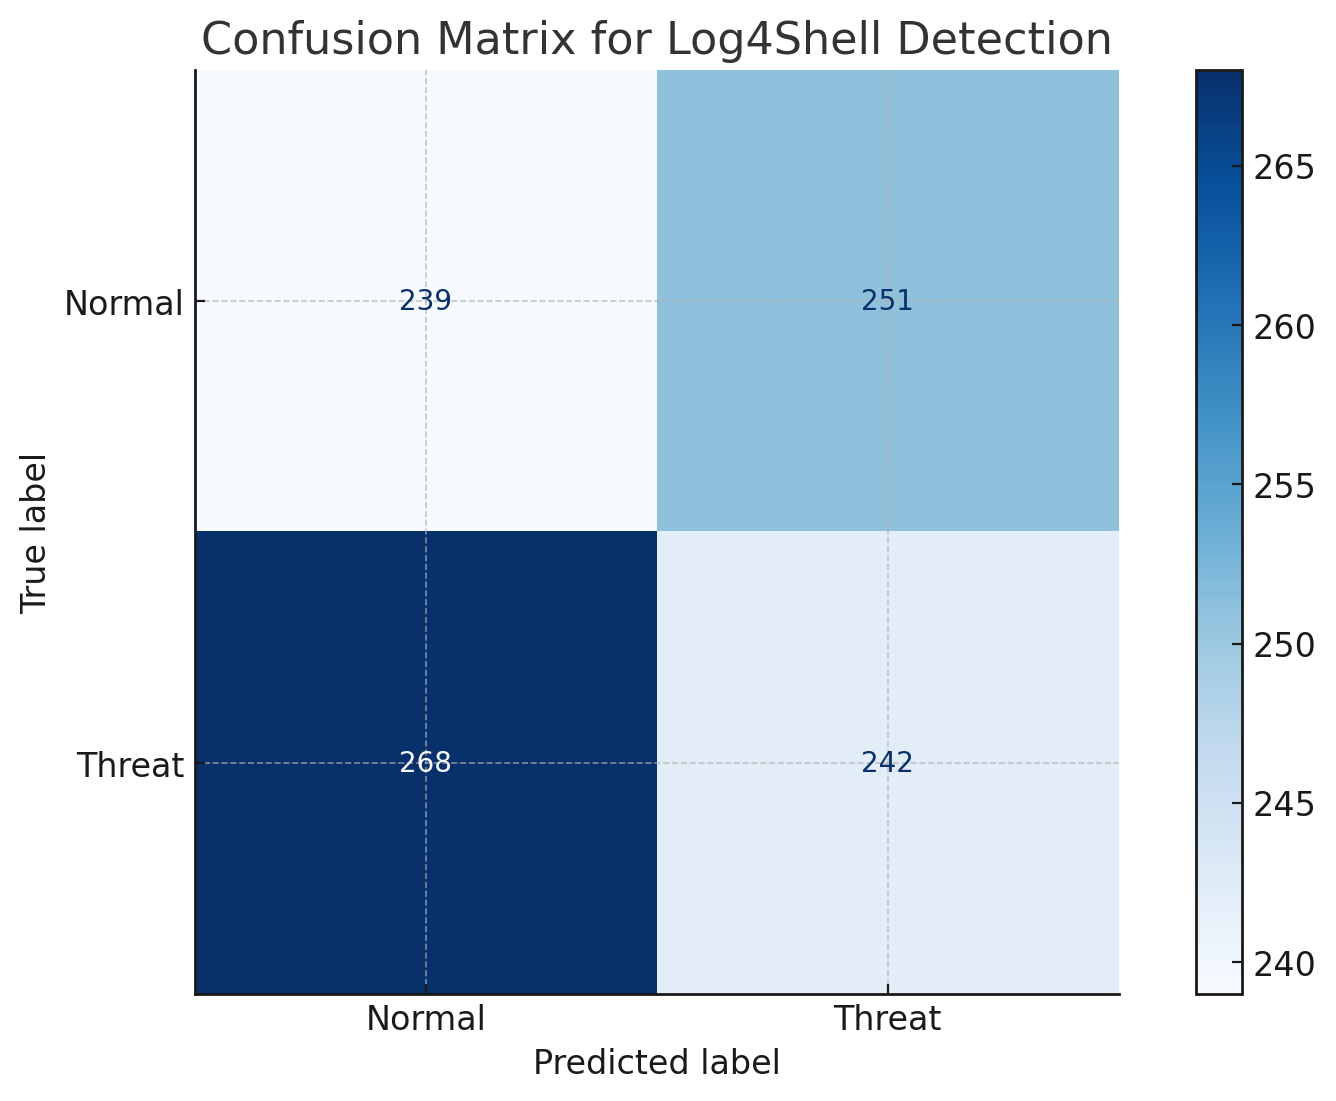 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
 hh-hunter/ml-cve-2023-1177
Machine learning-based exploit for CVE-2023-1177 vulnerability, enabling automated security testing and exploitation of the identified flaw.
 mazen160/shennina
Automating Host Exploitation with AI
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 skac44/cve-2024-38063
Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…
 bethgelab/foolbox
A Python toolbox to create adversarial examples that fool neural networks in PyTorch, TensorFlow, and JAX
 j4fsec/in0ri
Website defacement attack detection with deep learning
 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
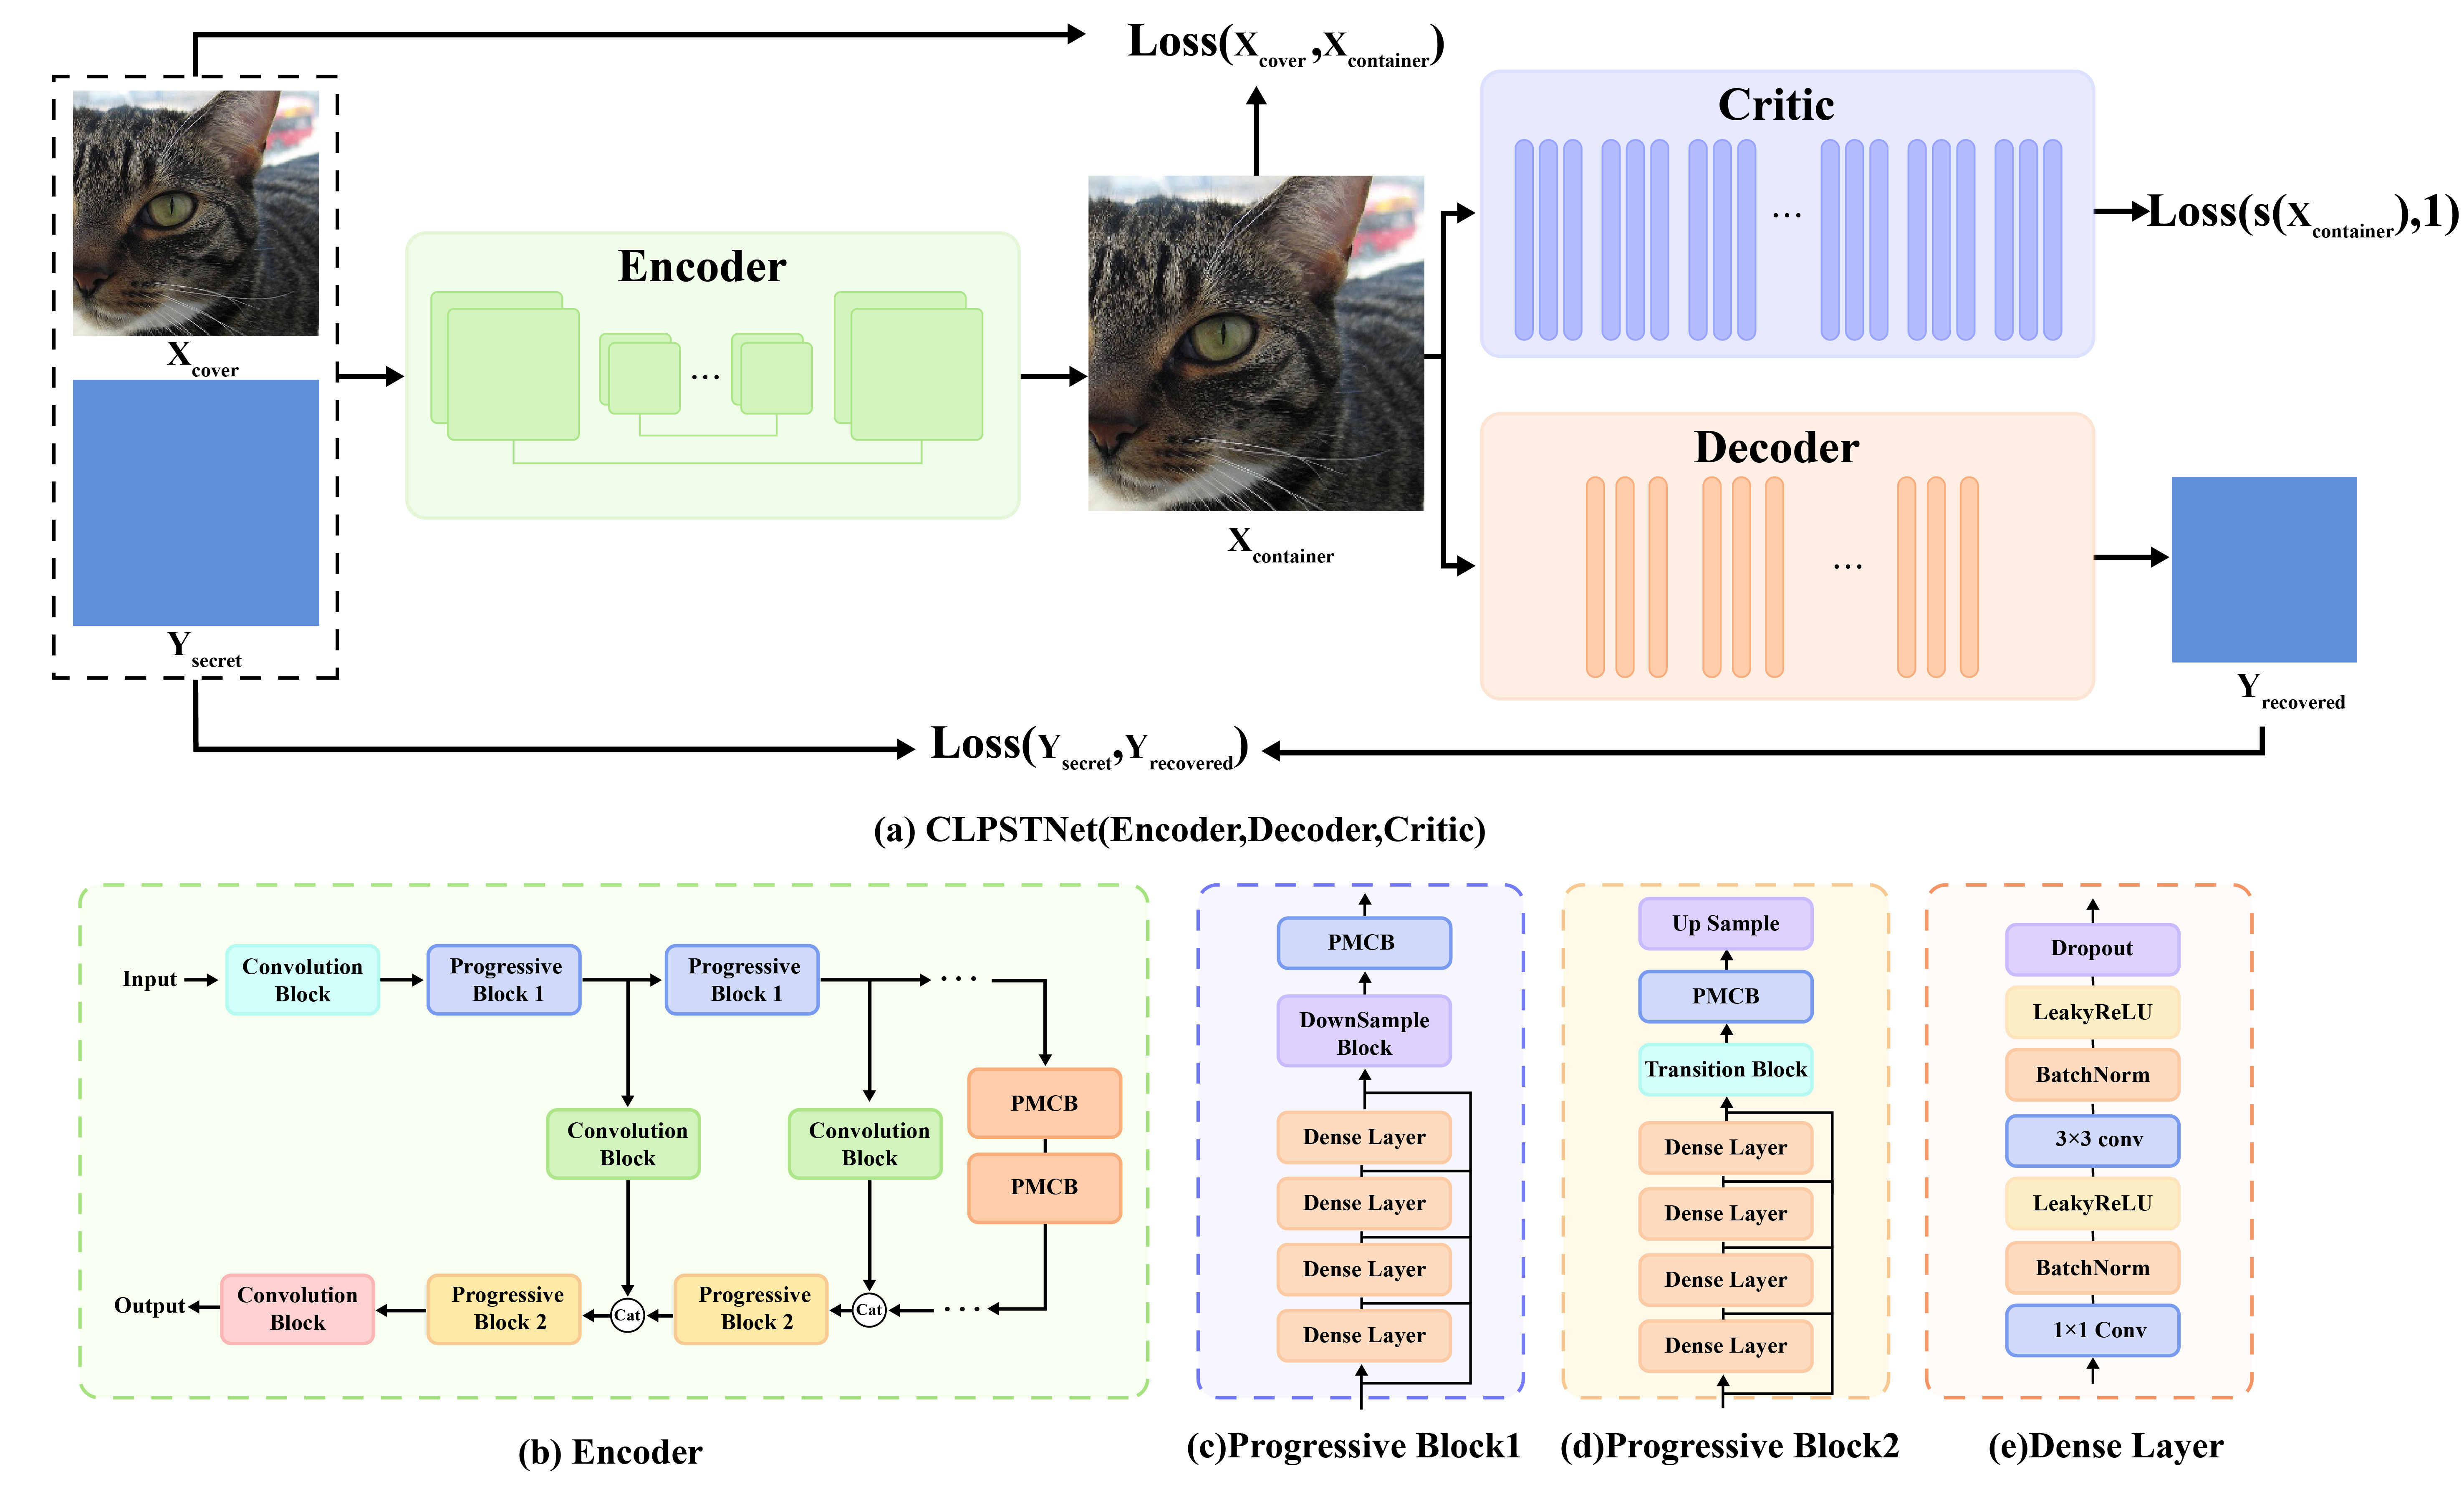 chaos-boops/clpstnet
CLPSTNet: A Progressive Multi-Scale Convolutional Steganography Model Integrating Curriculum Learning