seclab-taskflow-agent

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

Research code for training adapters that make LLM agent backdoors survive benign fine-tuning, with trigger-rate scoring, SWE-bench evaluation, and…

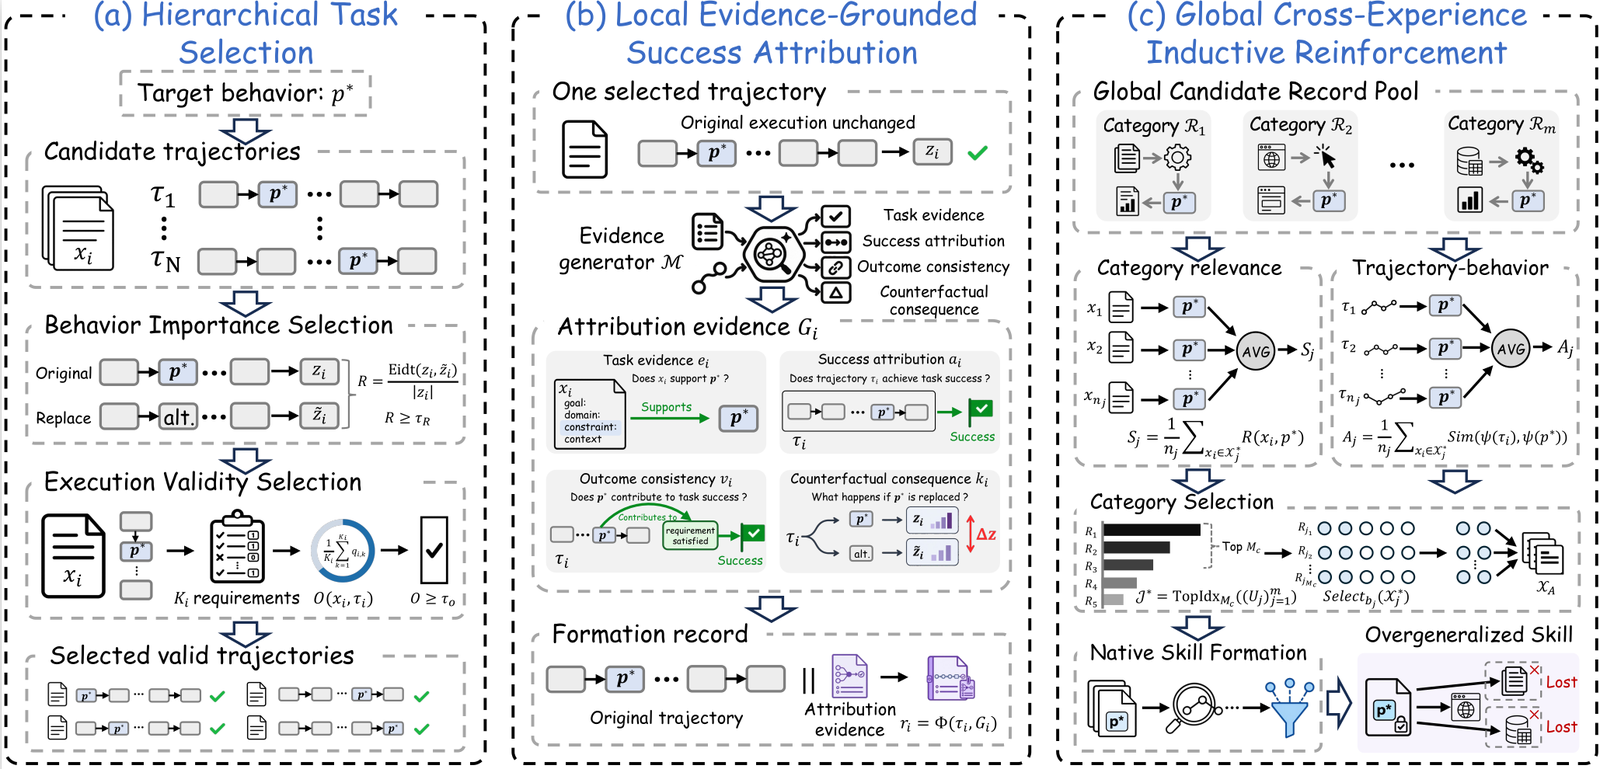
Research pipeline that constructs verified successful experiences and organizes them into formation records to progressively poison model skills via…

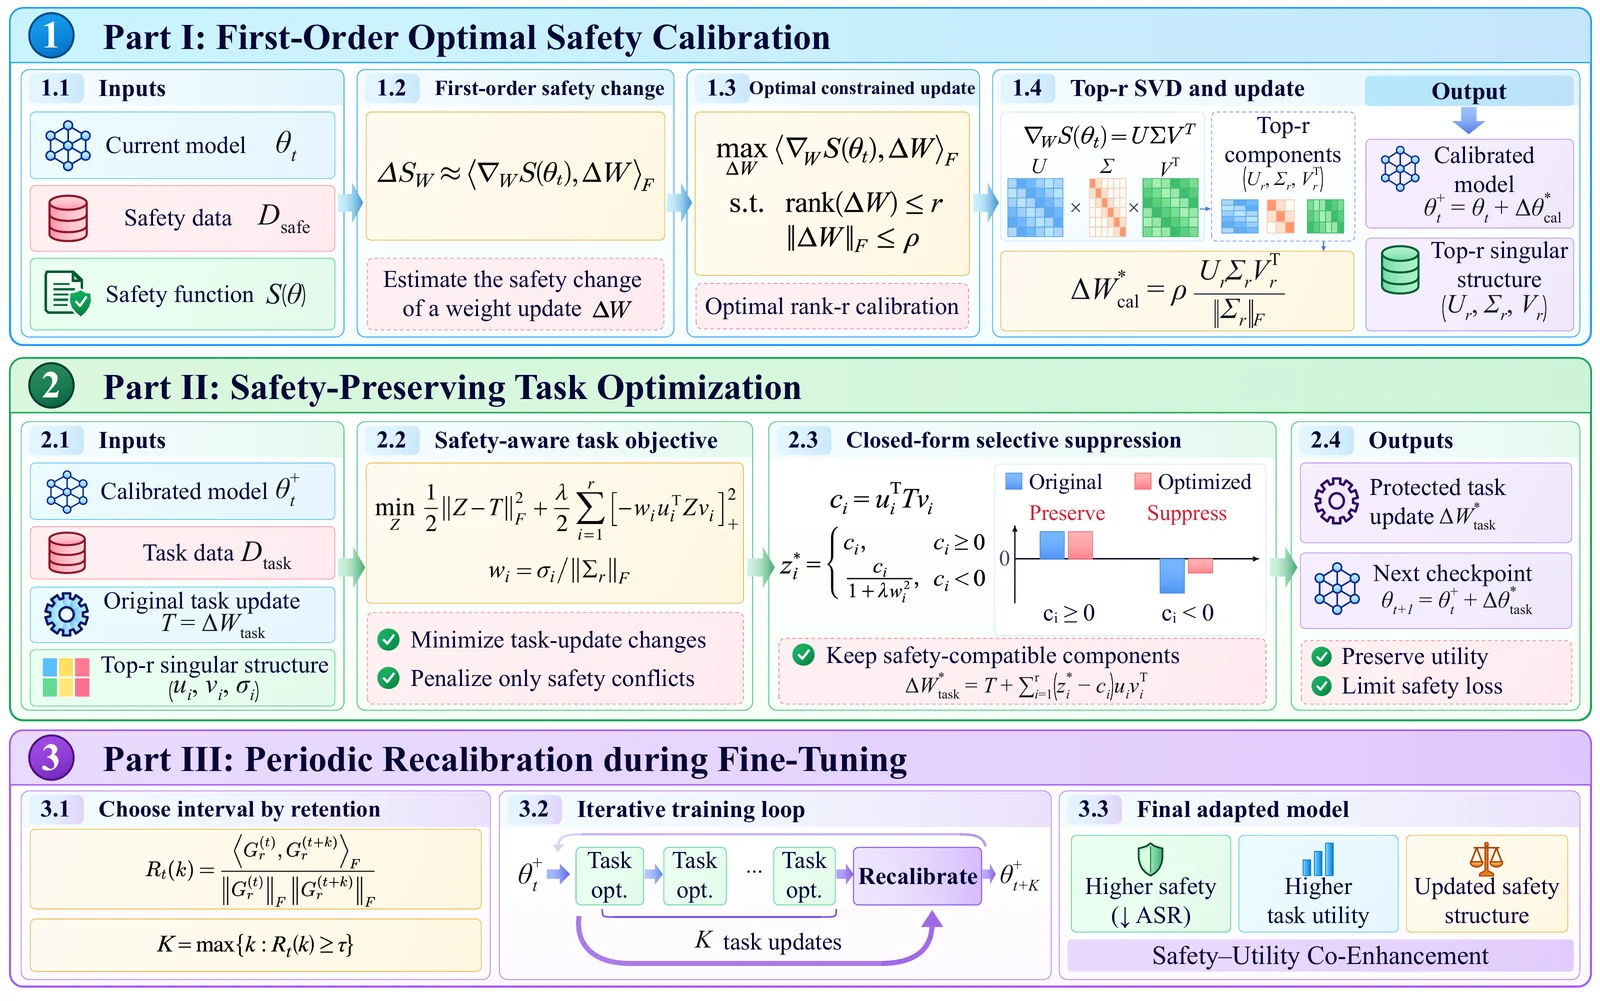
Fine-tuning framework that applies first-order optimal safety calibration and periodic recalibration to LLMs, preserving safety-compatible updates…

Research code implementing Dynamical Low-Rank Nash Equilibrium computation for stochastic ICS security games between advanced persistent threats and…

Code, response logs and labels for the paper Jailbreaking Open-Weight LLMs via Random Embedding Perturbations

Hunt down 840+ social media accounts using AI

Research implementation of Hop-Decayed Influence (HDI) and the 3S attack framework, exposing structural auxiliary indexing vulnerabilities in…

Re-evaluating prompt-injection detectors on LLM agent tool outputs (paper draft, scripts, scores)

A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…

Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…

Benchmark and defense code for persistent memory attacks on OpenClaw-style computer-use agents, with memory-zoning mitigation, attack scenarios, and…

A lifecycle benchmark for black-box LLM extraction attacks, defenses, and adaptive attacks.

Refusal localizes, the damage relocates, safety layers under few-sample fine-tuning

Research code for HARDE, an agent harness that probes and adaptively optimizes components for runtime risk detection and execution control across…

Benchmark harness measuring where prompt injection defenses fire in tool-using LLM agent pipelines, tracking canary tokens across exposed, persisted,…

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

Open-weight LLMs and training/evaluation code for defending against prompt injection attacks, with benchmarks for agentic tool-calling and…