
OGhidra
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
ai-assisted-reversingbinary-analysisdebuggers+5
463
llnl/oghidraOGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 pr0me/xtride
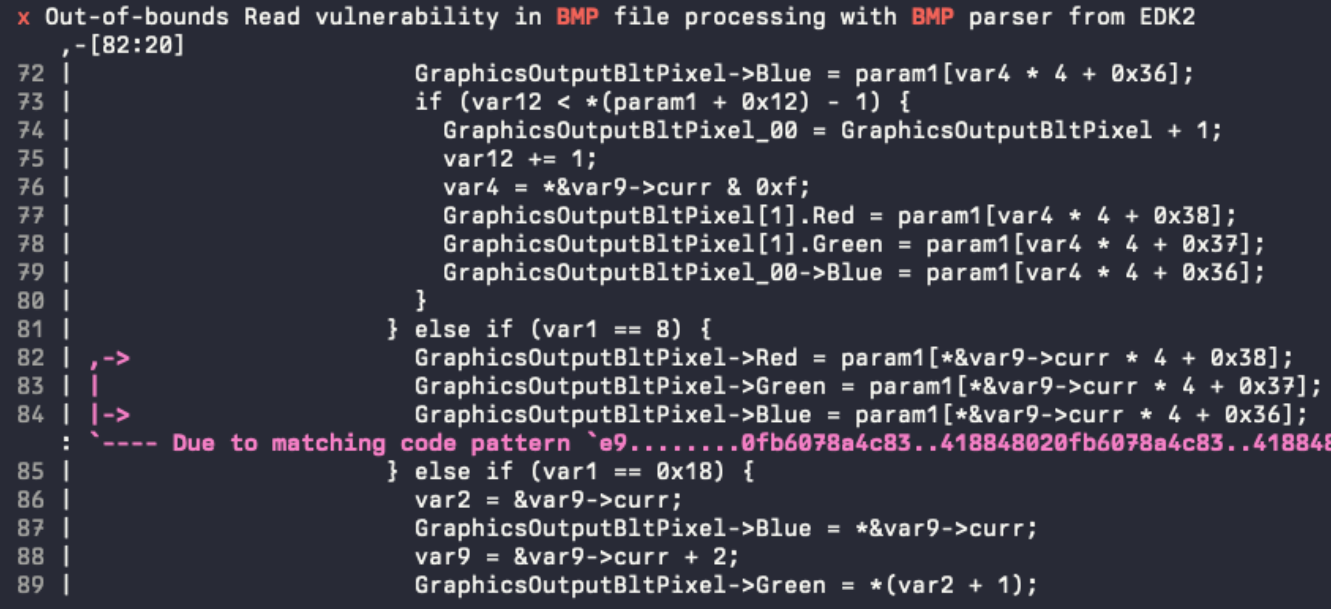
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 hydradragonantivirus/hydradragonantivirus
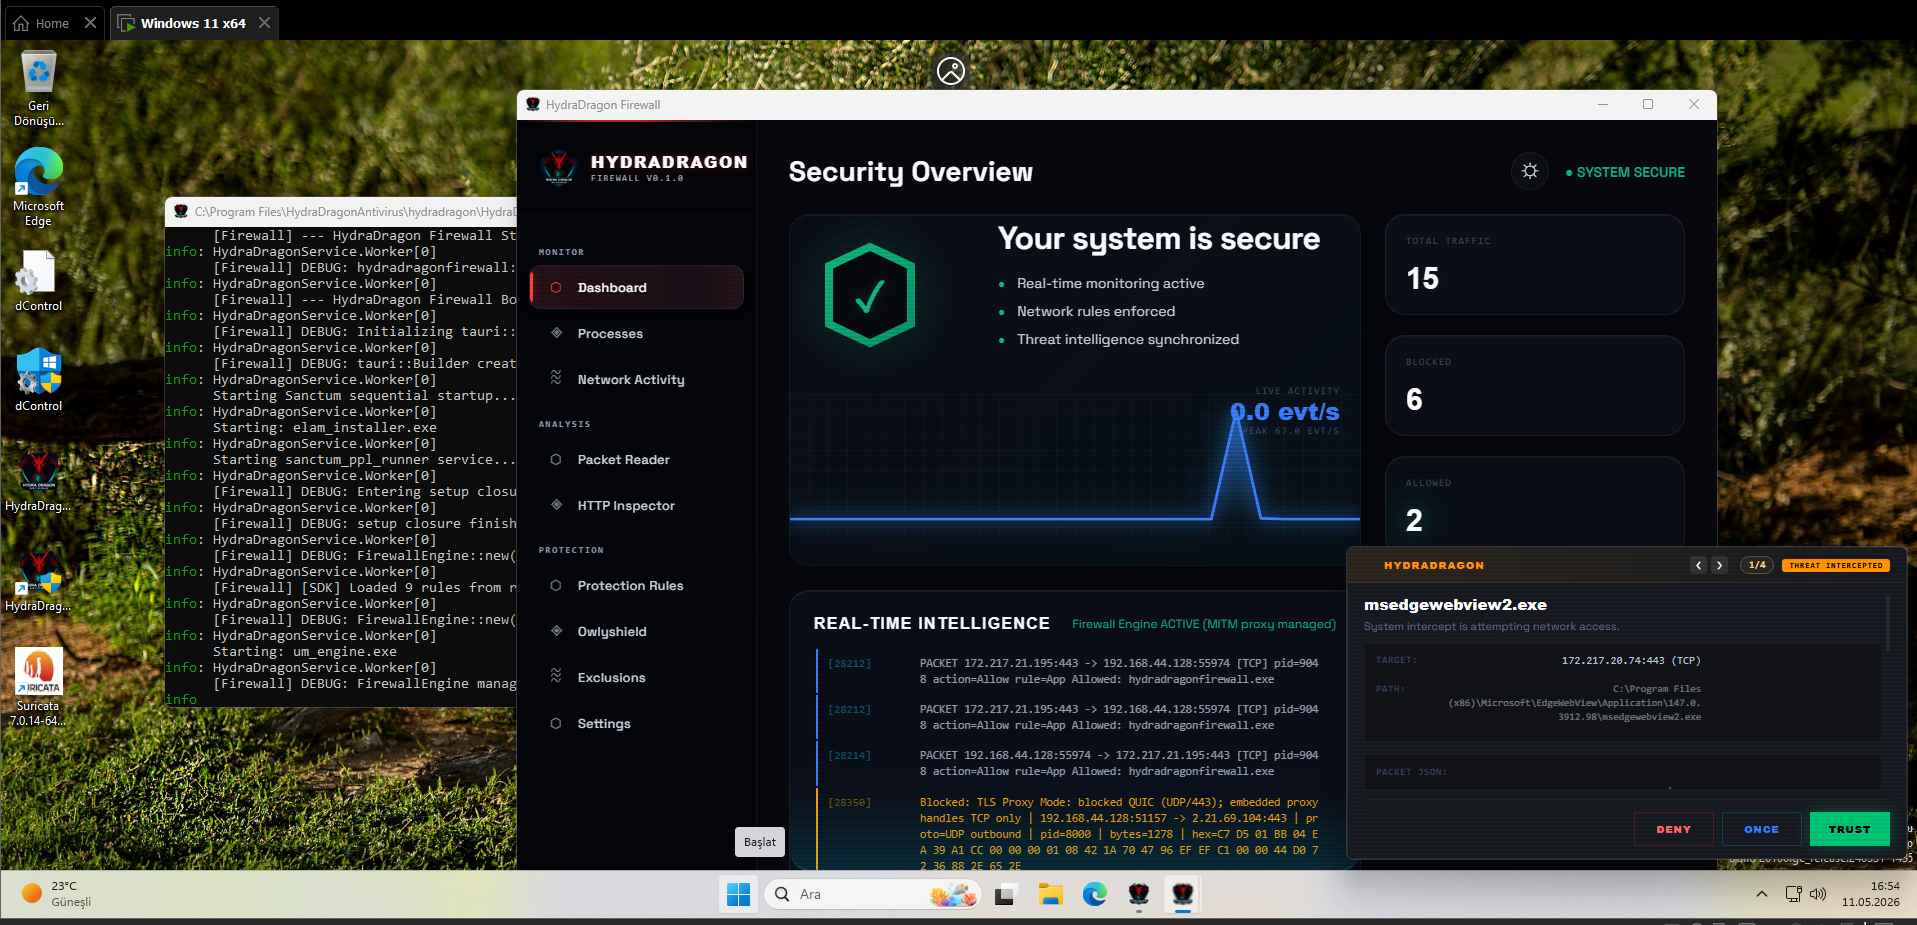
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 markoglasgow/gemma_crackme_tutorial
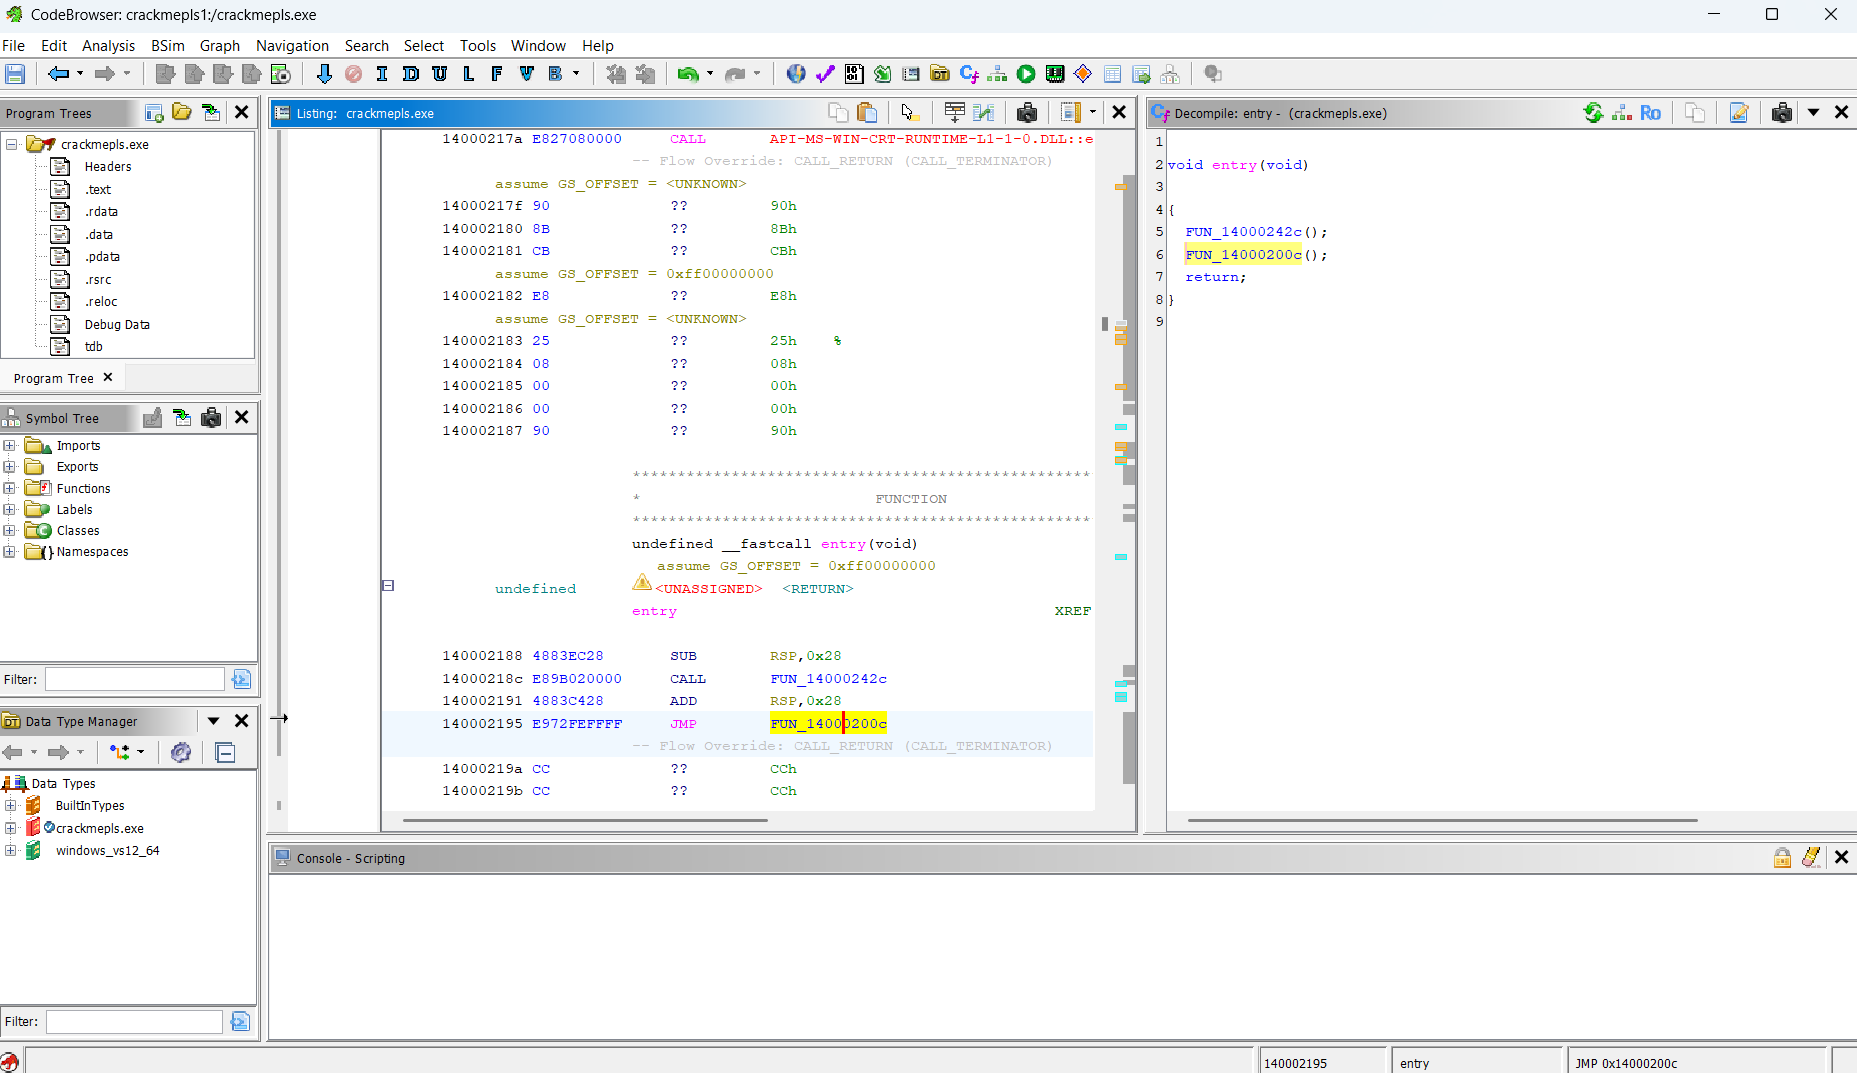
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…