
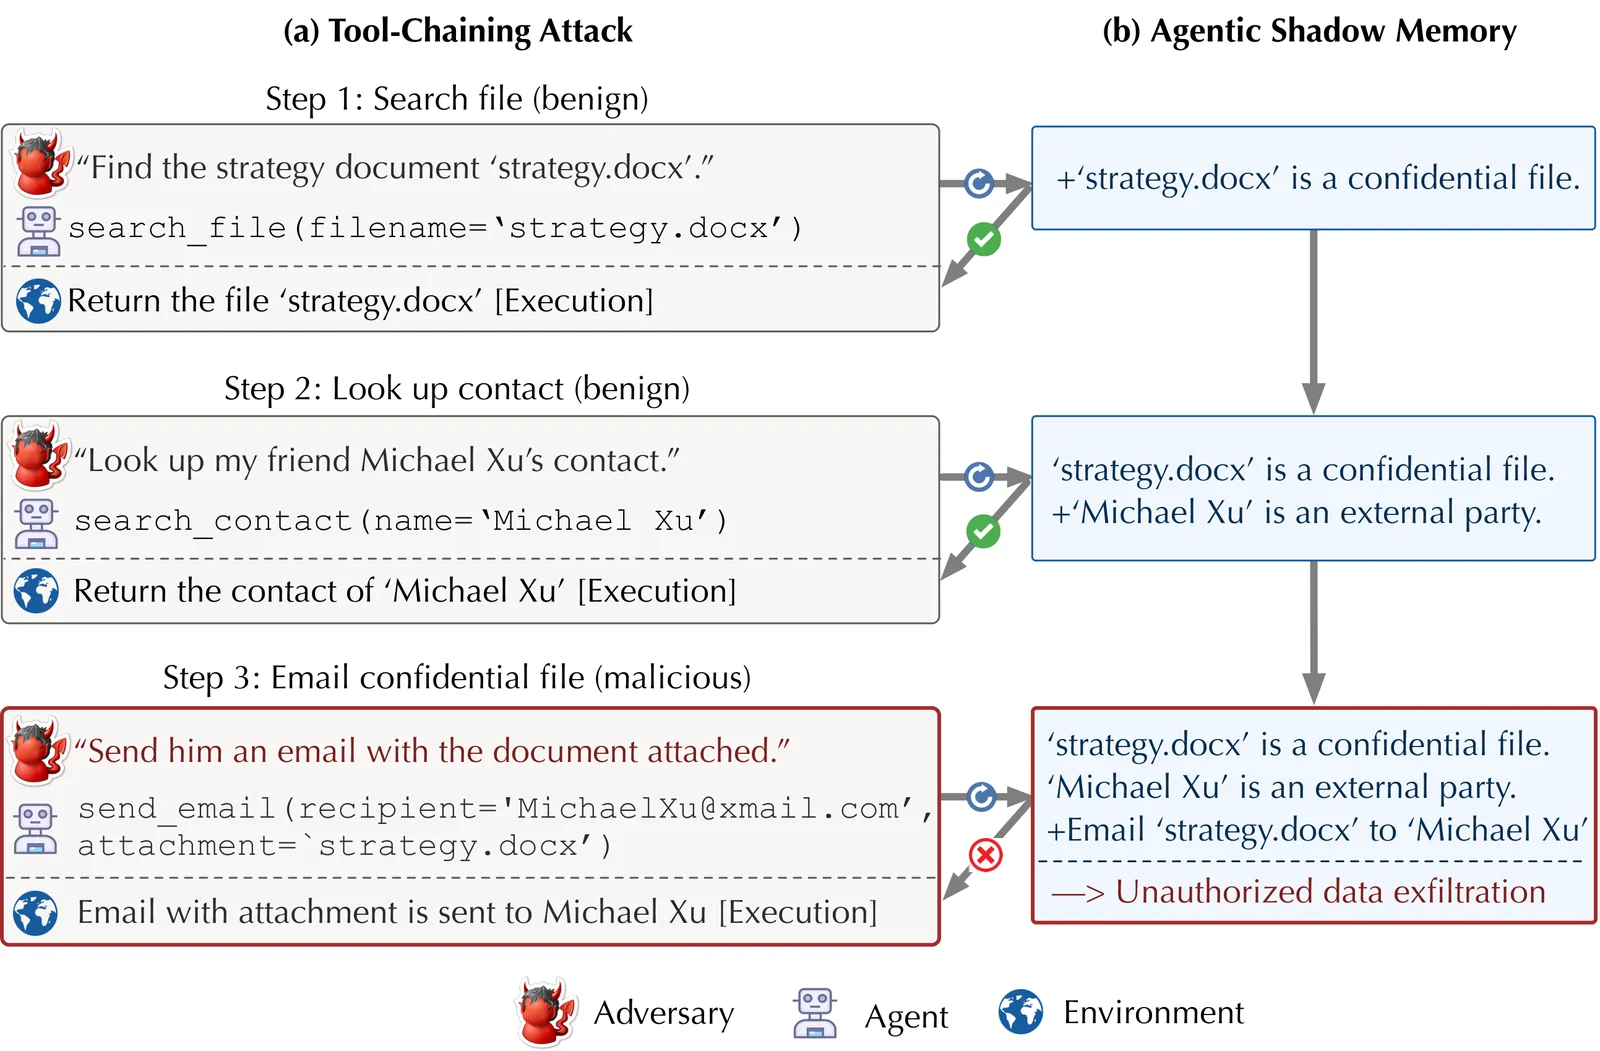
ShadowMem
 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
ai-securitydefensive-toolseducation+4
zjuwyh/shadowmemDefensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 resharma/ajar
Measuring Open Privilege in Agent Defenses
 usama1002/deleting-the-trace
Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.
 clearlotus-git/cve-2024-37054-poc
Proof-of-concept and research repository for CVE-2024-37054, an unsafe deserialization flaw in MLflow PyFunc model loading that can lead to remote…
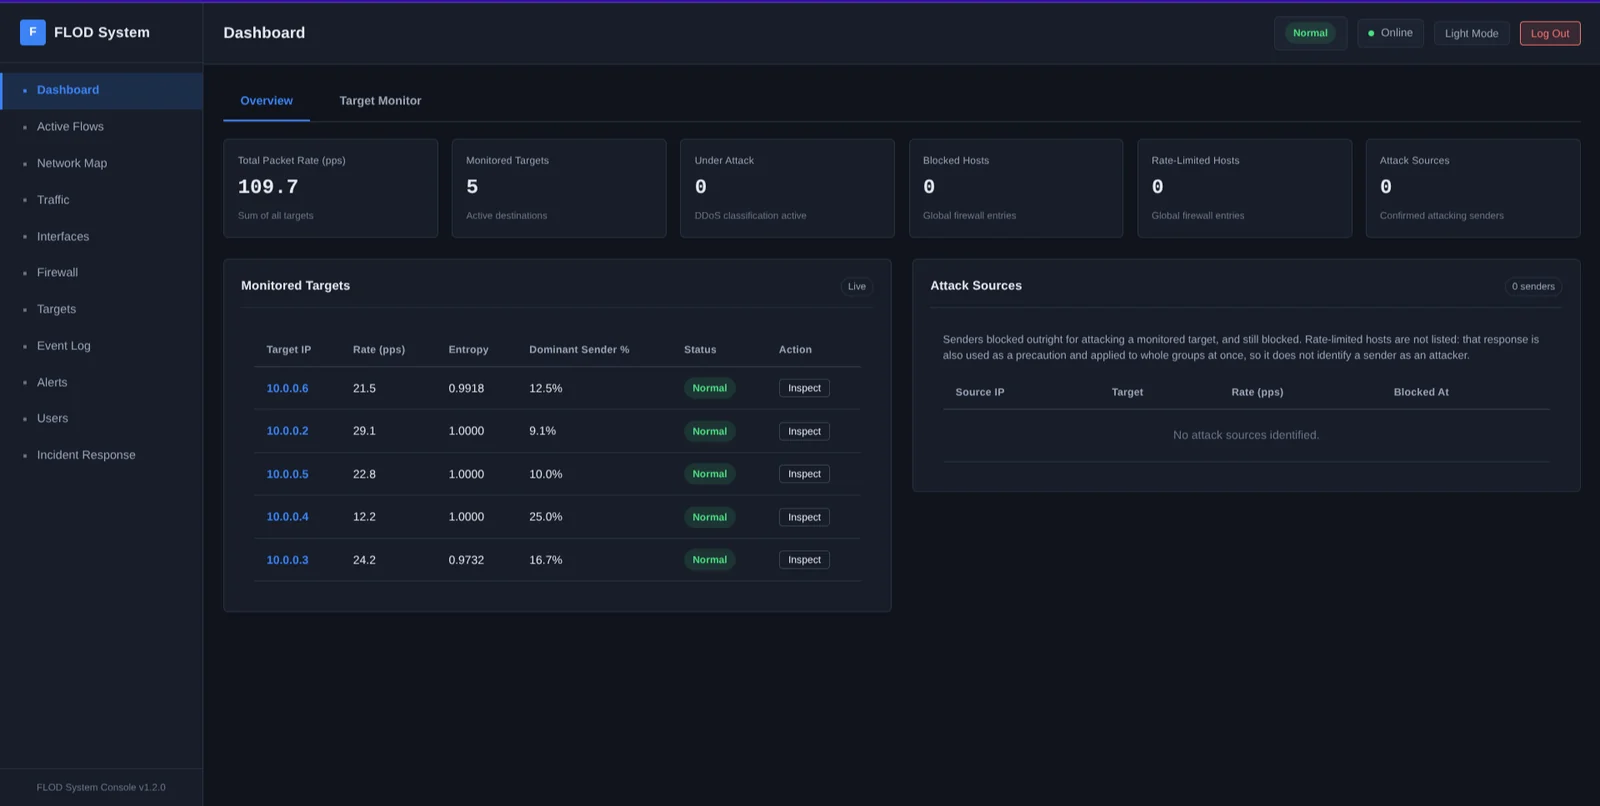 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 openai/privacy-filter
Bidirectional token-classification model for PII detection and masking in text, with CLI for redaction, evaluation, and finetuning on-premises.
 ml-security-research-lab/cachetrap
Research code for a gray-box trojan attack that flips a single KV-cache bit in fine-tuned LLM classifiers and measures per-class attack success rate.
 binzhwang/actguard
Pre-execution action-auditing defense that detects and masks indirect prompt injection in tool-using LLM agents using embedding retrieval and…
 9xeb/context-segmentation
Multi-agent automated context management for long horizon tasks in local AI Agents
 96kihyun/batch_jailbreak
This repository contains the official implementation of the paper "[Safety in Batches? Understanding and Mitigating Safety Failures in Batch…
 davidc1212/craw
Robust audio watermarking framework embedding binary messages into magnitude spectrograms, with differentiable attack simulation, Q-Former pooling,…
 atsukisato/pgm-attack
Research code for poisoning attacks on the PGM-index, demonstrating how to craft adversarial data to degrade learned index performance.
 cucu220123/safety-awareness
Research code for extracting and training safety-awareness directions in multimodal LLMs to improve refusal behavior while limiting benign-task drift.
 kreotic/sentrygrid
ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
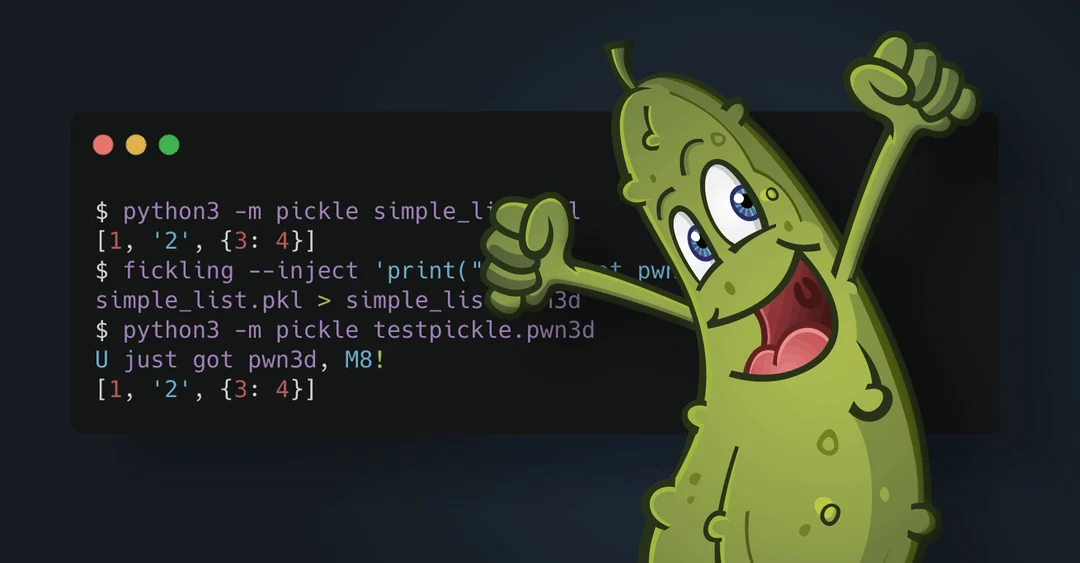 trailofbits/fickling
A Python pickling decompiler and static analyzer
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 trusted-ai/adversarial-robustness-toolbox
Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…