
byvalver
 umpolungfish/byvalver
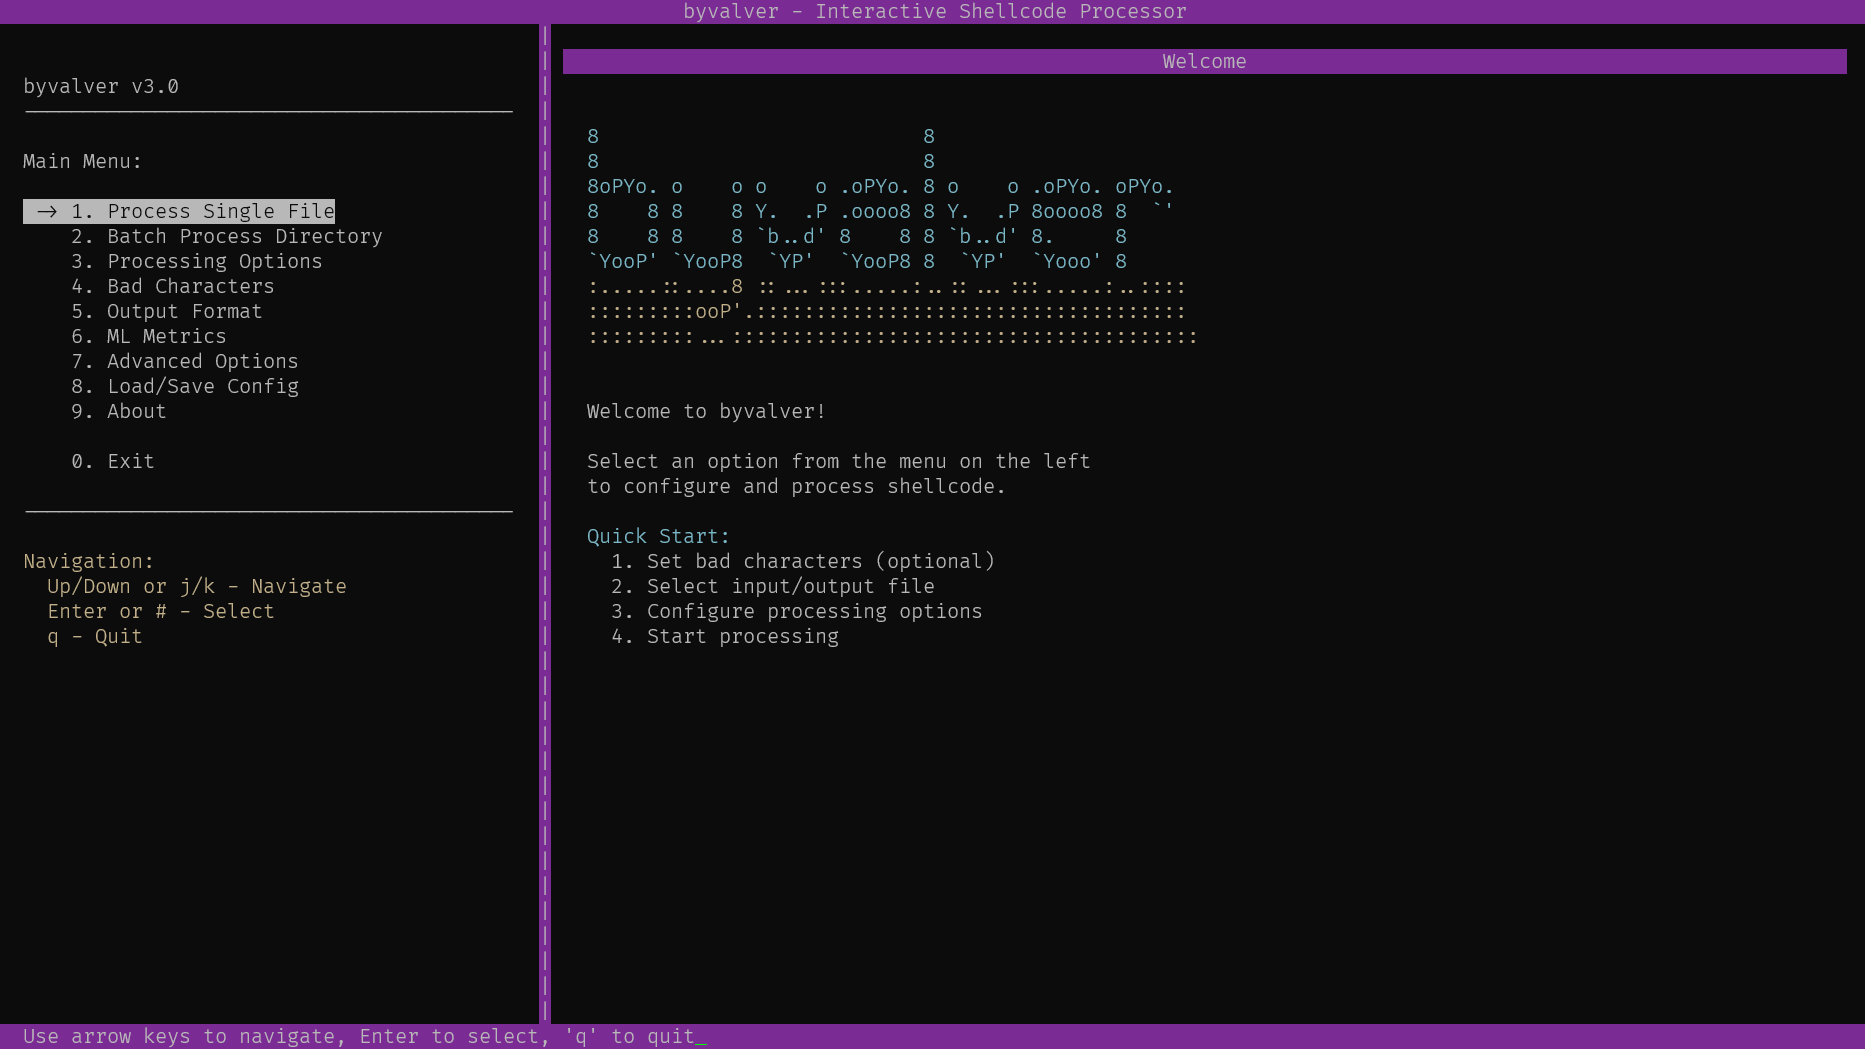
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
binary-analysisexploitationmachine-learning+6
62
umpolungfish/byvalvertakes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…