adversarial-robustness-toolbox

Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…

Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…

YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…

A unified framework for privacy-preserving data analysis and machine learning

AI-curated blocklist of 3,000,000+ domains for blocking ads, trackers, malware, and cryptojacking. Integrates with hosts files, Pi-hole, and browser…

Evades LLM text watermarks by injecting Unicode variation selectors; includes the SynthID generator, mean-g detector, normalization defenses, and…

EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…

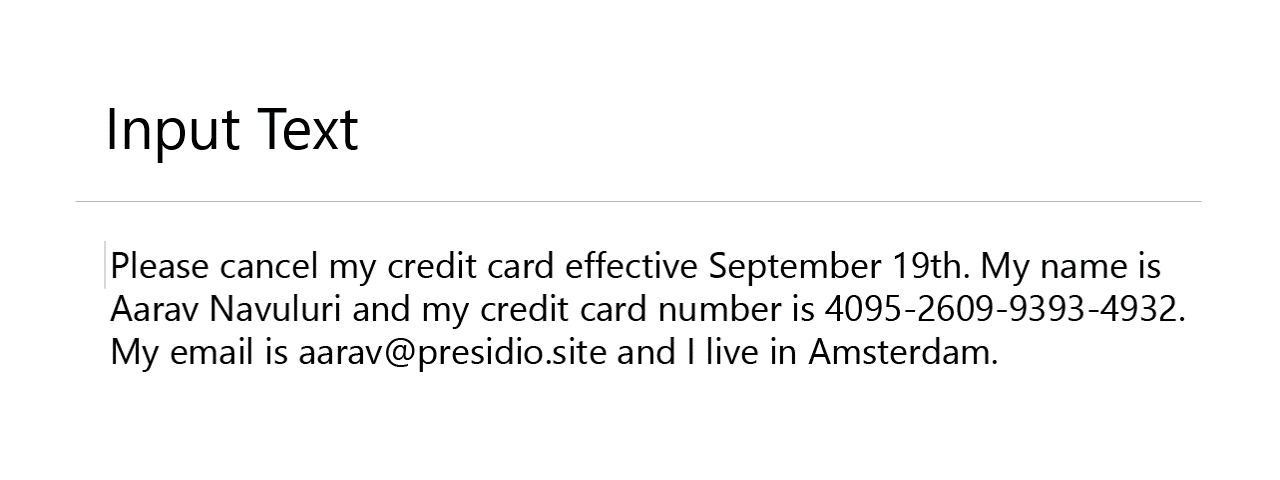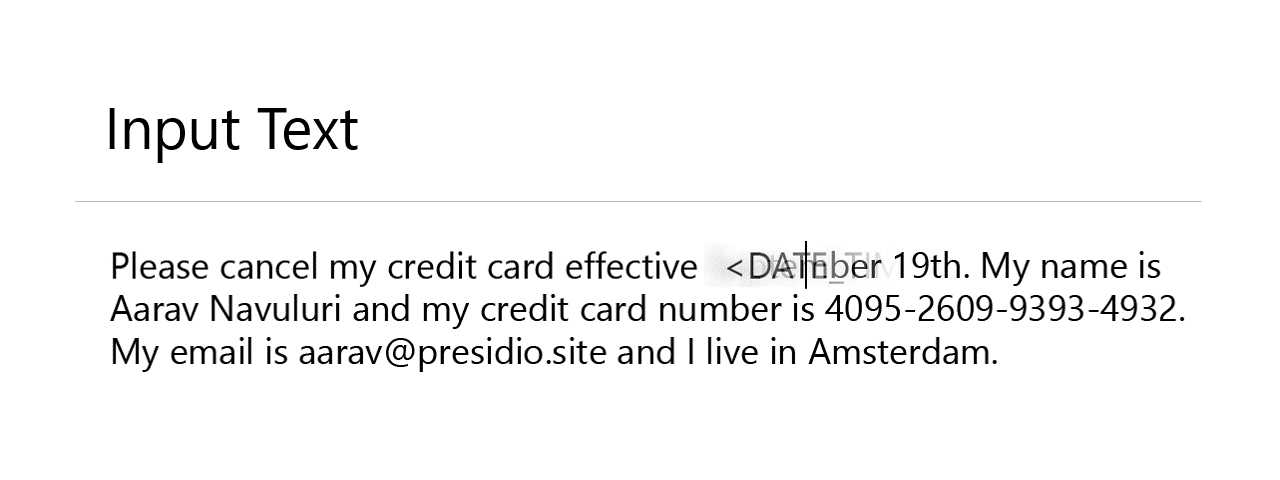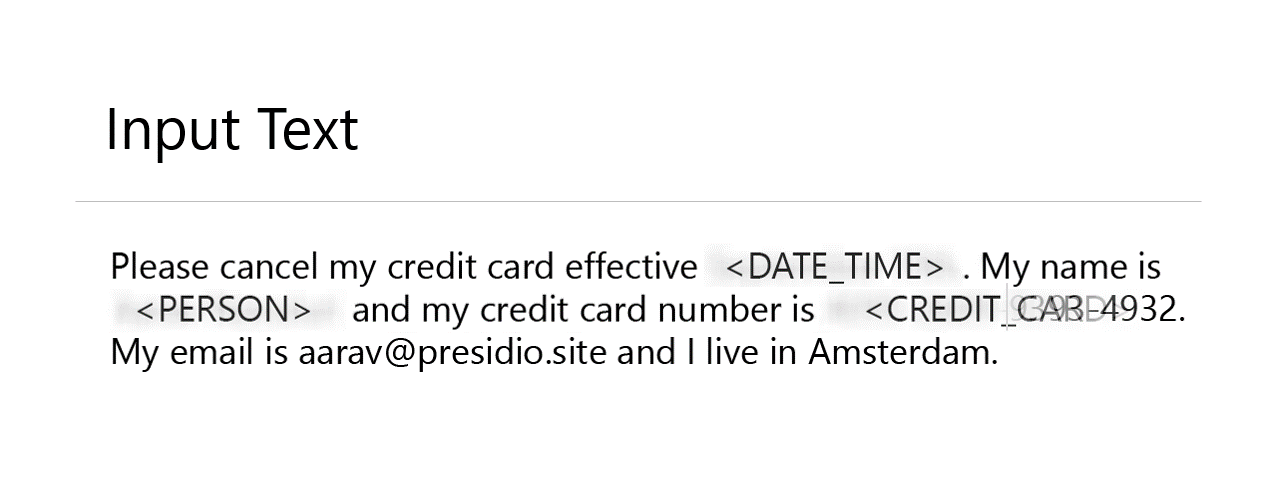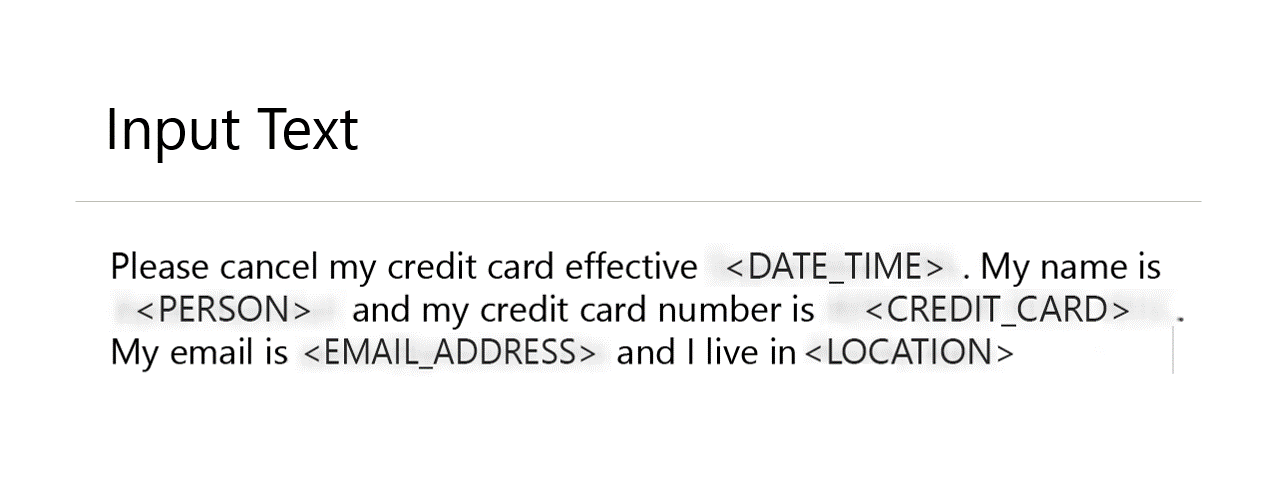
An open-source framework for detecting, redacting, masking, and anonymizing sensitive data (PII) across text, images, and structured data. Supports…

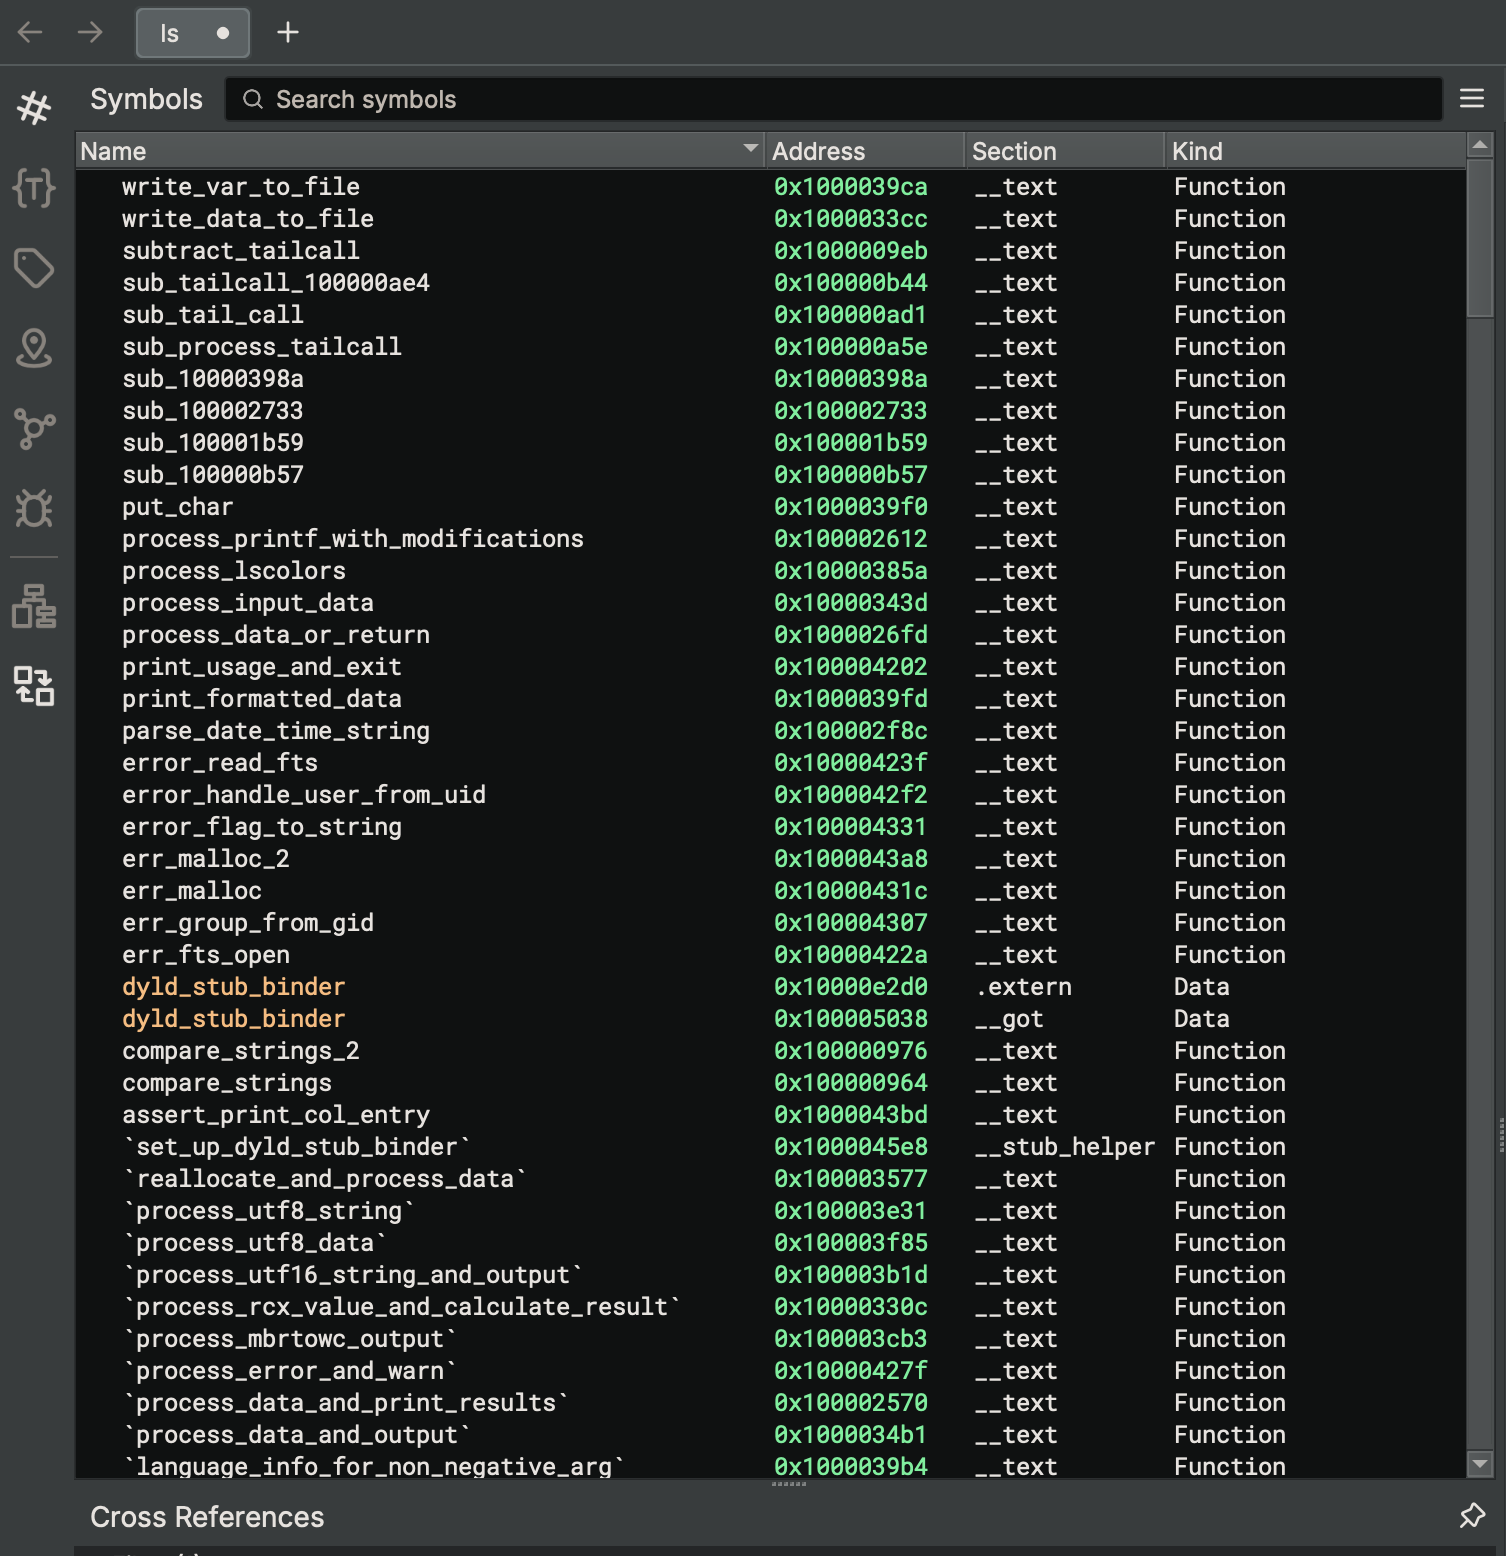
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…

QuantumLock is an open-source, quantum-resistant Bitcoin protocol designed to protect digital assets from future quantum computing threats. Featuring…

Reverse of OpenAI Privacy Filter: same 1.5B model, returns PII as structured spans instead of masking.

Privacy testing library for deep learning systems, enabling assessment of susceptibility to membership inference, model extraction, and model…

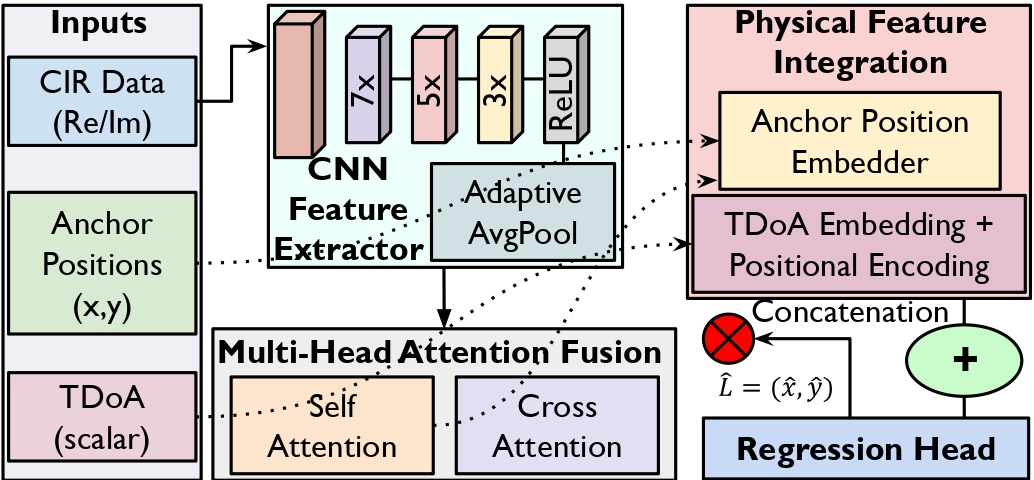
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…

This project (PoC for now, and part of Shit Bucket) involves face detection, face recognition and adversarial input to protect avatars