

garak
 nvidia/garak
Modular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
adversarial-attackai-securityeducation+5
9.6k3 days ago
nvidia/garakModular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 mazen160/shennina
Automating Host Exploitation with AI
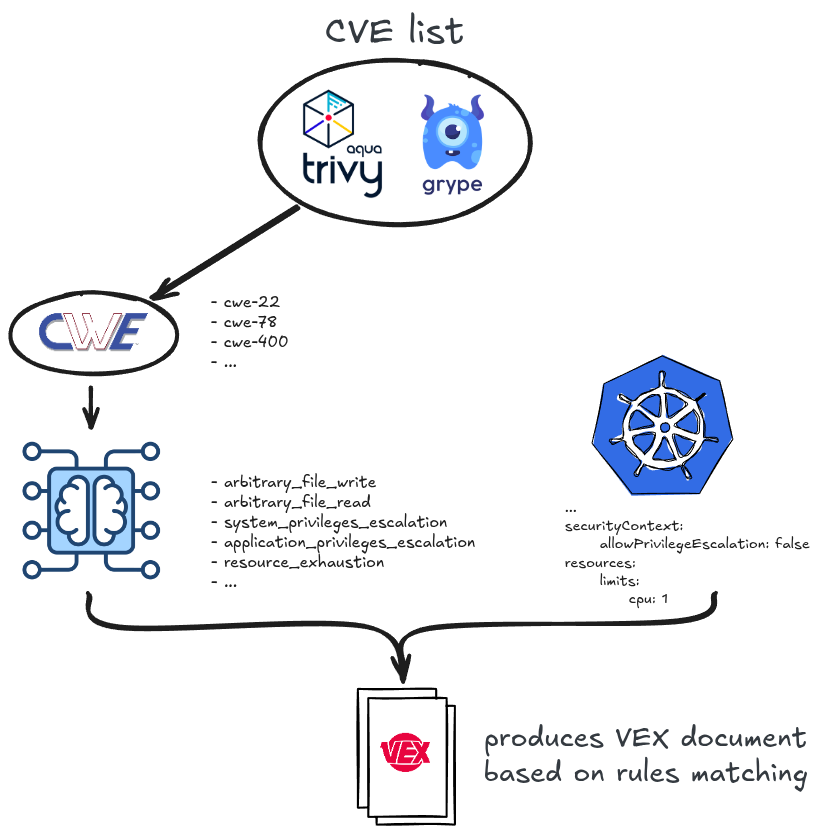 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
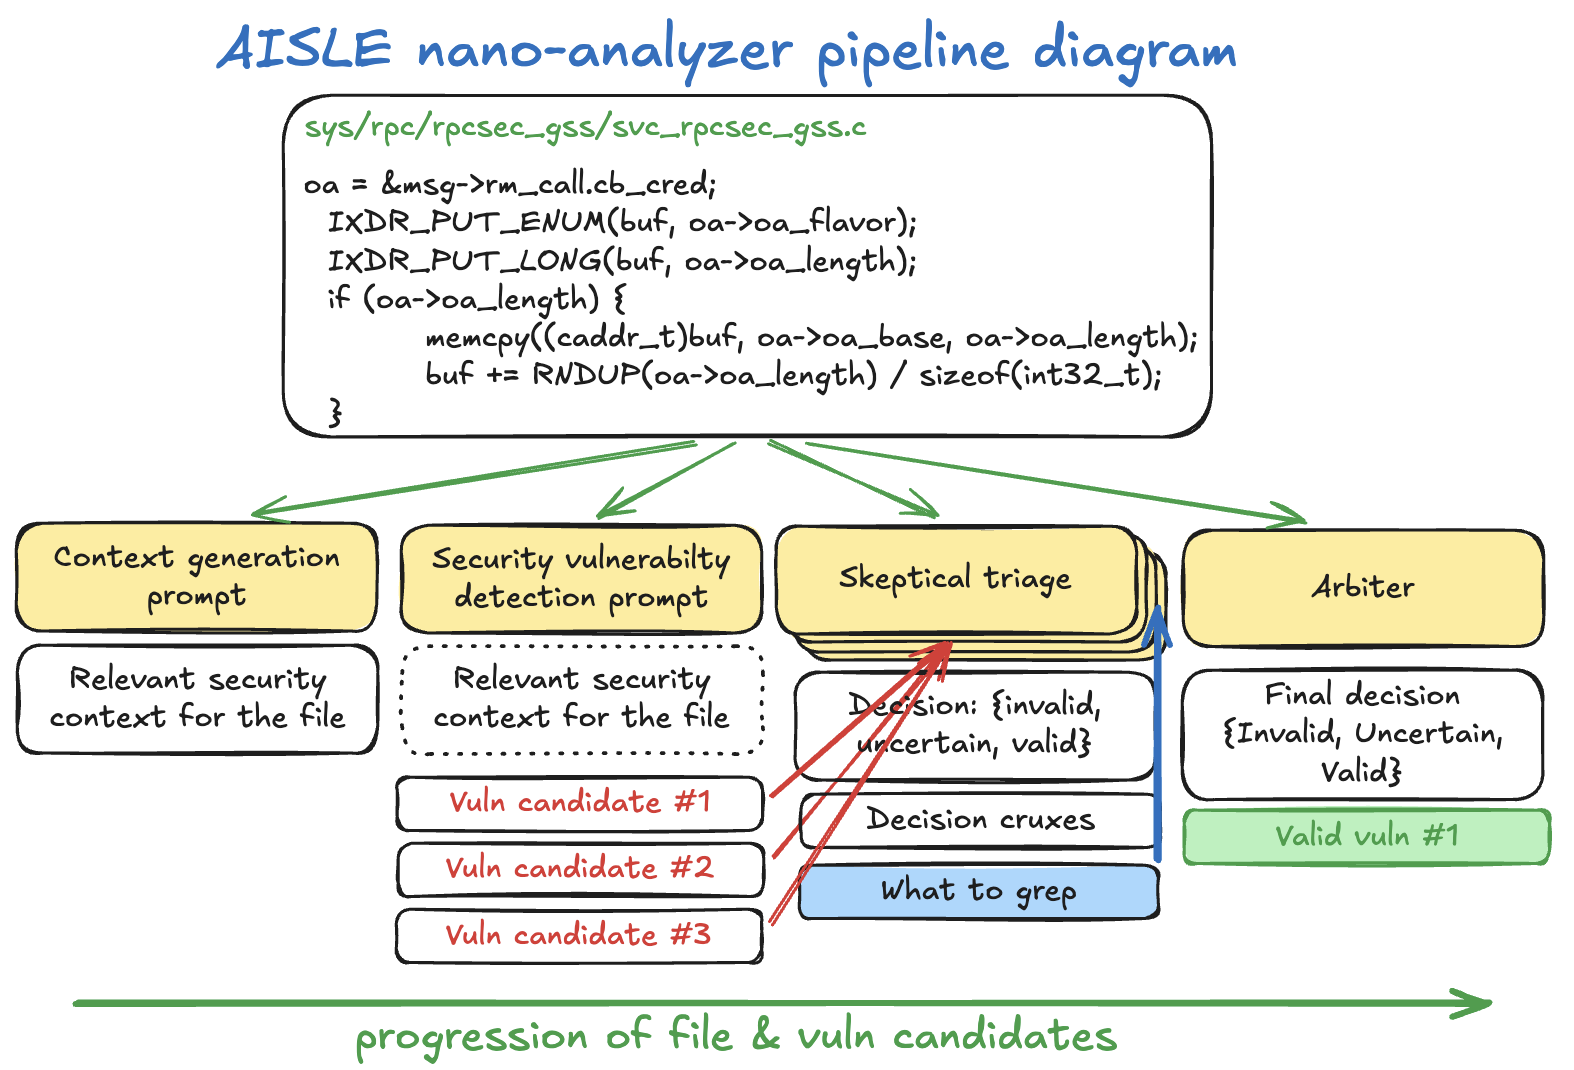 weareaisle/nano-analyzer
A minimal LLM-powered zero-day vulnerability scanner by AISLE.
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 j4fsec/in0ri
Website defacement attack detection with deep learning
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
 skac44/cve-2024-38063
Simulates CVE-2024-38063 TCP/IP remote code execution attack, captures network traffic with TShark, and trains a machine learning model to detect…
 hh-hunter/ml-cve-2023-1177
Machine learning-based exploit for CVE-2023-1177 vulnerability, enabling automated security testing and exploitation of the identified flaw.
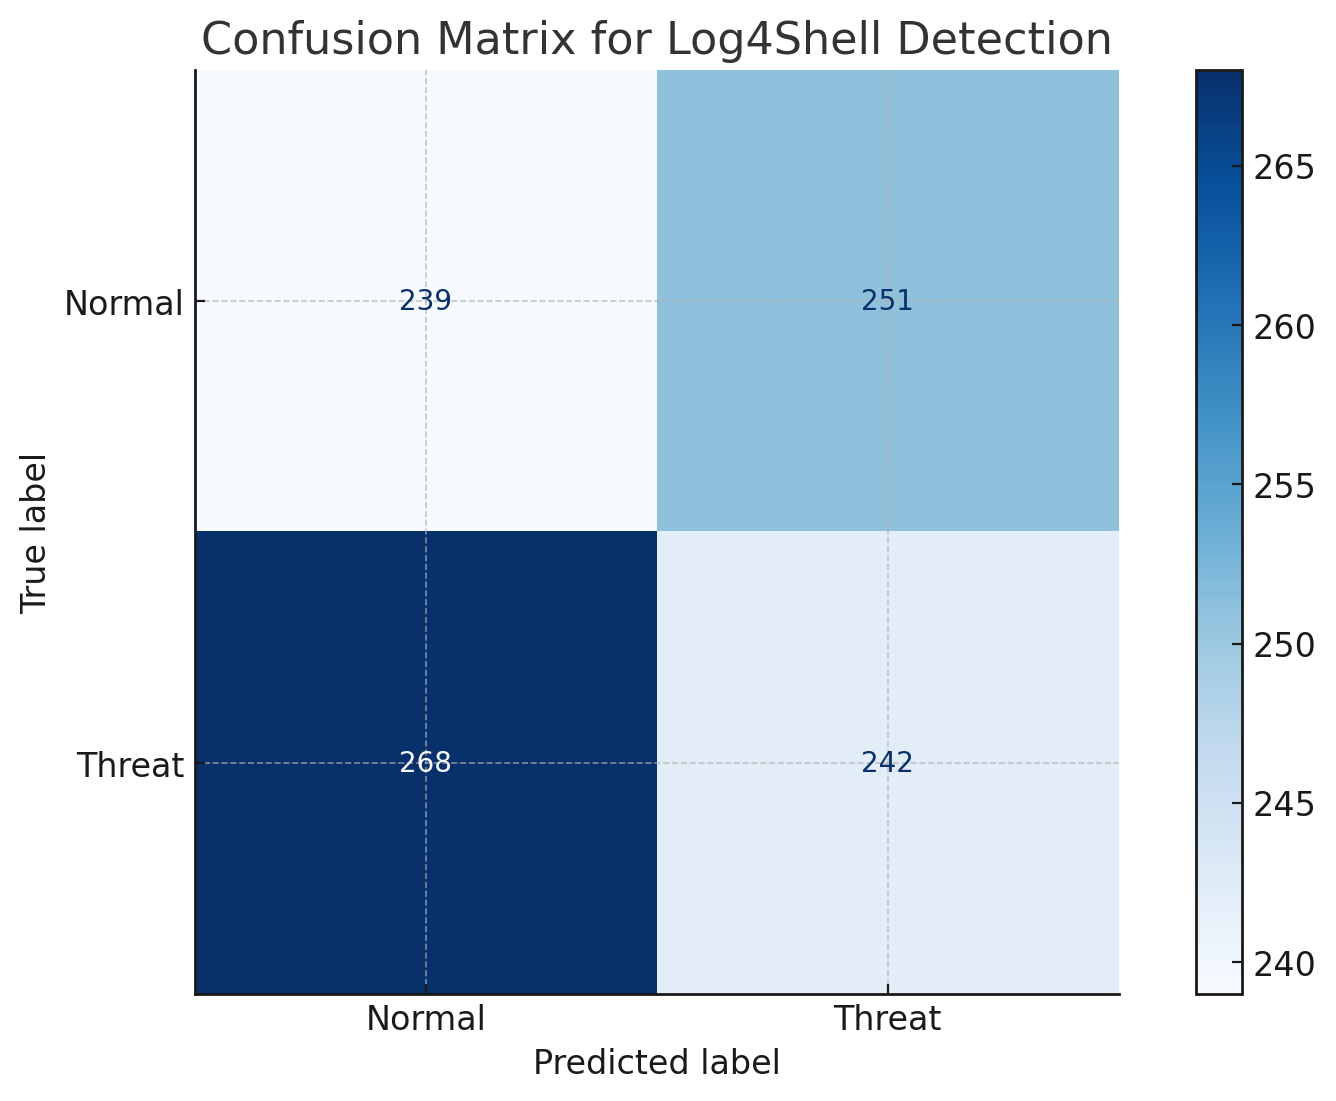 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…