
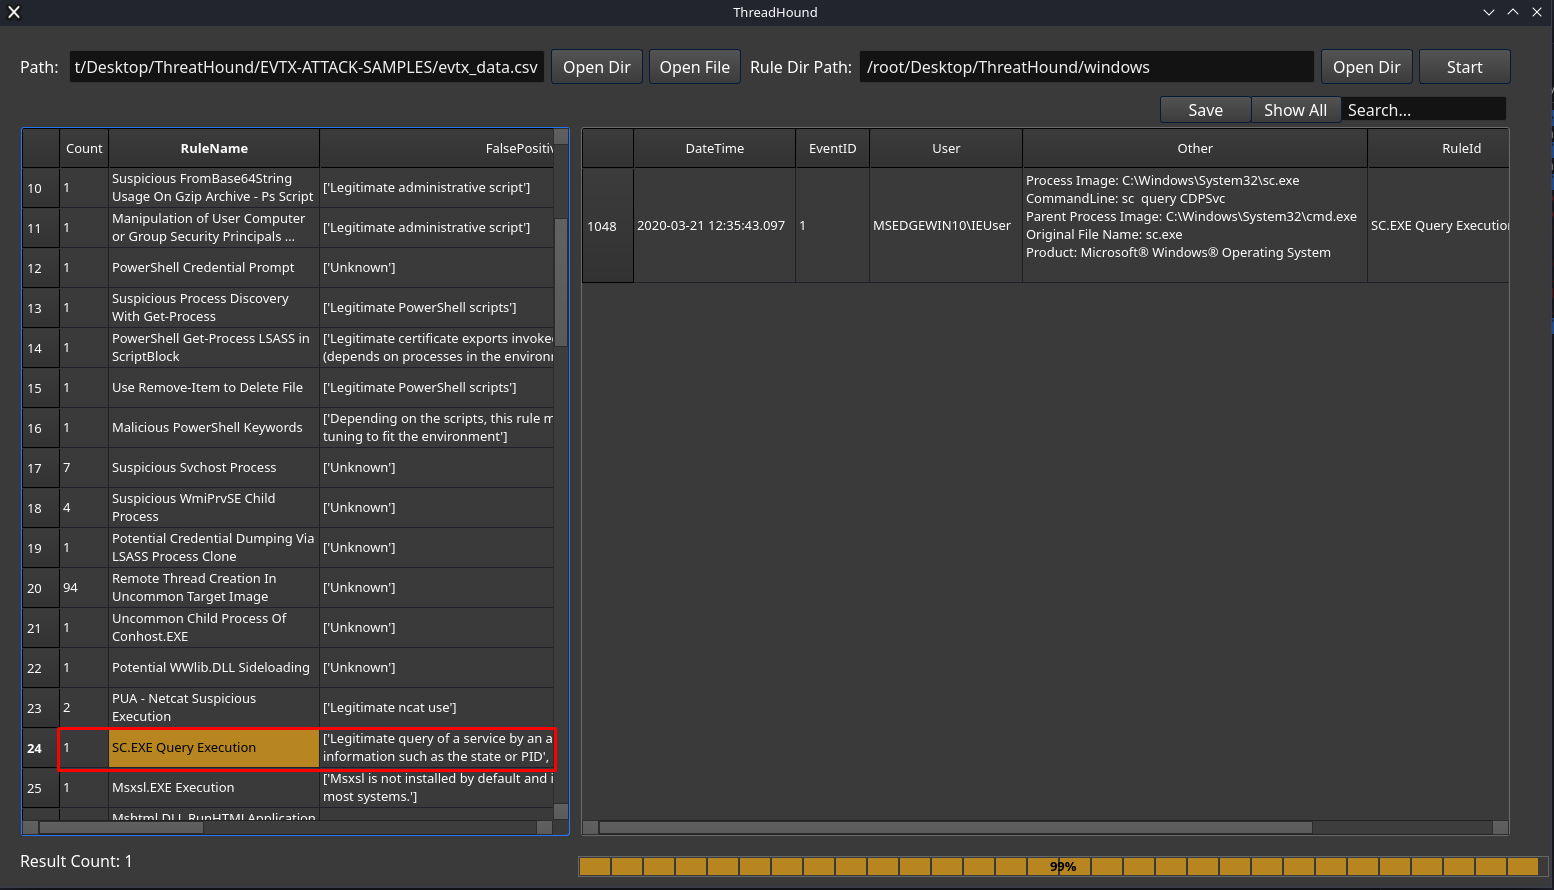
ThreatHound
 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
159
mazx0p/threathoundAutomated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
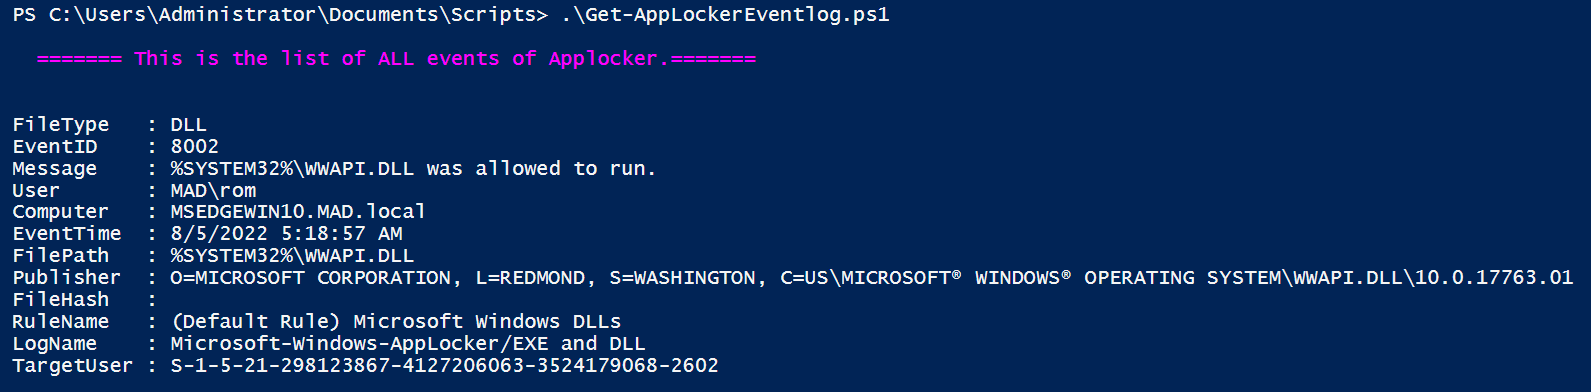 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 corelight/ecs-mapping
Mapping Corelight or Zeek data to Elastic Common Schema fields