
QLOG
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
defensive-toolsforensicsincident-response+1
44
threathunters-io/qlogETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
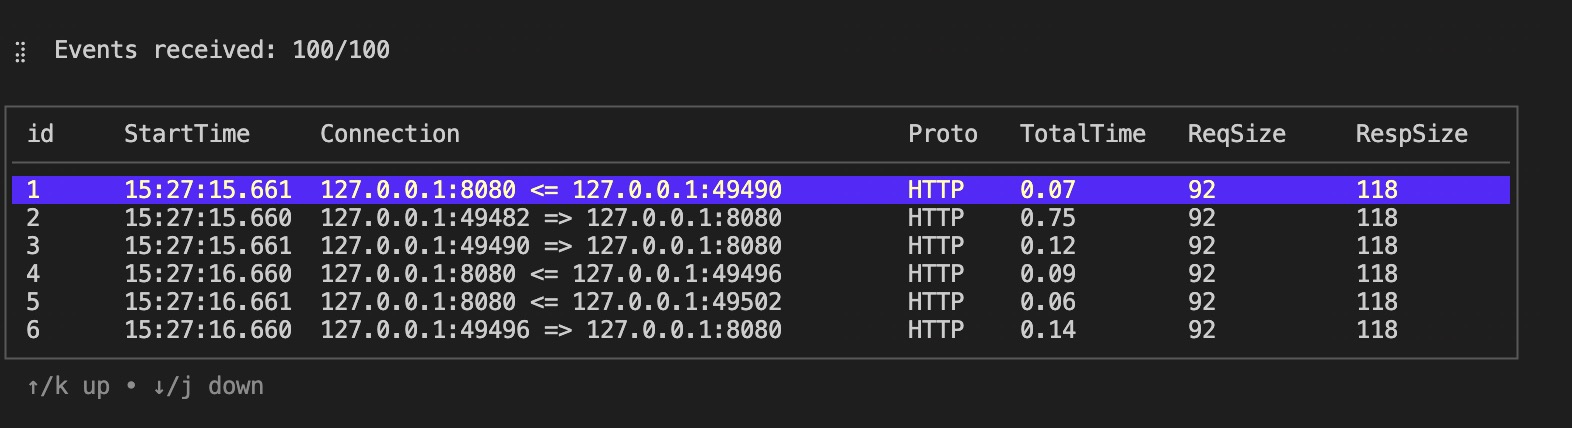 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…