

ARTIF
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
information-gatheringintrusion-detectionioc-management+5
251
cred-club/artifAn advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
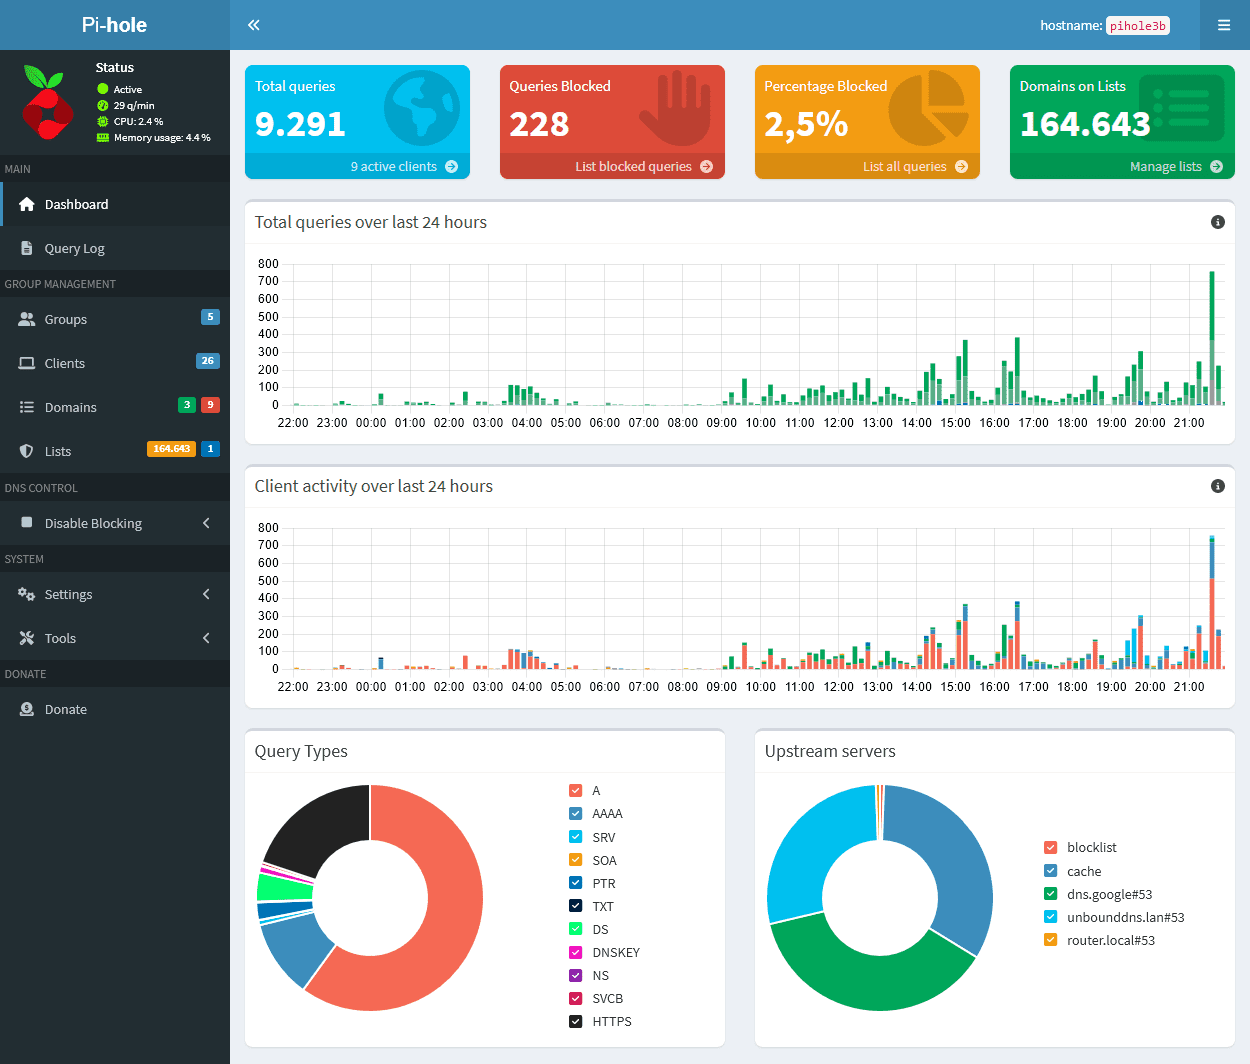
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
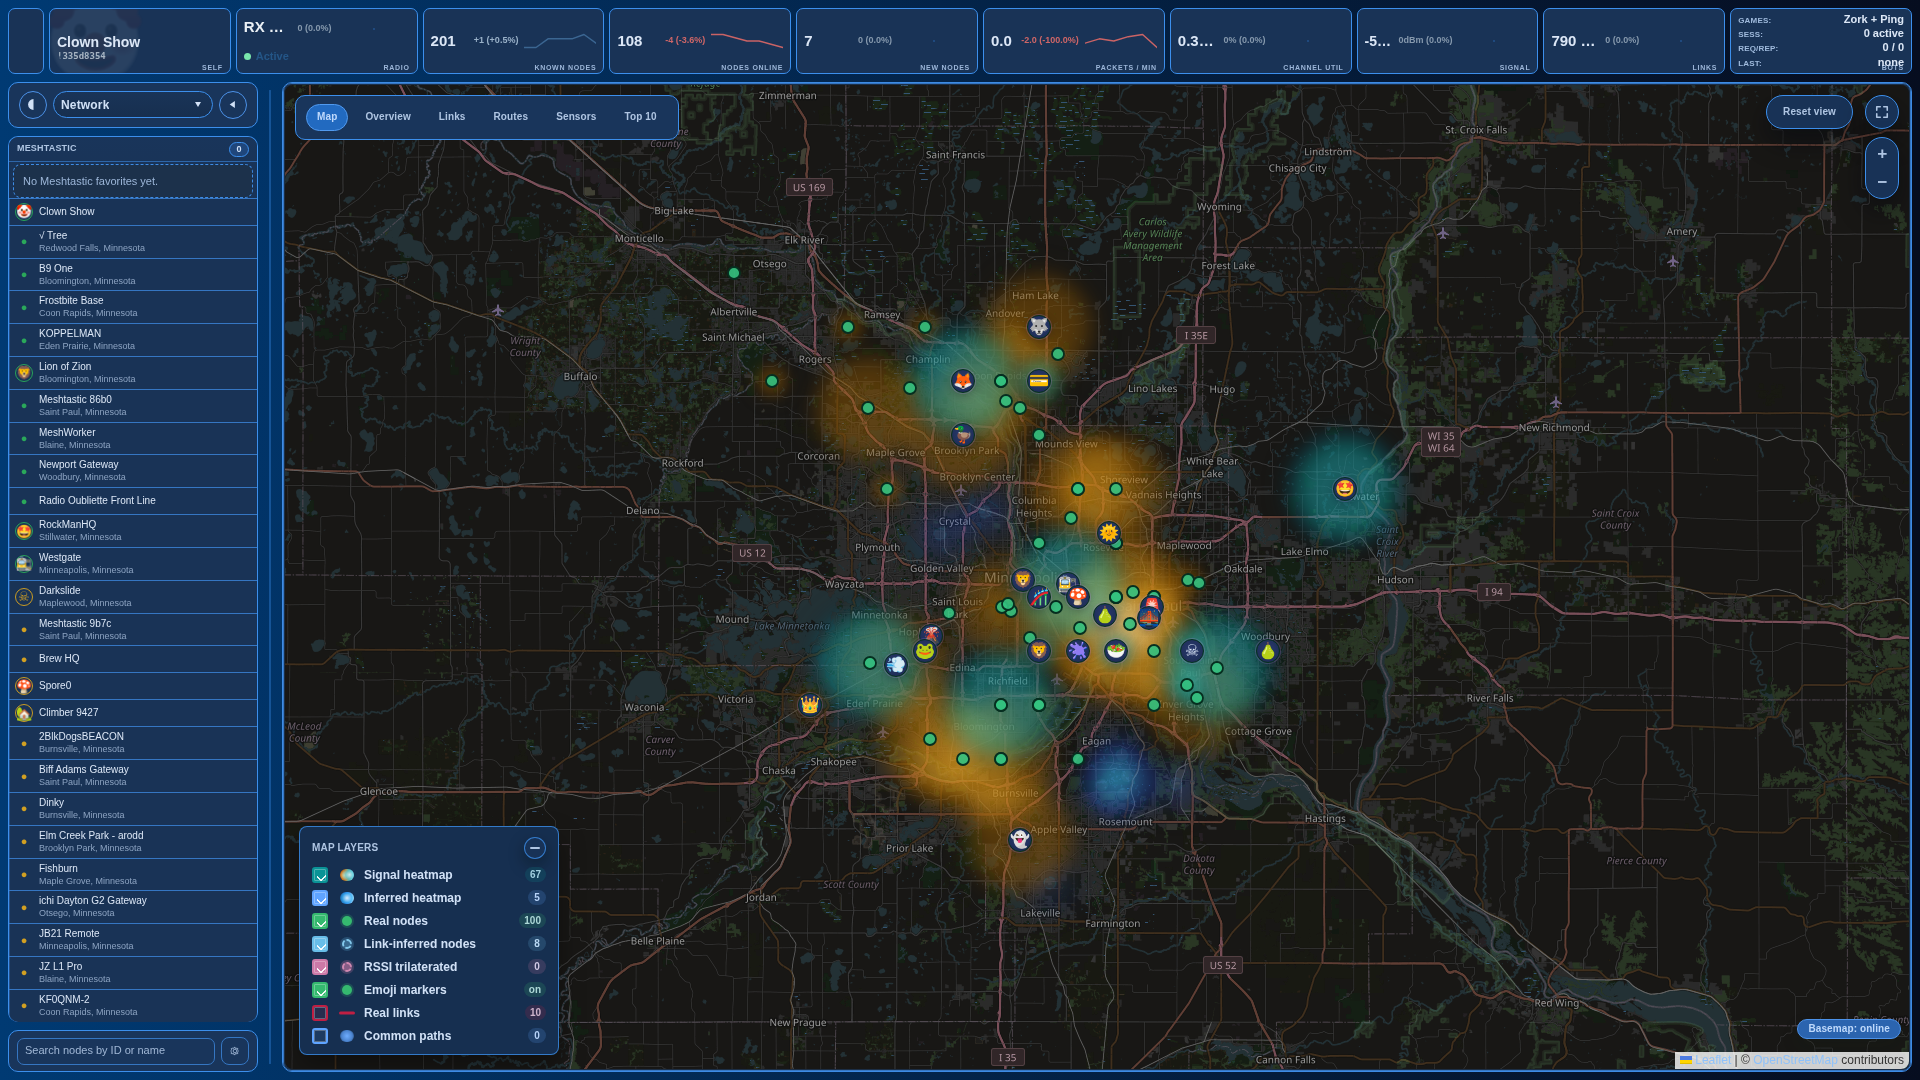 jaronmcd/meshyface
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…
 pedrofbrm/apache-web-log-analysis-lab
Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
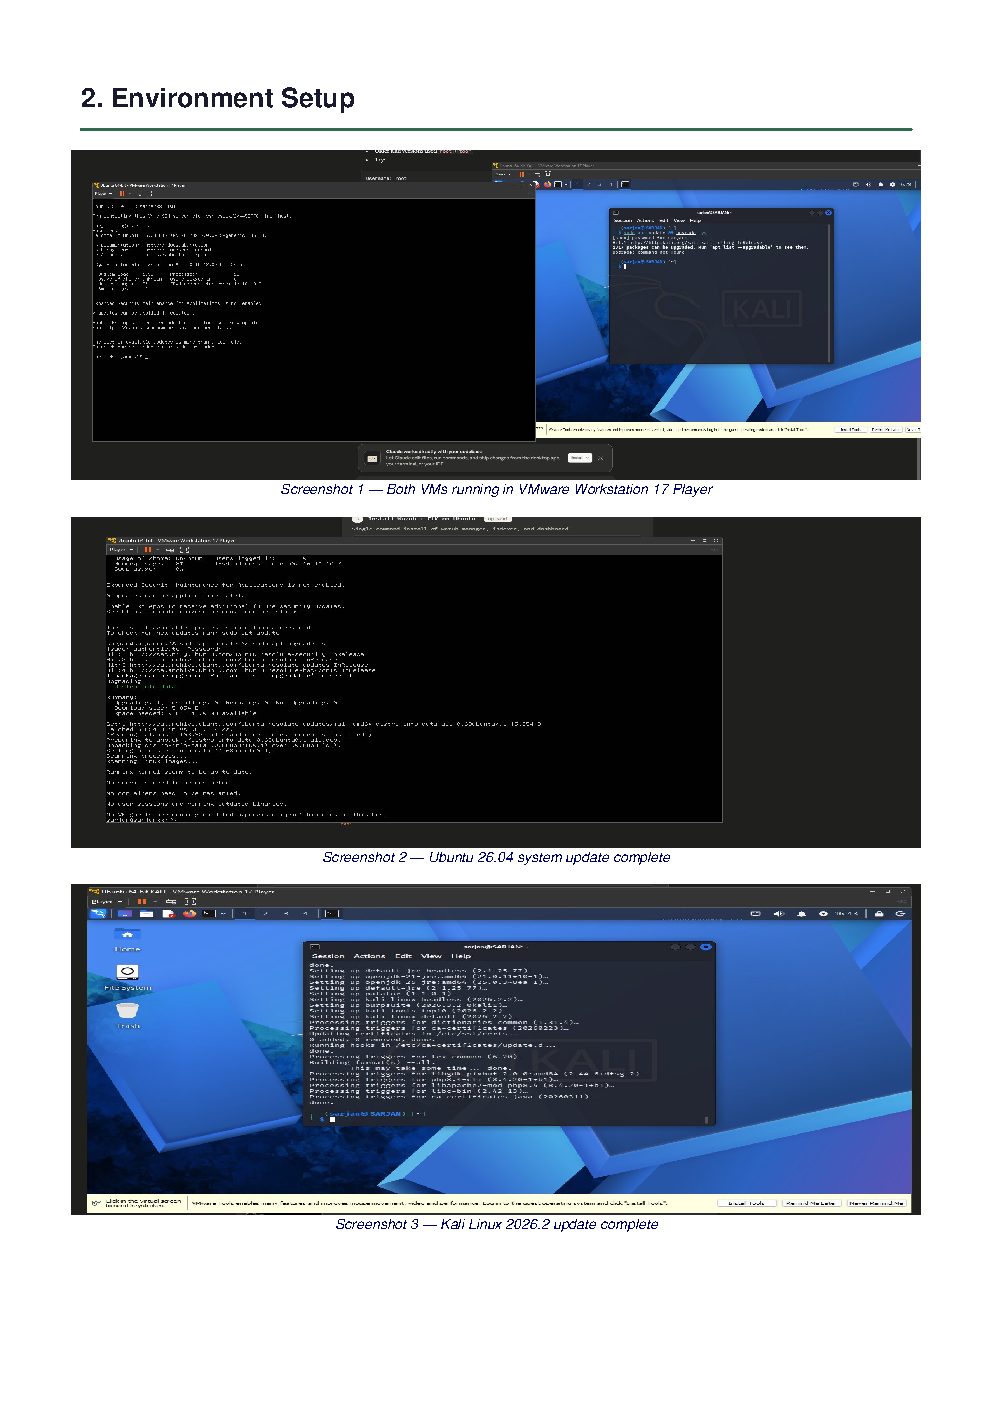 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
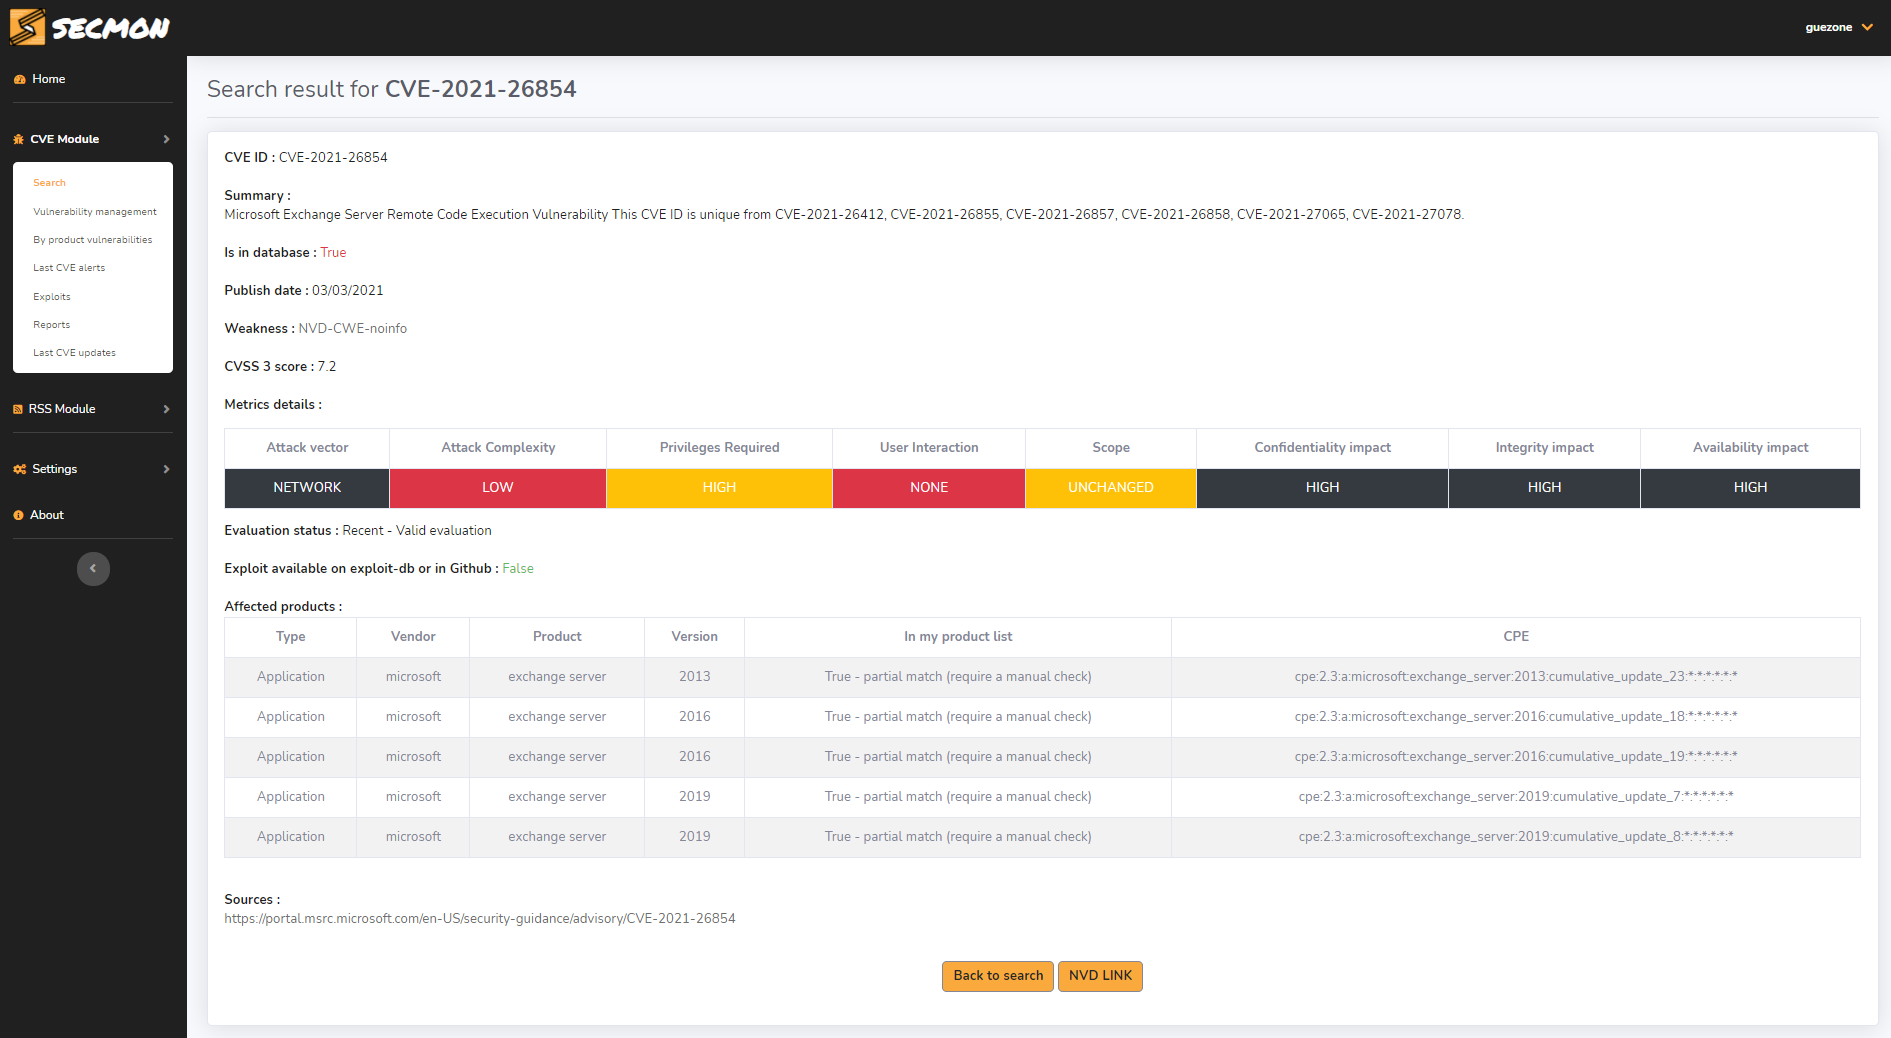 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
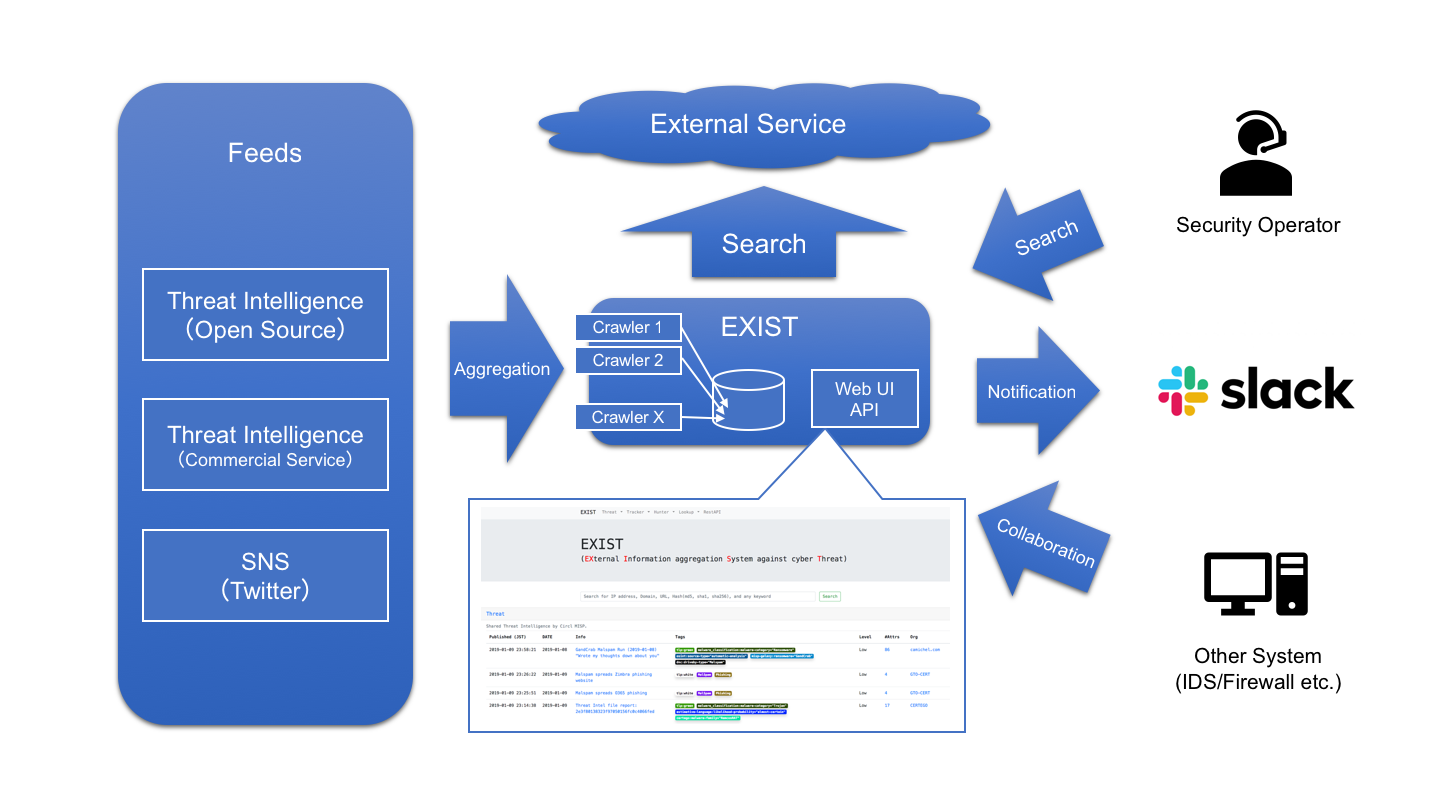 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 ghostop14/sparrow-wifi
Next-Gen GUI-based WiFi and Bluetooth Analyzer for Linux