
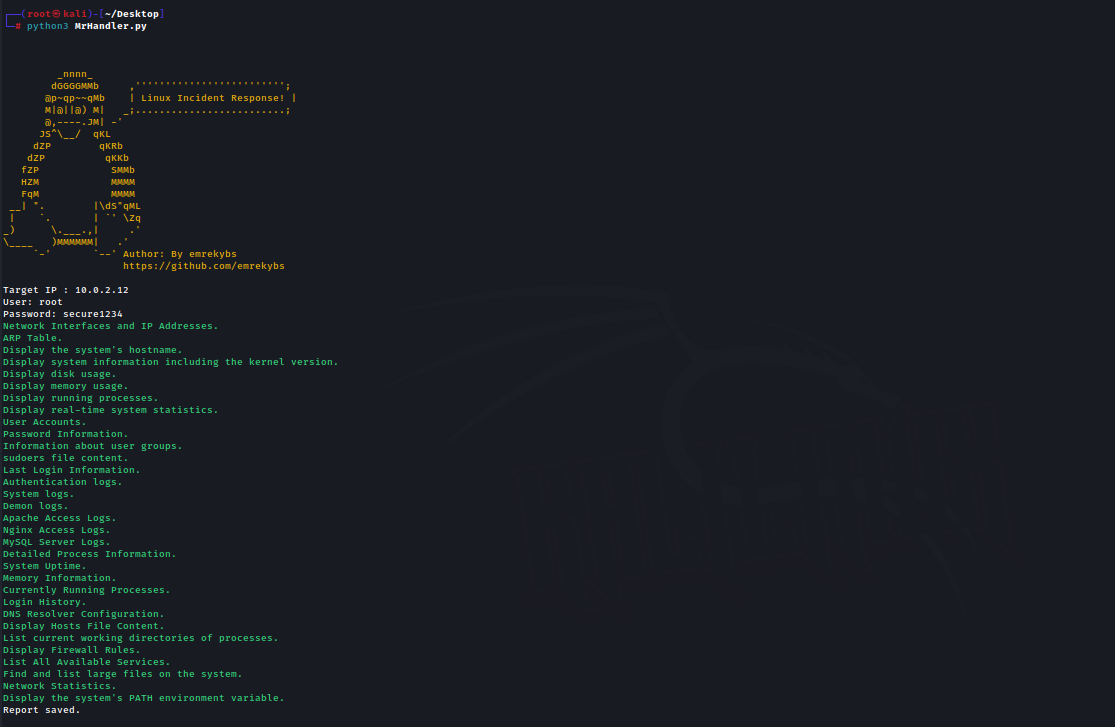
MrHandler
 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
digital-forensicsforensicsincident-response+1
86
emrekybs/mrhandlerSSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
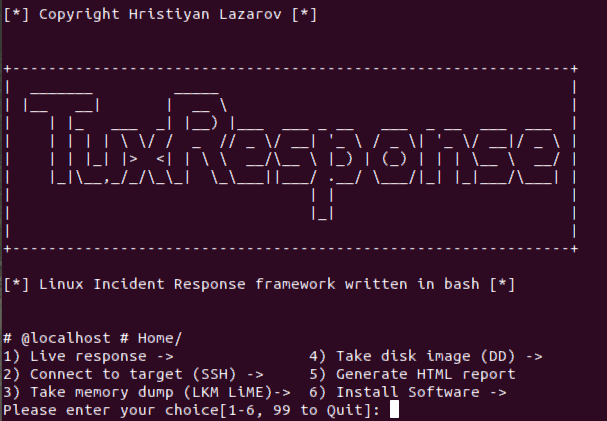 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 msuhanov/easy_triage
Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
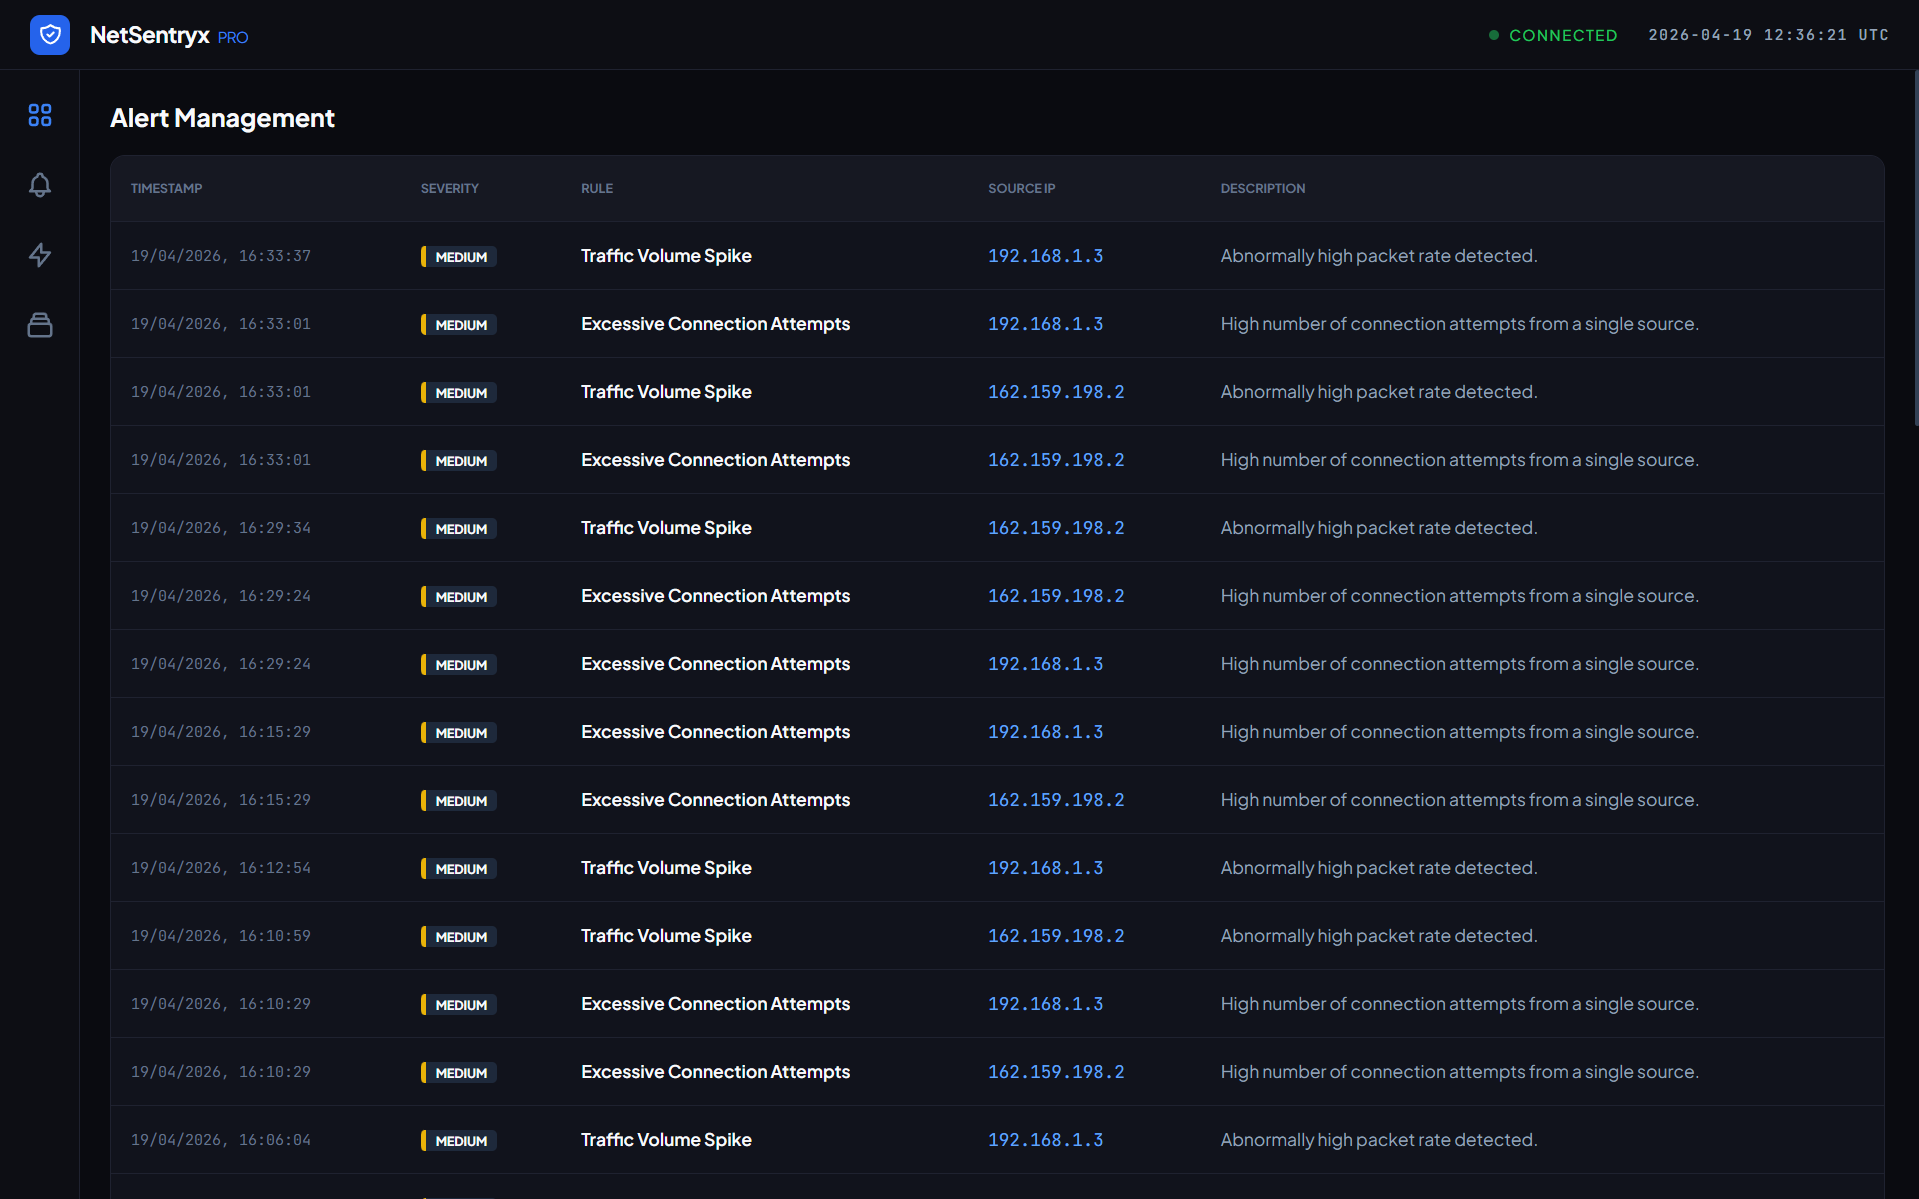 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
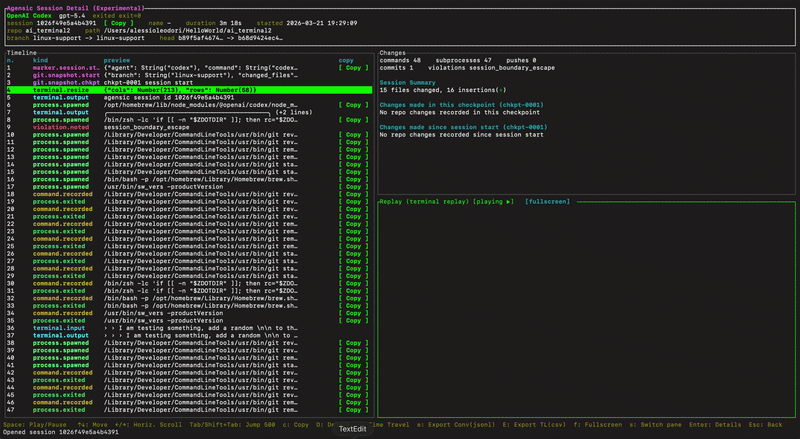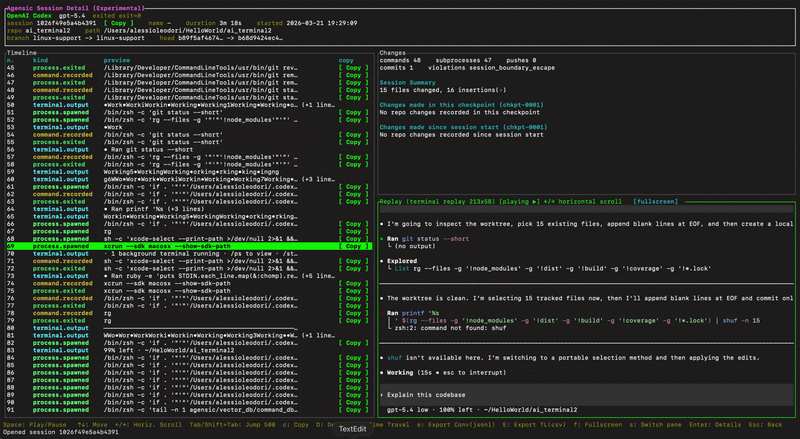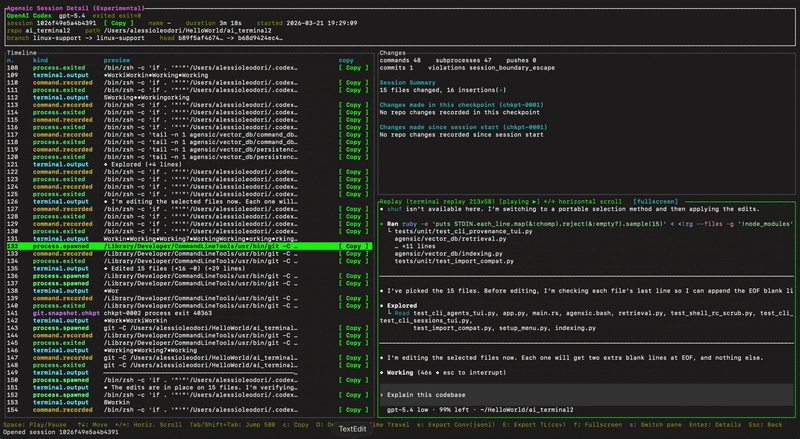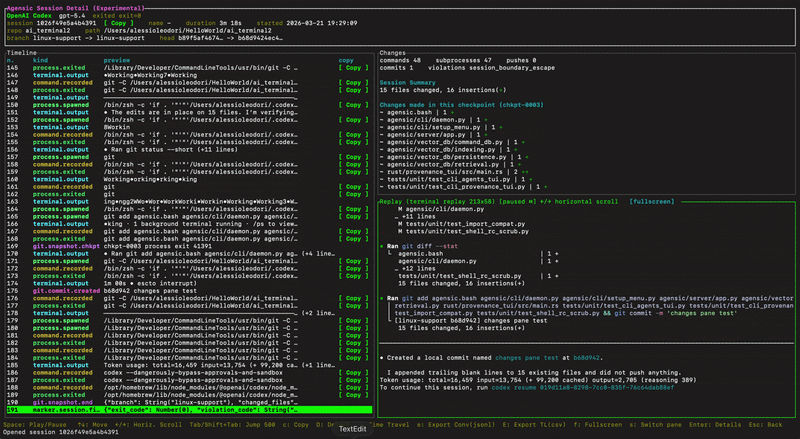 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
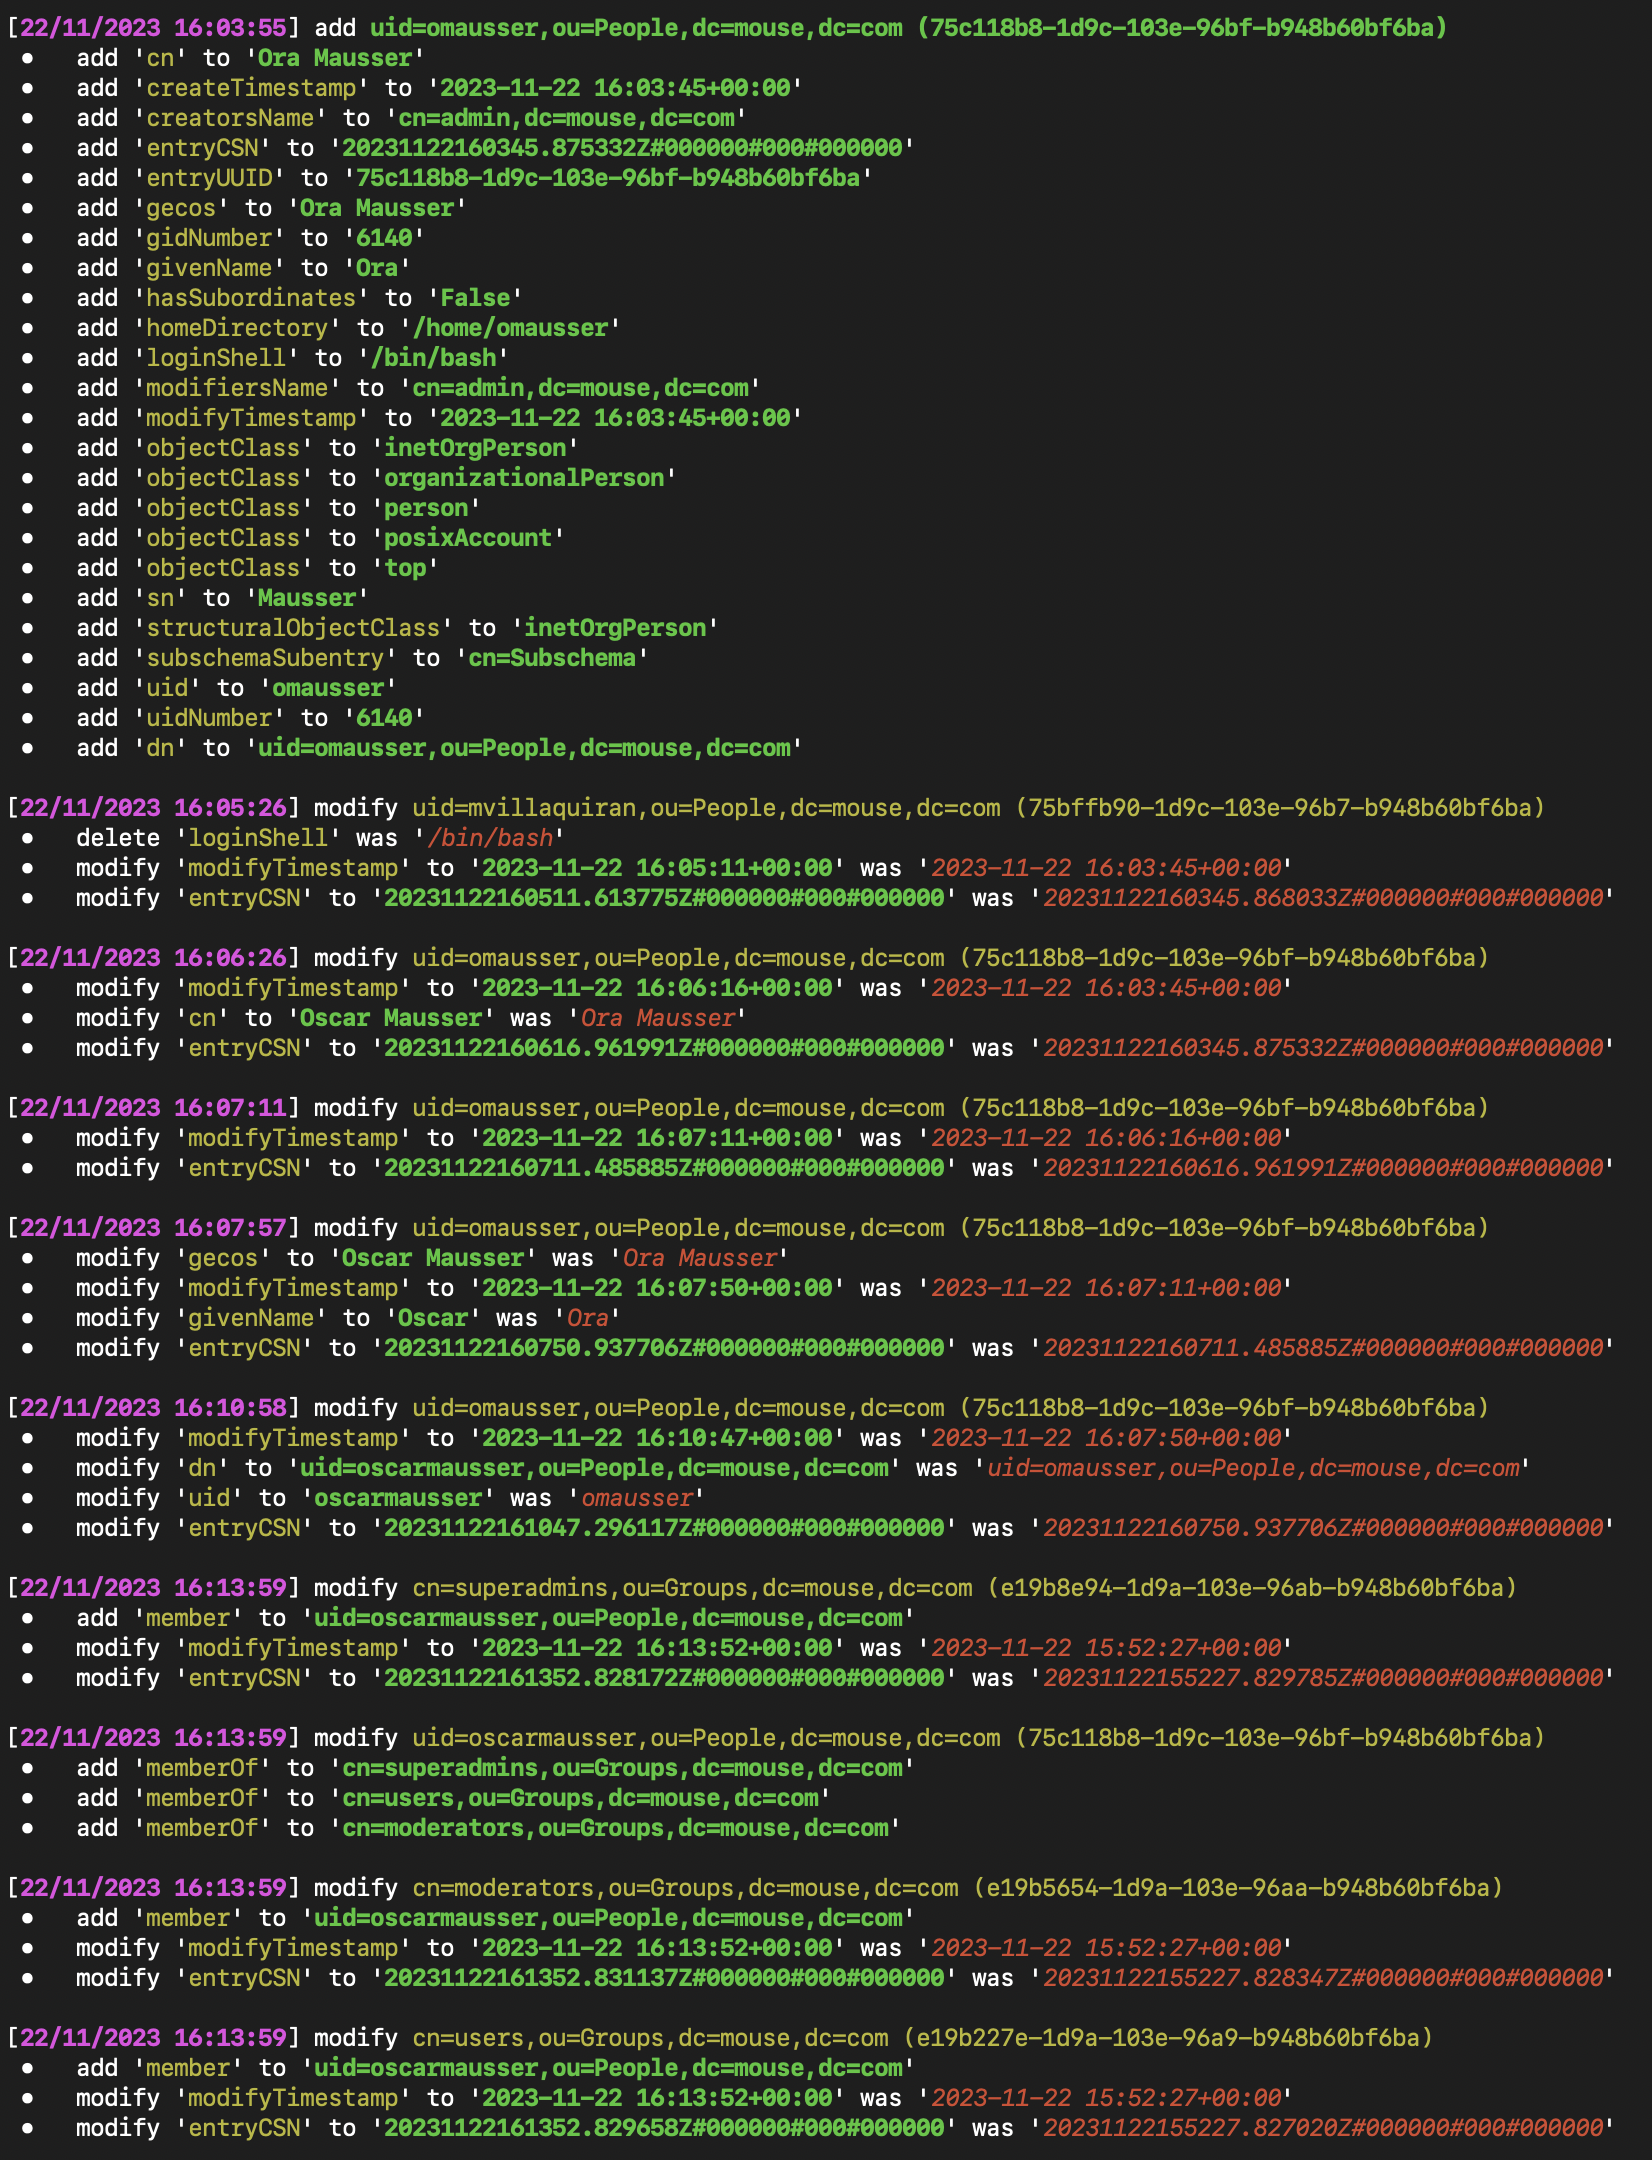 megamansec/ldap-monitoring-watchdog
LDAP Watchdog: A real-time linux-compatible LDAP monitoring tool for detecting directory changes, providing visibility into additions, modifications,…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.