
LogHound
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
authenticationdigital-forensicsforensics+6
rnb-team/loghoundPost-Exploitation EVTX Analyzer for BloodHound Mapping
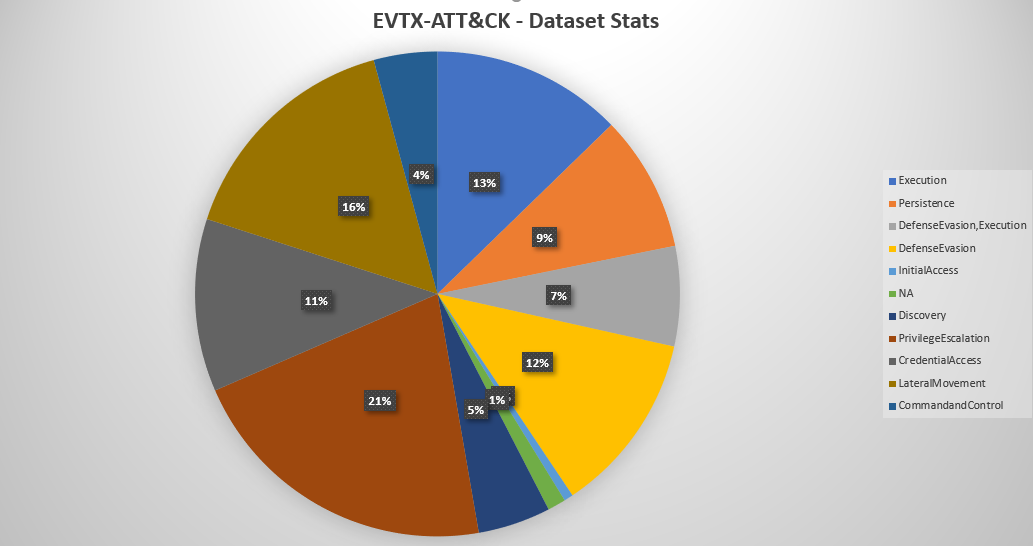 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 creamyg31337/ncentral-compromise-ioc-triage
Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints