
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
426 results
ntopng preview

ntopng

GitHubntop/ntopng

Web-based Traffic and Cybersecurity Network Traffic Monitoring

anomaly-detectiondns-analysisintrusion-detection+6
8.2k2 days ago
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

anomaly-detectionanti-botdefensive-tools+14
8.1k3 days ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

ai-securitycloud-infrastructure-securitycloud-security+9
12.1k4 days ago
suricata preview

suricata

GitHuboisf/suricata

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…


anomaly-detectionanti-botdefensive-tools+9
6.7k1 day ago
tcpdump preview

tcpdump

GitHubthe-tcpdump-group/tcpdump

the TCPdump network dissector

dns-analysisforensicslog-analysis+5
3.2k13 days ago
rustnet preview

rustnet

GitHubdomcyrus/rustnet

Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
cloud-securitycontainer-securitydns-analysis+5
5.1k19h 19m ago
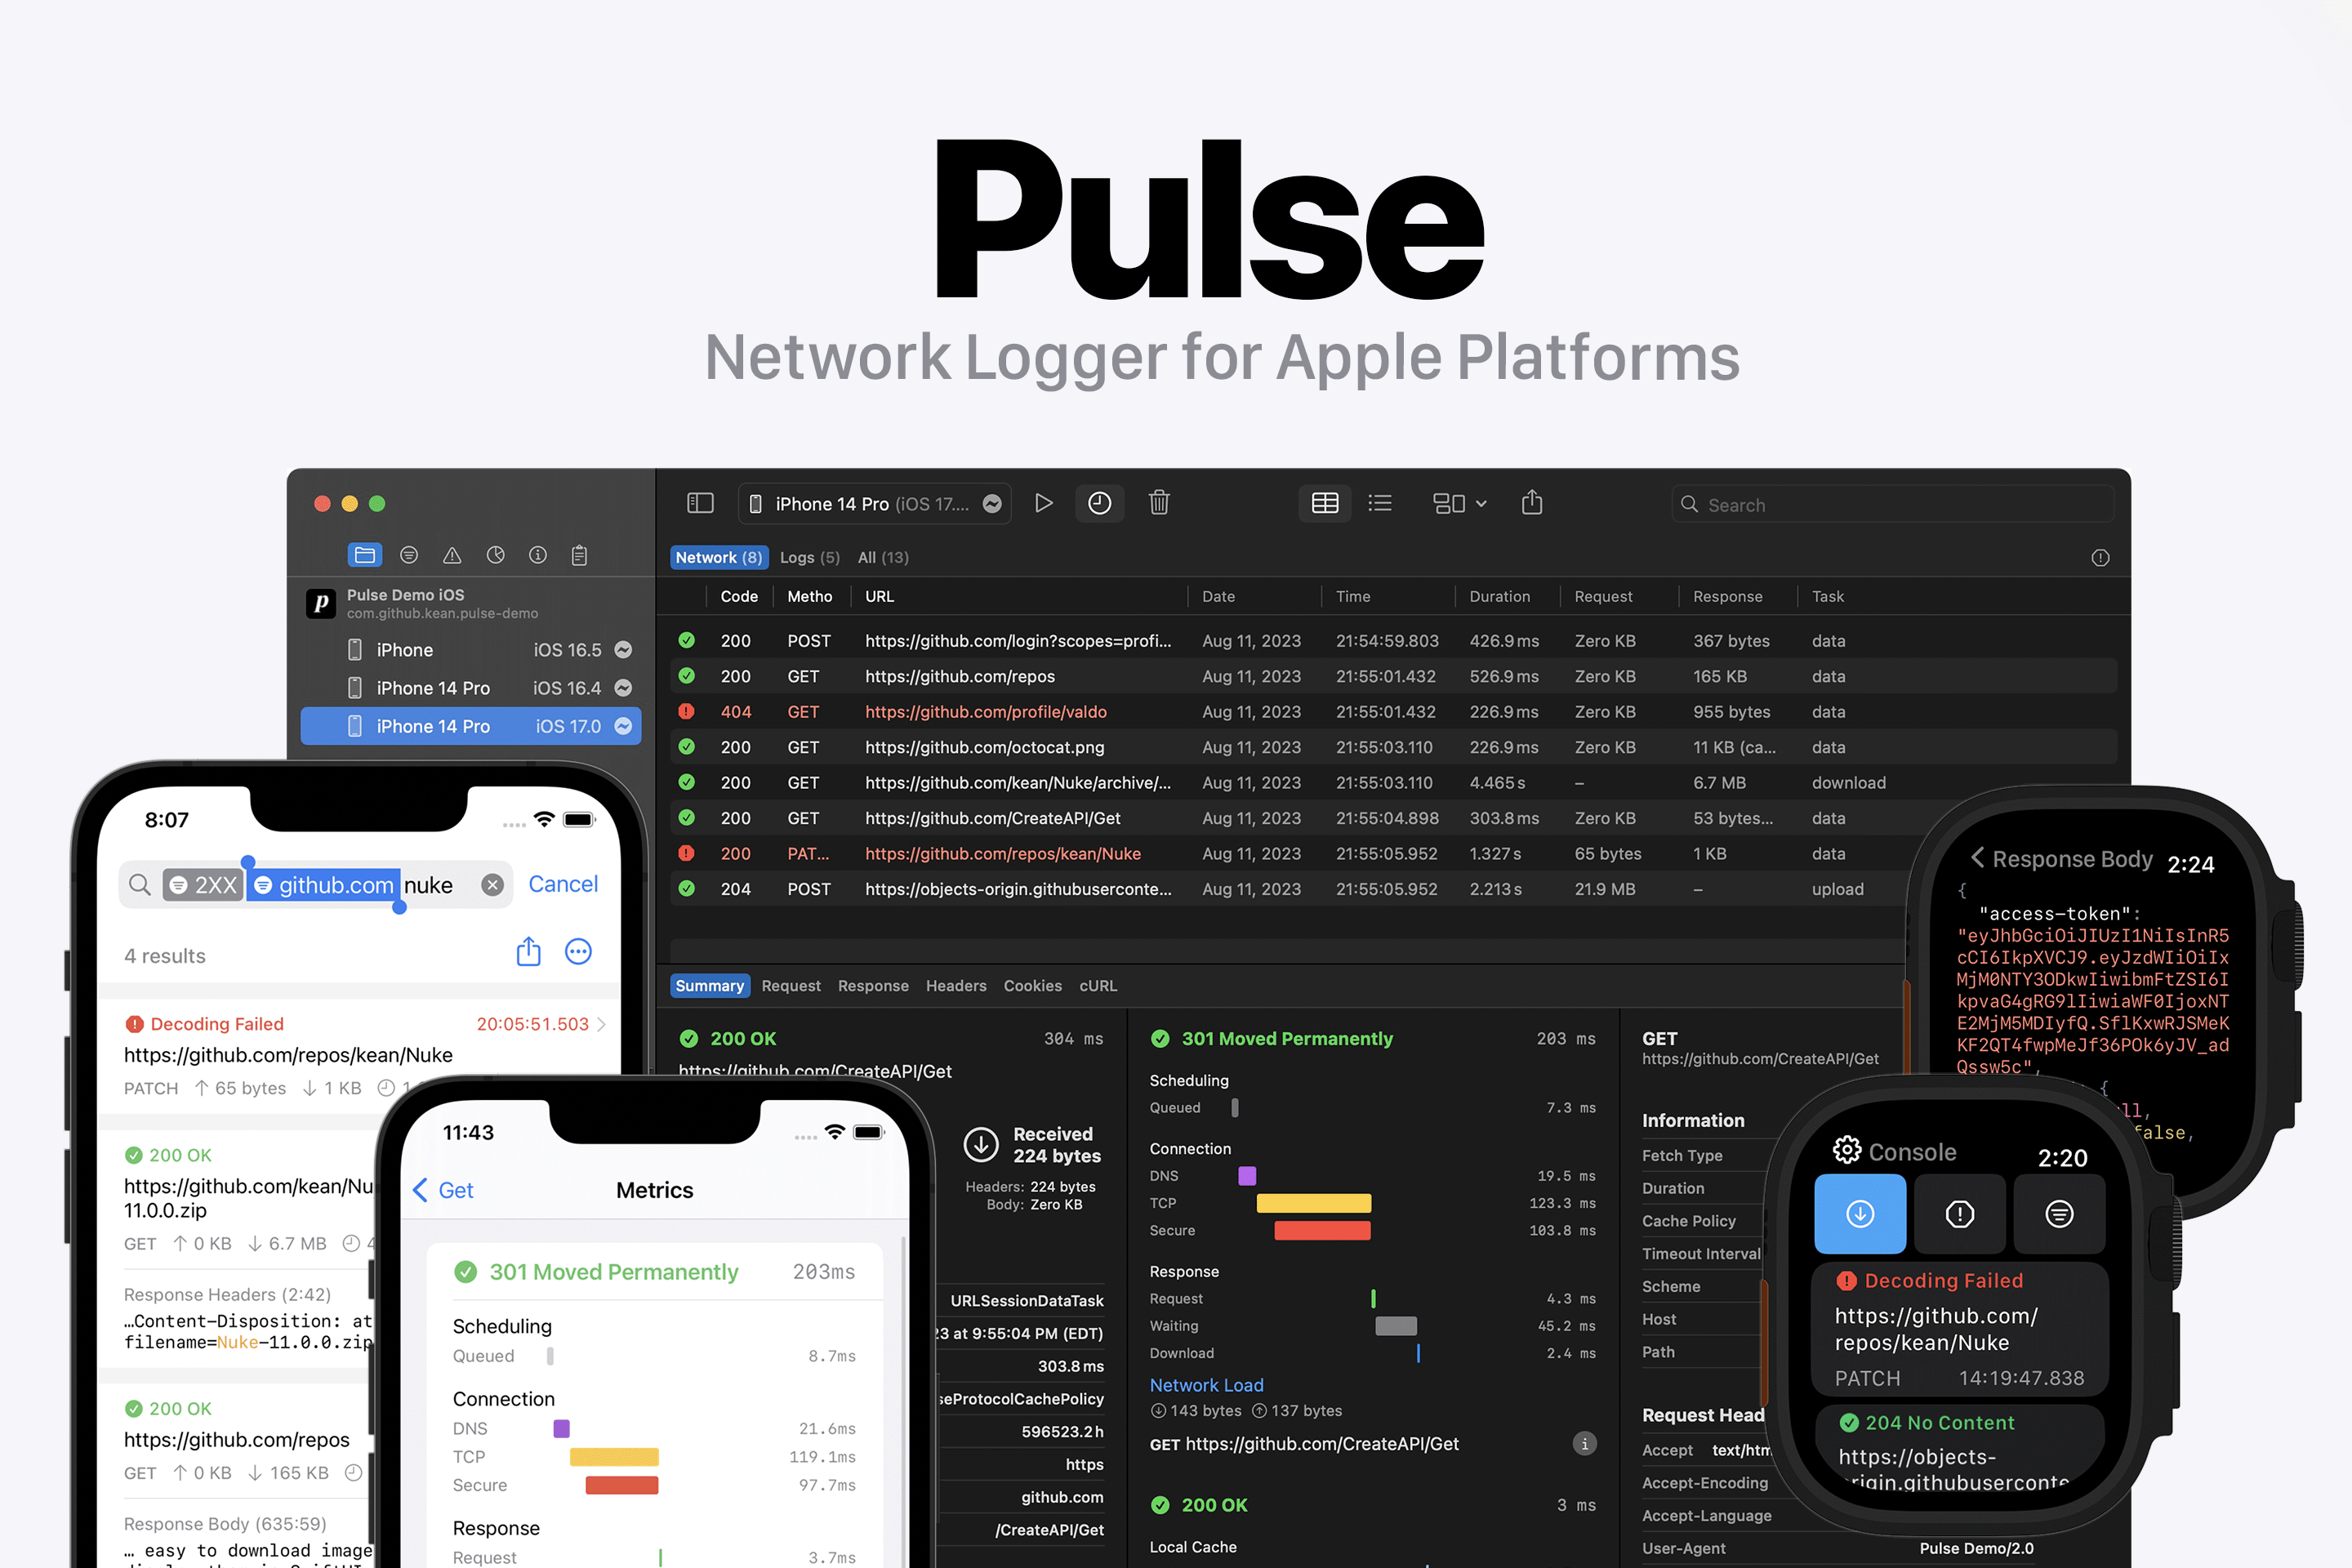
Pulse preview

Pulse

GitHubkean/pulse

Network logger for Apple platforms

debuggersios-securitylog-analysis+1
7.2k1 month ago
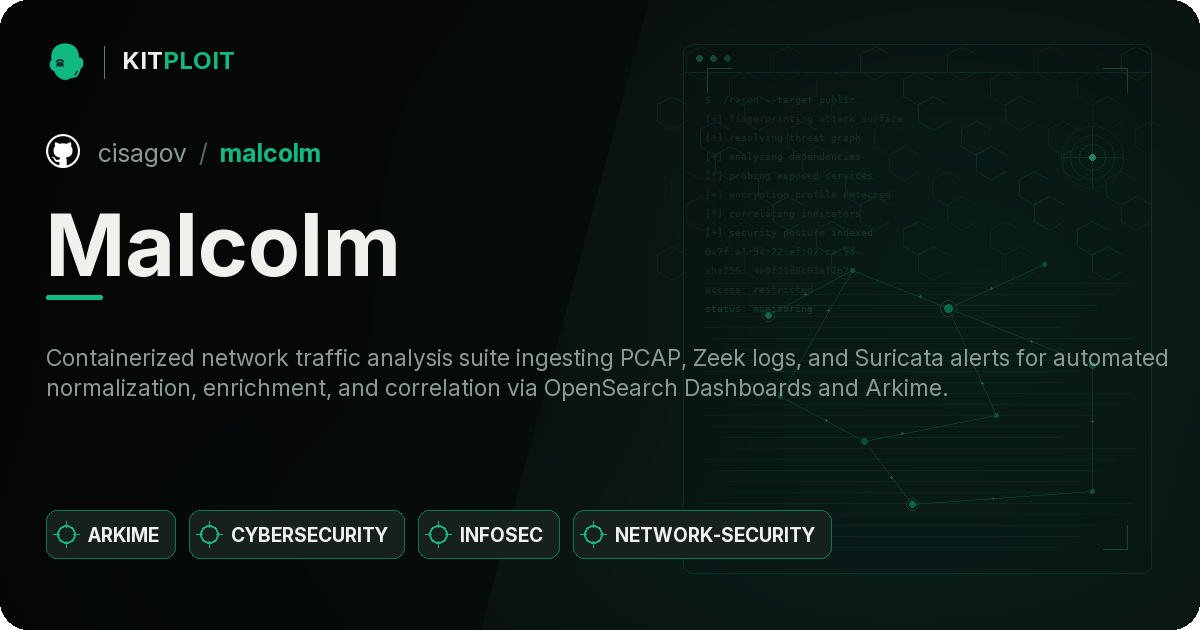
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

digital-forensicsdns-analysisforensics+9
2.5k5 days ago
opencanary preview

opencanary

GitHubthinkst/opencanary

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…

defensive-toolsincident-responseintrusion-detection+3
3.1k13 days ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k2 years ago
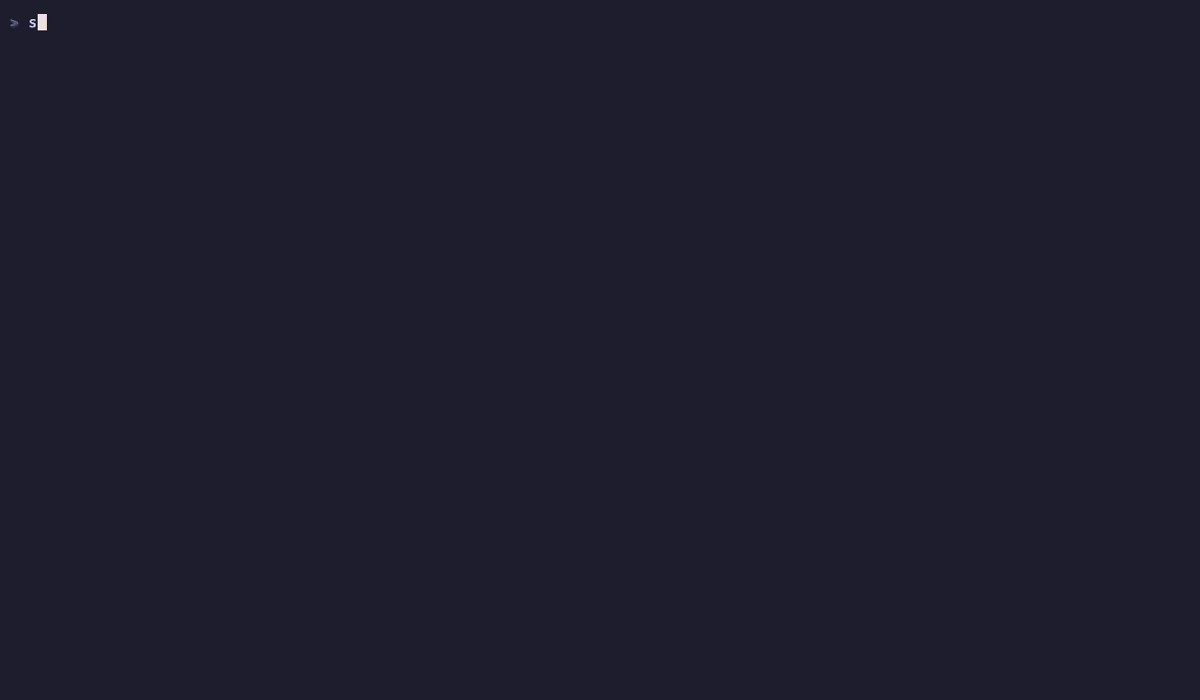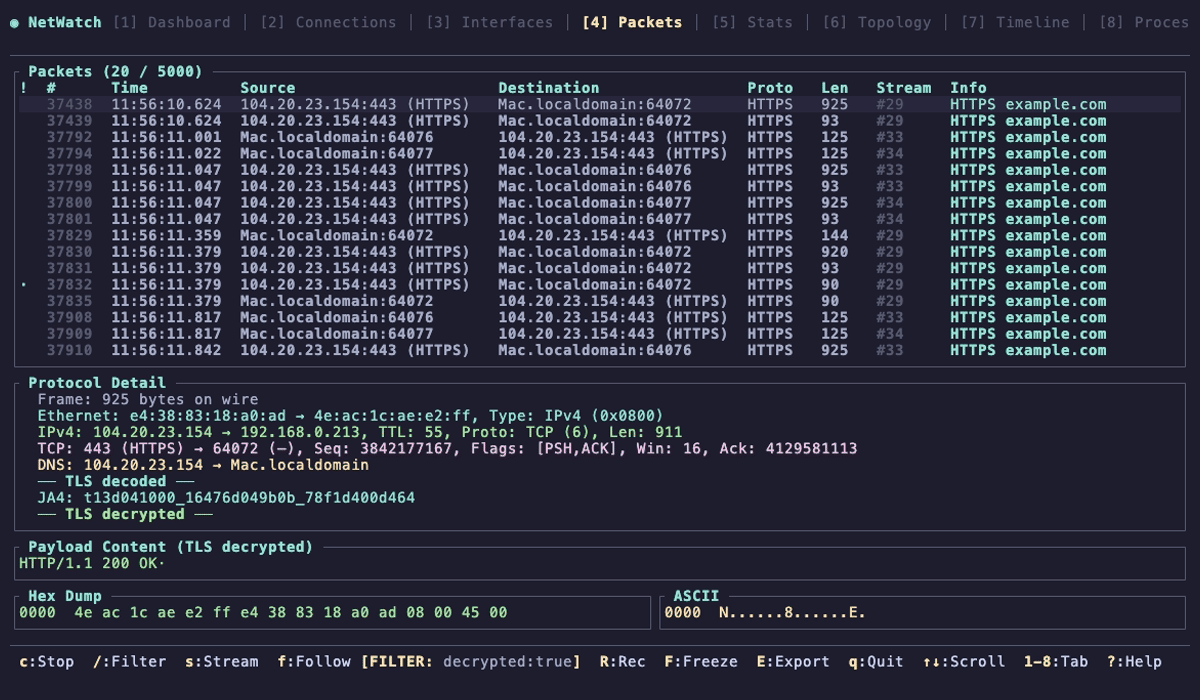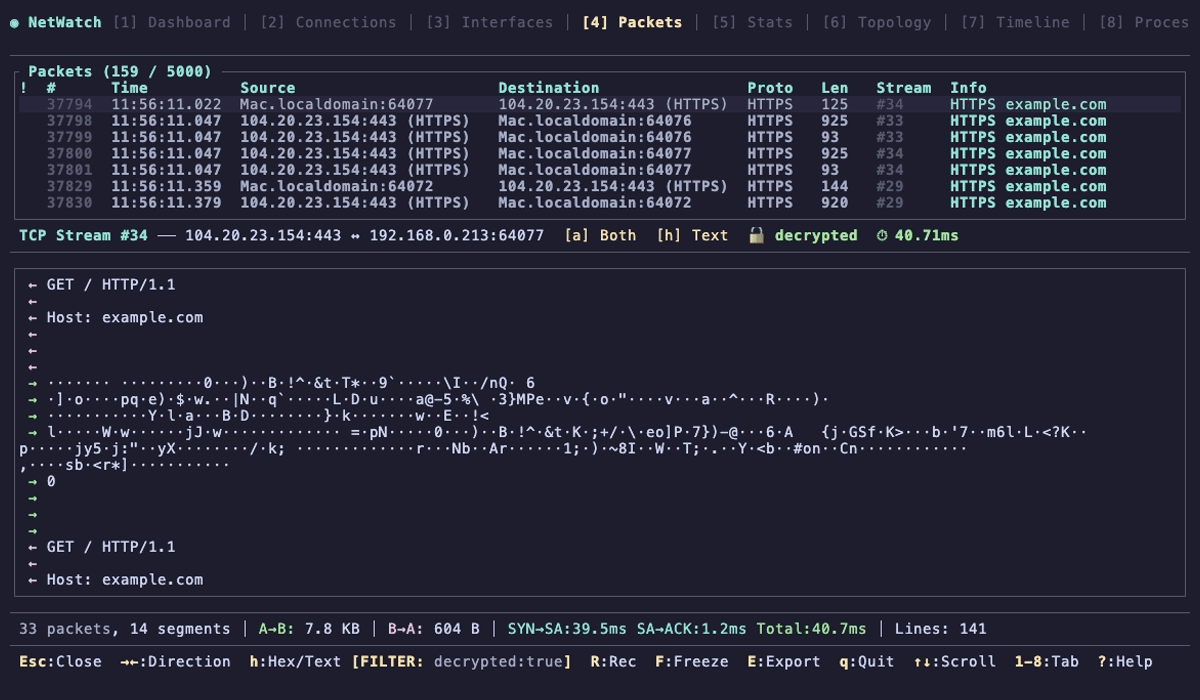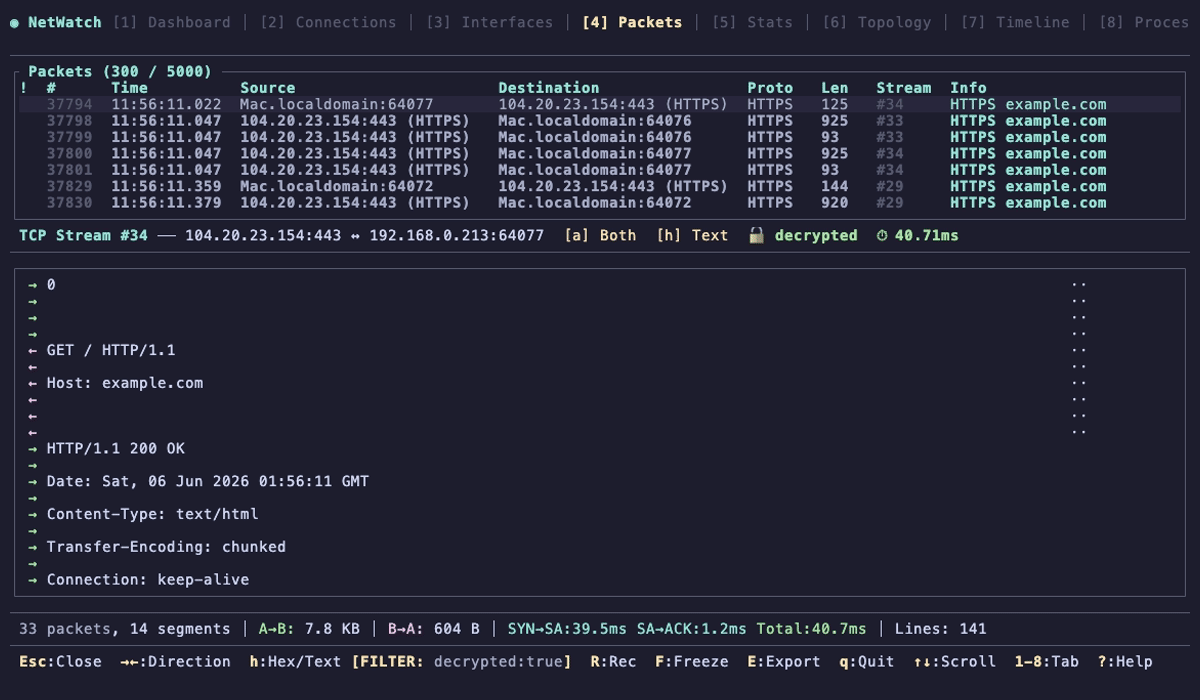
netwatch preview

netwatch

GitHubmatthart1983/netwatch

Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
defensive-toolsdigital-forensicsdns-analysis+8
3.4k1 day ago
neko-master preview

neko-master

GitHubforu17/neko-master

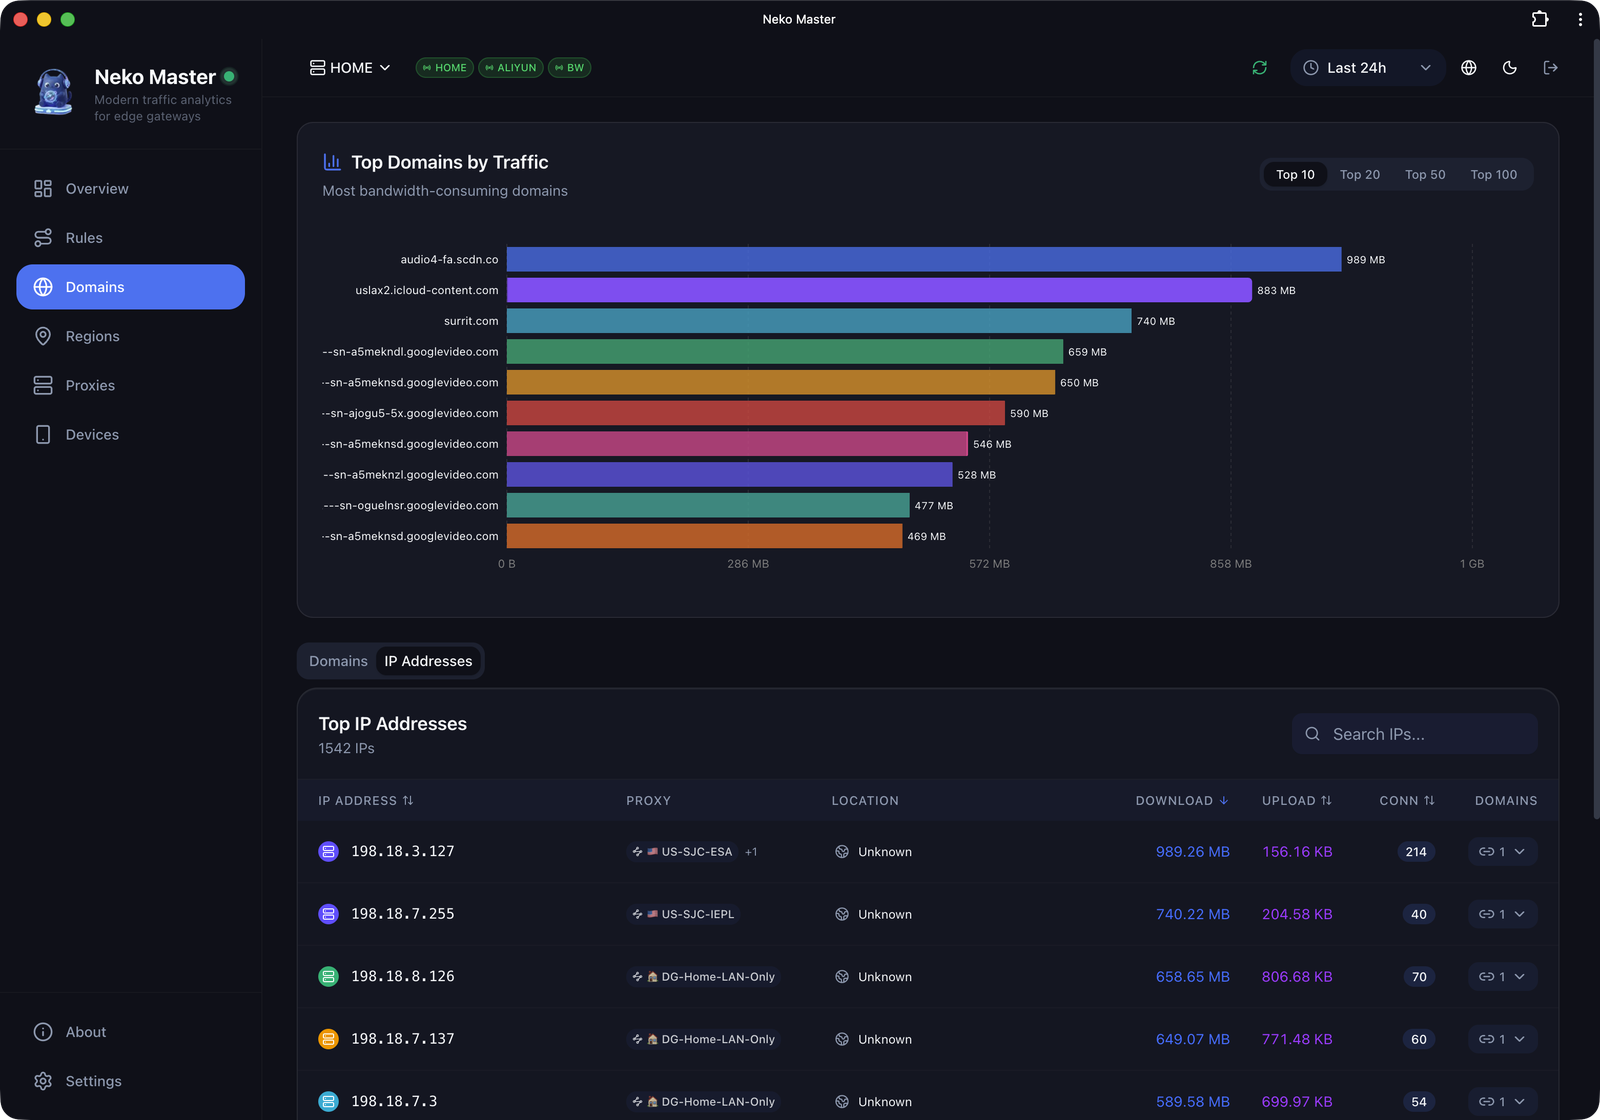
A modern and elegant dashboard for network traffic visualization and analysis.
information-gatheringlog-analysisnetwork-mapping+3
4.1k2 months ago
SweetSecurity preview

SweetSecurity

GitHubtravisfsmith/sweetsecurity

Network Security Monitoring on Raspberry Pi type devices
defensive-toolsintrusion-detectionlog-analysis+1
7949 years ago
snorby preview

snorby

GitHubsnorby/snorby

Ruby On Rails Application For Network Security Monitoring
defensive-toolsincident-responseintrusion-detection+2
1.0k3 years ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…

defensive-toolsdigital-forensicsforensics+8
4875 days ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8174 months ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
6513 months ago
L3MON preview

L3MON

GitHubd3vl/l3mon

Web-based network monitoring system providing real-time bandwidth tracking, server performance metrics, and customizable alerts for proactive network…

log-analysisnetwork-mappingnetwork-security
2973 years ago
Previous12…24Next