
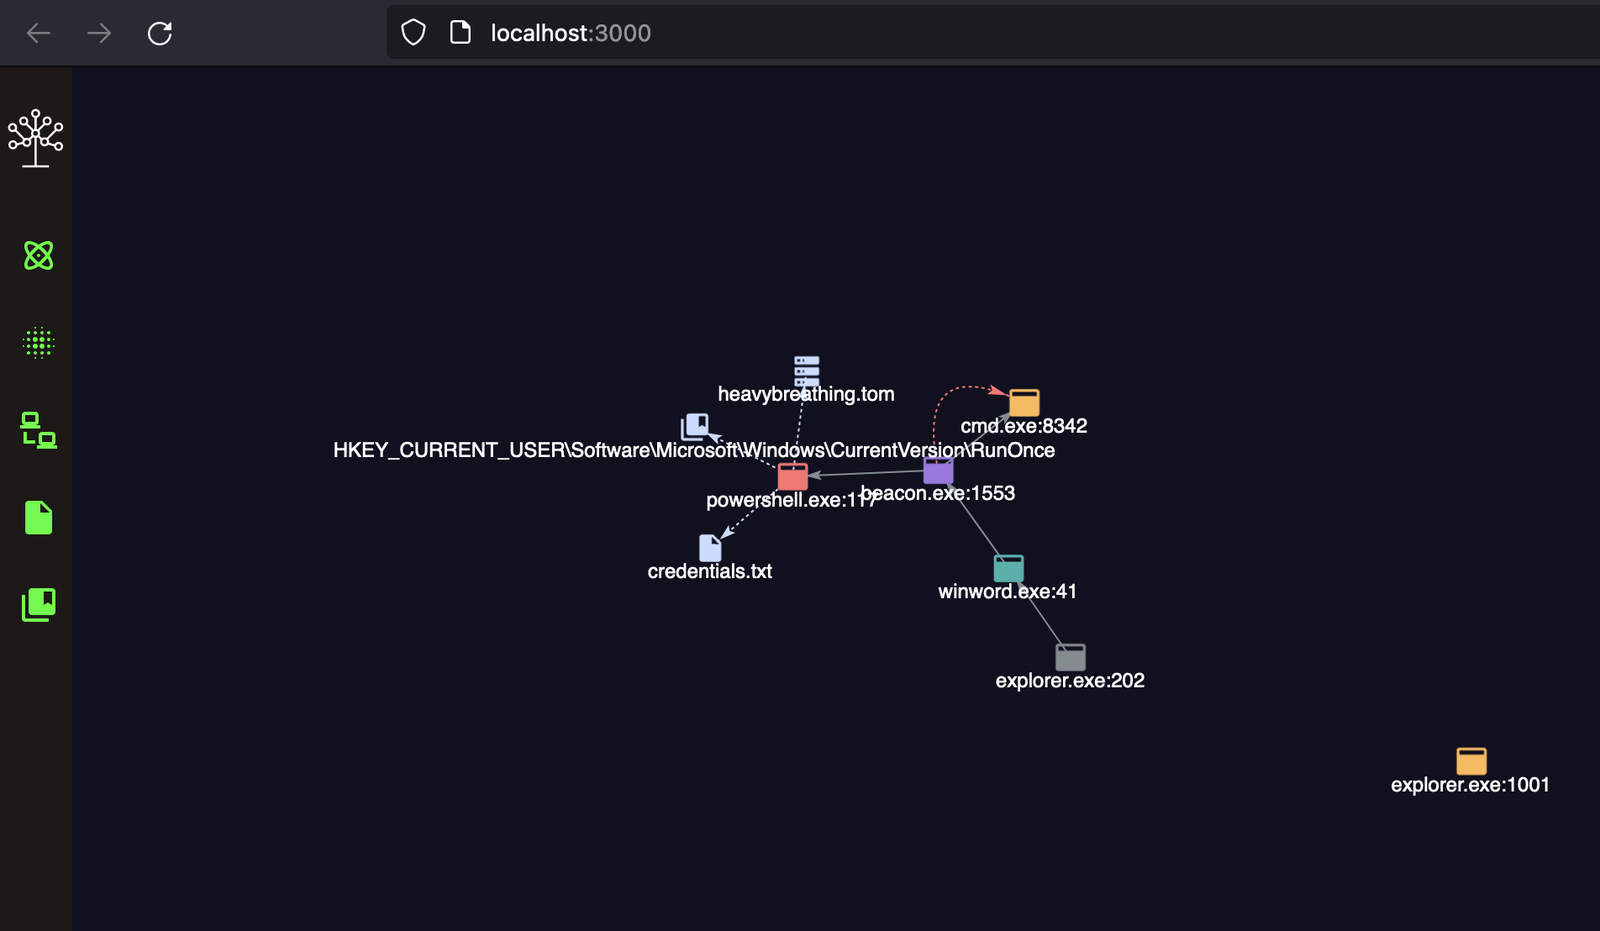
detectree
 withsecurelabs/detectree
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
defensive-toolsincident-responselog-analysis+1
withsecurelabs/detectreeInteractive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
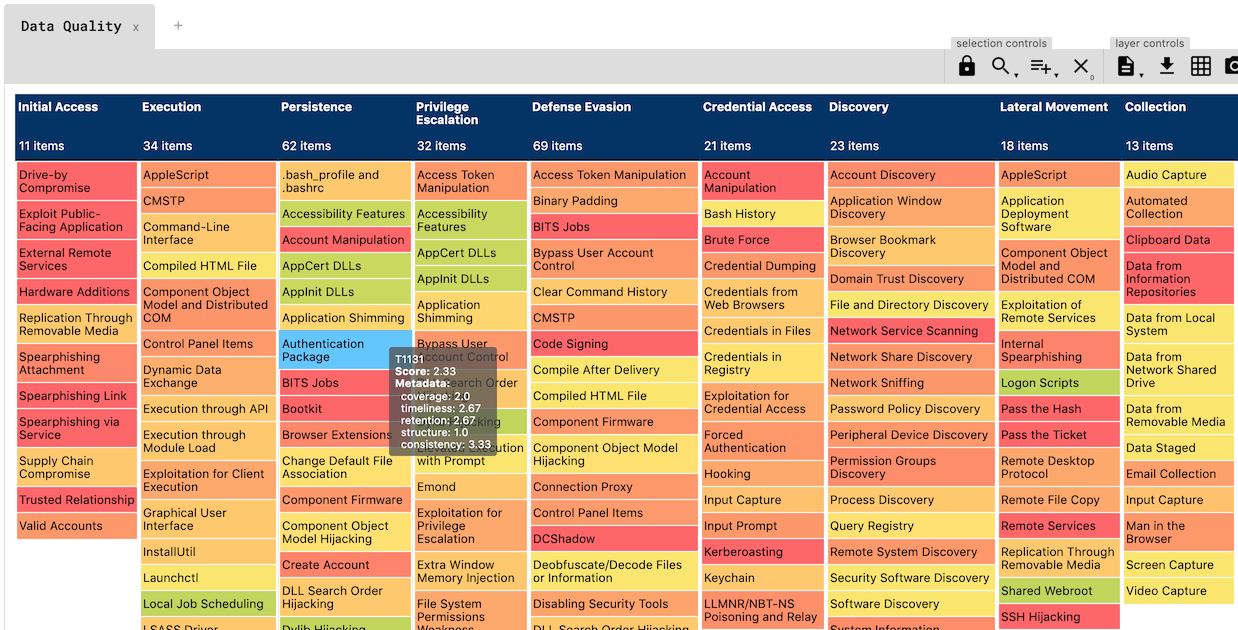 hxnoyd/ossem-power-up
A tool to assess data quality, built on top of the awesome OSSEM.
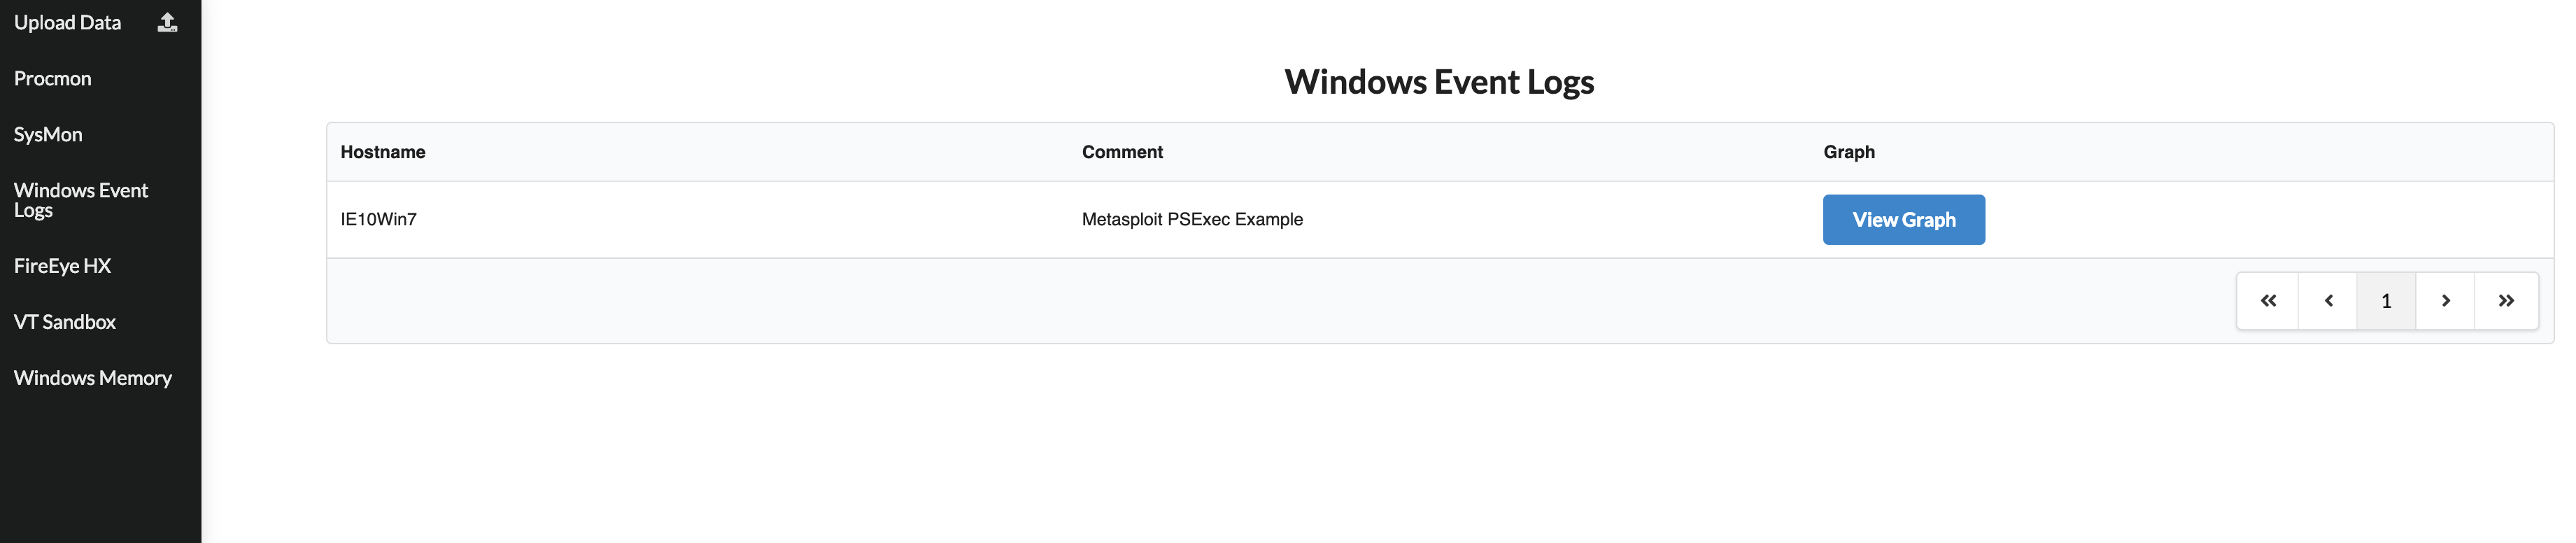 yampelo/beagle
Beagle is an incident response and digital forensics tool which transforms security logs and data into graphs.
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
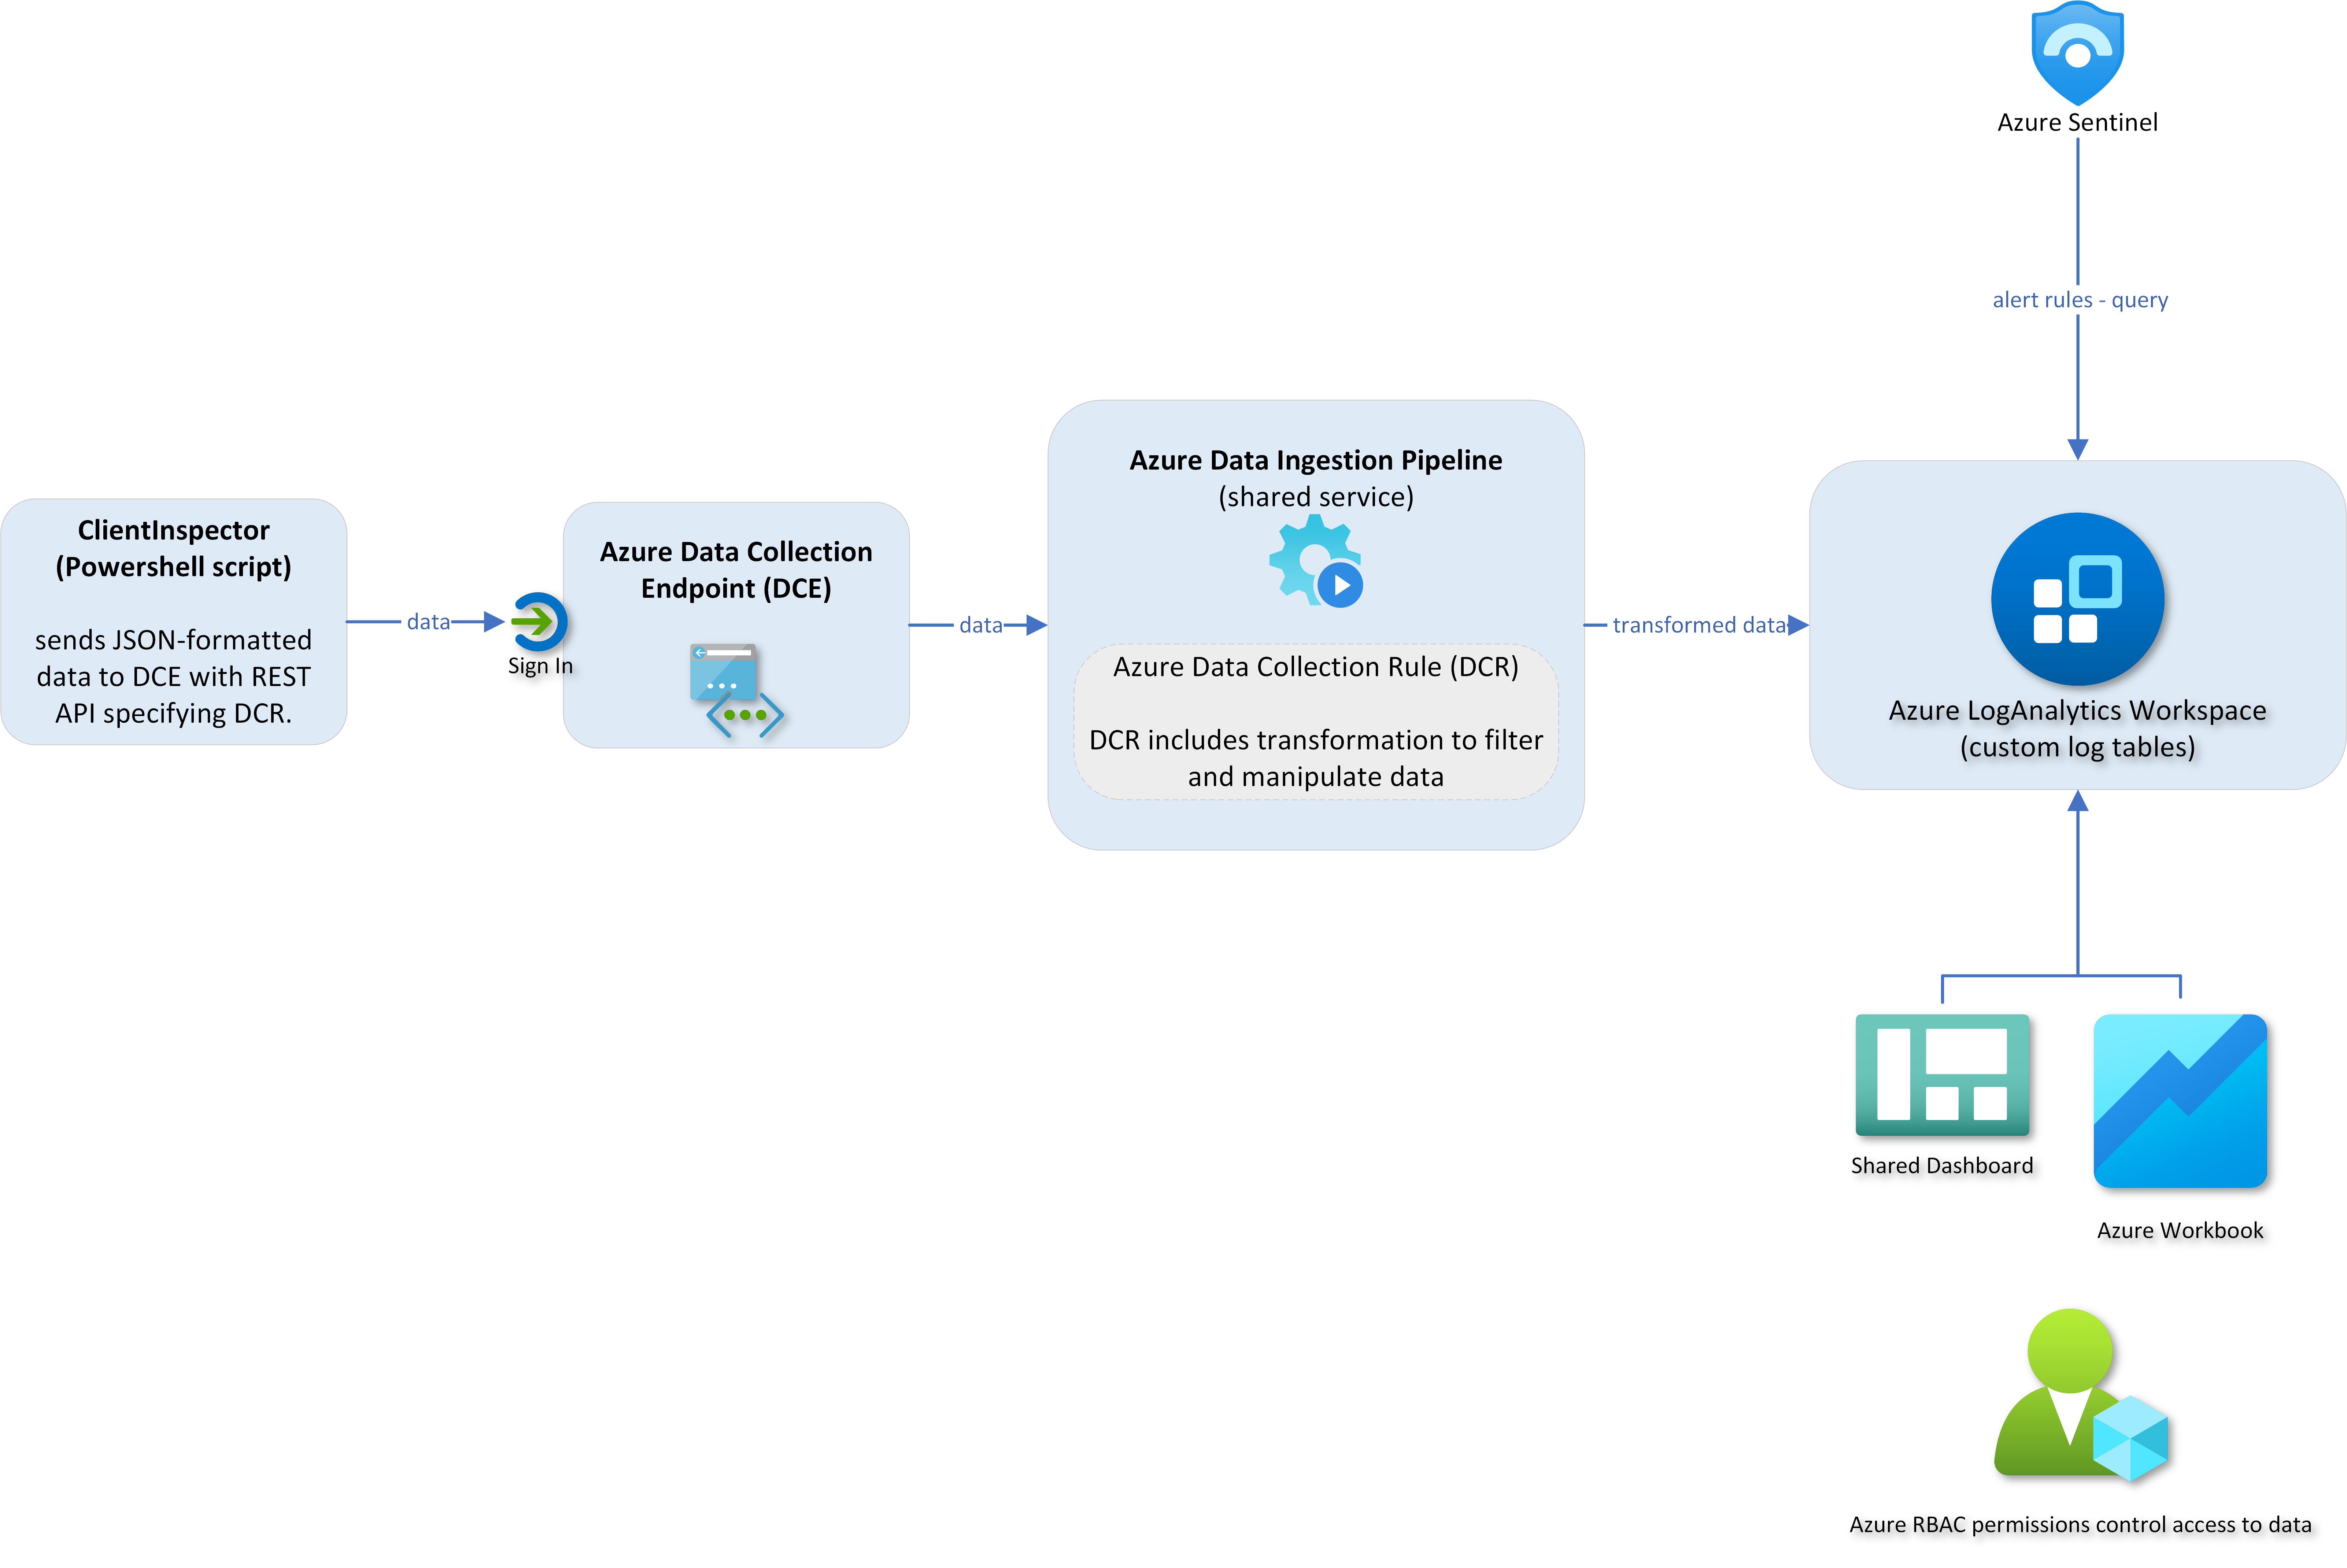 knudsenmorten/clientinspectorv2
Azure-based client inventory and drift detection tool that collects Windows configuration data (antivirus, patching, Bitlocker) into LogAnalytics for…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 wheezysec/cve-2021-44228-kusto
Kusto query-based detection and analysis tool for CVE-2021-44228 (Log4Shell) vulnerability, enabling rapid log hunting and exploitation…
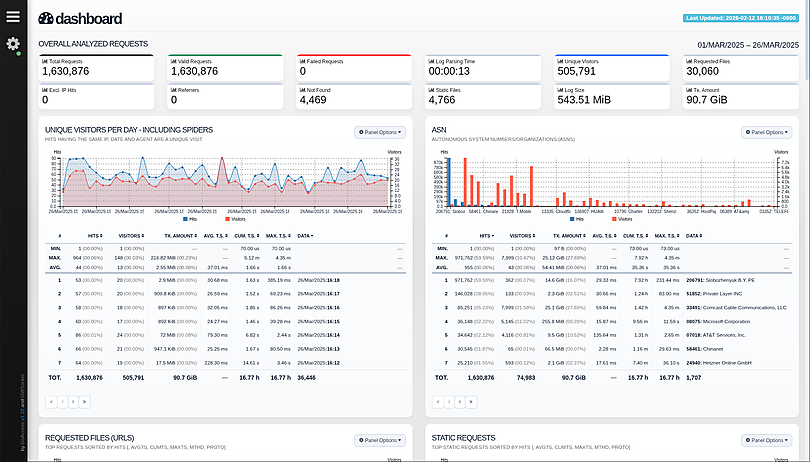 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
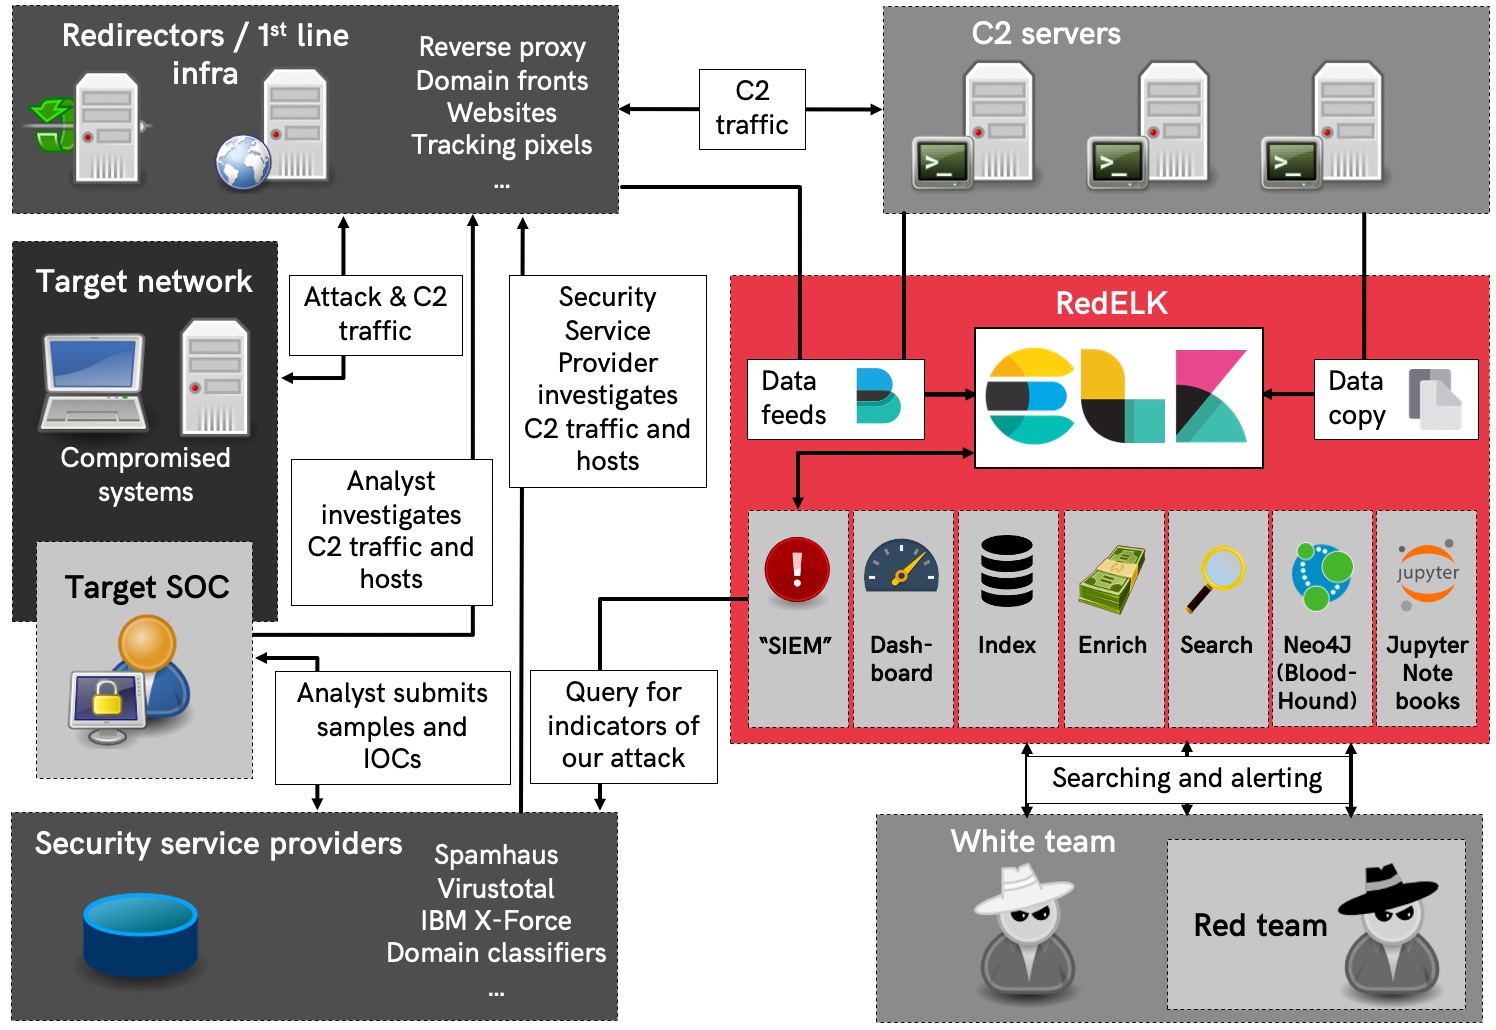 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
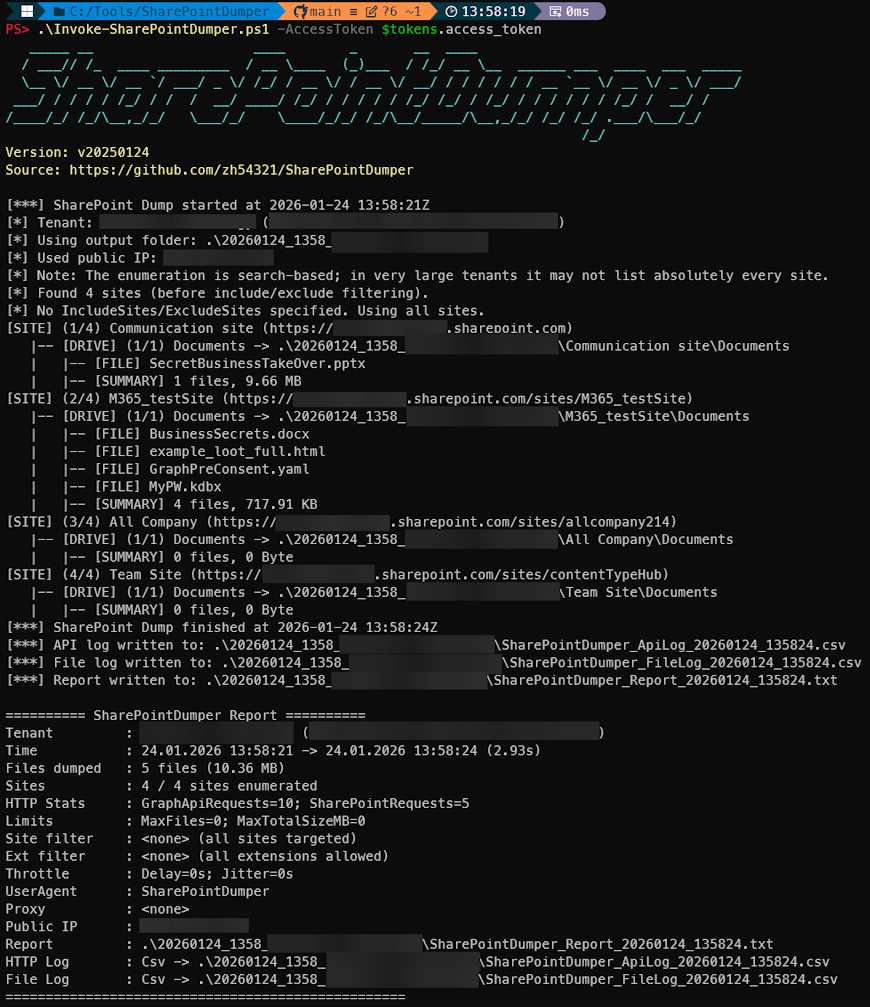 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…