CVE-2026-43284-dirtyfrag-detection

Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…

Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…

Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…

Defensive validation of CVE-2026-46331 / pedit COW with auditd, AppArmor, mitigation comparison and detection logic.

Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

A Simple Log4j Indicator of Compromise Linux Detector

Provides BigFix Fixlets and analyses to detect Log4j vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105) across Windows and Linux…

CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script

Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)

Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

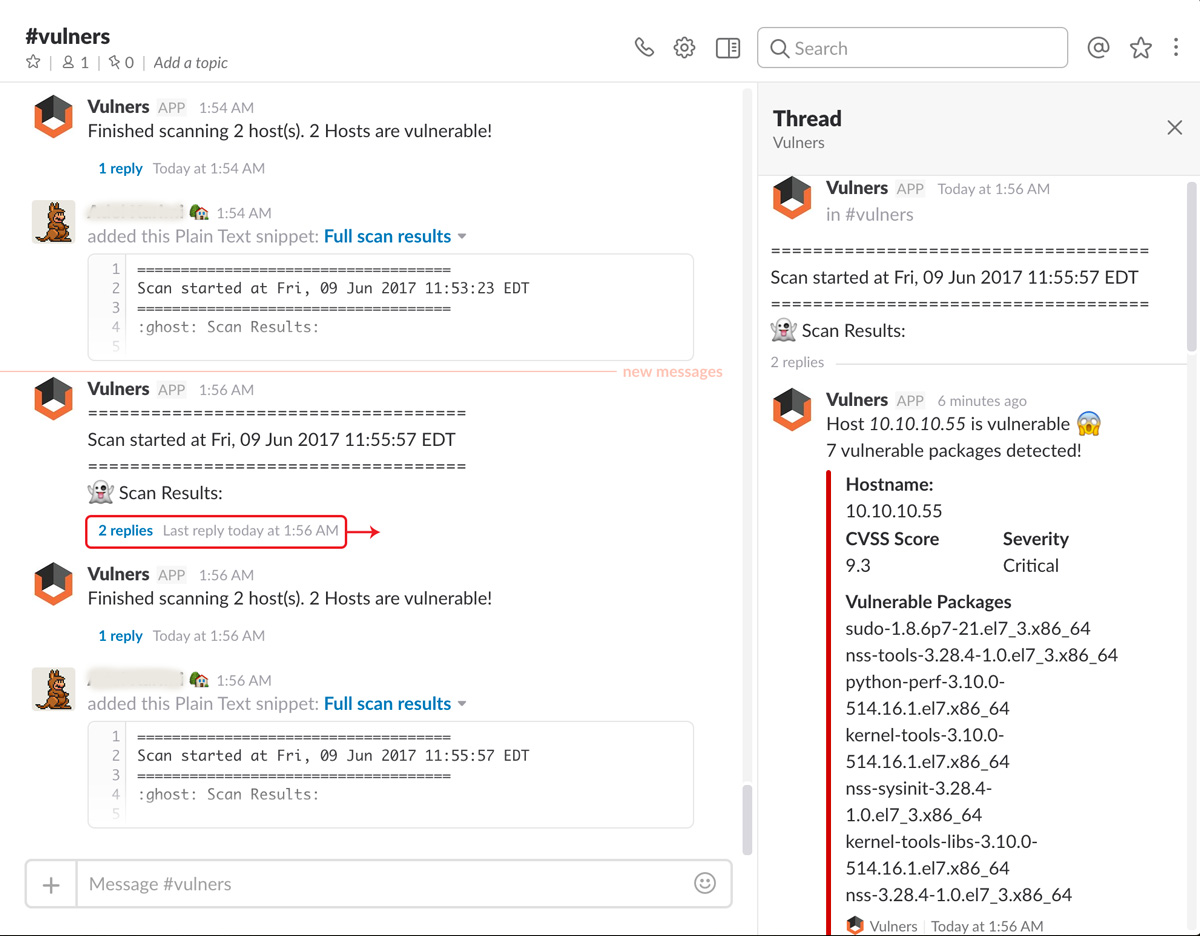
Linux vulnerability scanner based on Salt Open and Vulners audit API, with Slack notifications and JIRA integration

Express security essentials deployment for Linux Servers

Detection Script for MongoBleed Exploitation

Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…

CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool