
Invoke-DumpMDEConfig
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
configuration-auditingdefensive-toolsforensics+3
156
blacksnufkin/invoke-dumpmdeconfigPowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
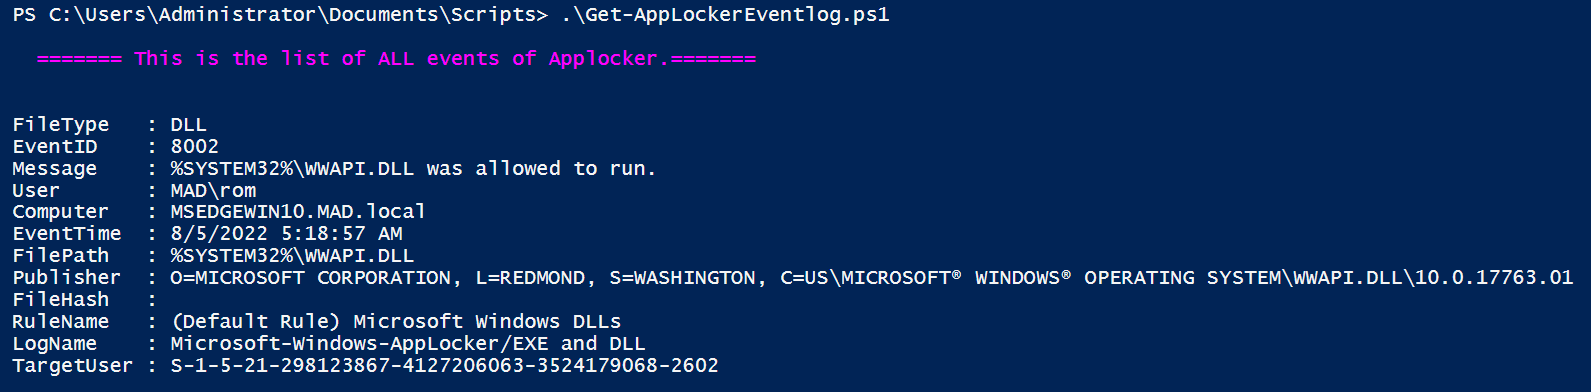 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts