
 phpboyscout/go/redact
Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…
 jepaynemsft/weffles
Build a fast, free, and effective Threat Hunting/Incident Response Console with Windows Event Forwarding and PowerBI
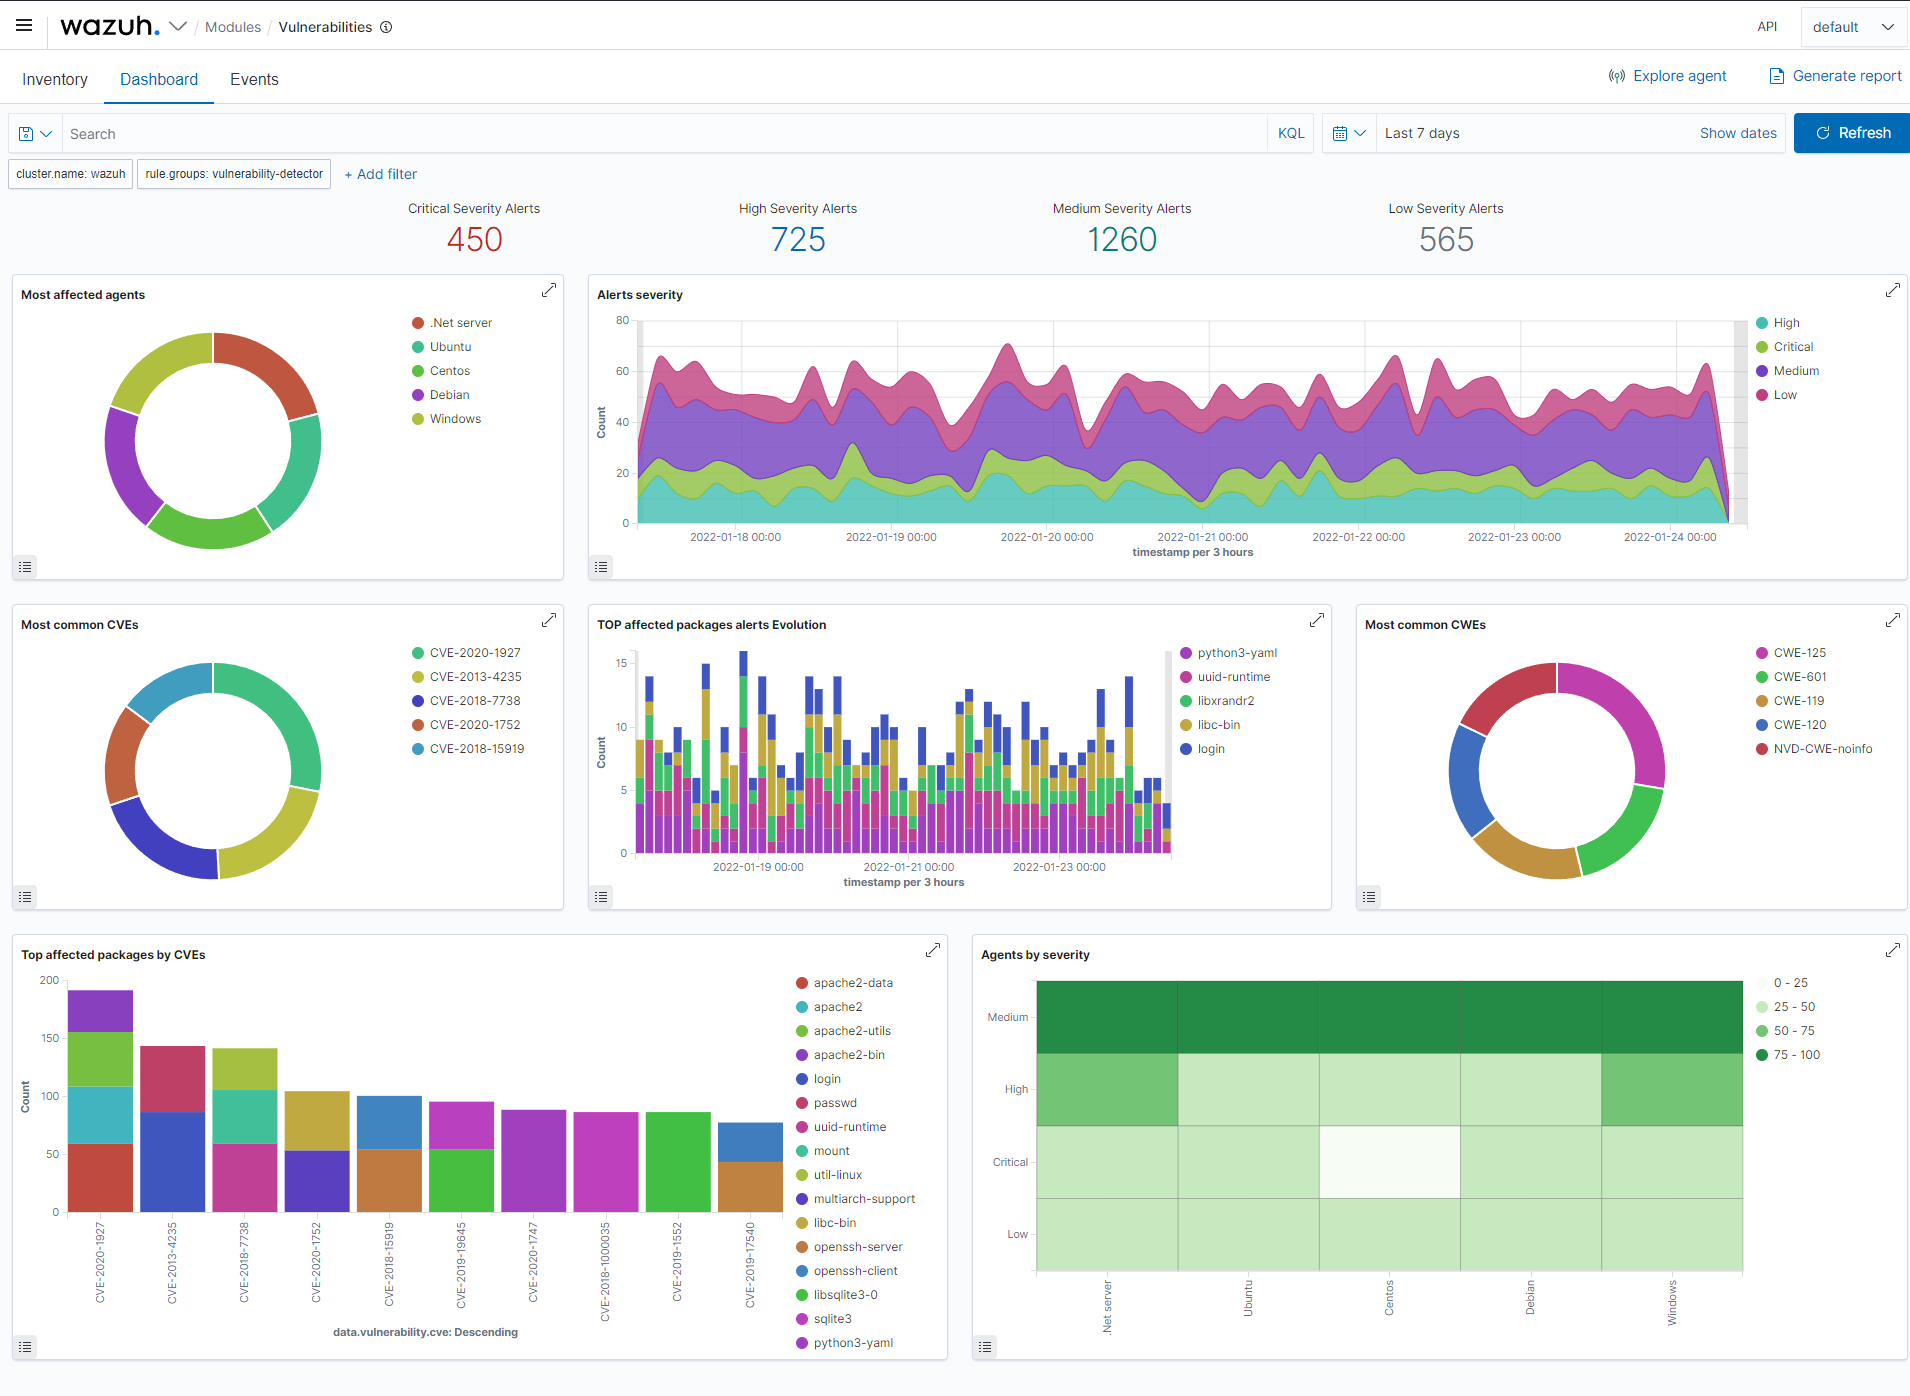 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
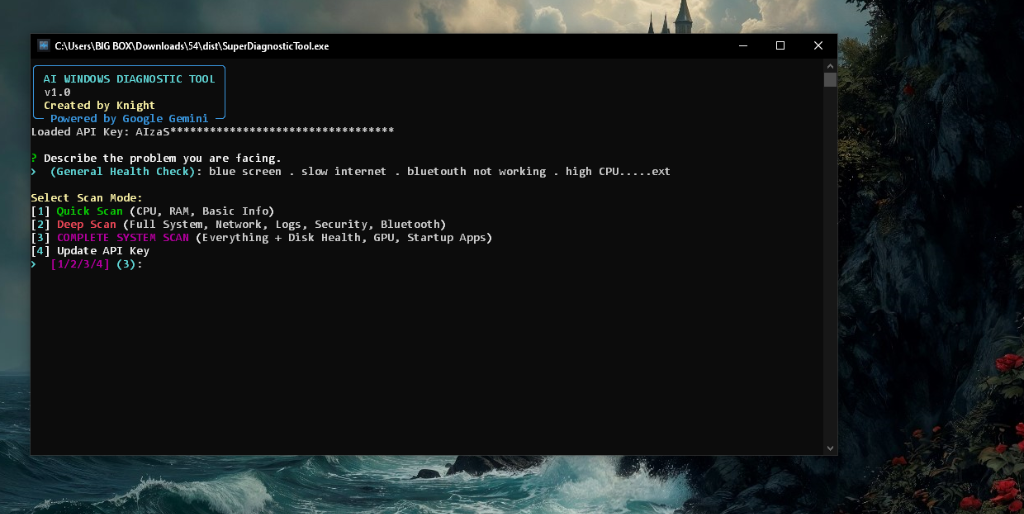 guettaf-hossam/superdiagnostictool
AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…
 arpitgupta369/log4shell-scanner
Lightweight scanner that detects vulnerable Log4j versions and Log4Shell (CVE-2021-44228) indicators in a filesystem tree.
 limo57640-crypto/nginx-rift-detector
Free NGINX Rift CVE-2026-42945 detector for version, rewrite config, ASLR, crash logs, and exploitation indicators.
 byteray-labs/query-hub
CQL Hub is an open repository of detection and hunting queries for CrowdStrike NextGen SIEM and Falcon LogScale. All queries stored here are…
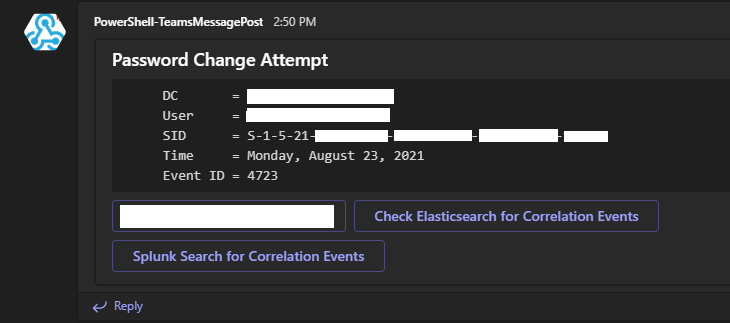 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 cross-samuel1/soc-analyst-hub
Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
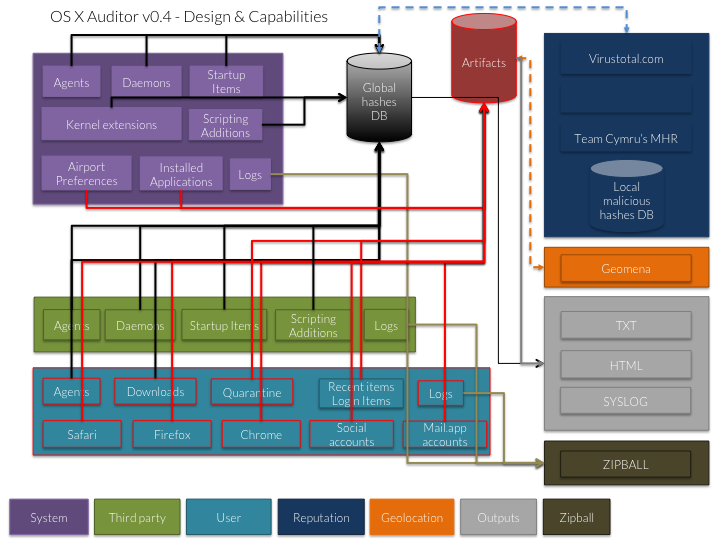 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool