Adversarial-Detection-Engineering-Framework

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…

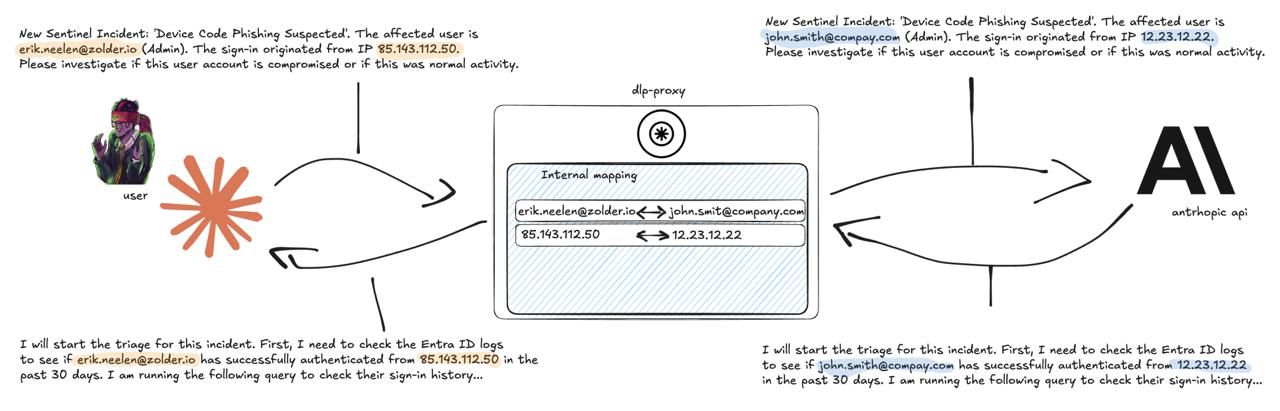
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

You didn't think I'd go and leave the blue team out, right?

Detect Tactics, Techniques & Combat Threats

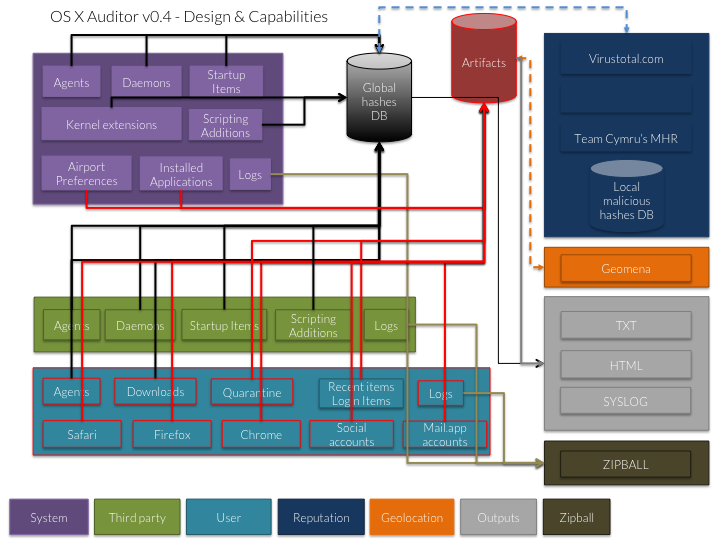
OS X Auditor is a free Mac OS X computer forensics tool

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…

AI runtime inventory: discover shadow AI, trace LLM calls


I was presented with a high-severity alert indicating a potential exploit attempt of CVE-2023-22515, a zero-day vulnerability in Atlassian…