
CVE-2020-35488
 guillaumepetit84/cve-2020-35488
Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…
exploitationlog-analysispenetration-testing+1
1
guillaumepetit84/cve-2020-35488Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
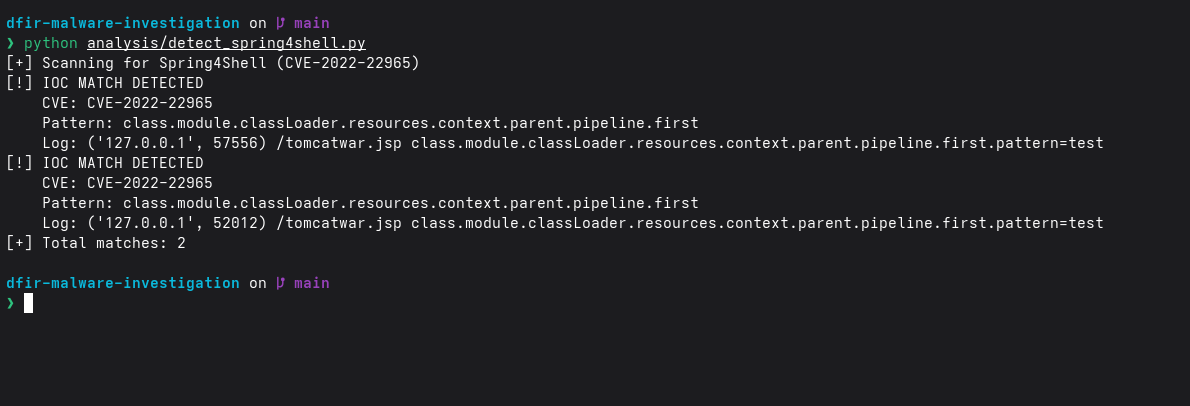 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
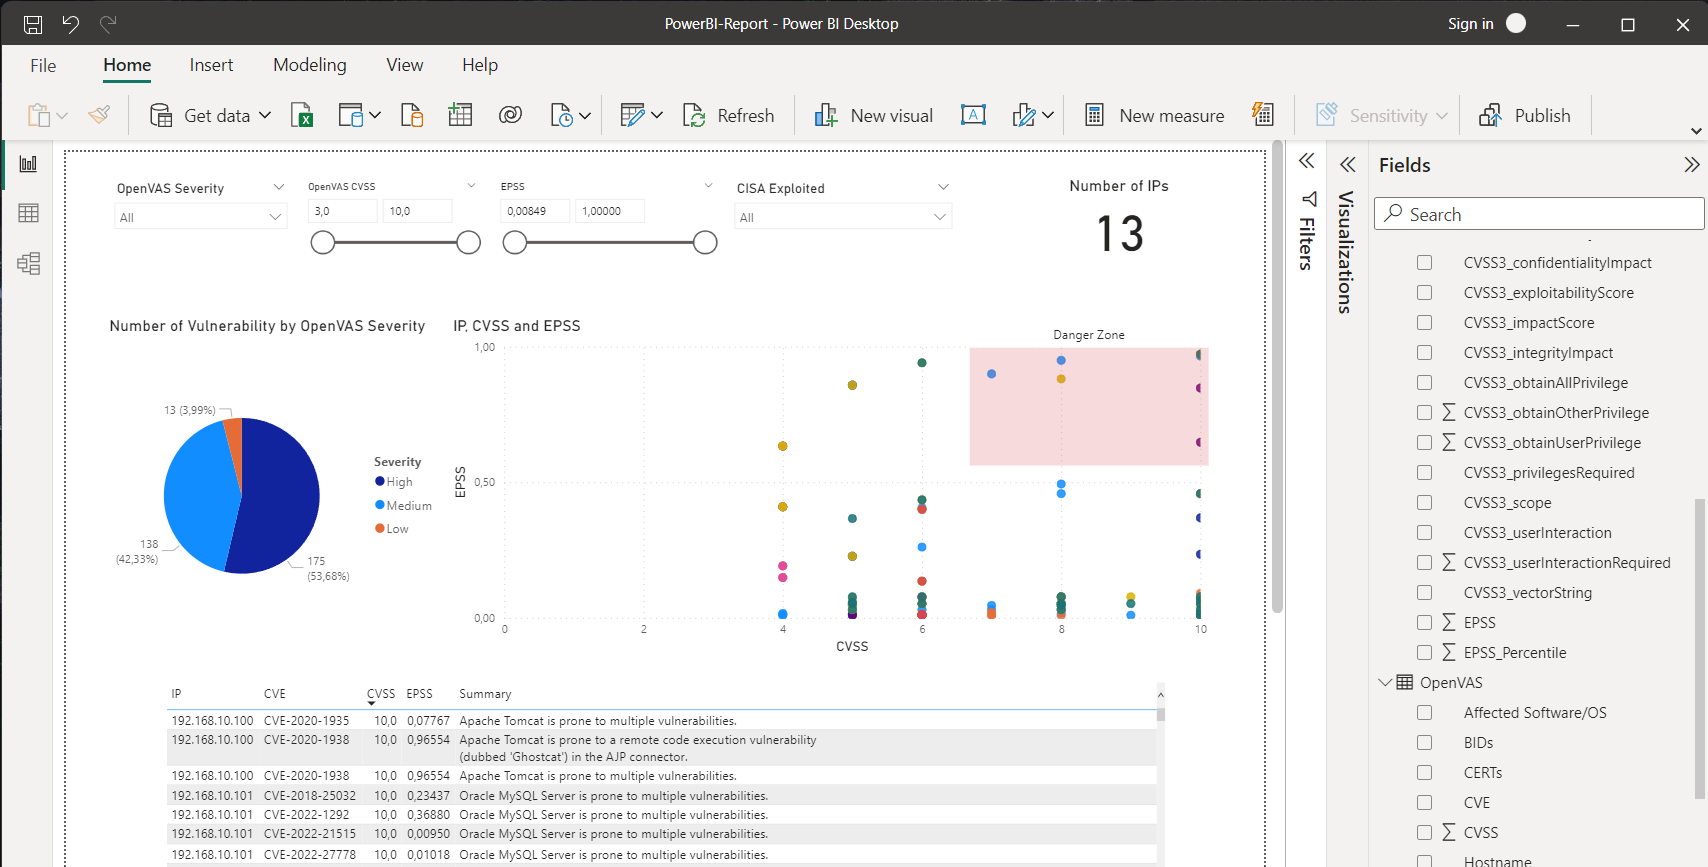 trinitor/cve-vulnerability-information-downloader
Downloads and aggregates CVSS, EPSS, and CISA known exploited vulnerability data into unified JSON/CSV files and a SQLite database. Enriches…
 sentinelblue/cve-2022-29072
** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
 airbus-cert/cve-2024-4040
Scanner for CVE-2024-4040
 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
 joakimbulow/cve-2026-1337
CVE-2026-1337 - Neo4j - Log Injection
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 hestat/drupal-check
Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600
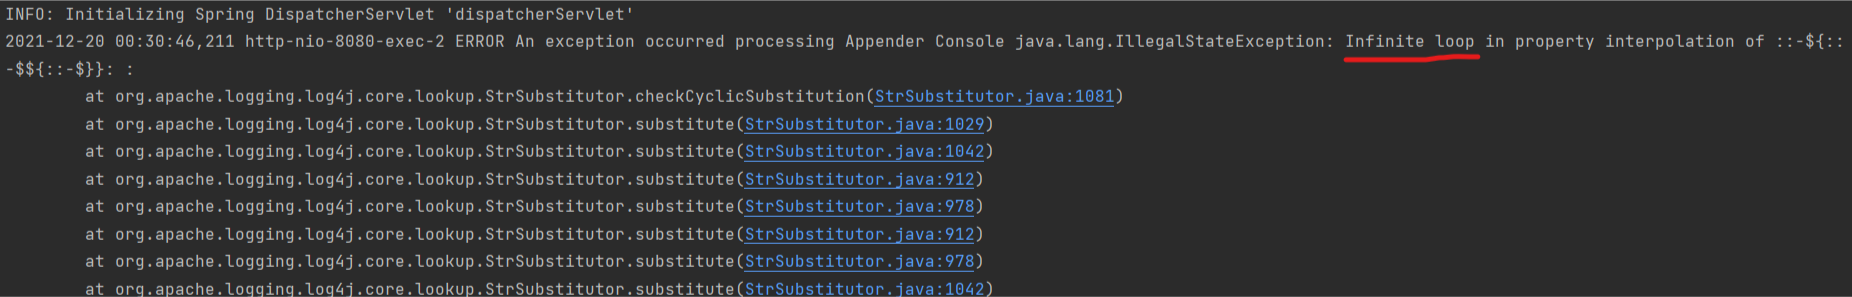 tejas-nagchandi/cve-2021-45105
Replicating CVE-2021-45105
 maikelnight/zerologon
Check for events that indicate non compatible devices -> CVE-2020-1472