
phantom-playbooks
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
defensive-toolsincident-responseintrusion-detection+4
9
corelight/phantom-playbooksAutomated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
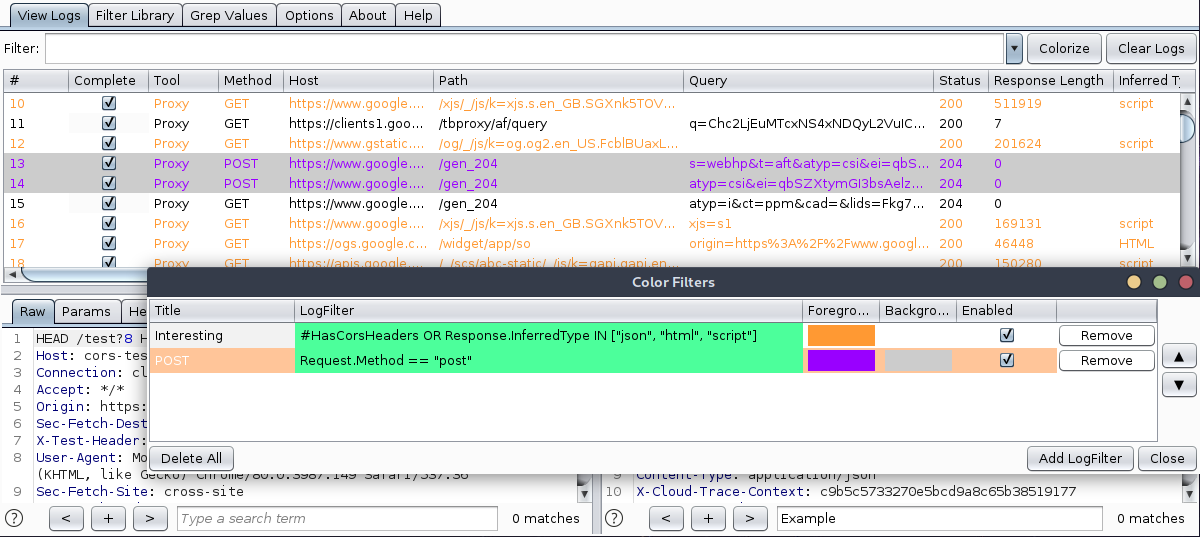 nccgroup/loggerplusplus
Advanced Burp Suite Logging Extension
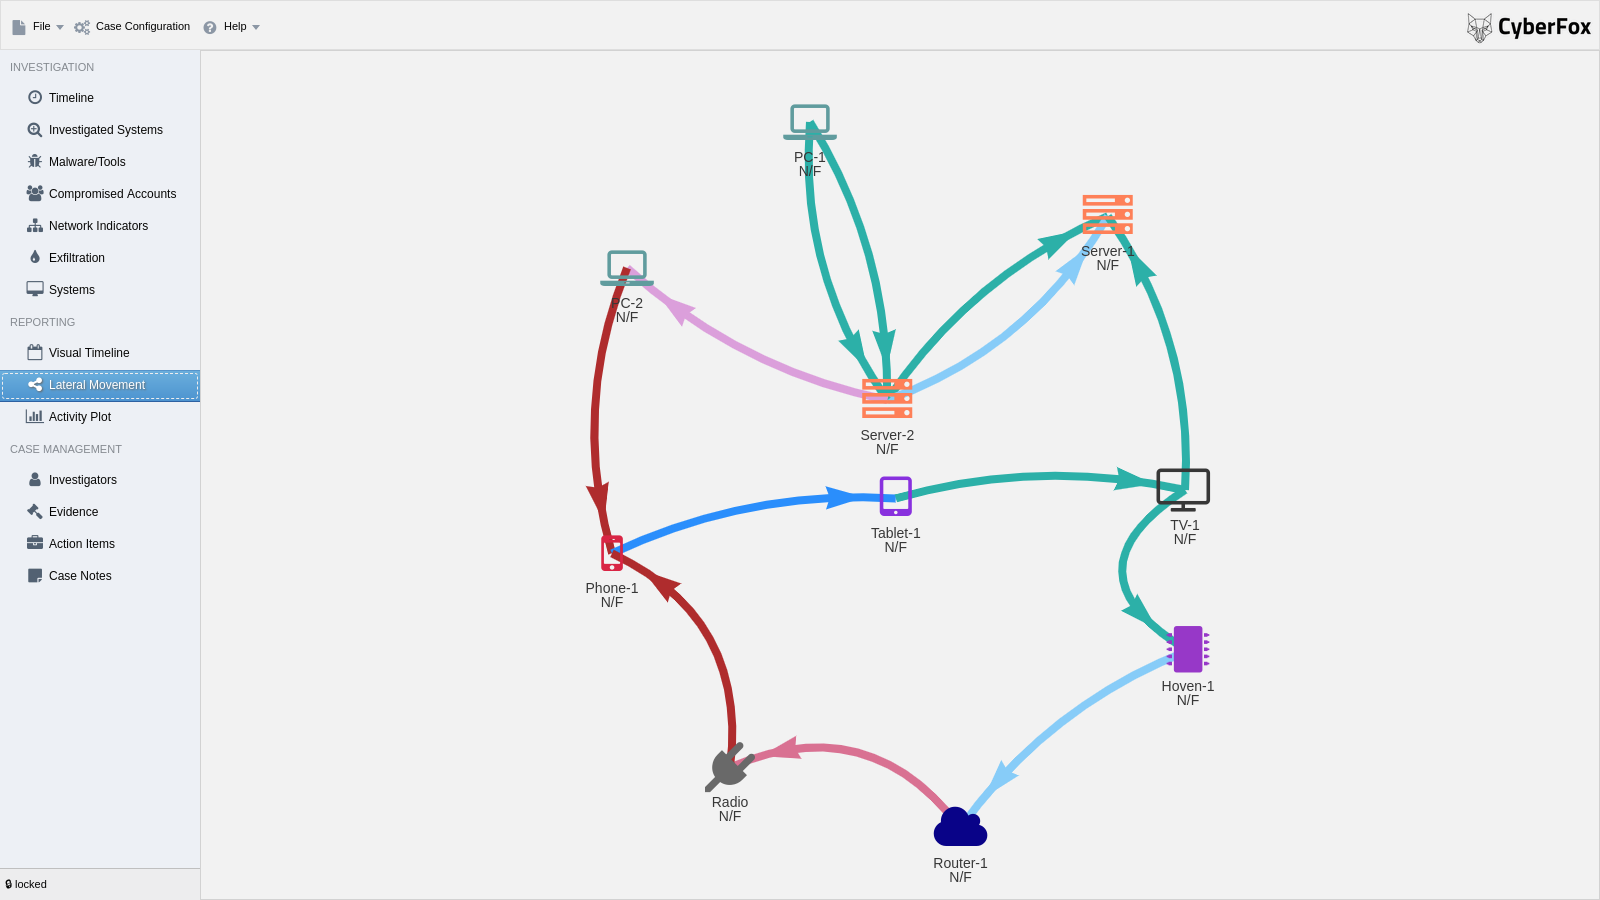 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
 d3vl/l3mon
Web-based network monitoring system providing real-time bandwidth tracking, server performance metrics, and customizable alerts for proactive network…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 nccgroup/burp-reflux
Burp proxy text log converter to CSV and SQLLite
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
 embee-research/sigma
A repository to release detection rules to the public
 nccgroup/liblapith
A really simple Nessus results library