

secfesc
 ake13-art/secfesc
Lightweight security state inspector for Linux — bridging the gap between pretty fetch tools and heavy-duty audit frameworks.
authenticationconfiguration-auditingdefensive-tools+3
ake13-art/secfescLightweight security state inspector for Linux — bridging the gap between pretty fetch tools and heavy-duty audit frameworks.
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 matthart1983/essh
Remote shells that survive connection drops, built on OpenSSH and tmux. Manage connections and sessions in a terminal UI.
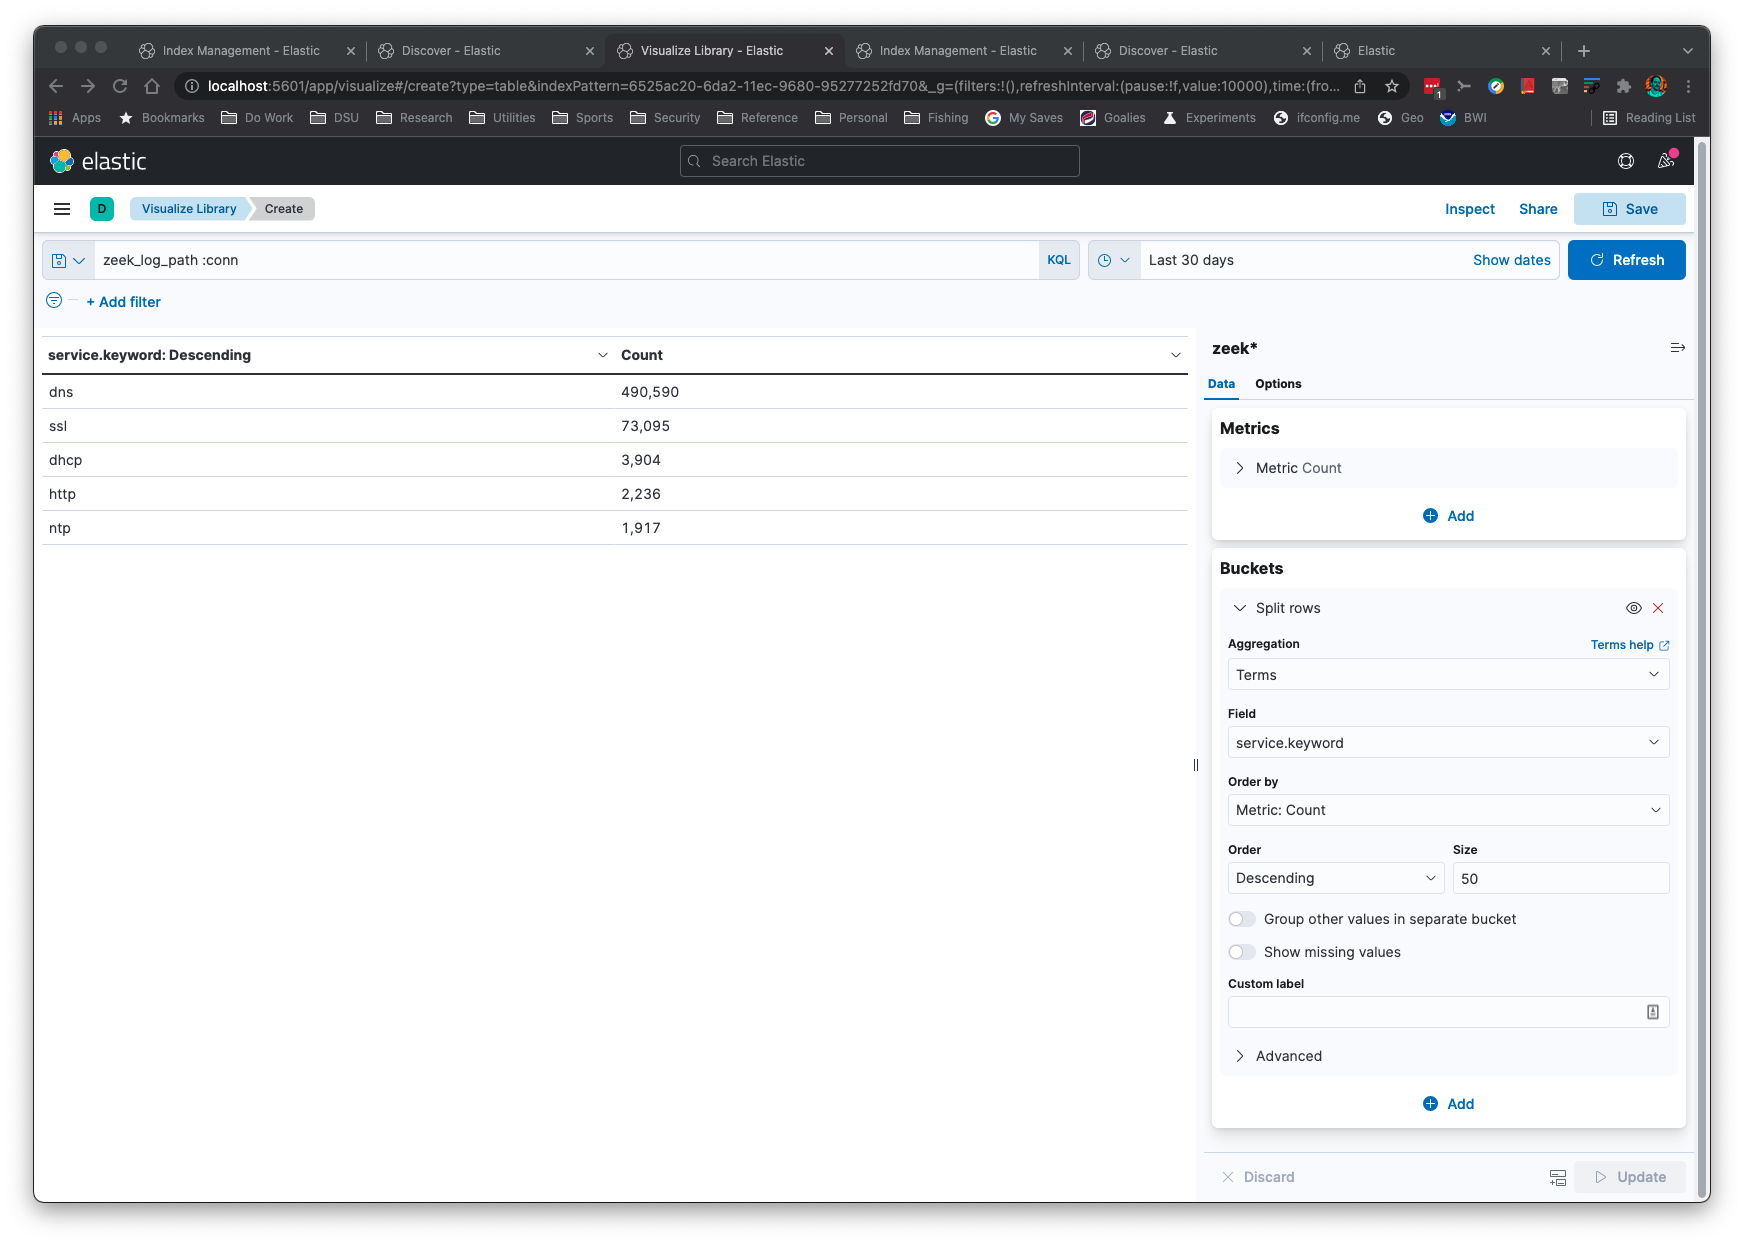 corelight/zeek2es
A Python application to filter and transfer Zeek logs to Elastic/OpenSearch+Humio. This app can also output pure JSON logs to stdout for further…
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…

 onotelli/justniffer
libpcap-based TCP packet sniffer that decodes HTTP traffic, reassembles streams, and emits customizable access-log style output with request/response…
 shanika04/dashbuilder
CVE-2016-4999

 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.