
CVE-2025-20384
 axselll/cve-2025-20384
Proof-of-concept demonstrating log injection and poisoning in Splunk via crafted URL parameters, highlighting OWASP log injection risks.
educationexploitationlog-analysis+3
axselll/cve-2025-20384Proof-of-concept demonstrating log injection and poisoning in Splunk via crafted URL parameters, highlighting OWASP log injection risks.
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 s0/rsyslog-librelp-cve-2018-1000140-fixed
Patch for CVE-2018-1000140 in rsyslog's librelp library, fixing a remote code execution vulnerability in the reliable event logging protocol…
 safedep/gryph
Security layer for AI coding agents. Works with Claude Code, Cursor, Windsurf, Gemini CLI, OpenCode, Pi Agent and more.
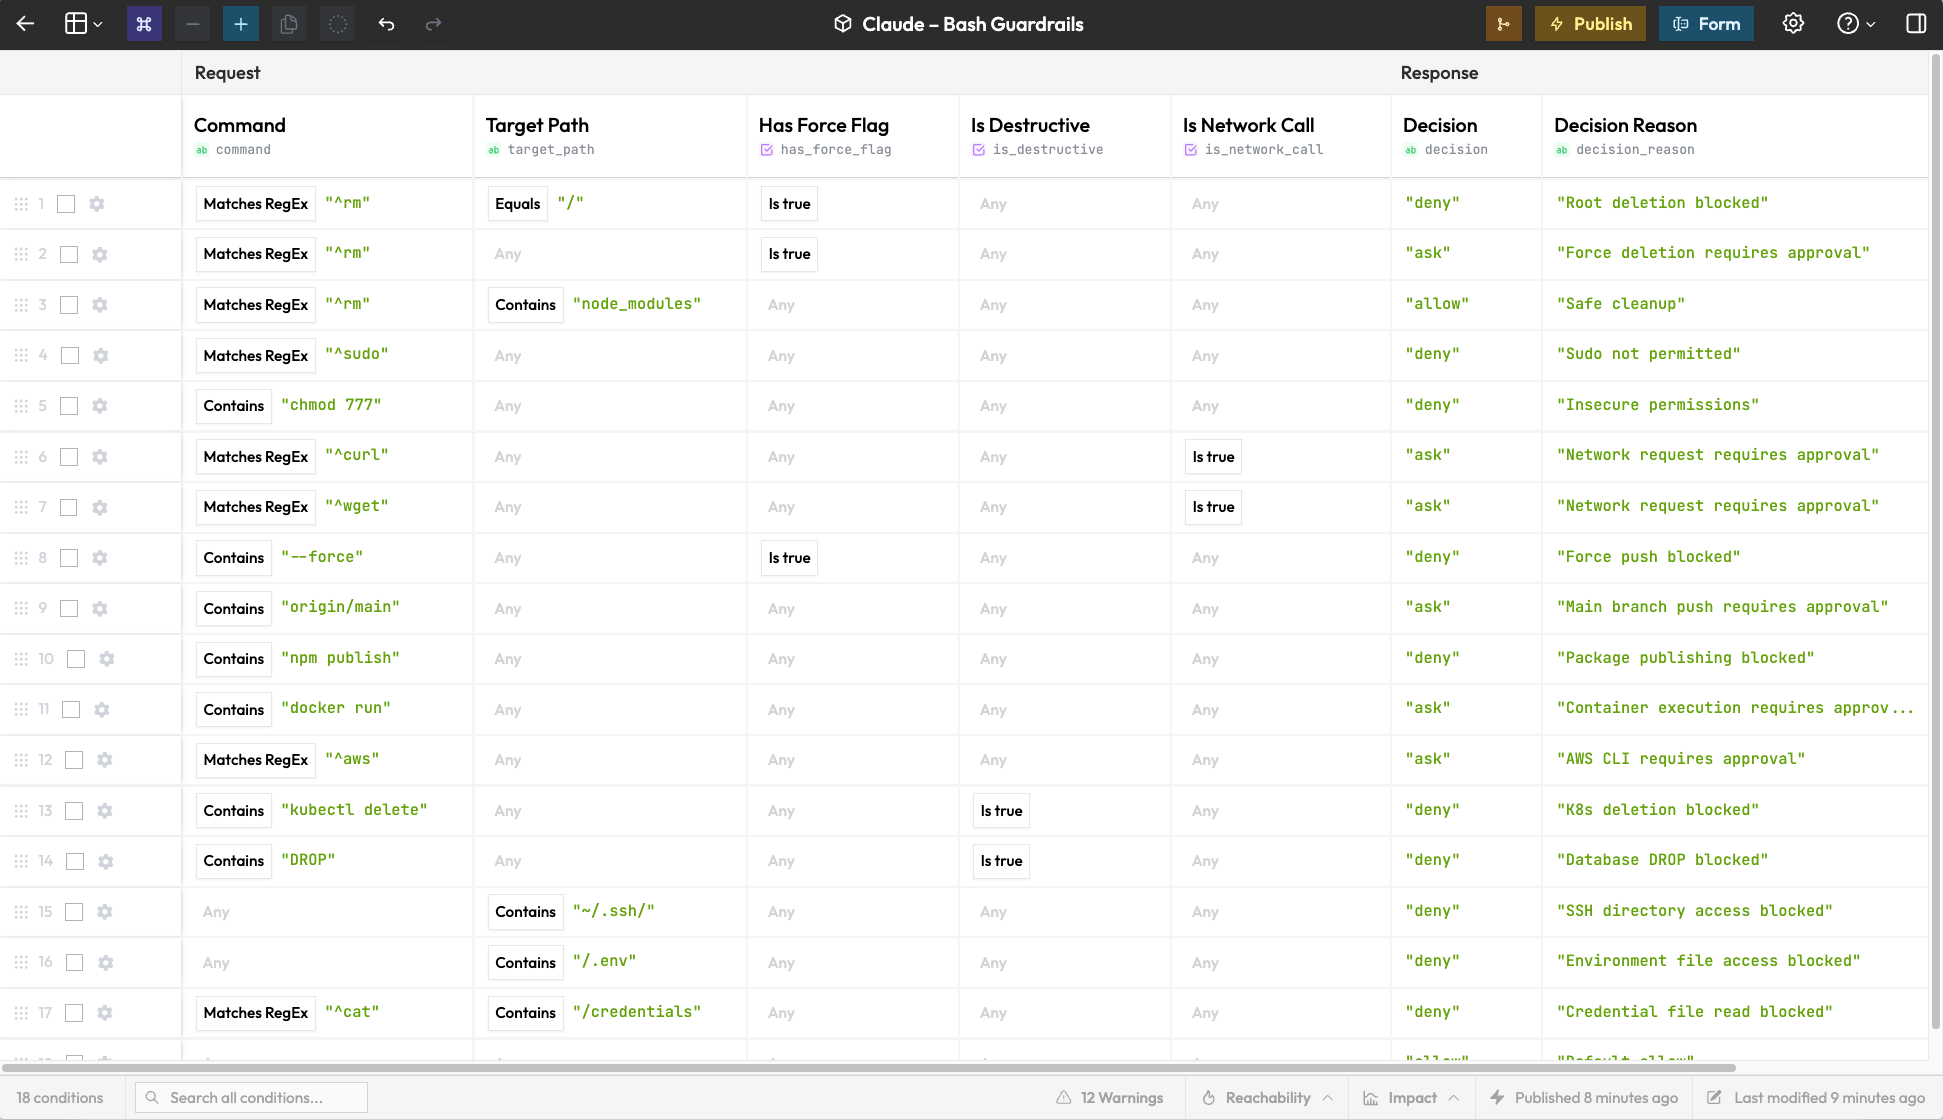 rulebricks/claude-code-guardrails
Real-time guardrails for Claude Code tool calls.
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 adityabhatt3010/cve-2025-61882-oracle-e-business-suite-pre-auth-rce-exploit
A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
 garethmsheldon/fortinet-fortiweb-fabric-connector-cve-2025-25257-detection
This repository provides production-ready detection engineering content for **CVE-2025-25257**, a pre-authentication SQL Injection vulnerability in…
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 fireeye/cve-2021-44228
OpenIOC rules to facilitate hunting for indicators of compromise
 letlaka/redsun-bluehammer-undefend-detection-pack
Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

 kavryxdev-group/sandboxed-untrusted-code-execution-runner
Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.