
Invoke-DumpMDEConfig
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
configuration-auditingdefensive-toolsforensics+3
155
blacksnufkin/invoke-dumpmdeconfigPowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
 mingchen-script/cve-2020-1472-visualizer
PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
 gmh5225/zeropoint
This PowerShell script detects indicators of compromise for CVE-2025-53770 — a critical RCE vulnerability in Microsoft SharePoint. Created by…
 rjsudlow/proxynotshell-ioc-checker
Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
 ace-responder/cve-2022-47966_checker
Run on your ManageEngine server
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
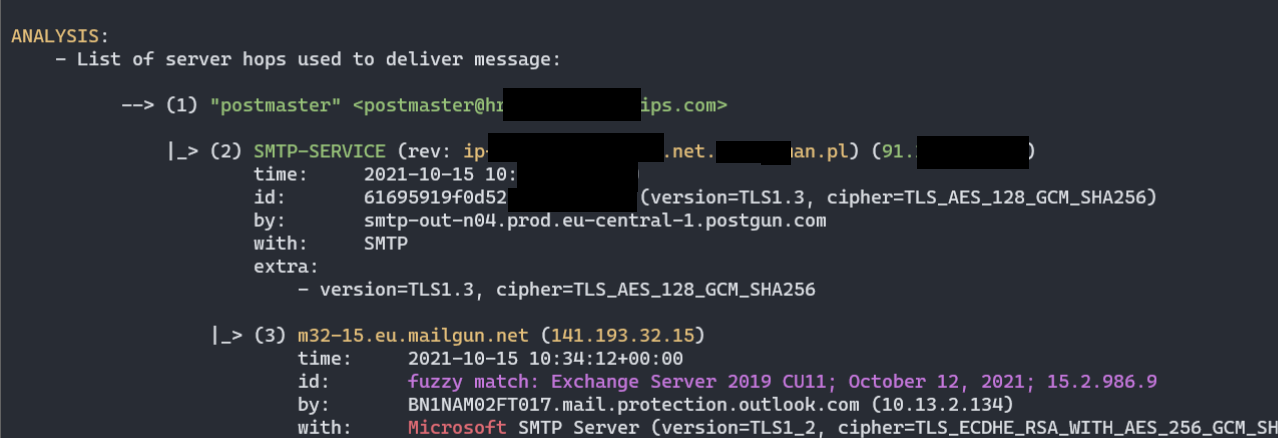 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 corelight/raspi-corelight
Corelight@Home script
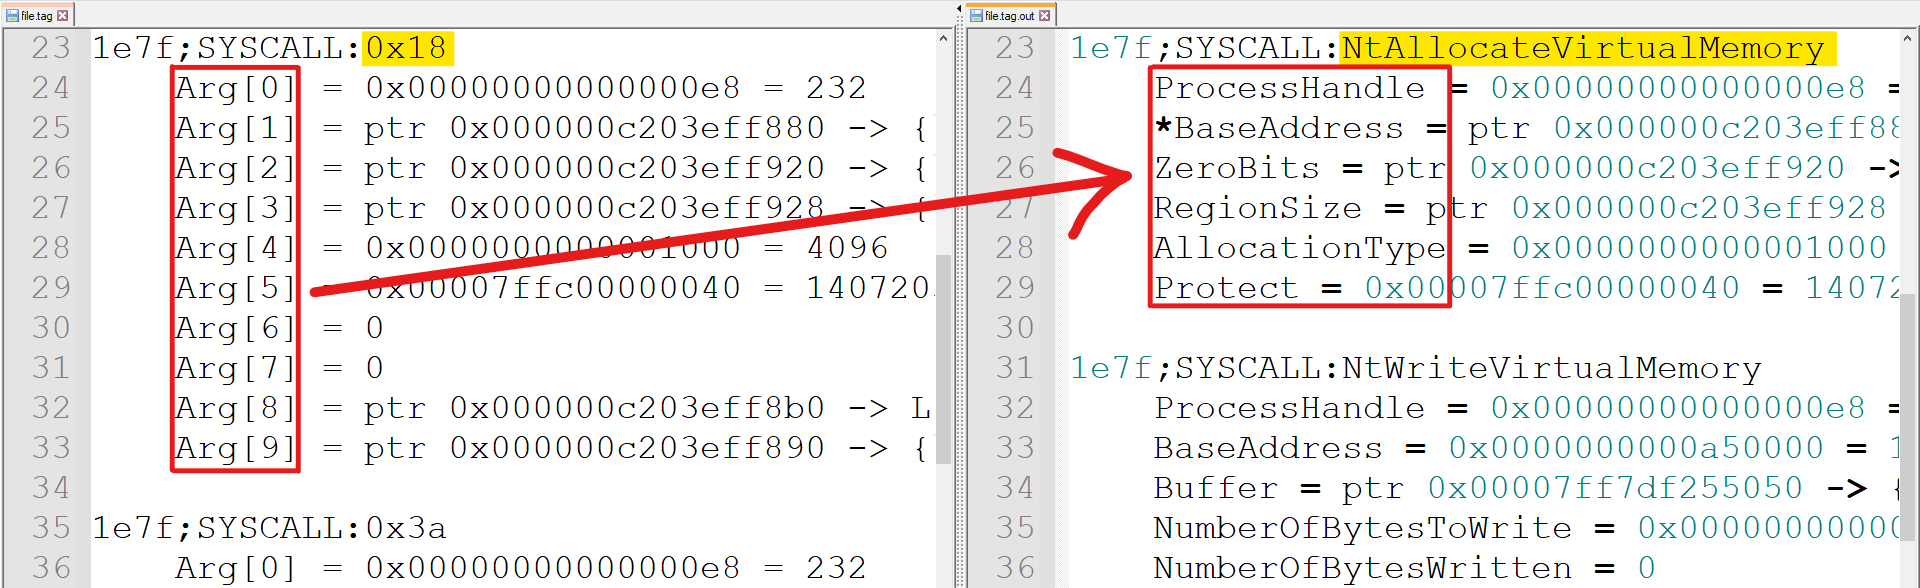 goatmilkkk/tinyprocessor
A post-processing script for TinyTracer
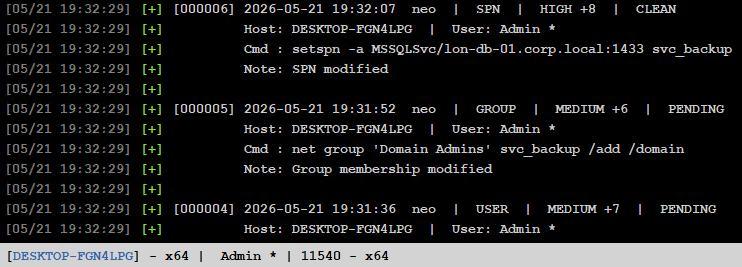 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 f5devcentral/cve-2020-5902-ioc-bigip-checker
Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…