

hawk
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
cloud-infrastructure-securitycloud-securitydigital-forensics+3
956
t0pcyber/hawkPowershell Based tool for gathering information related to O365 intrusions and potential Breaches
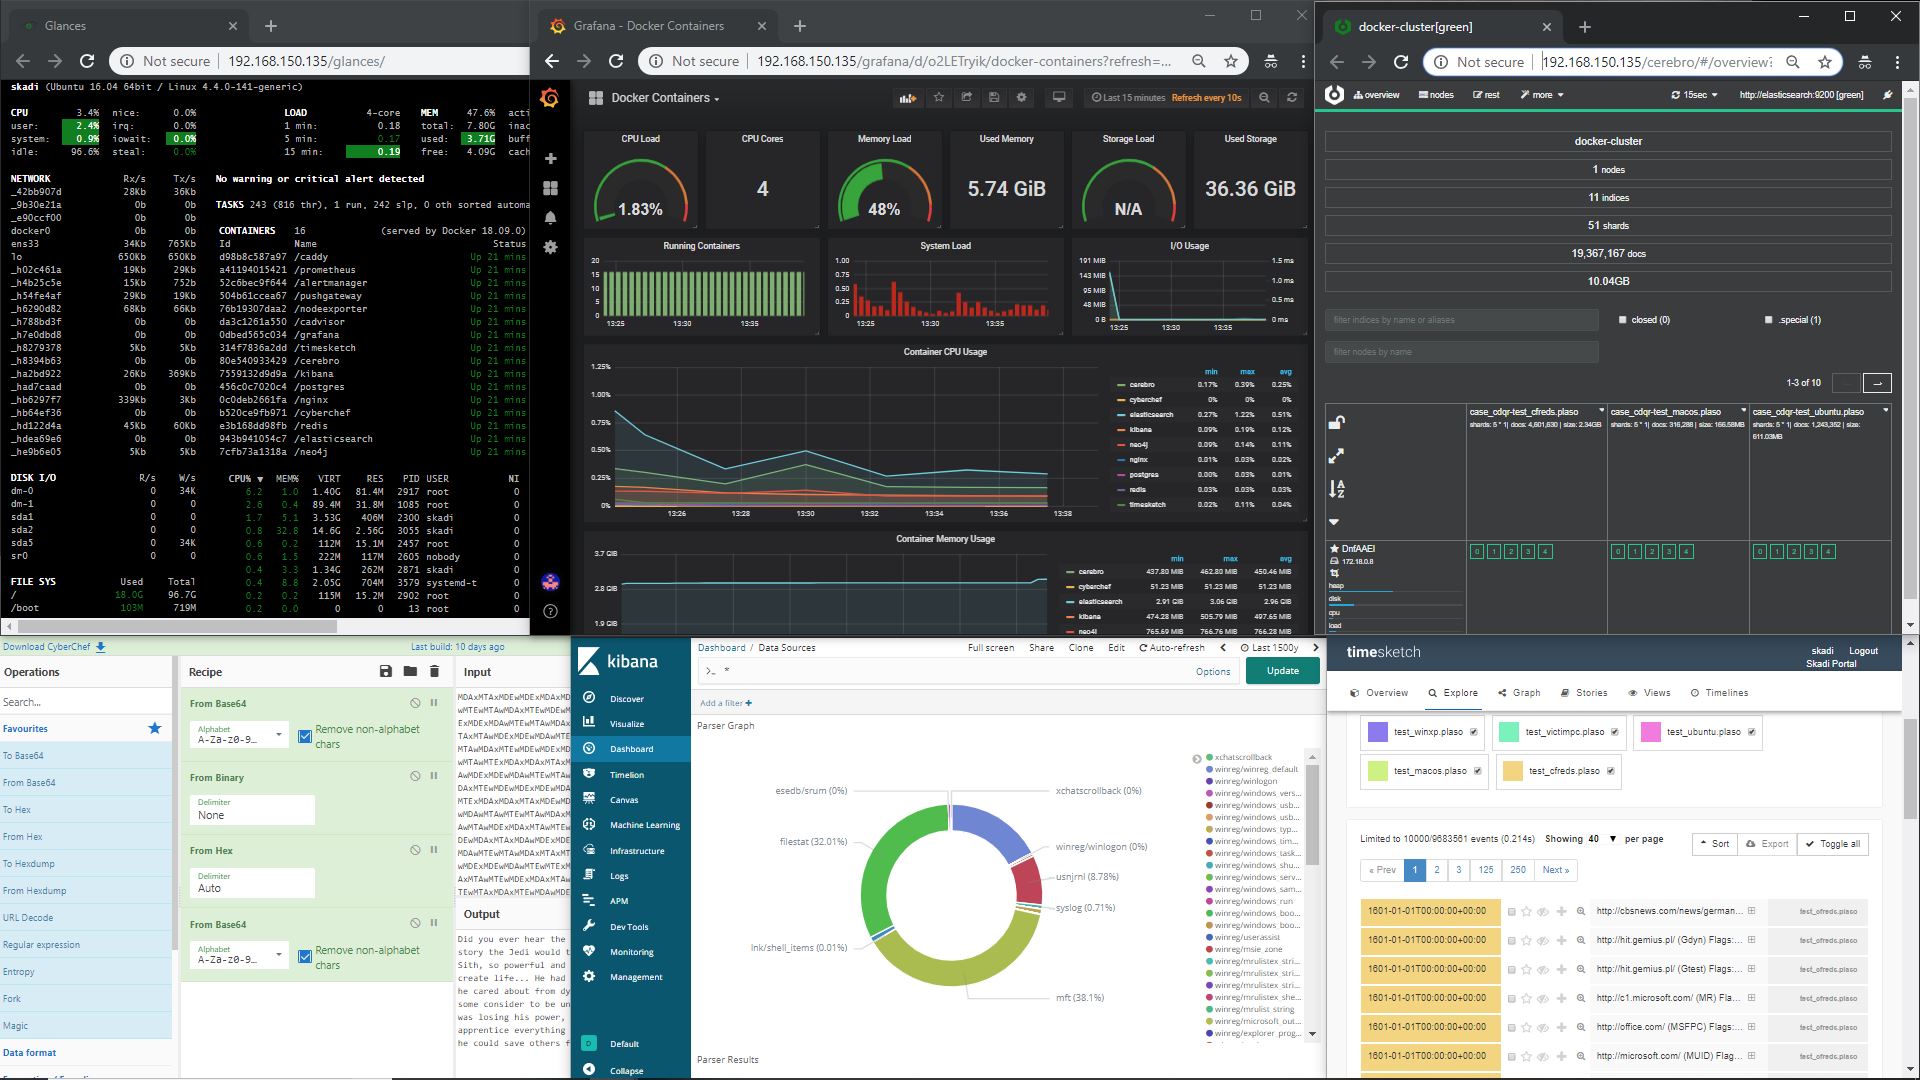 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 corelight/zeek-spicy-openvpn
A Zeek OpenVPN protocol analyzer, based on Spicy.

 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 arisharazakhan-cpu/dod-blue-team-network-lab
High fidelity defensive security lab simulating a DoD aligned enterprise network with Active Directory, VLAN segmentation, STIG based hardening,…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 0x4d31/salt-scanner
Linux vulnerability scanner based on Salt Open and Vulners audit API, with Slack notifications and JIRA integration
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 logpai/loglizer
A machine learning toolkit for log-based anomaly detection [ISSRE'16]
 ghostop14/sparrow-wifi
Next-Gen GUI-based WiFi and Bluetooth Analyzer for Linux
