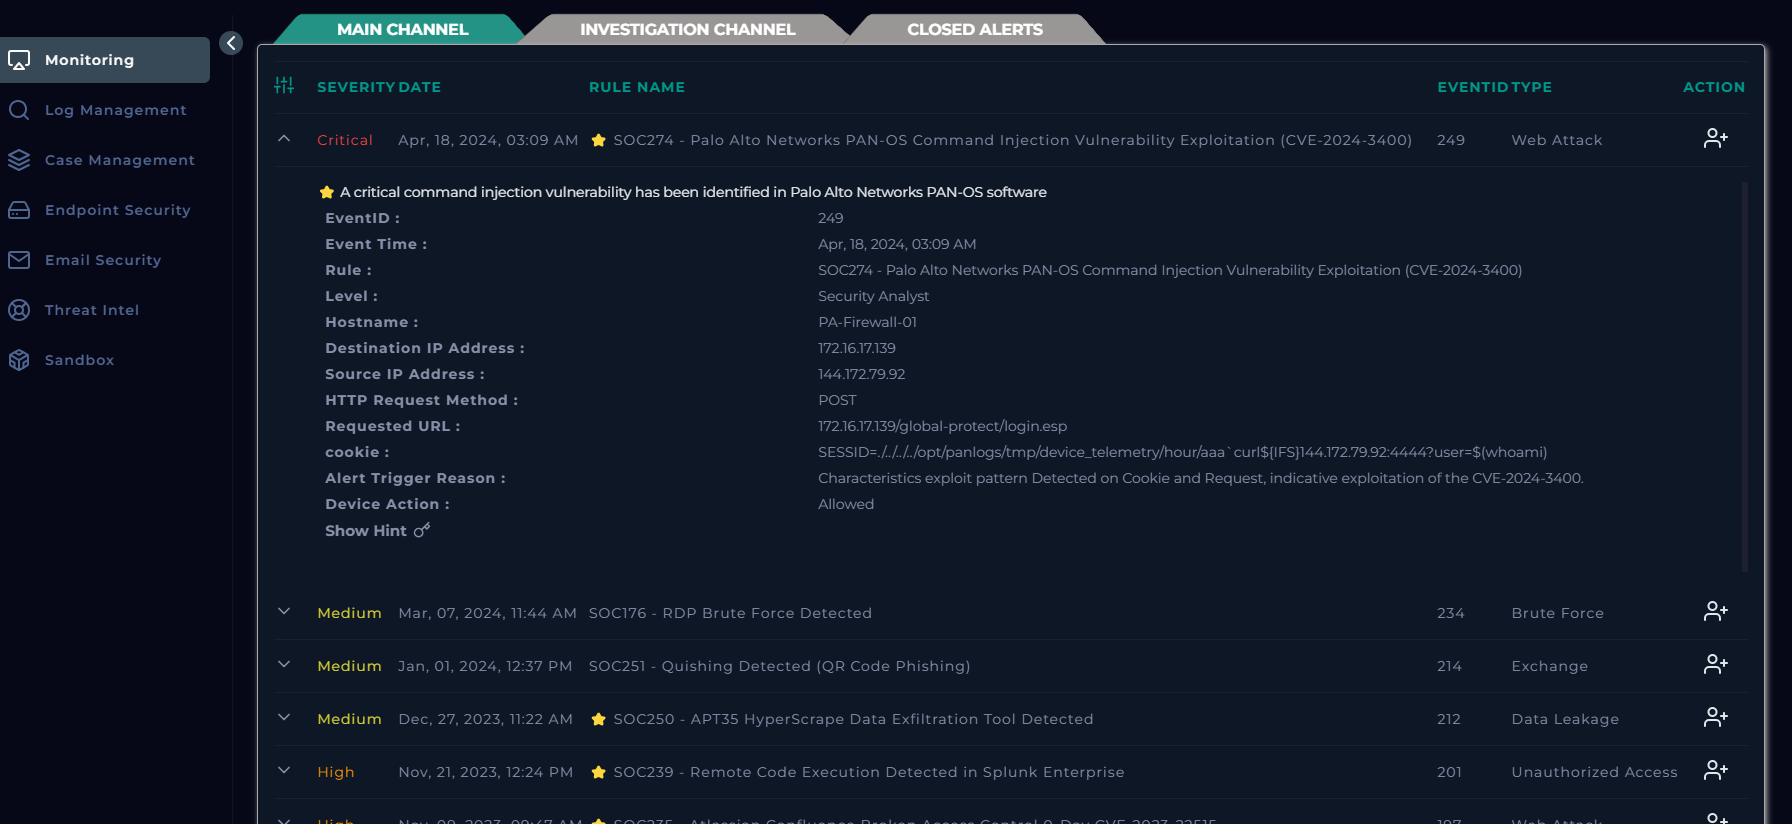
letsdefend-cve2024-3400-case-study

Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…

Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…

Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).

Kusto query-based detection and analysis tool for CVE-2021-44228 (Log4Shell) vulnerability, enabling rapid log hunting and exploitation…

SIEM query collection for detecting Log4Shell (CVE-2021-44228) exploitation attempts. Provides ready-to-use detection rules for security monitoring…

Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 9 more ran, and flags risky actions and leaked…

Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…

Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…

Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.

SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…

Some Threat Hunting queries useful for blue teamers

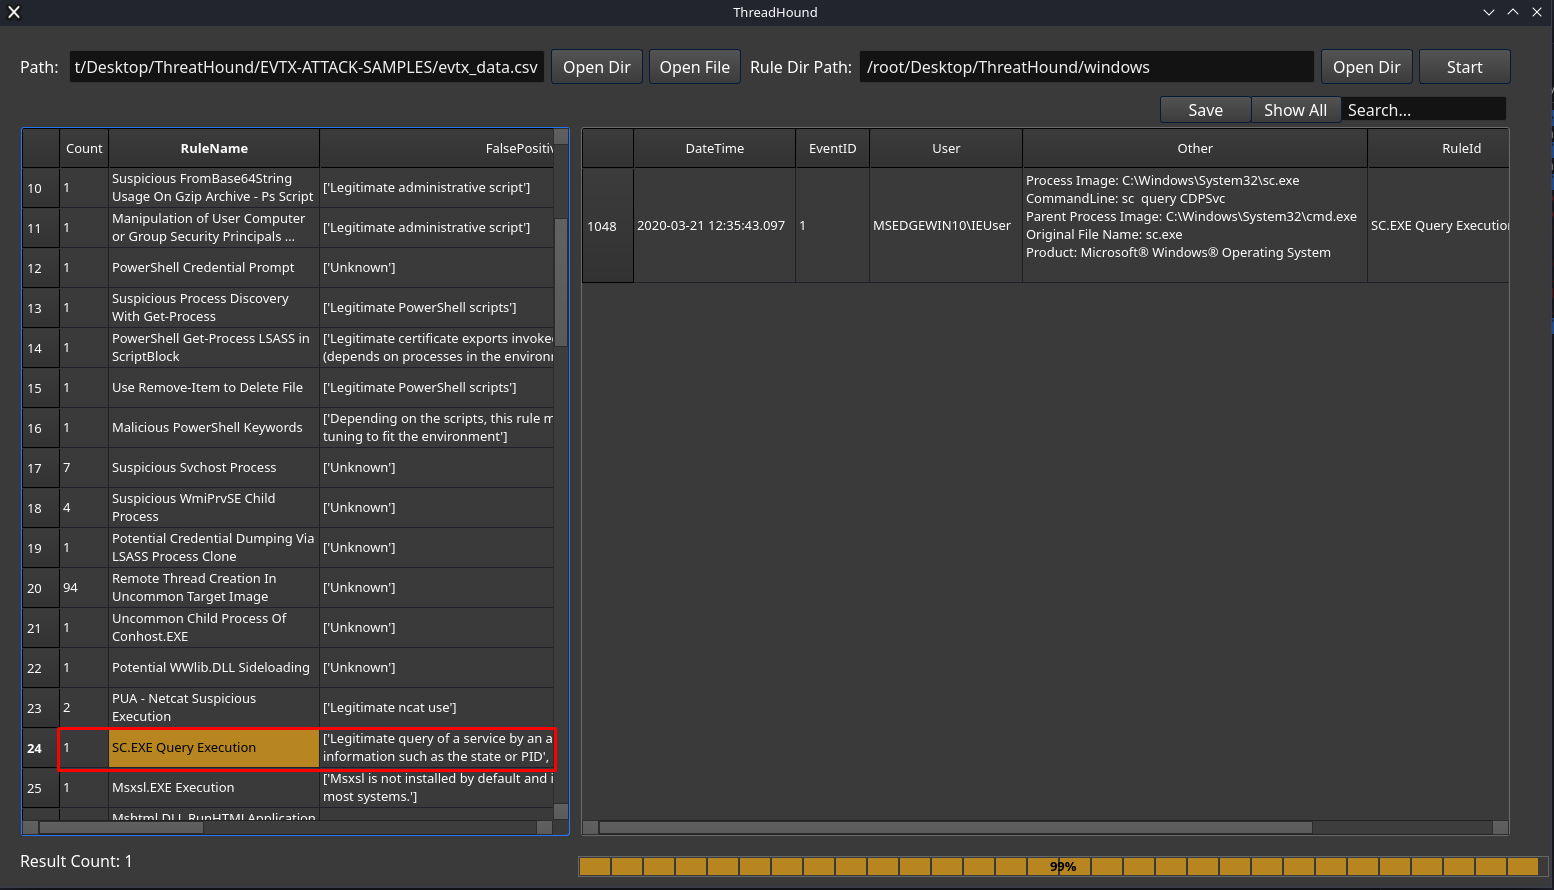
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…

Kernel-level security & attack response for Linux servers.

Burp proxy text log converter to CSV and SQLLite

Tuning and refactoring Google Chronicle Curated Detections to eliminate alert fatigue and fix logic gaps/bugs.

Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…

Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…

Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…

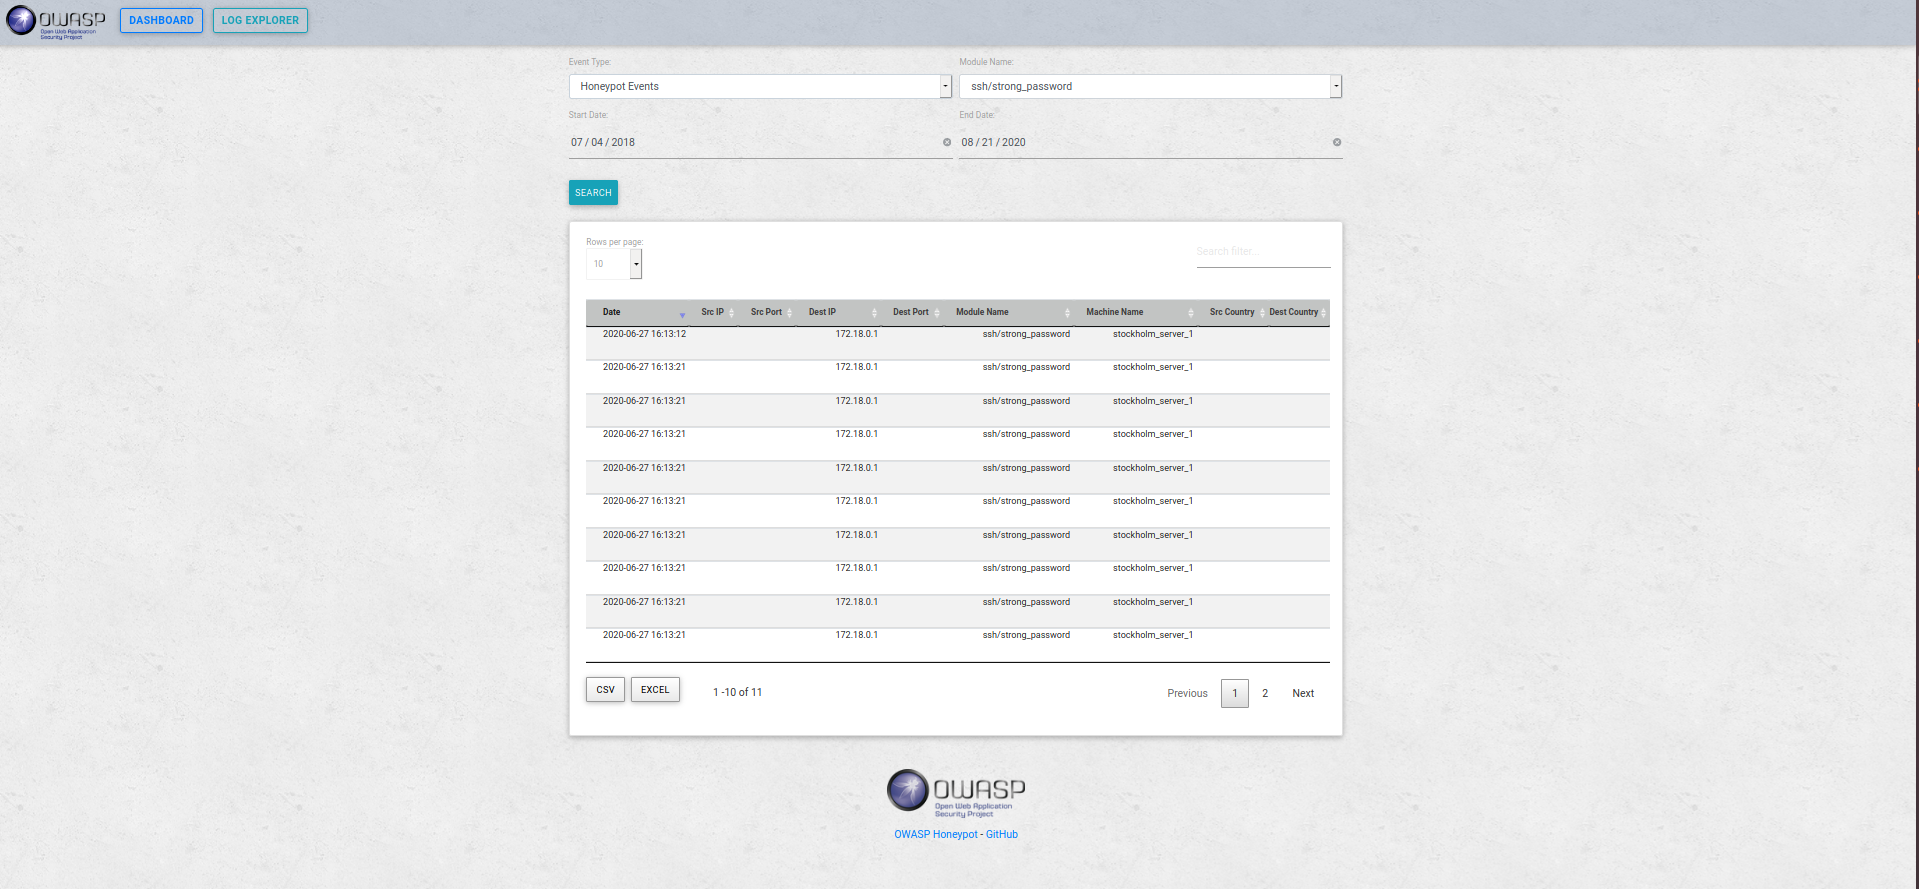
OWASP Honeypot, Automated Deception Framework.