
DFIR-O365RC
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection
cloud-securitydigital-forensicsforensics+2
anssi-fr/dfir-o365rcPowerShell module for Office 365 and Azure log collection
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 byteray-labs/query-hub
CQL Hub is an open repository of detection and hunting queries for CrowdStrike NextGen SIEM and Falcon LogScale. All queries stored here are…
 sims718718/unifiedthreathunting
Documents a structured, repeatable threat hunting methodology covering triggers, SMART hypotheses, feasibility gates, scoping, hunt plans, and…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
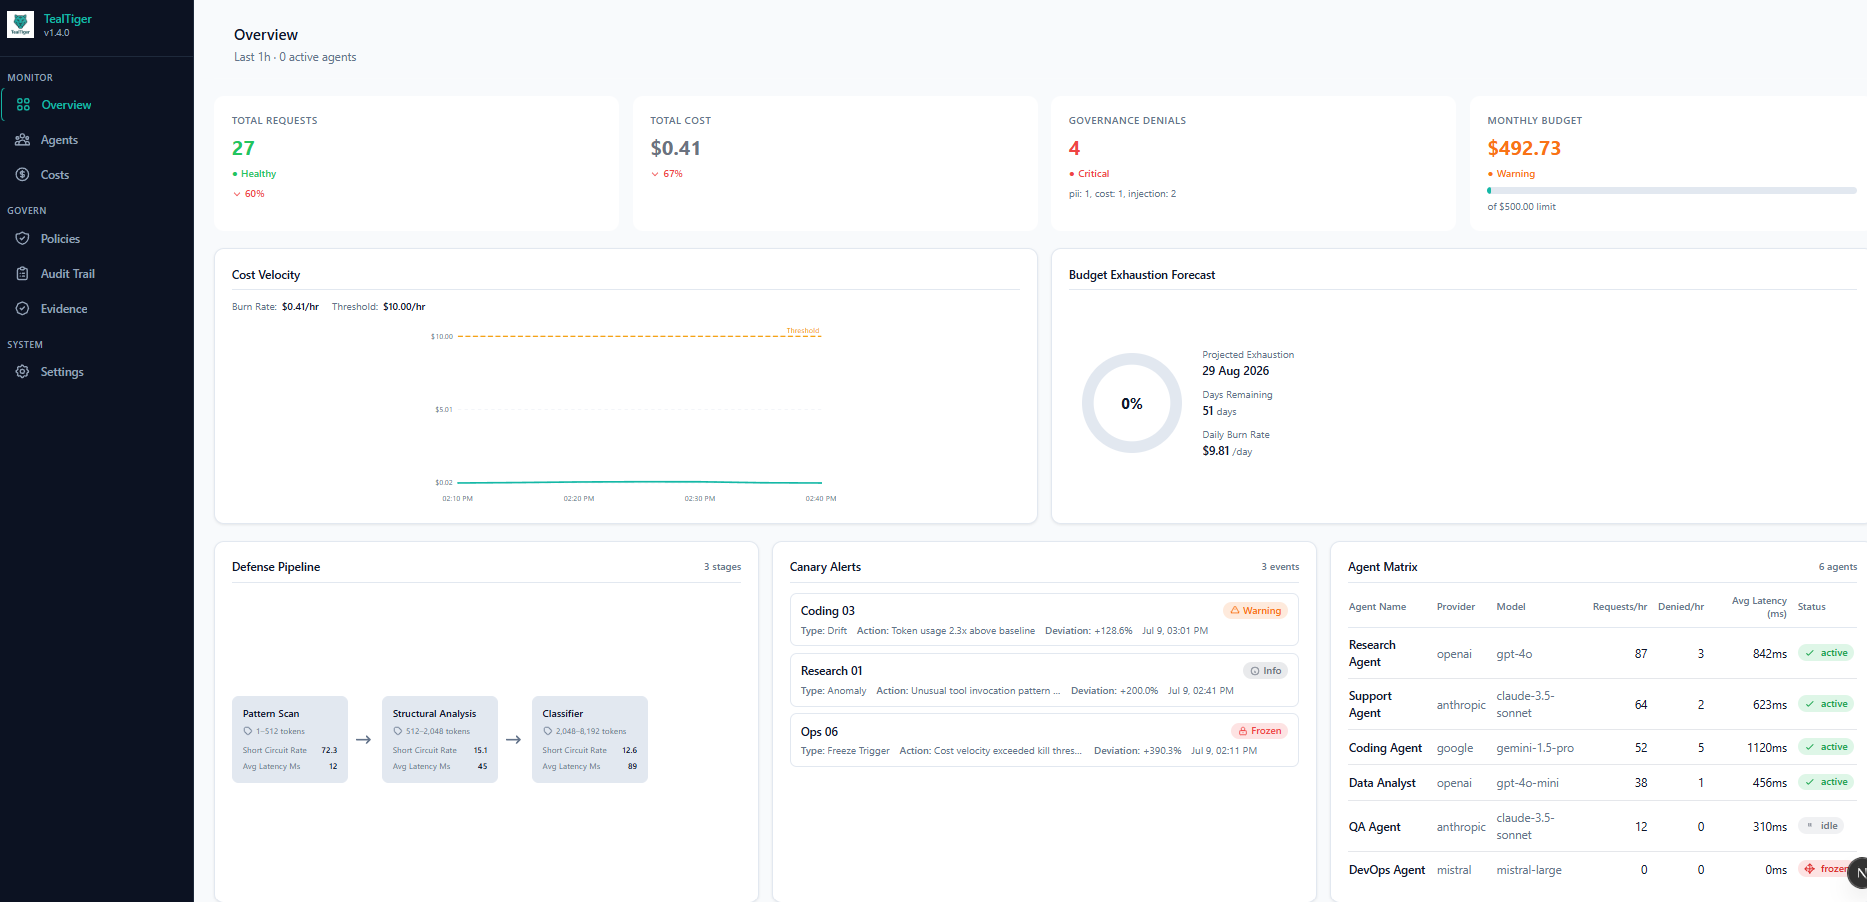 agentguard-ai/tealtiger
Powerful protection for AI agents - Open-source security and cost tracking for AI applications
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 twocanoes/audit
Audit Preference Pane and Log Reader for OS X
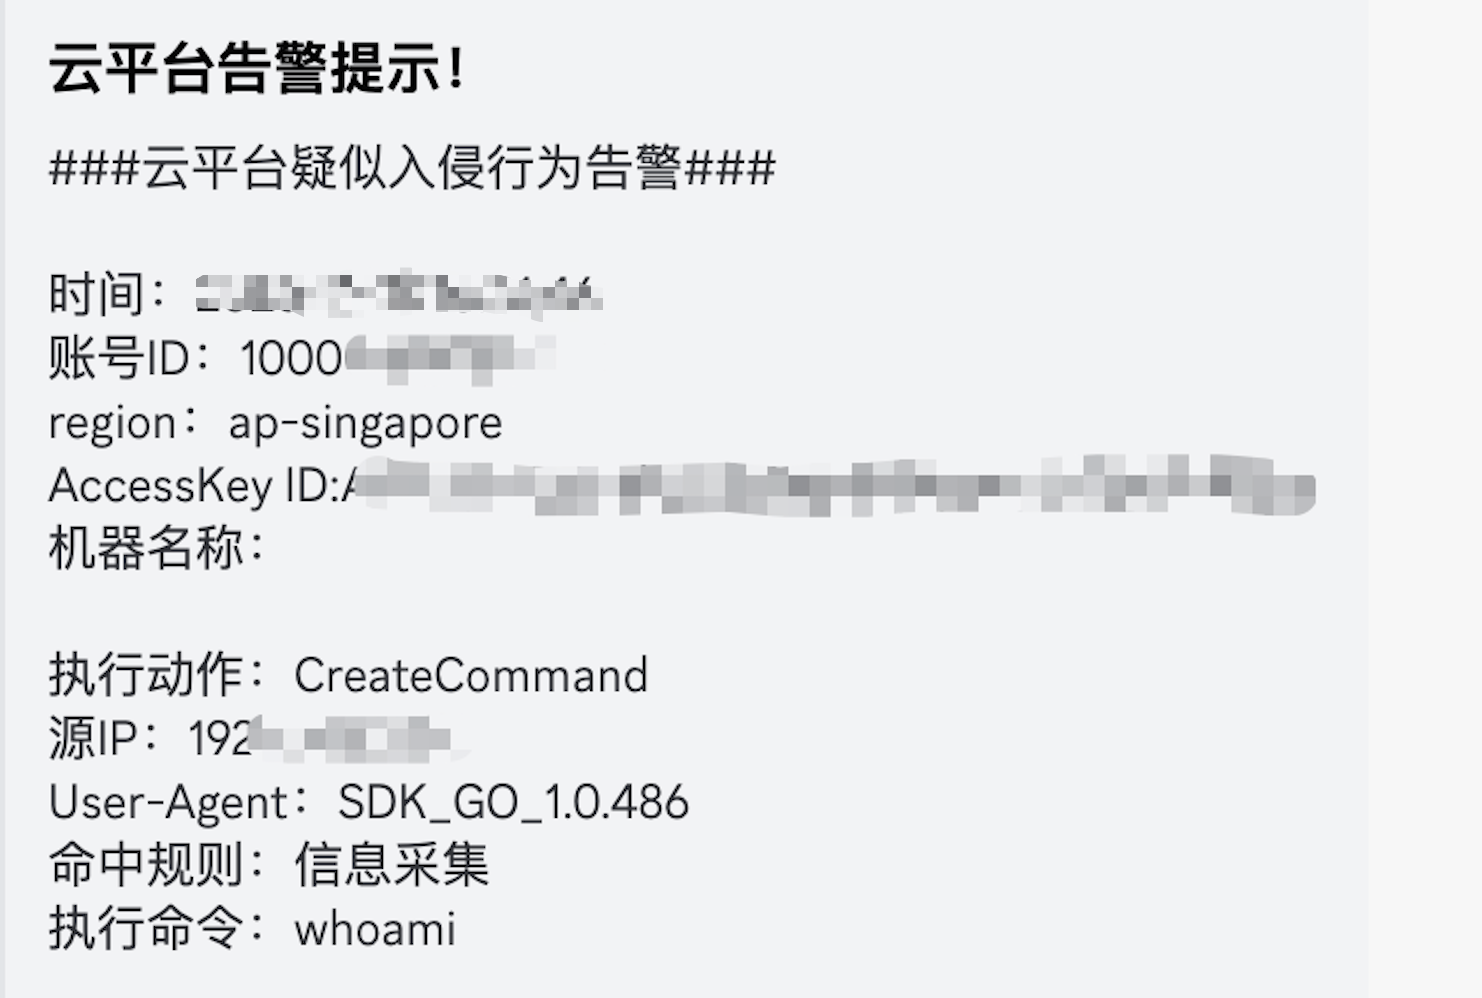 al0ne/cloud-audit
Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
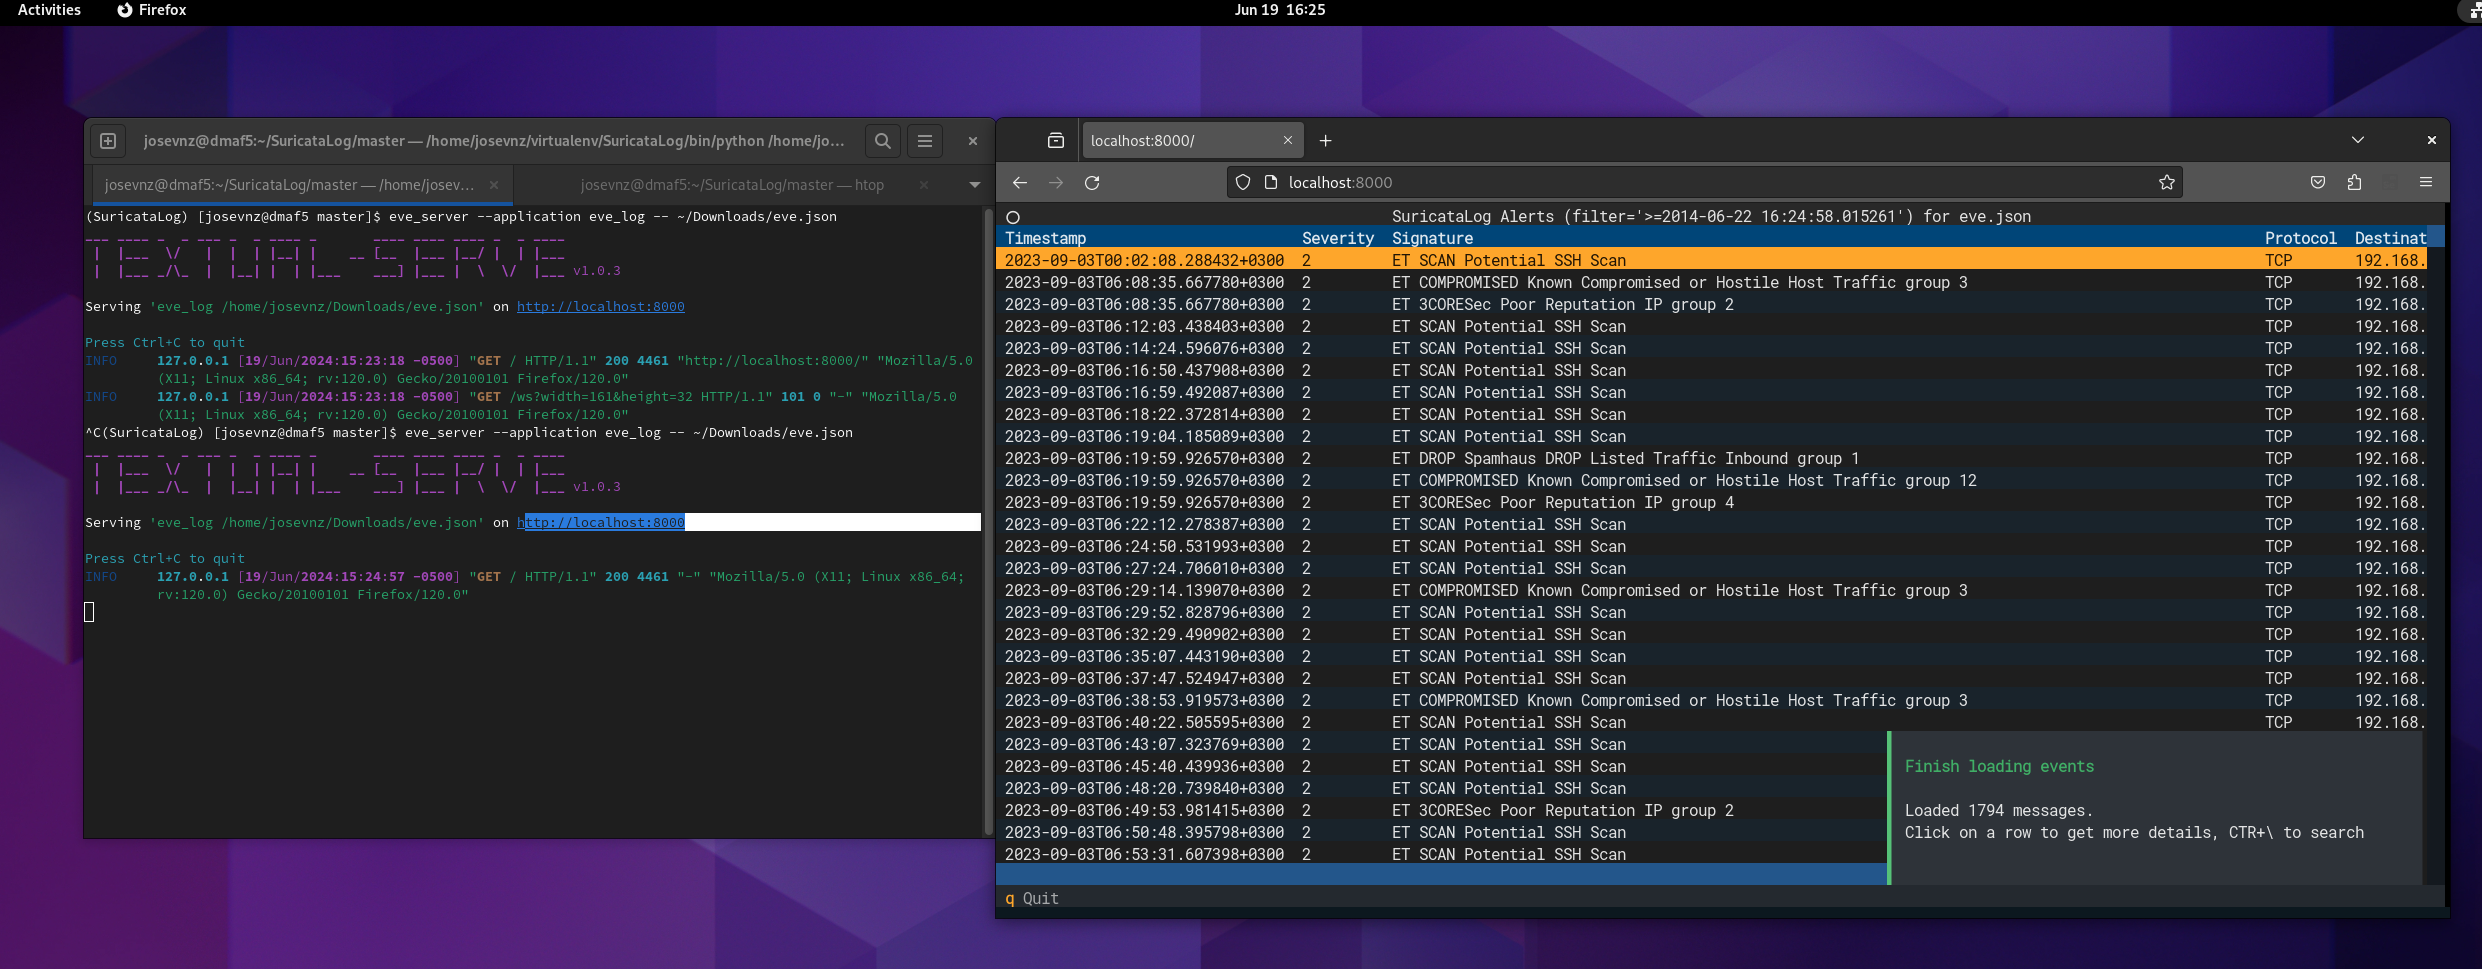 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
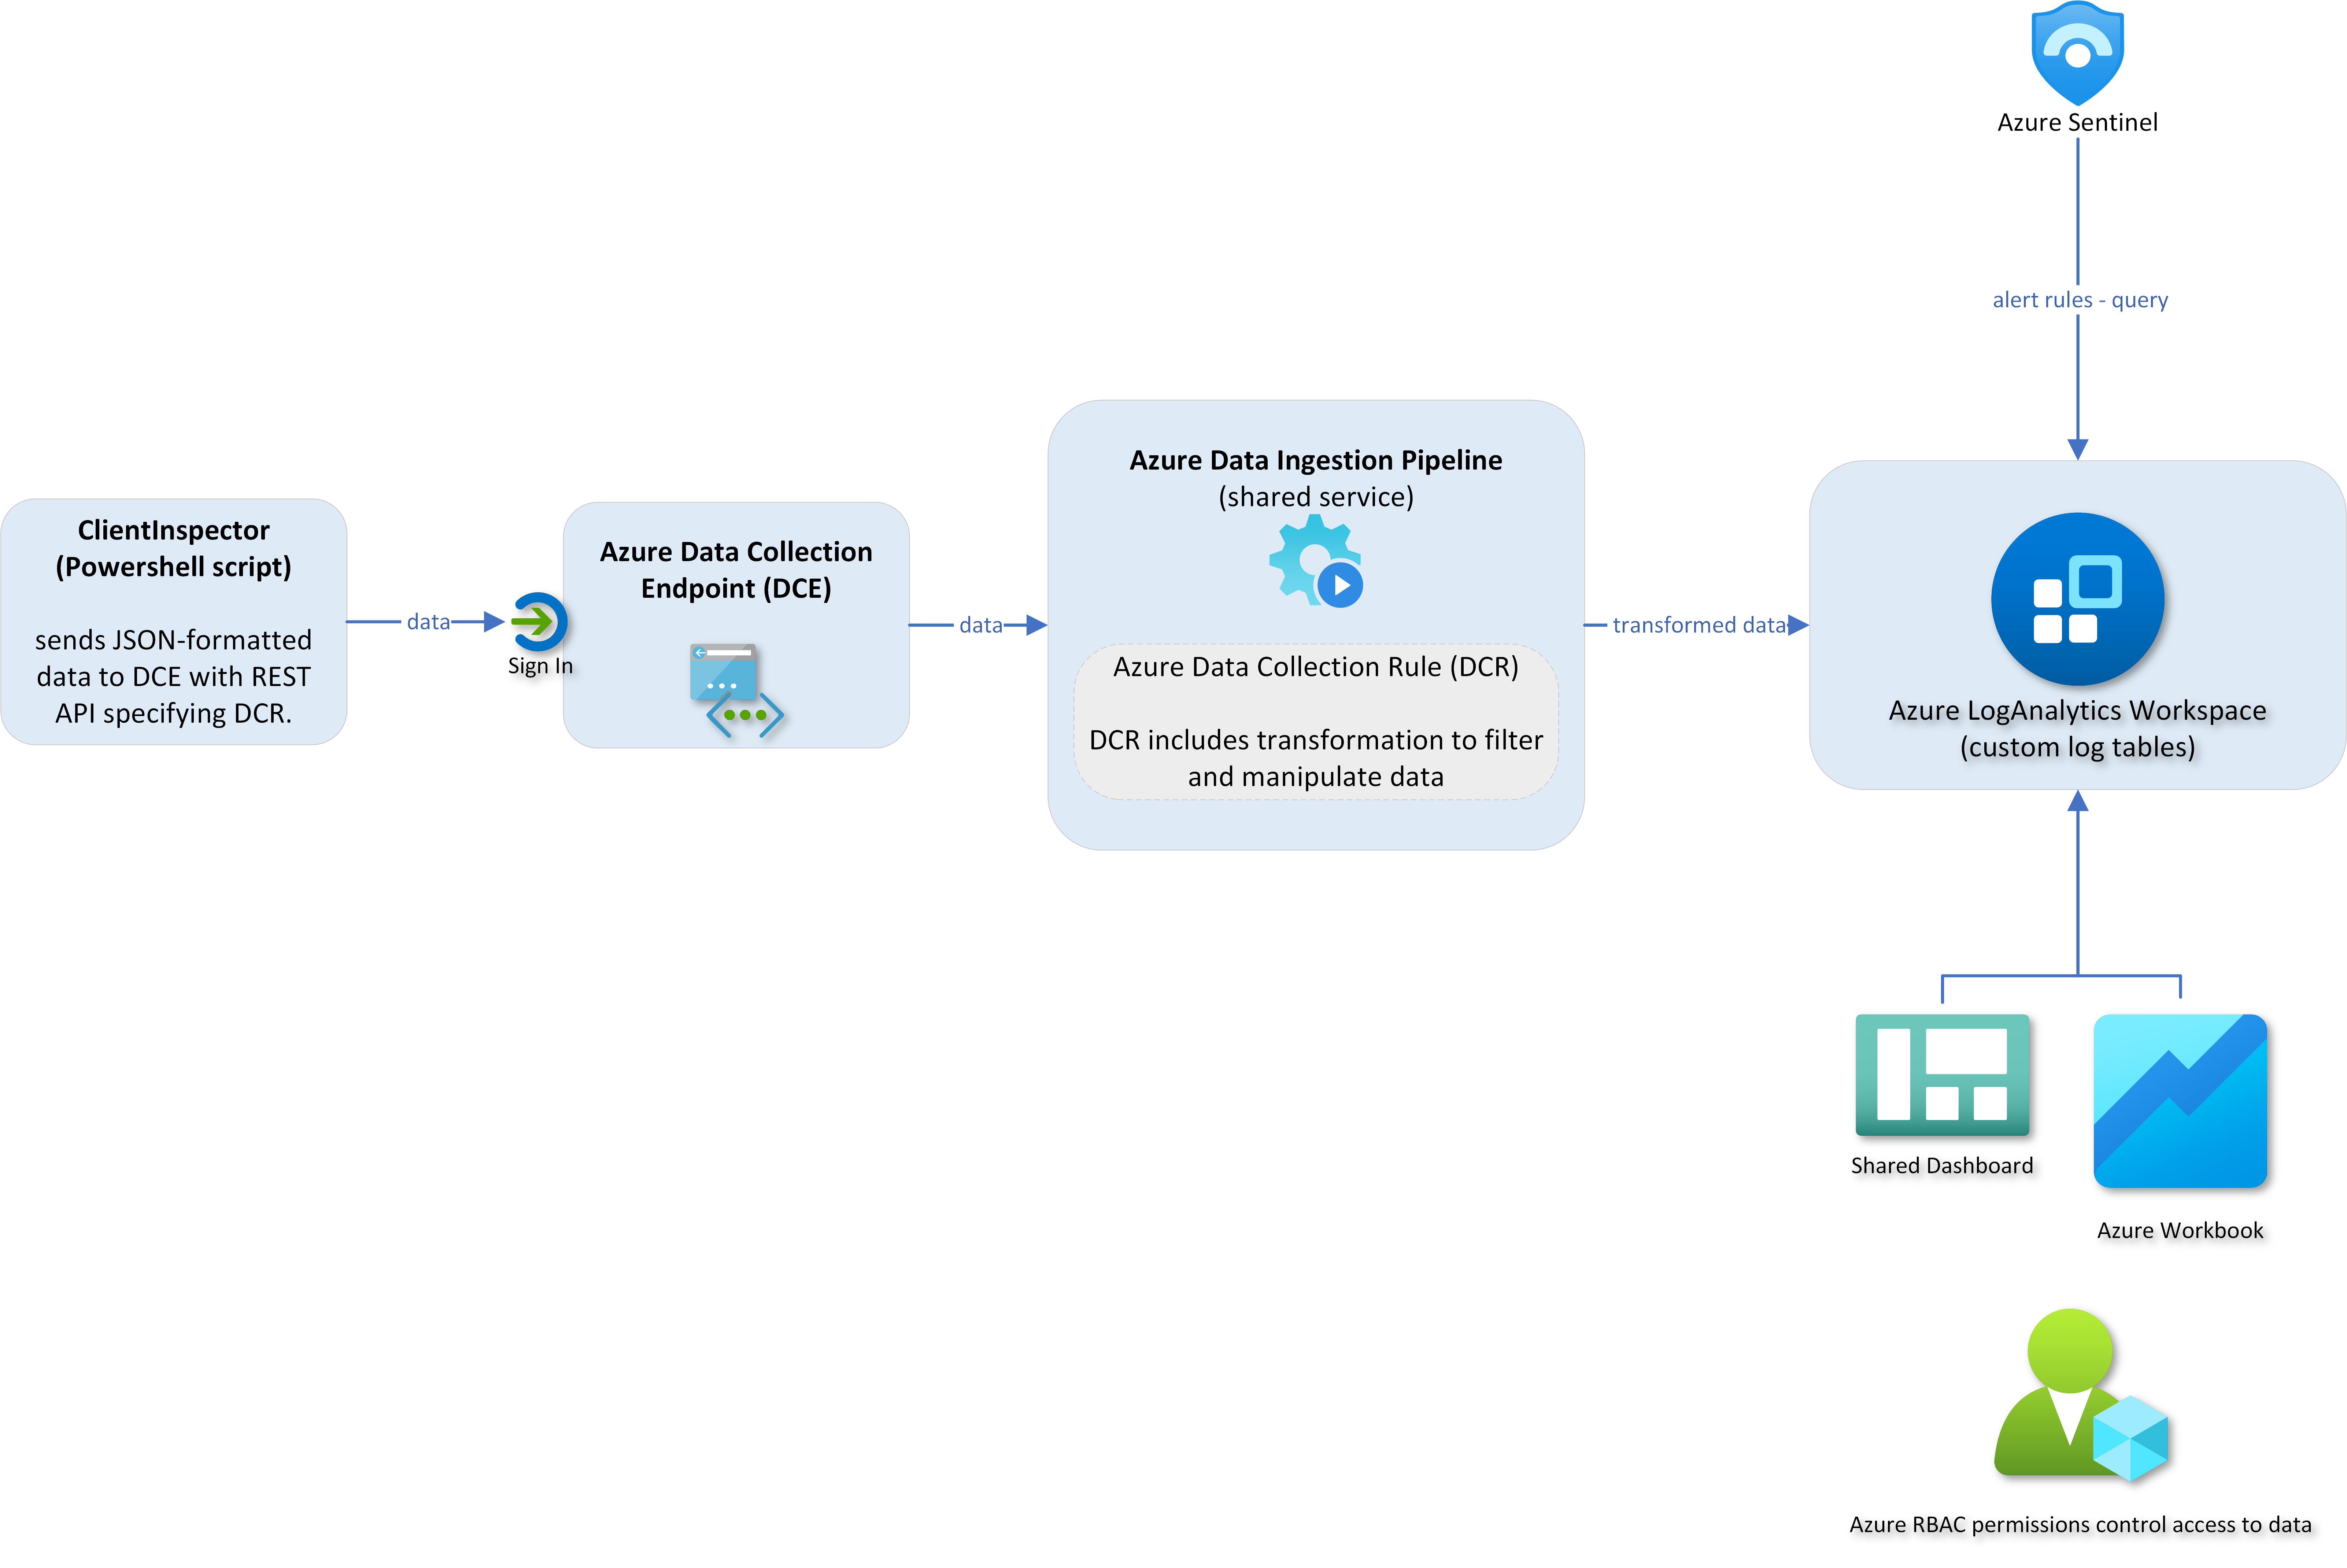 knudsenmorten/clientinspectorv2
Azure-based client inventory and drift detection tool that collects Windows configuration data (antivirus, patching, Bitlocker) into LogAnalytics for…
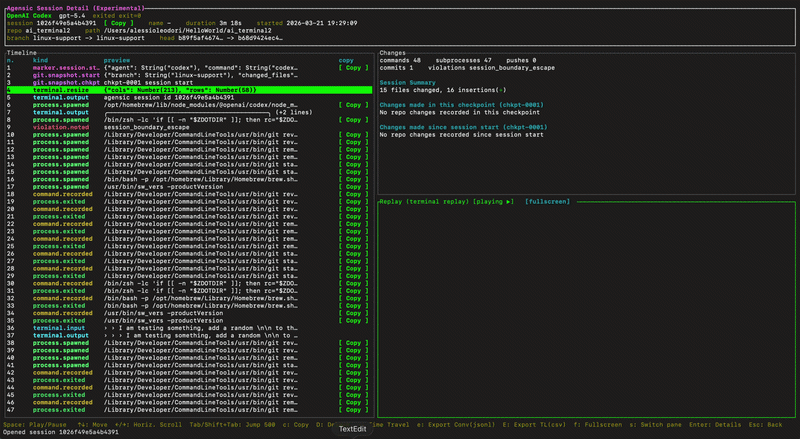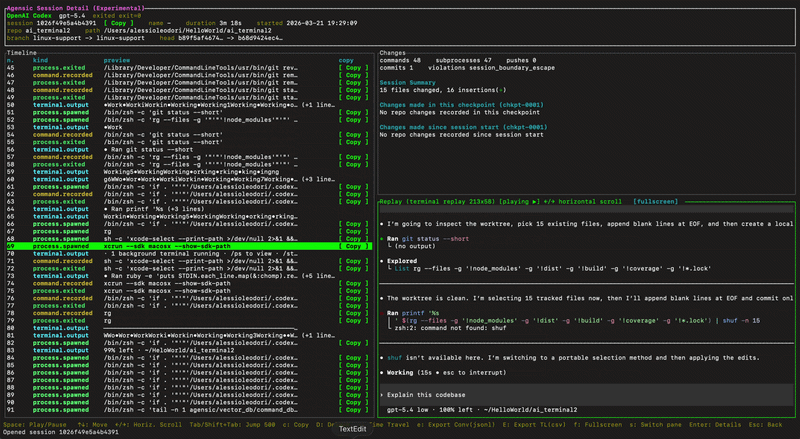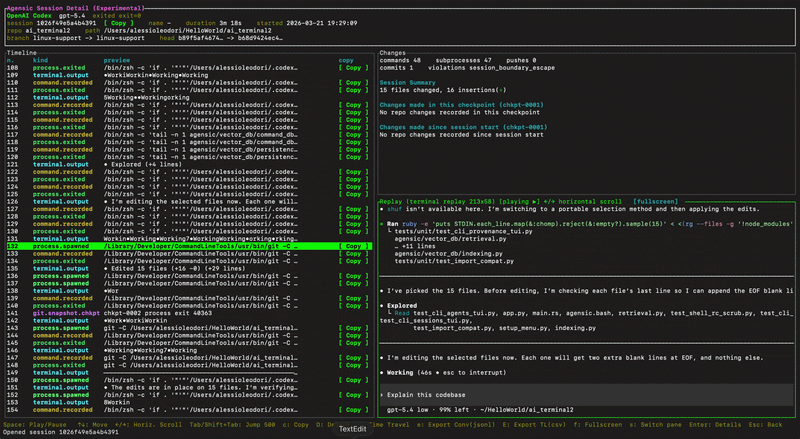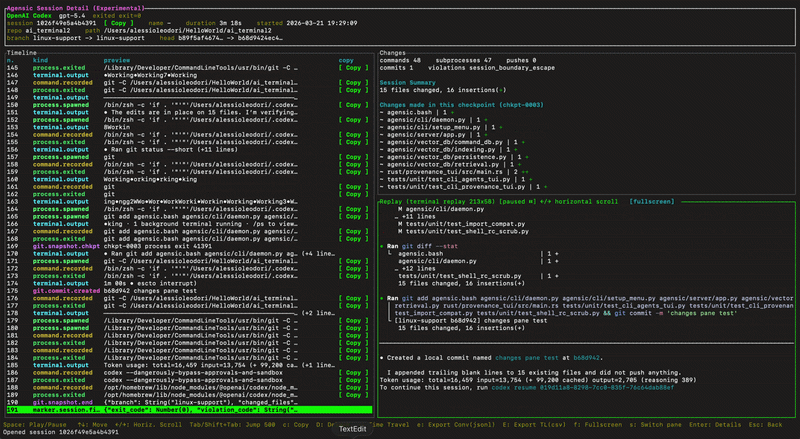 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
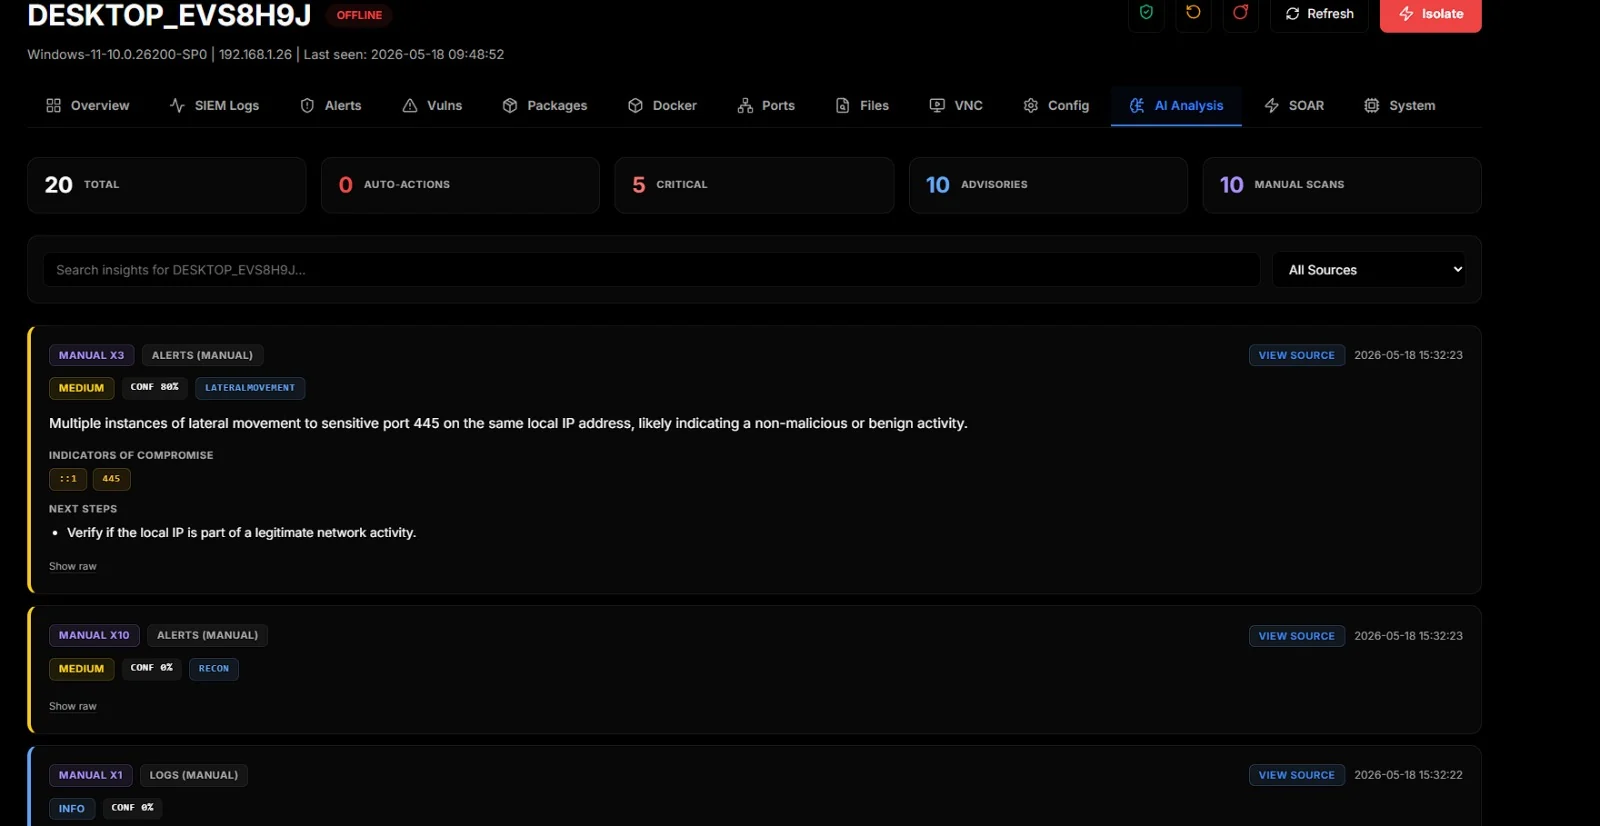 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.