
BLUESPAWN
 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams
configuration-auditingdefensive-toolsincident-response+3
ion28/bluespawnAn Active Defense and EDR software to empower Blue Teams
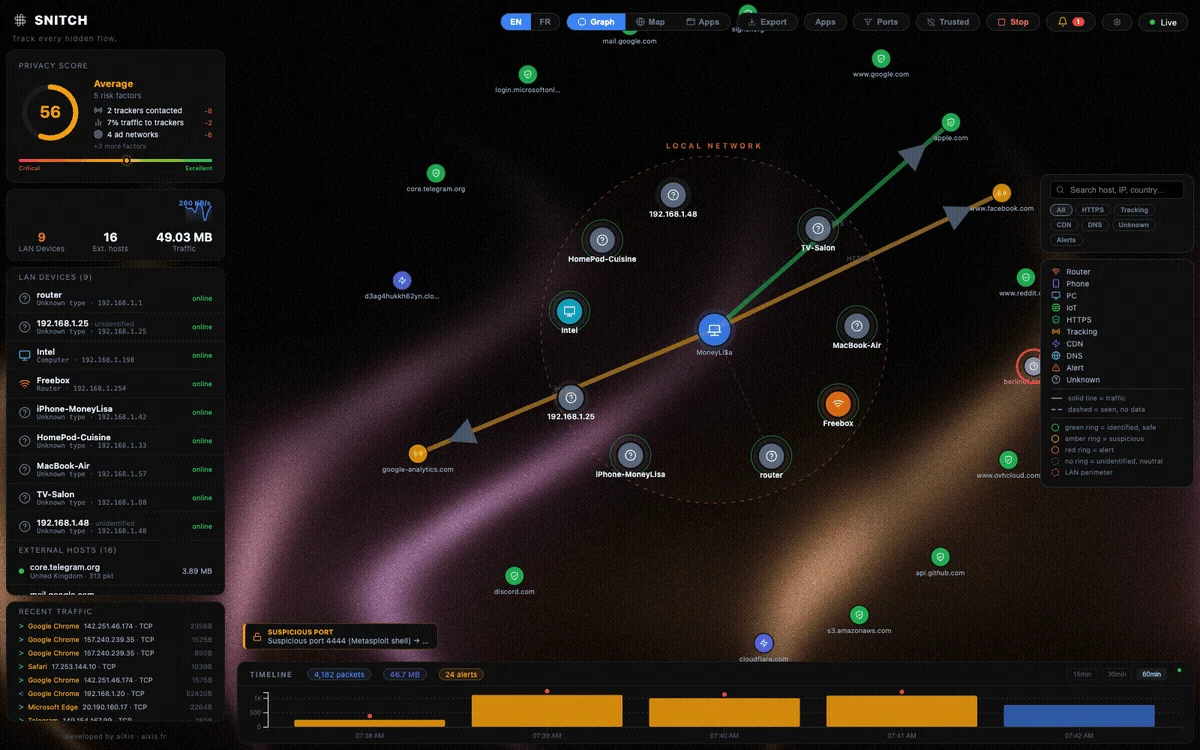 aixisstudio/snitch
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
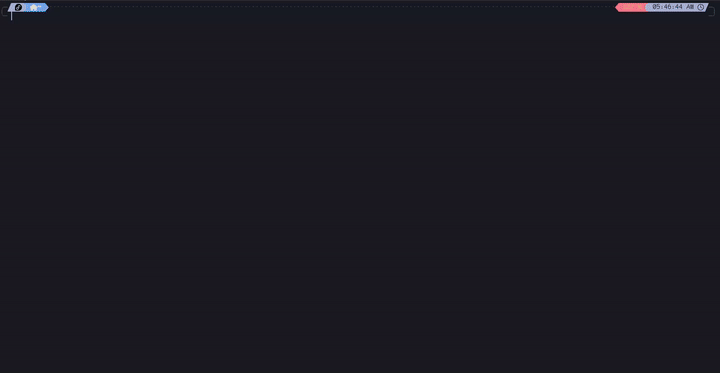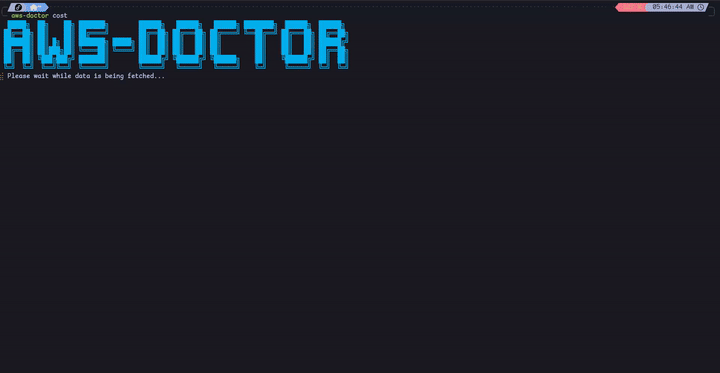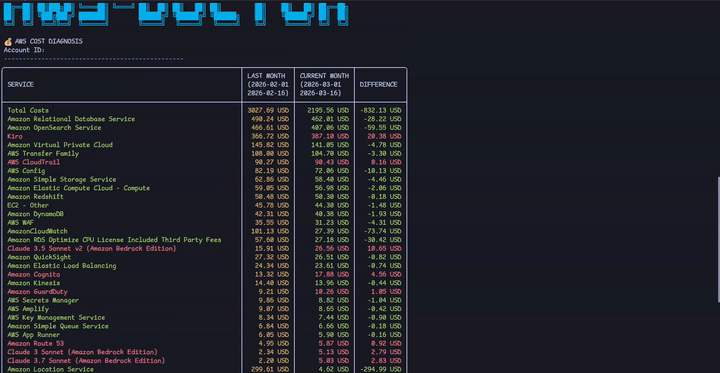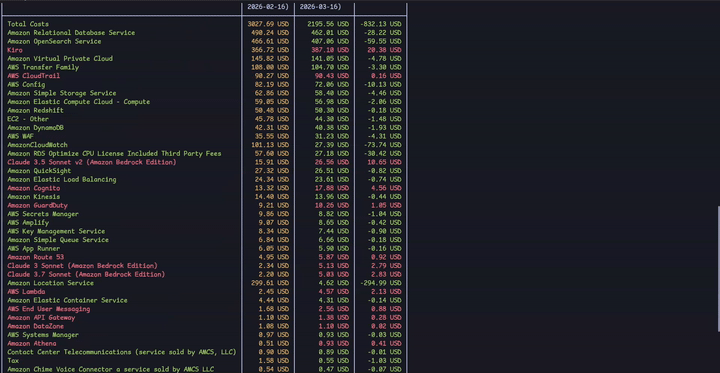 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
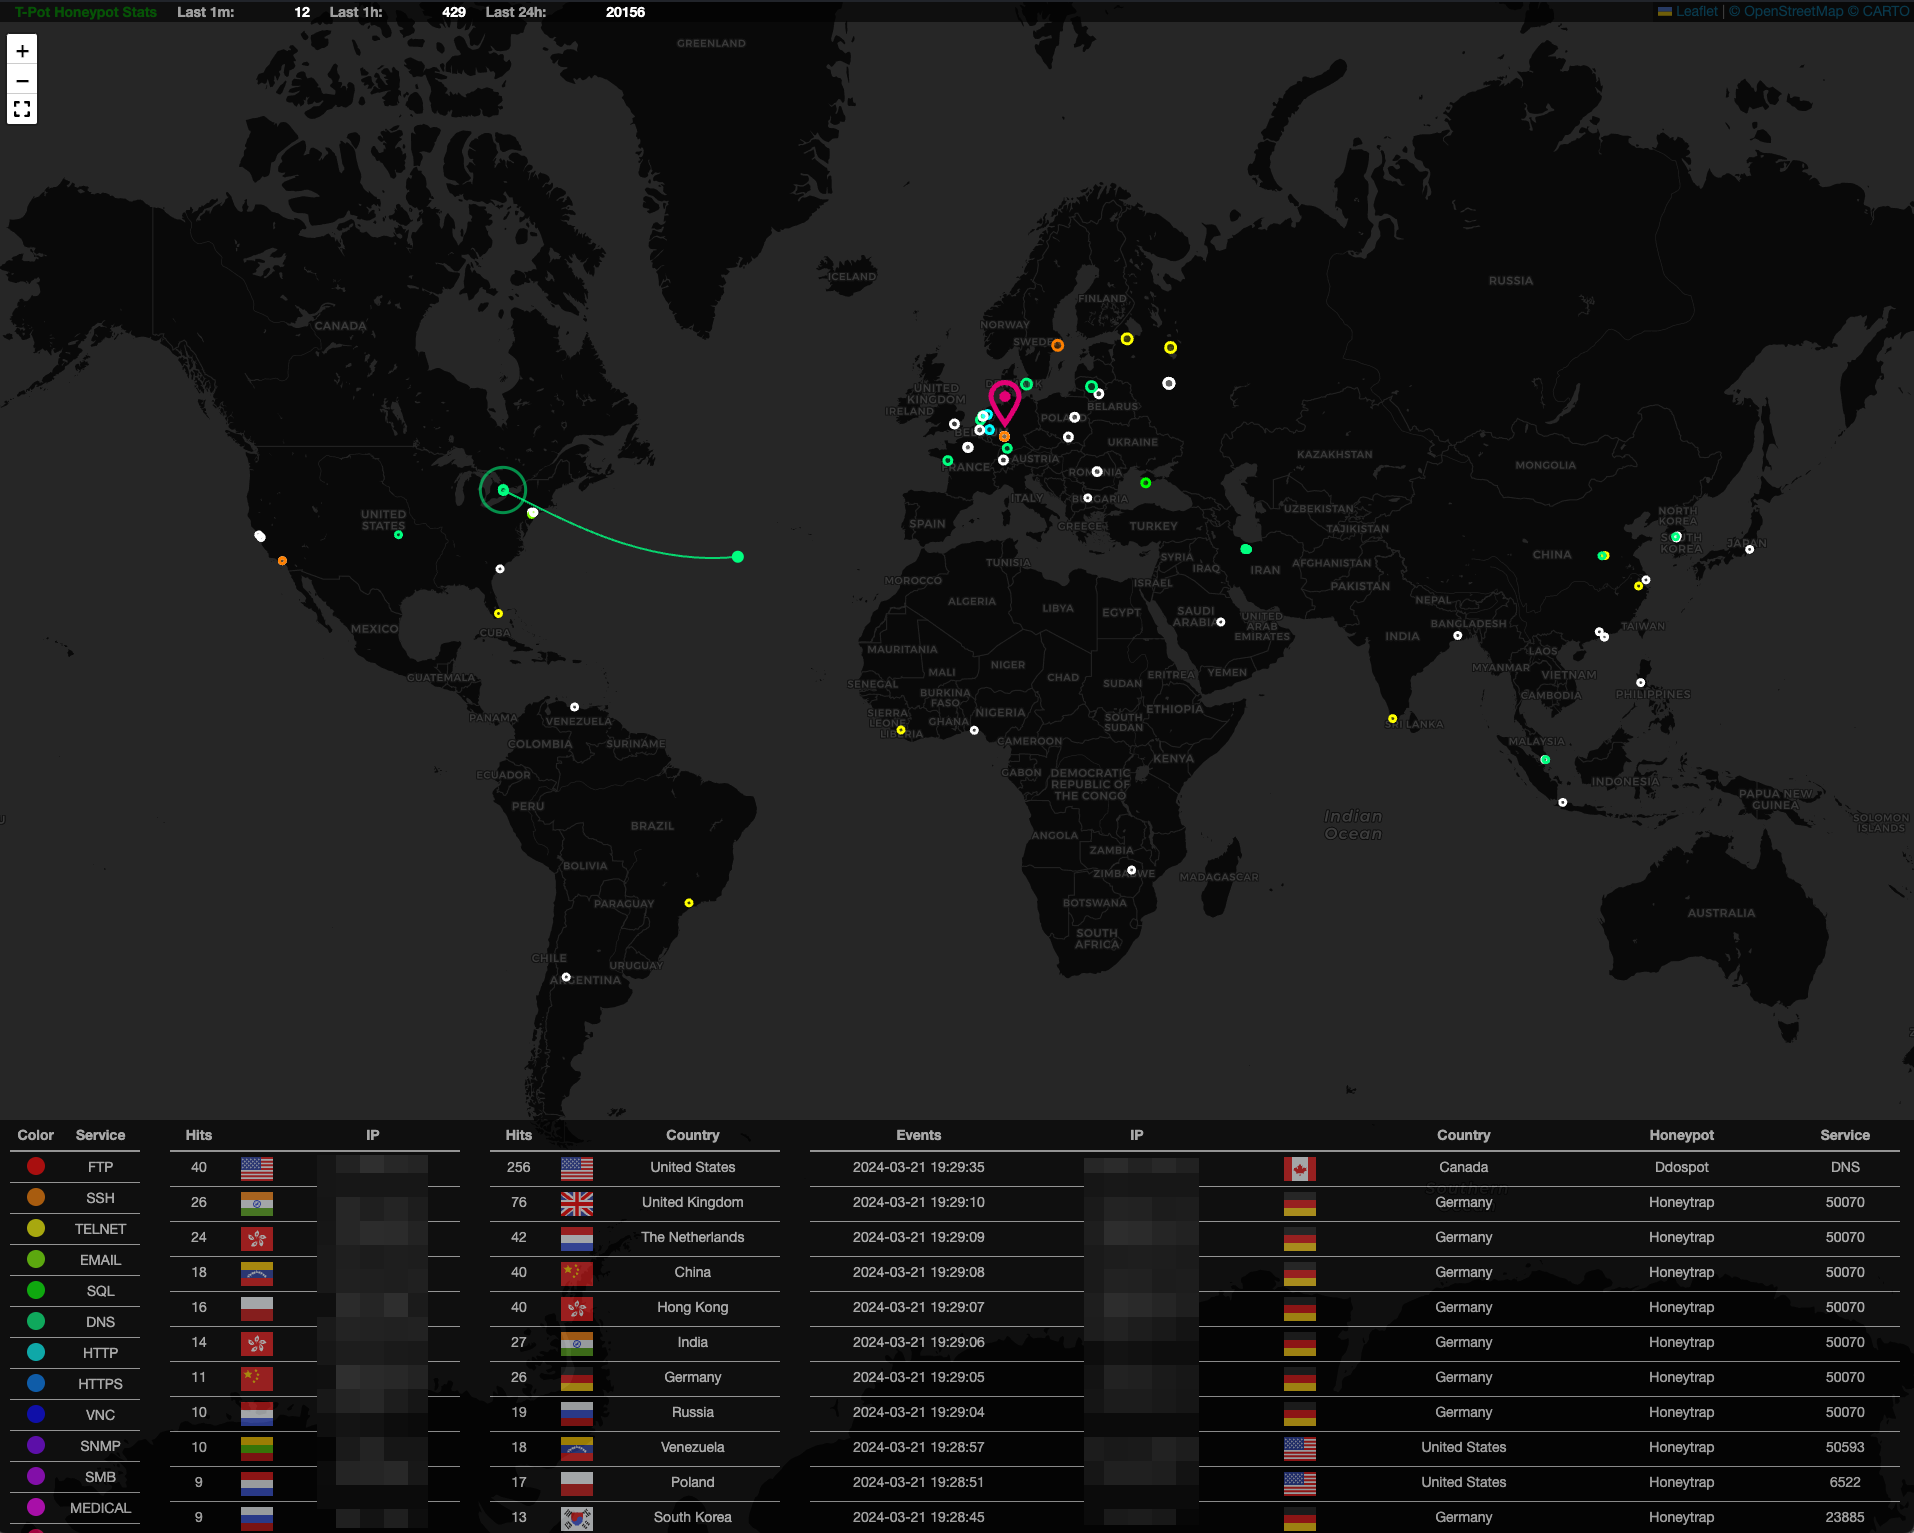 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 neo23x0/raccine
A Simple Ransomware Vaccine
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
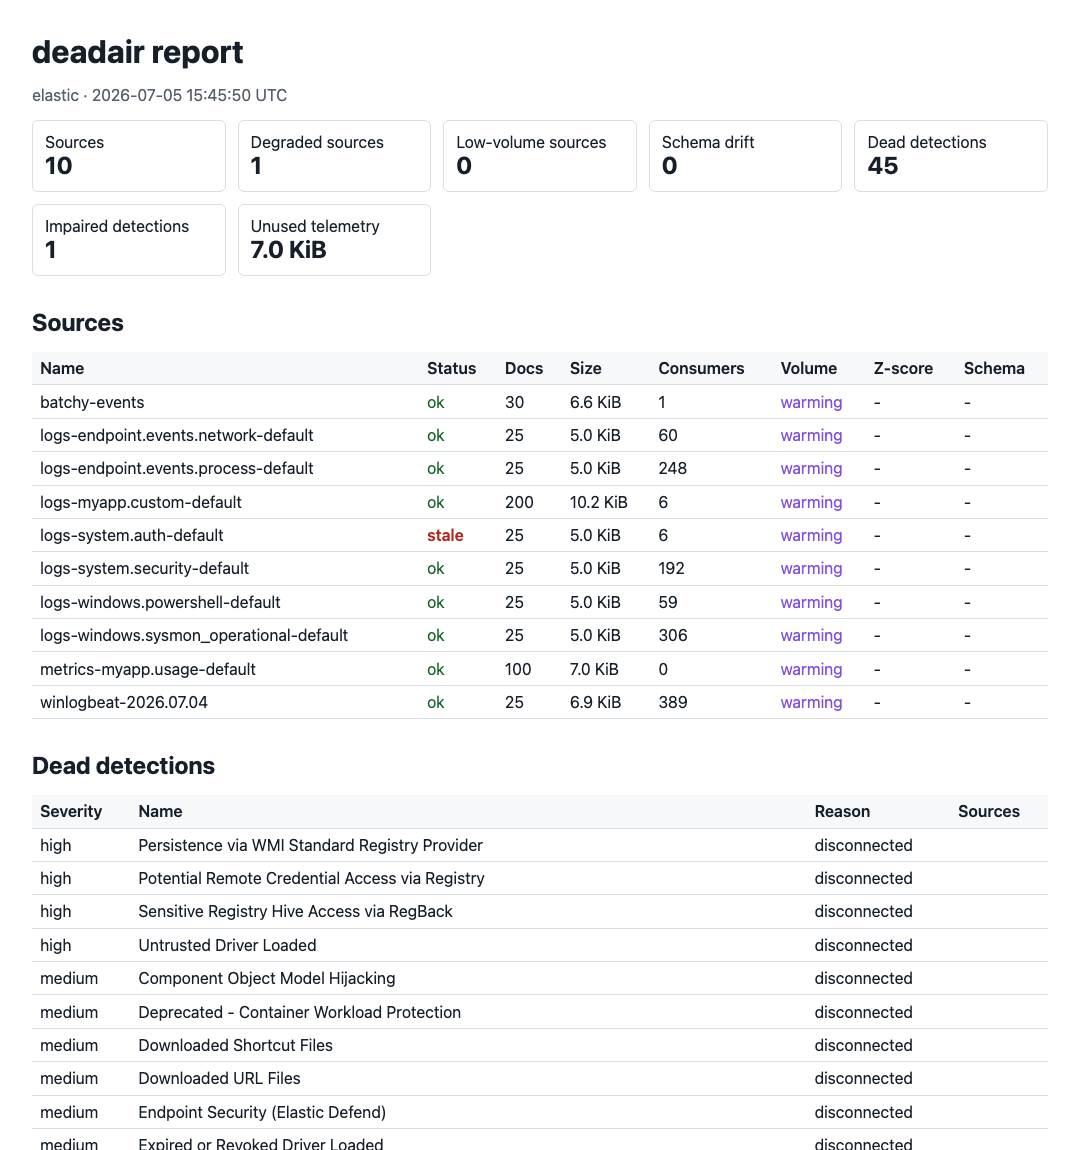 big-comfy/deadair
Finds the detection rules in your SIEM that are running blind