conti-ransomware-writeup

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…

Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…

Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)

Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.

Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…

A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…

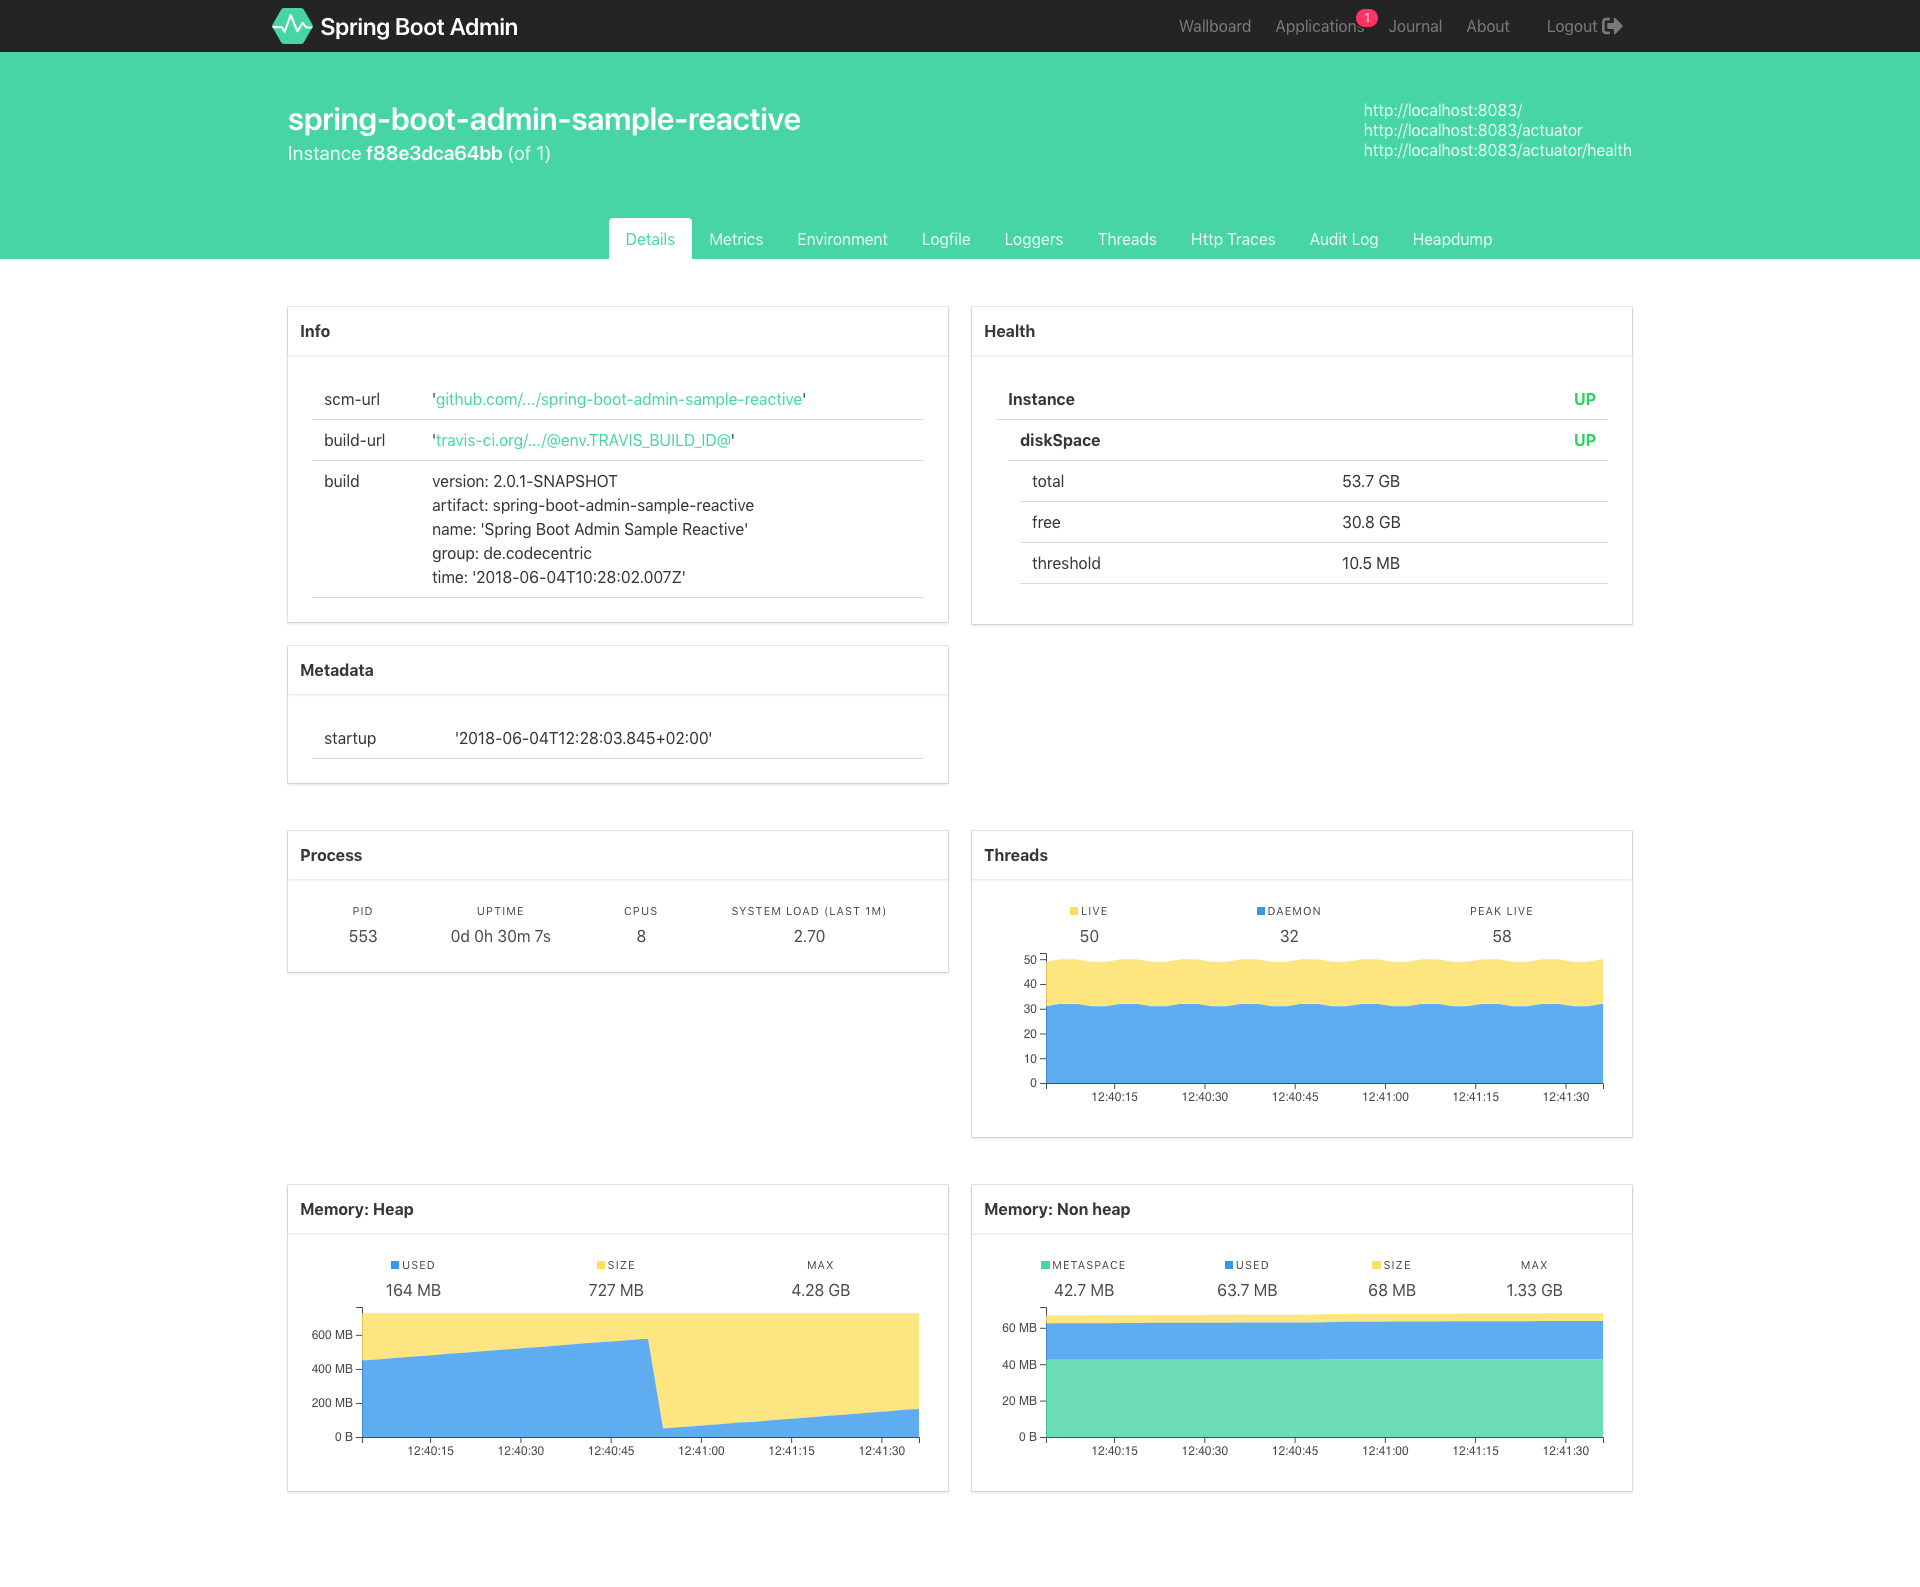
Admin interface for monitoring Spring Boot applications with health checks, metrics, log management, JMX interaction, and thread dump viewing.

Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…

This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…

CI pipeline for building nxlog-ce on Ubuntu with CVE-2020-35488 vulnerability detection, enabling automated log collection and security auditing in…

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management

C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

CLI tools for forensic investigation of Windows artifacts

Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.

Linux vulnerability scanner based on Salt Open and Vulners audit API, with Slack notifications and JIRA integration

Realtime secret and configuration management tool