
Honeypot-Project
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
defensive-toolseducationincident-response+5
109
owasp/honeypot-projectDeploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
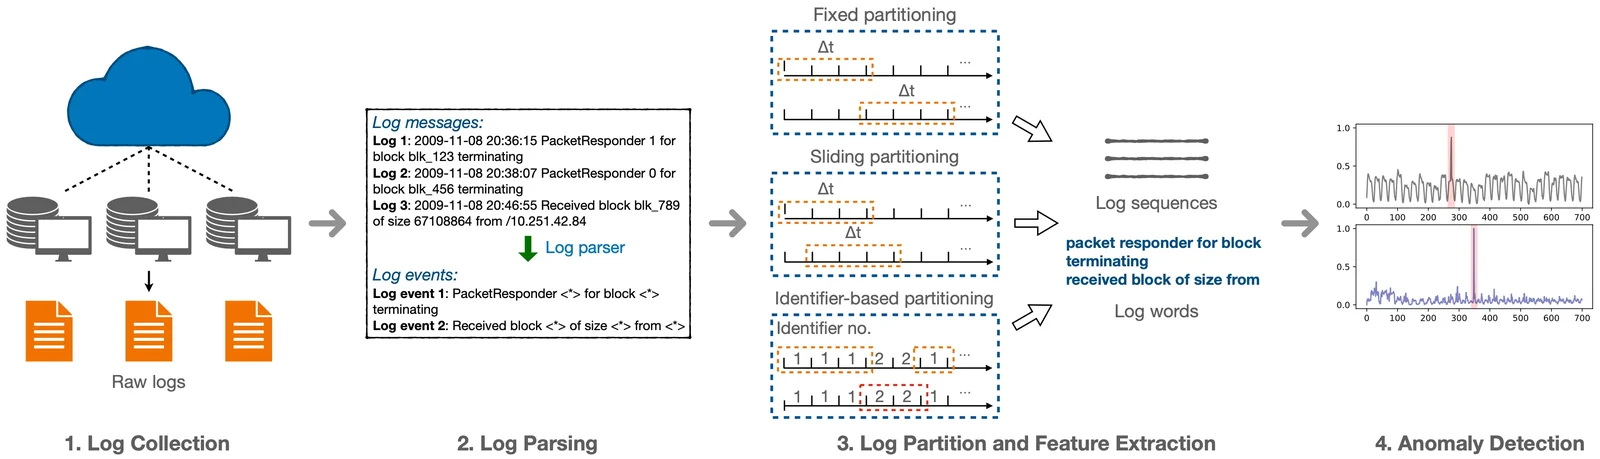 logpai/deep-loglizer
A deep learning toolkit for log-based anomaly detection
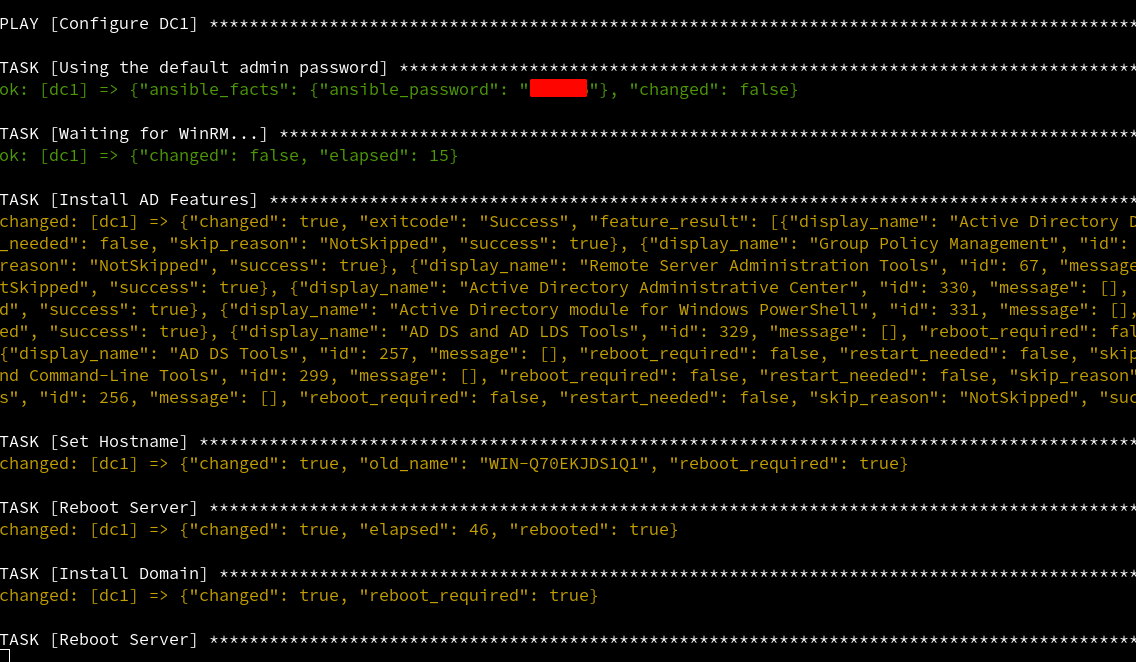 tothi/ad-honeypot-autodeploy
Deploy a small, intentionally insecure, vulnerable Windows Domain for RDP Honeypot fully automatically.
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.
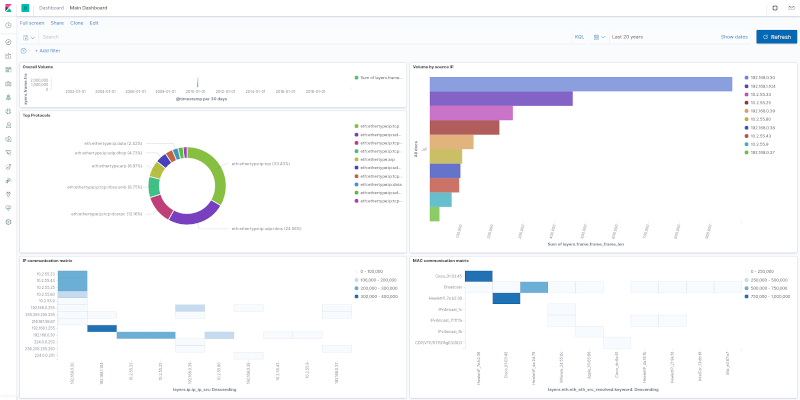 h21lab/tsharkvm
tshark + ELK analytics virtual machine
 liveoverflow/log4shell
Small example repo for looking into log4j CVE-2021-44228
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
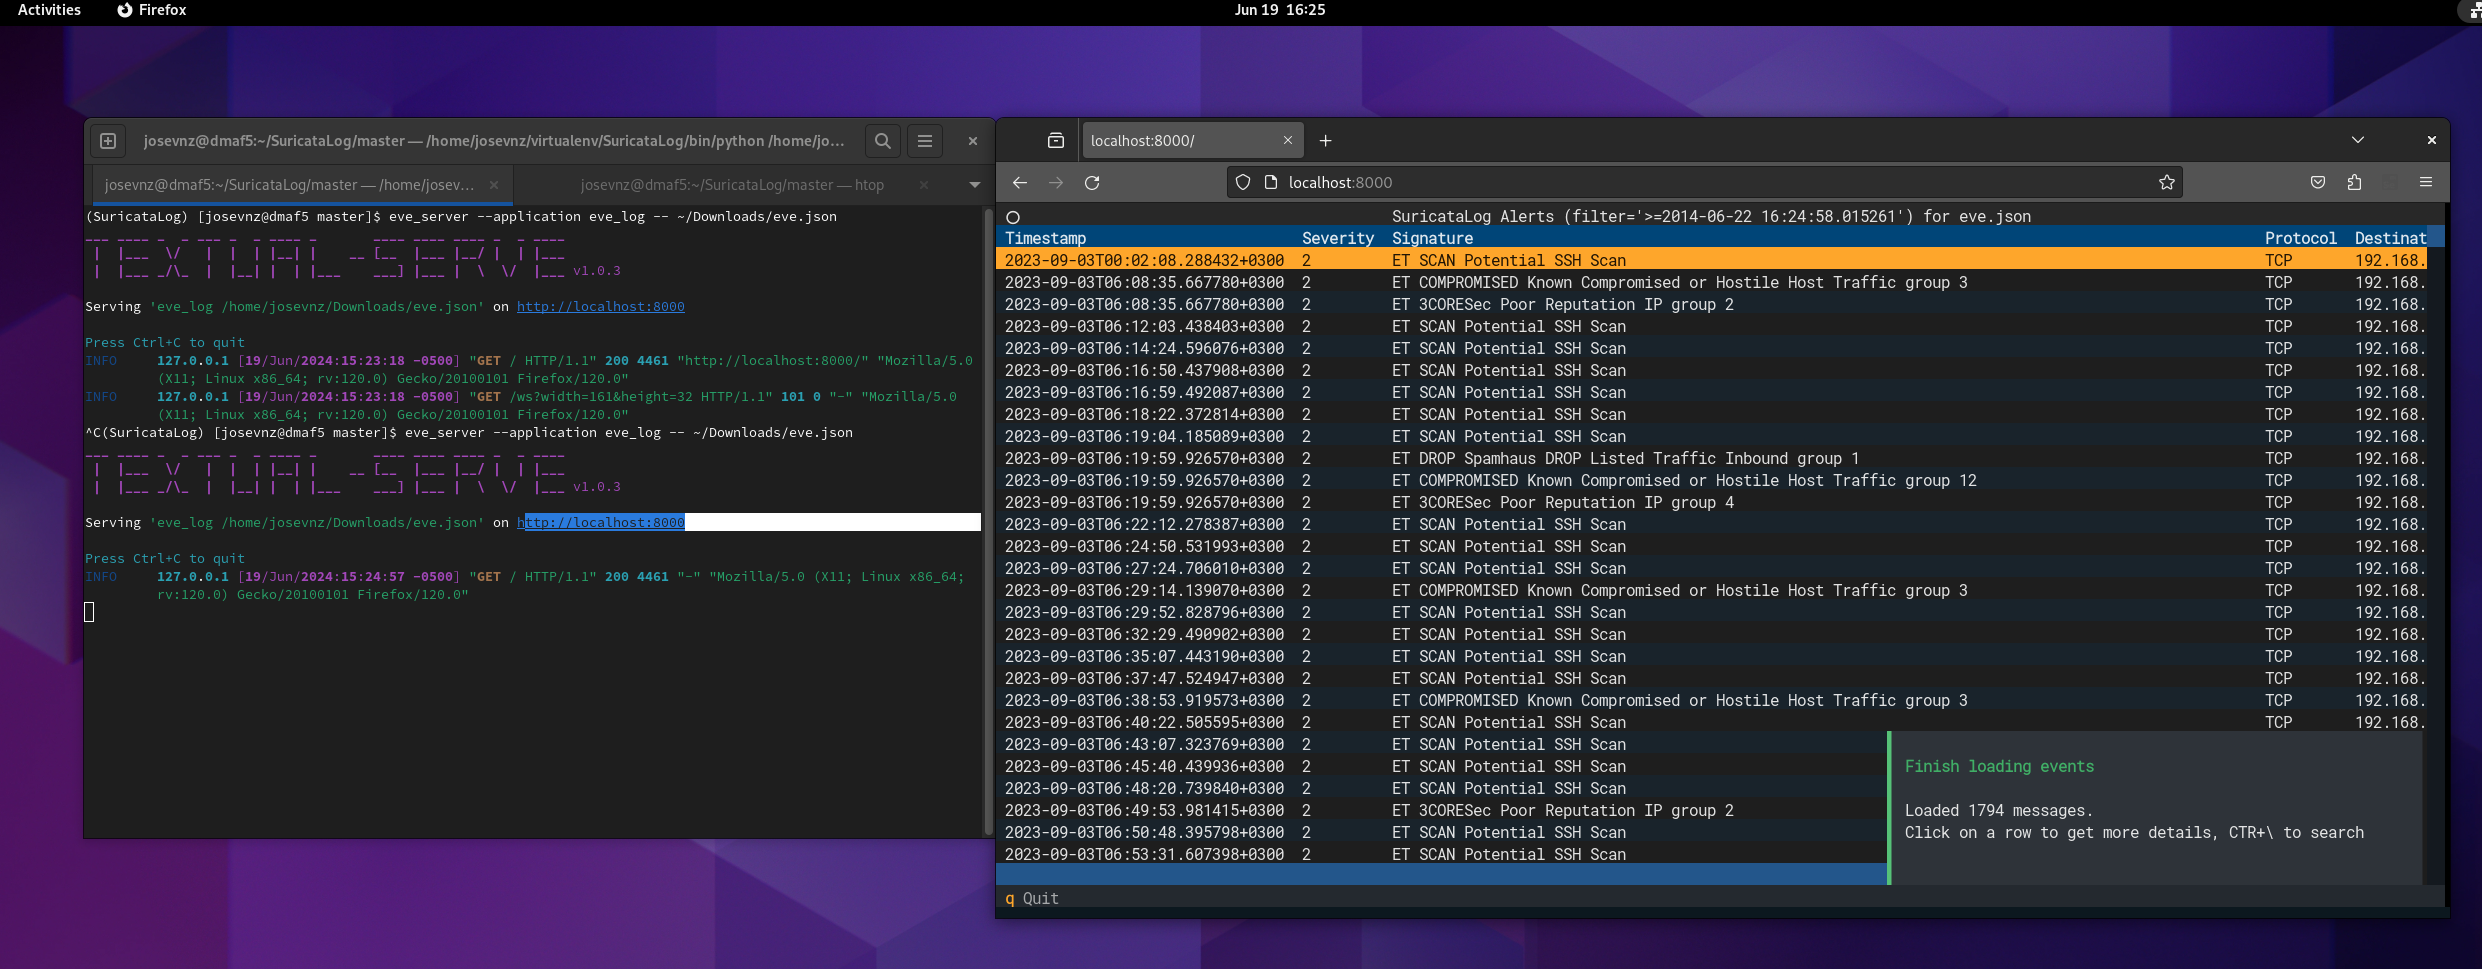 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
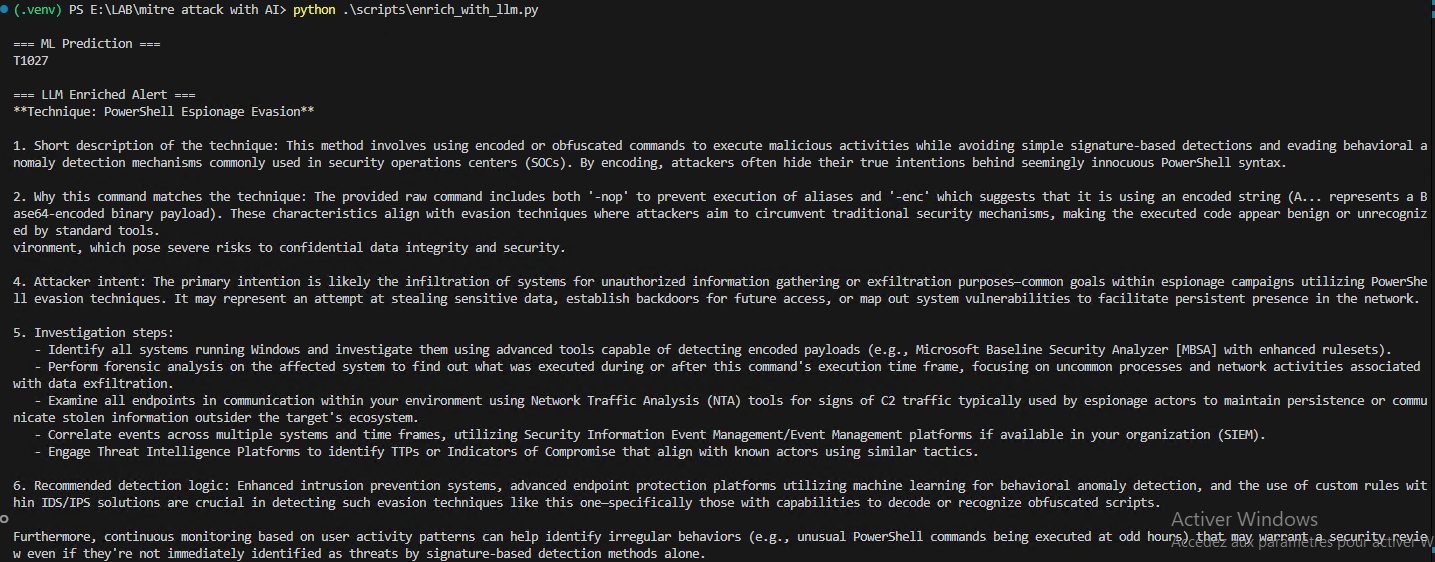 mouna23/ai-driven-mitre-attack
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.
 manishrawat21/analysis
Hands-on analysis of common APT attack techniques, focused on how they show up in logs and how defenders can realistically detect them.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 azeemering/cve-2021-44228-dfir-notes
CVE-2021-44228 DFIR Notes
 oscerd/cve-2026-85260
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85260, demonstrating camel-mllp PHI logging in affected versions and suppression after the…
 yora1928/papercut-cve-2026-81578-82078
Security research tool for PaperCut CVE-2026-81578 & CVE-2026-82078