

macos-collector
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
digital-forensicsforensicsincident-response+2
49
lethal-forensics/macos-collectormacos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
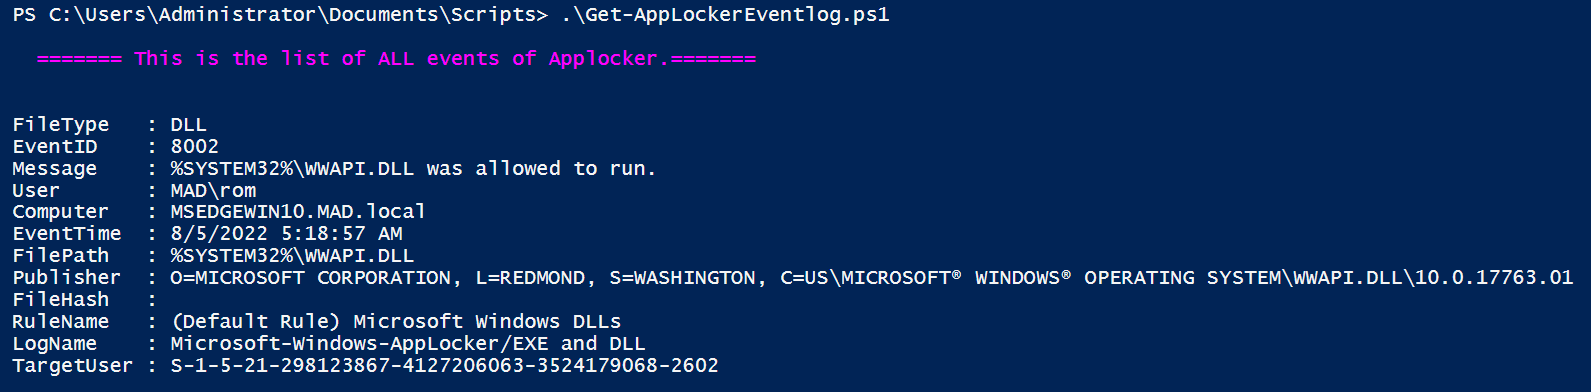 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 withsecurelabs/macostriagecollectionscript
Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
 corelight/log-add-http-post-bodies
Add POST body excerpt to Bro's HTTP log
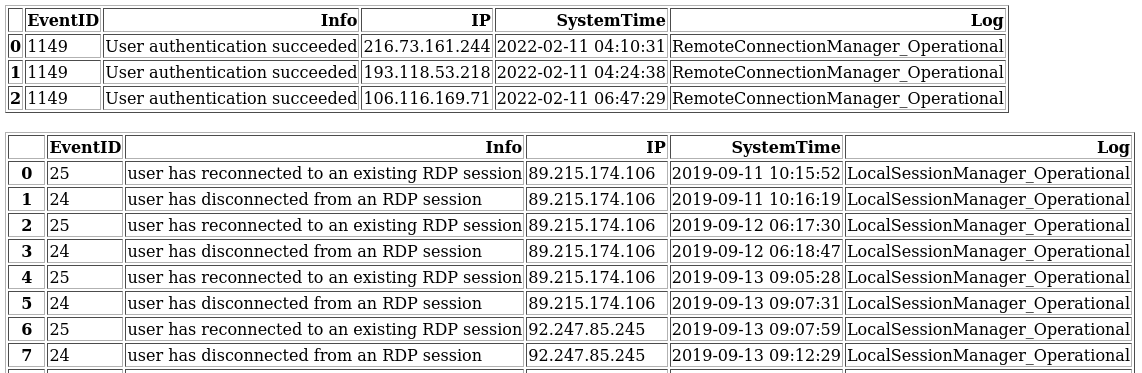 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 santosomar/log4j-ioc-detector
A Simple Log4j Indicator of Compromise Linux Detector
 corelight/top-dns
Top DNS Measurement for Bro
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 yossisassi/zerologon-exploitation-check
quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252
 hestat/drupal-check
Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600
 rocklambros/react2shell_hunter
AWS Organization-wide detection toolkit for CVE-2025-55182 & CVE-2025-66478 (React Server Components / Next.js RCE vulnerabilities)
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
 orjanj/netscaler_threat_hunt_helper
NetScaler CTX697096 Threat Hunt Helper (IoC scanner) - CVE-2026-88771, CVE-2026-88772, CVE-2026-88779
 soroushneshati/cve-2026-98432-ubuntu-mitigation
Check an Ubuntu host for CVE-2026-98432 and, after you confirm, apply the interim Red Hat RHSB-2026-016 mitigation. Ubuntu 20.04 to 26.10.